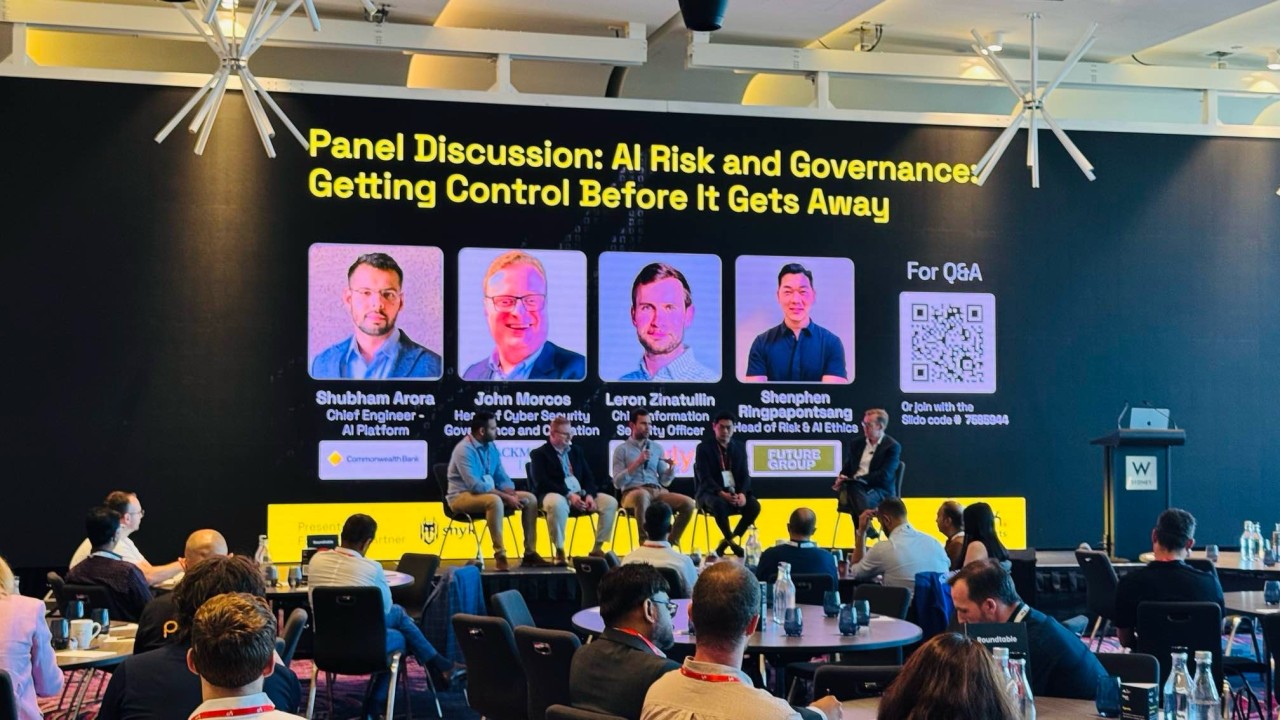
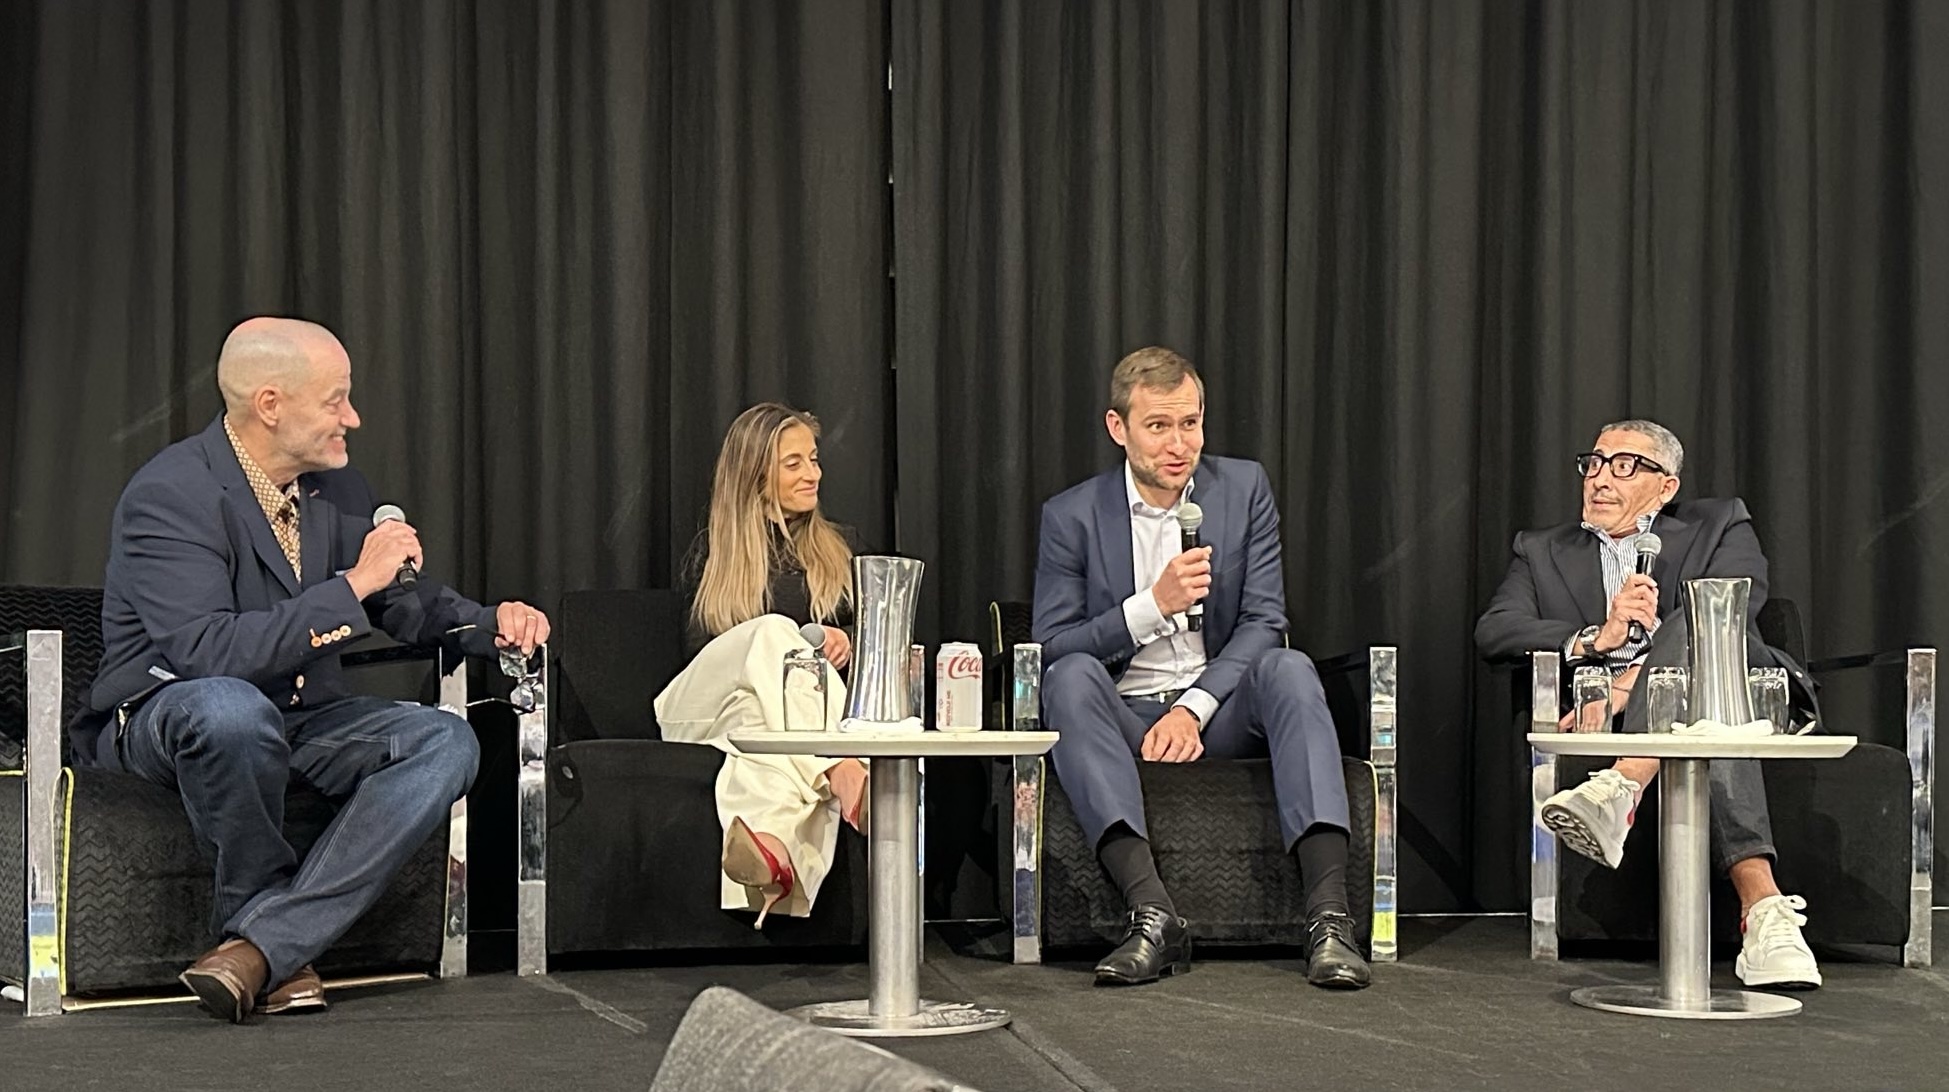
I recently took the stage to talk about one of the most consequential inflection points facing FinTech: the rapid arrival of agentic AI – systems that plan, decide and act autonomously – and what it means for risk, reputation, regulation and customer trust. Below is a distillation of the talk: what agentic AI actually is, why FinTechs are racing to adopt it, the real cyber threats it brings, and a pragmatic playbook leaders can use today.
I recently presented on how supplier relationships shape cybersecurity risk and why that risk ultimately becomes a reputational and trust challenge for organisations of every size and sector. Below is a summary of the most important lessons I shared, plus practical next steps security leaders can apply today.
I had the privilege of sharing my views on AI Risk at the AI Security Summit, where senior leaders and practitioners came together to translate high-level fear into practical guardrails. In this blog I share a short playbook of the key themes and real-world strategies.
It was good to attend the Essential Director Update – a timely reminder that good governance now requires foresight as well as oversight.
Staying on the forefront of contemporary governance demands AI and cybersecurity competency.
My key takeaways for boards and executives: ☑️ Data is the fuel: protect data integrity (accurate, consistent, timely) and focus governance where it creates the most value. ☑️ AI is everywhere, no longer just an IT challenge: adopt a human-centred approach, define guardrails around intent, and factor legal and ethical considerations into every deployment. ☑️ Balance innovation with risk: prioritise highest-value use cases, automate safety controls where possible, but don’t outsource accountability. ☑️ Cybersecurity must be risk-based: know your crown jewels, expect incidents, build crisis response plans and regularly test your defences. ☑️ People first: changing work practices will affect roles and culture; steer the transition and invest in policy and education.
It was great to join last night’s panel, where I shared practical lessons from managing AI in vendor ecosystems – including ethical implications, regulatory uncertainties and resilience at scale.
If you run a restaurant, your supplier gives you a batch of ingredients and you use them in meals for customers. You’re responsible if the food makes people sick. AI vendors are ingredient suppliers – you are the chef.
Guardrails don’t have to block progress – they can make AI reliable and trustworthy.
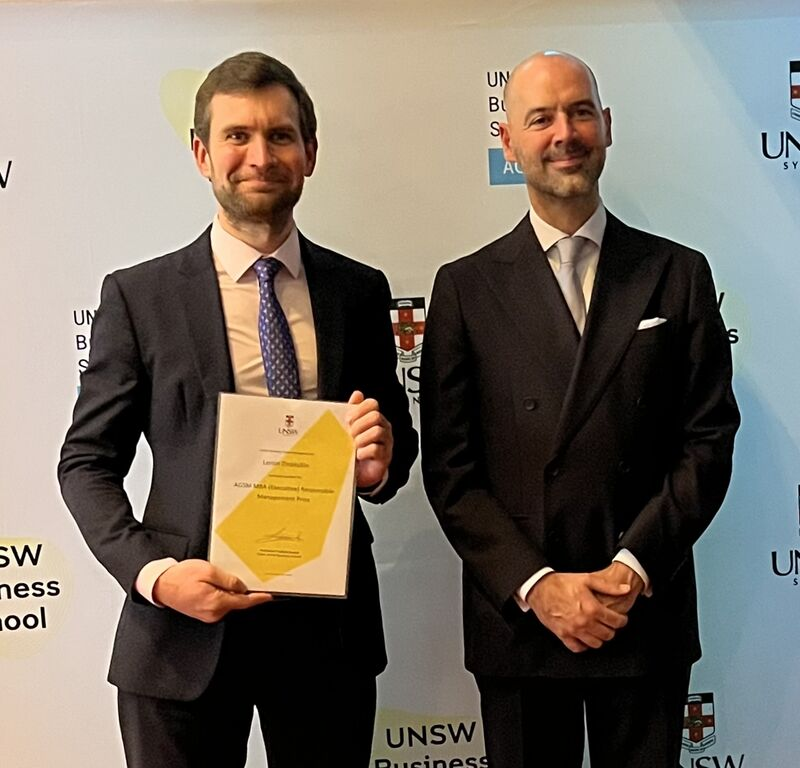
I’ve been awarded the Responsible Management Prize 🏆
This award recognises the values that guide me every day: honesty, integrity and leading with purpose.
In today’s evolving business landscape, where AI, risk management and cybersecurity intersect, ethical practice is essential. Because what we stand for today shapes the world we build tomorrow.
As algorithms power more of our decisions, we must ensure they’re transparent, fair and aligned with human values. Balancing innovation with resilience means anticipating unintended consequences, protecting stakeholders and driving sustainable outcomes.
Safeguarding data and privacy isn’t merely a technical challenge – it’s a trust imperative that underpins every relationship.
Thank you to the selection committee for recognising the work we’ve done together to build an inclusive, principled and forward-looking learning community.
I have just completed two leadership programs, both focused on AI-powered strategy
I particularly enjoyed the interactive hands-on session on designing AI capabilities to better understand: ✅ What the current trajectory of AI is, and why it reinforces the need for a clear AI strategy ✅ How AI is reshaping strategic thinking and planning, and how we can use it to strengthen techniques such as scenario analysis ✅ How AI is transforming day-to-day work, and practical steps that can help us build genuine AI readiness
Huge thanks to the academics and industry experts for sharing their research-backed insights. I look forward to applying these frameworks and tools to drive purposeful, data-driven impact in my own leadership journey.
The program is designed to equip leaders with skills and practical experience for not-for-profit board and social impact leadership. I found the sessions on governance, finance, risk and strategy for not-for-profit directors very useful.
I appreciate the opportunity to contribute to an organisation that is truly making a difference and driving systemic change in our communities.
Just wrapped up an engaging panel on AI guardrails where we explored the shifting ground beneath enterprise AI adoption.
The best AI governance starts not with controls, but with culture. When people start asking not just ‘Can we do this?’ but ‘Should we?” that’s when you know you’re on the right path.
Secure by Design is a widely understood concept in cybersecurity, it can be extended to Ethics by Design when building and adopting AI capabilities. Ethical considerations should be embedded from the start, with continuous assurance throughout the lifecycle.
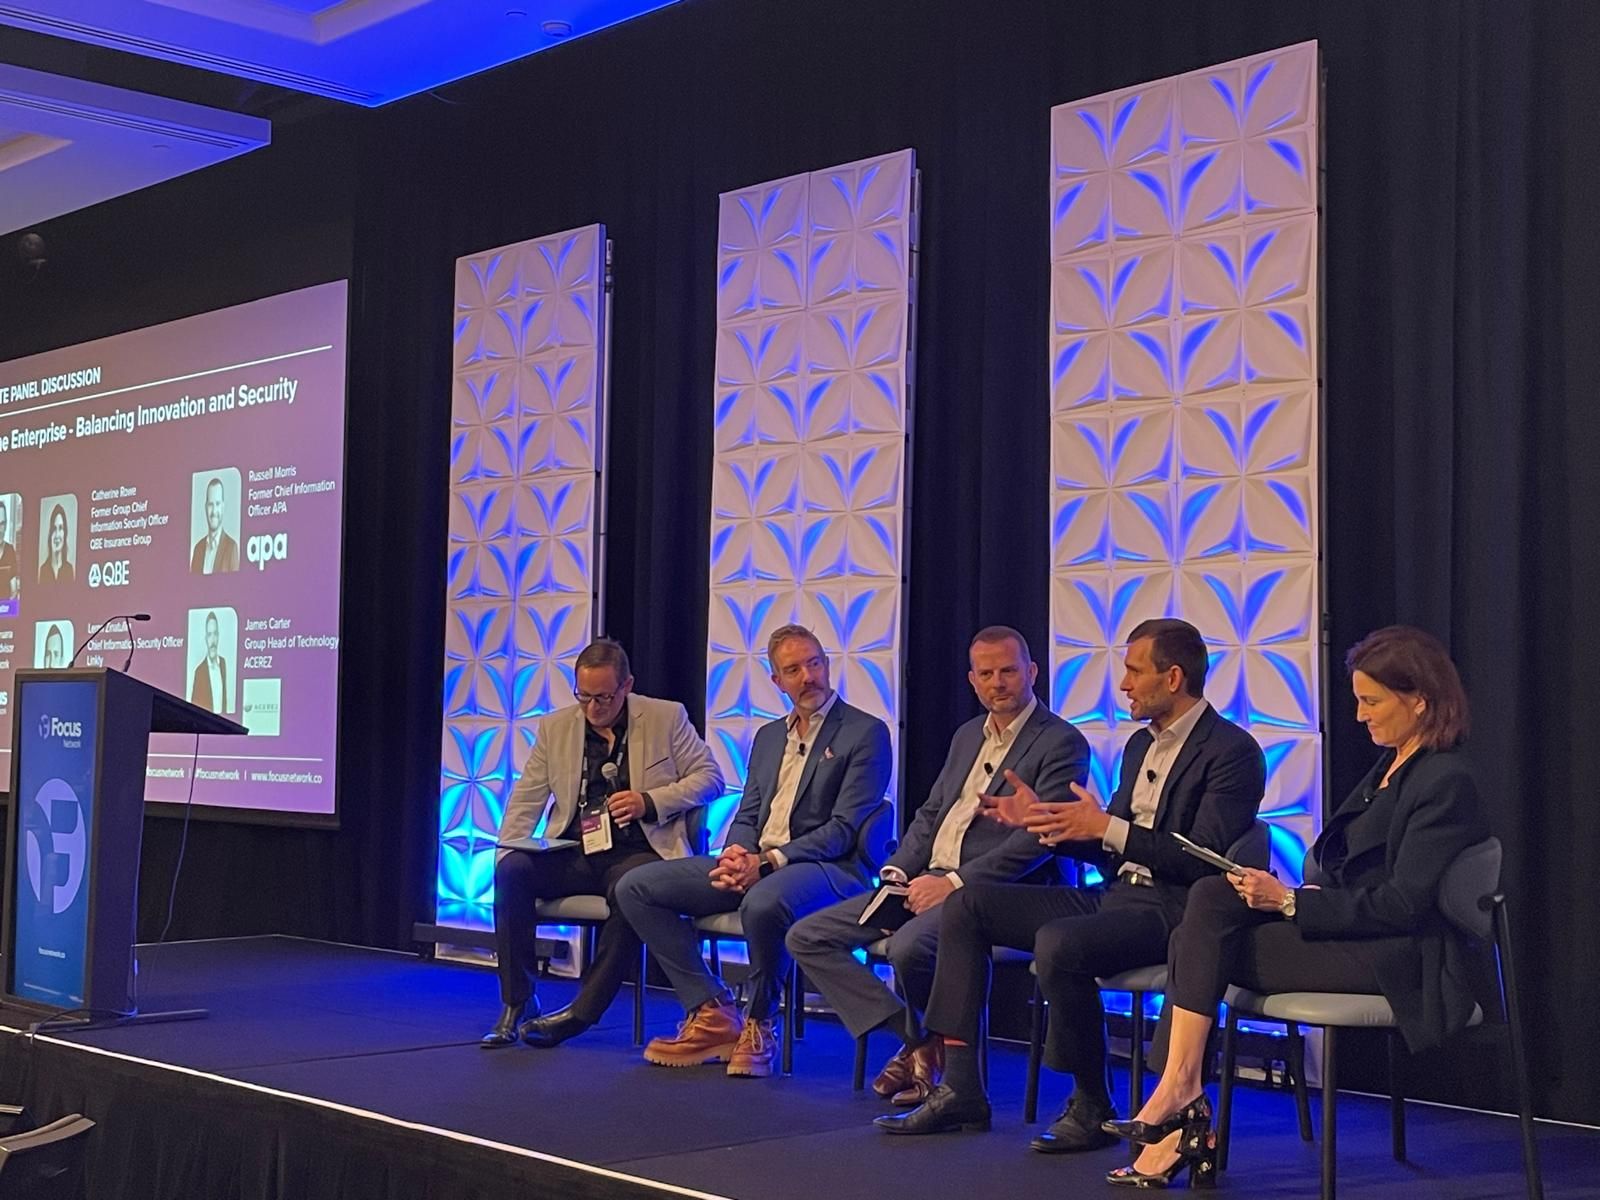
It was great to have a debate on balancing innovation and security keynote panel, where we dug into both the promise and the perils of AI adoption from the CISO and CIO perspectives.
Your biggest AI risks really depend on where and how you’re using it. I recommend reviewing your product roadmap for AI-powered features to anticipate potential gaps.
Map out whether AI is home-grown, vendor-sourced or embedded. When it comes to governance, we can borrow from what we learned with BYOD, cloud and shadow IT. Extend existing security reviews, supply-chain checks and third-party assessments into your AI program. For quick wins, manage it like a SaaS risk: think privacy controls and boundaries around sensitive data.