The application of AI for cyber defence: RSAC CISO Bootcamp

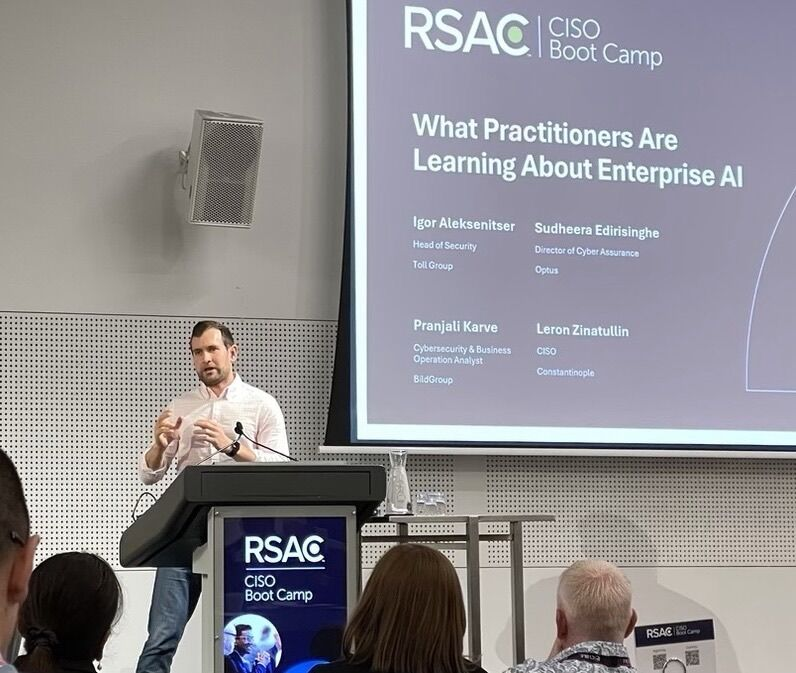
It was great to share my views on AI governance and the application of AI for cyber defence at the RSAC CISO Bootcamp.

I loved the audience participation – it’s a great community, and it’s a privilege to be able to exchange actionable tips with my peers.

Another wonderful day packed with practical sessions on cyber risk, board reporting, crisis response exercise practice, frontier AI model risk management, data breach mitigation and more.

Where else would you talk to the Deputy CISO of Anthropic and the former director of the US Cybersecurity and Infrastructure Security Agency (CISA) on the same day?
CSO30 Awards Winner

I’m proud to have been recognised as one of the top Chief Security Officers in Australia!

I couldn’t have done this without the support and commitment from my team, peers and the wider cyber security community globally.

Securing critical national infrastructure

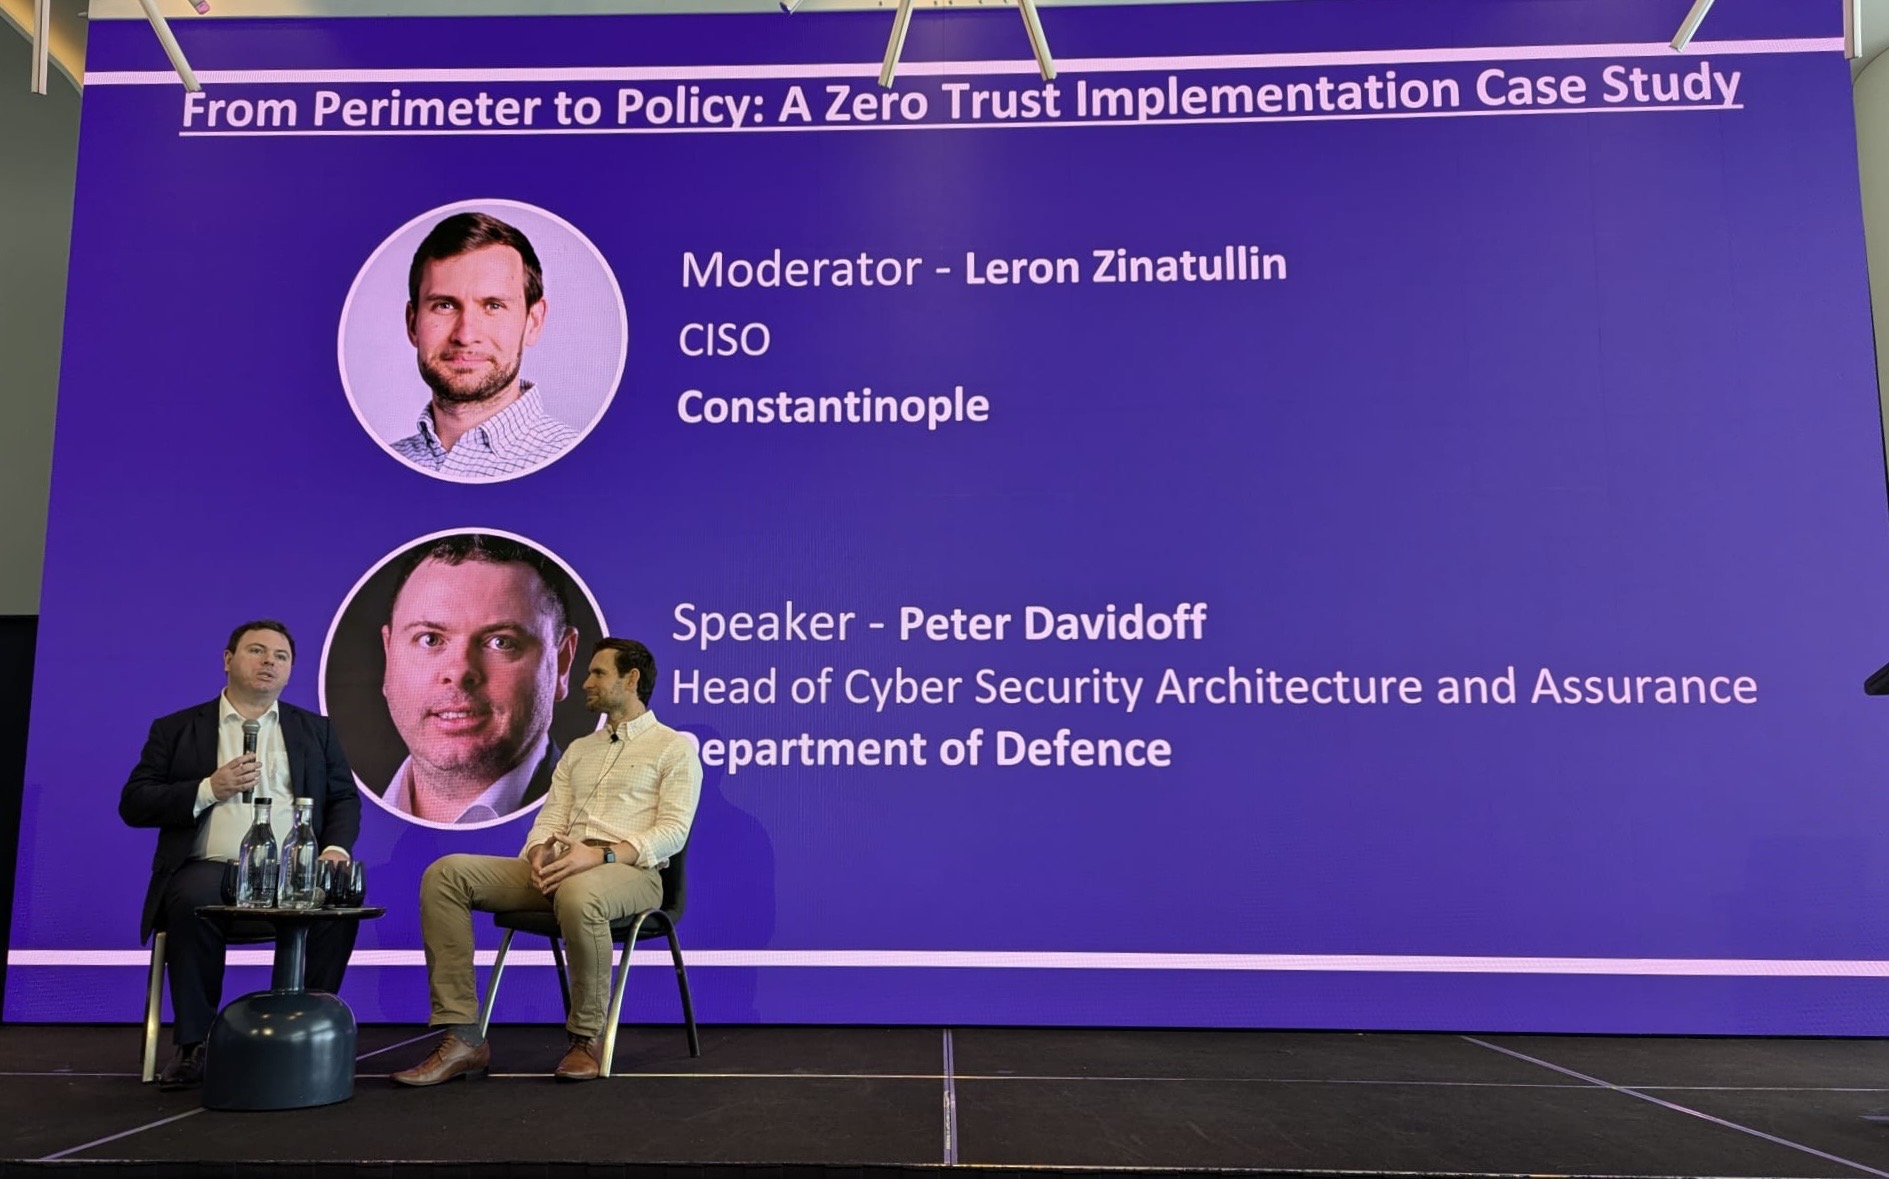
I had a great time talking to Peter Davidoff from the Australian Government about the evolving approach to security.

We touched on the challenges and opportunities of securing critical national infrastructure, the increasing role of AI and practical examples of developing a defence-in-depth approach to security architecture.

A big thanks to the audience for great questions!

Board Strategy Day

I”m very proud to have joined the board of SMART Recovery Australia with the mission to help people live a life beyond addiction through evidence-based, inclusive and empowering programs.

And no better way to start than with a strategy offsite bringing together fellow directors and the executive team for a day focusing on financial sustainability, AI governance, risk appetite and long-term impact measurement.

I look forward to contributing and applying my experience in board directorship, social impact measurement, AI in the not-for-profit sector, NFP governance, cybersecurity, strategy and leadership.

CISO Interview: Psychology and the Role of a CISO

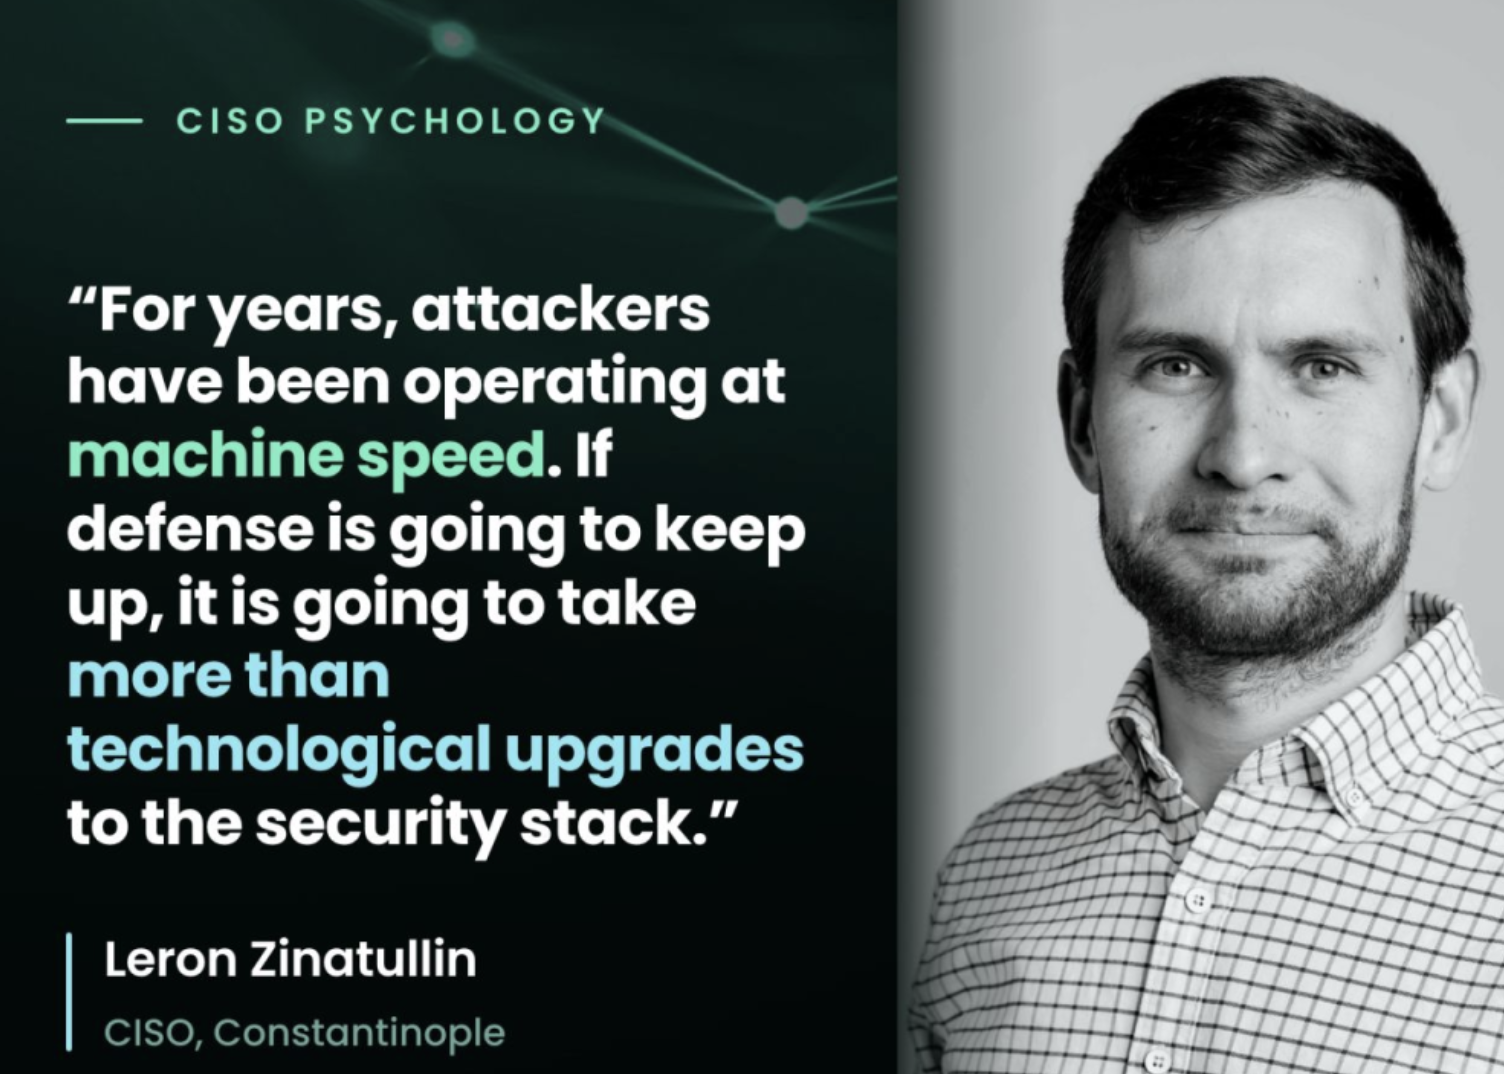
When both attackers and defenders use AI, it’s the people who become the edge.

Attackers already run at machine speed, and faster tools only close part of that gap.

It was great to sit down with Dan Raywood to talk about building security culture and the evolving role of a CISO 👇

More

Key points from the CIO keynote

Security failures are rarely just a technology problem. They’re a design problem – a mismatch between how controls are built and how people actually work.

That was my message keynoting at CIO Leadership Live.

AI has amplified the security fundamentals.

☑️ Defaults beat persuasion: passkeys by default, automatic updates, SSO. The secure choice should be the easiest choice.
☑️ Shadow AI is a friction signal, not a compliance failure. If people are pasting data into unapproved chatbots, your sanctioned path is too slow. Give them a fast, safe alternative.
☑️ Build trust, not fear. Blameless reviews and visible leadership create the psychological safety people need to report incidents early.

The CIOs who win with AI won’t be the ones with the strictest rules but the ones whose guardrails make the secure way the easy way.

More

Guest lecture: developing and implementing a security strategy

I had the pleasure of delivering a guest lecture on developing and implementing a cybersecurity strategy to students at the School of Information Systems and Technology Management, UNSW.
 
A security strategy is a set of decisions about what you will and won’t prioritise, made under real constraints – budget, headcount and a threat landscape that doesn’t wait for your roadmap to catch up.
 
Strategy starts with the business. If you can’t explain your security priorities in terms of what the organisation is trying to achieve, you won’t get the backing.
 
With AI, the fundamentals are still important, but the timelines are now compressed.
 
Thank you UNSW for the invitation, and to the students for the great discussion. This cohort is entering the field at a very interesting moment.

Global CISO 100

It’s great to be included in the Global CISO 100 🏆

This award recognises key pillars of our industry: innovation, strategic vision, leadership, team development and community contribution.

I’m incredibly grateful for the nomination and want to extend a big thank you to the judges and my network. Cyber security is a team effort, and I’m fortunate to work alongside an exceptional team and peer group every day.

Build Security for People – a keynote at CIO Leadership Live

I delivered a keynote at CIO Leadership Live.

For about a decade, our industry has had a favourite phrase: people are the weakest link. I made the opposite case – that the people we’ve been blaming are the most capable security asset we have, and we’ve spent that decade building systems that fight them instead of fit them.

The talk covered why training and punishment don’t work, why every workaround is actually free user research, and how you design your way to secure behaviour by making the secure path the easy path. And of course, where AI fits into all of it.

The intersection of AI and Cyber

It was great to share my thoughts on the intersection of AI and Cyber.

I kept it practical and worked through three key dimensions: how AI is changing the defender’s day-to-day, how we secure AI itself and how we defend when AI becomes the threat.

It was particularly relevant given the latest frontier model releases, like Anthropic’s Fable / Mythos (and OpenAI’s GPT-5.5-Cyber) and their applications to cybersecurity.

If attackers and defenders now have the same AI capabilities, your advantage comes not from the tools but from your people, your data and how well you’ve done the fundamentals.

Grateful to the panel and to everyone who put their hand up and got stuck into the discussion.