Board Strategy Day

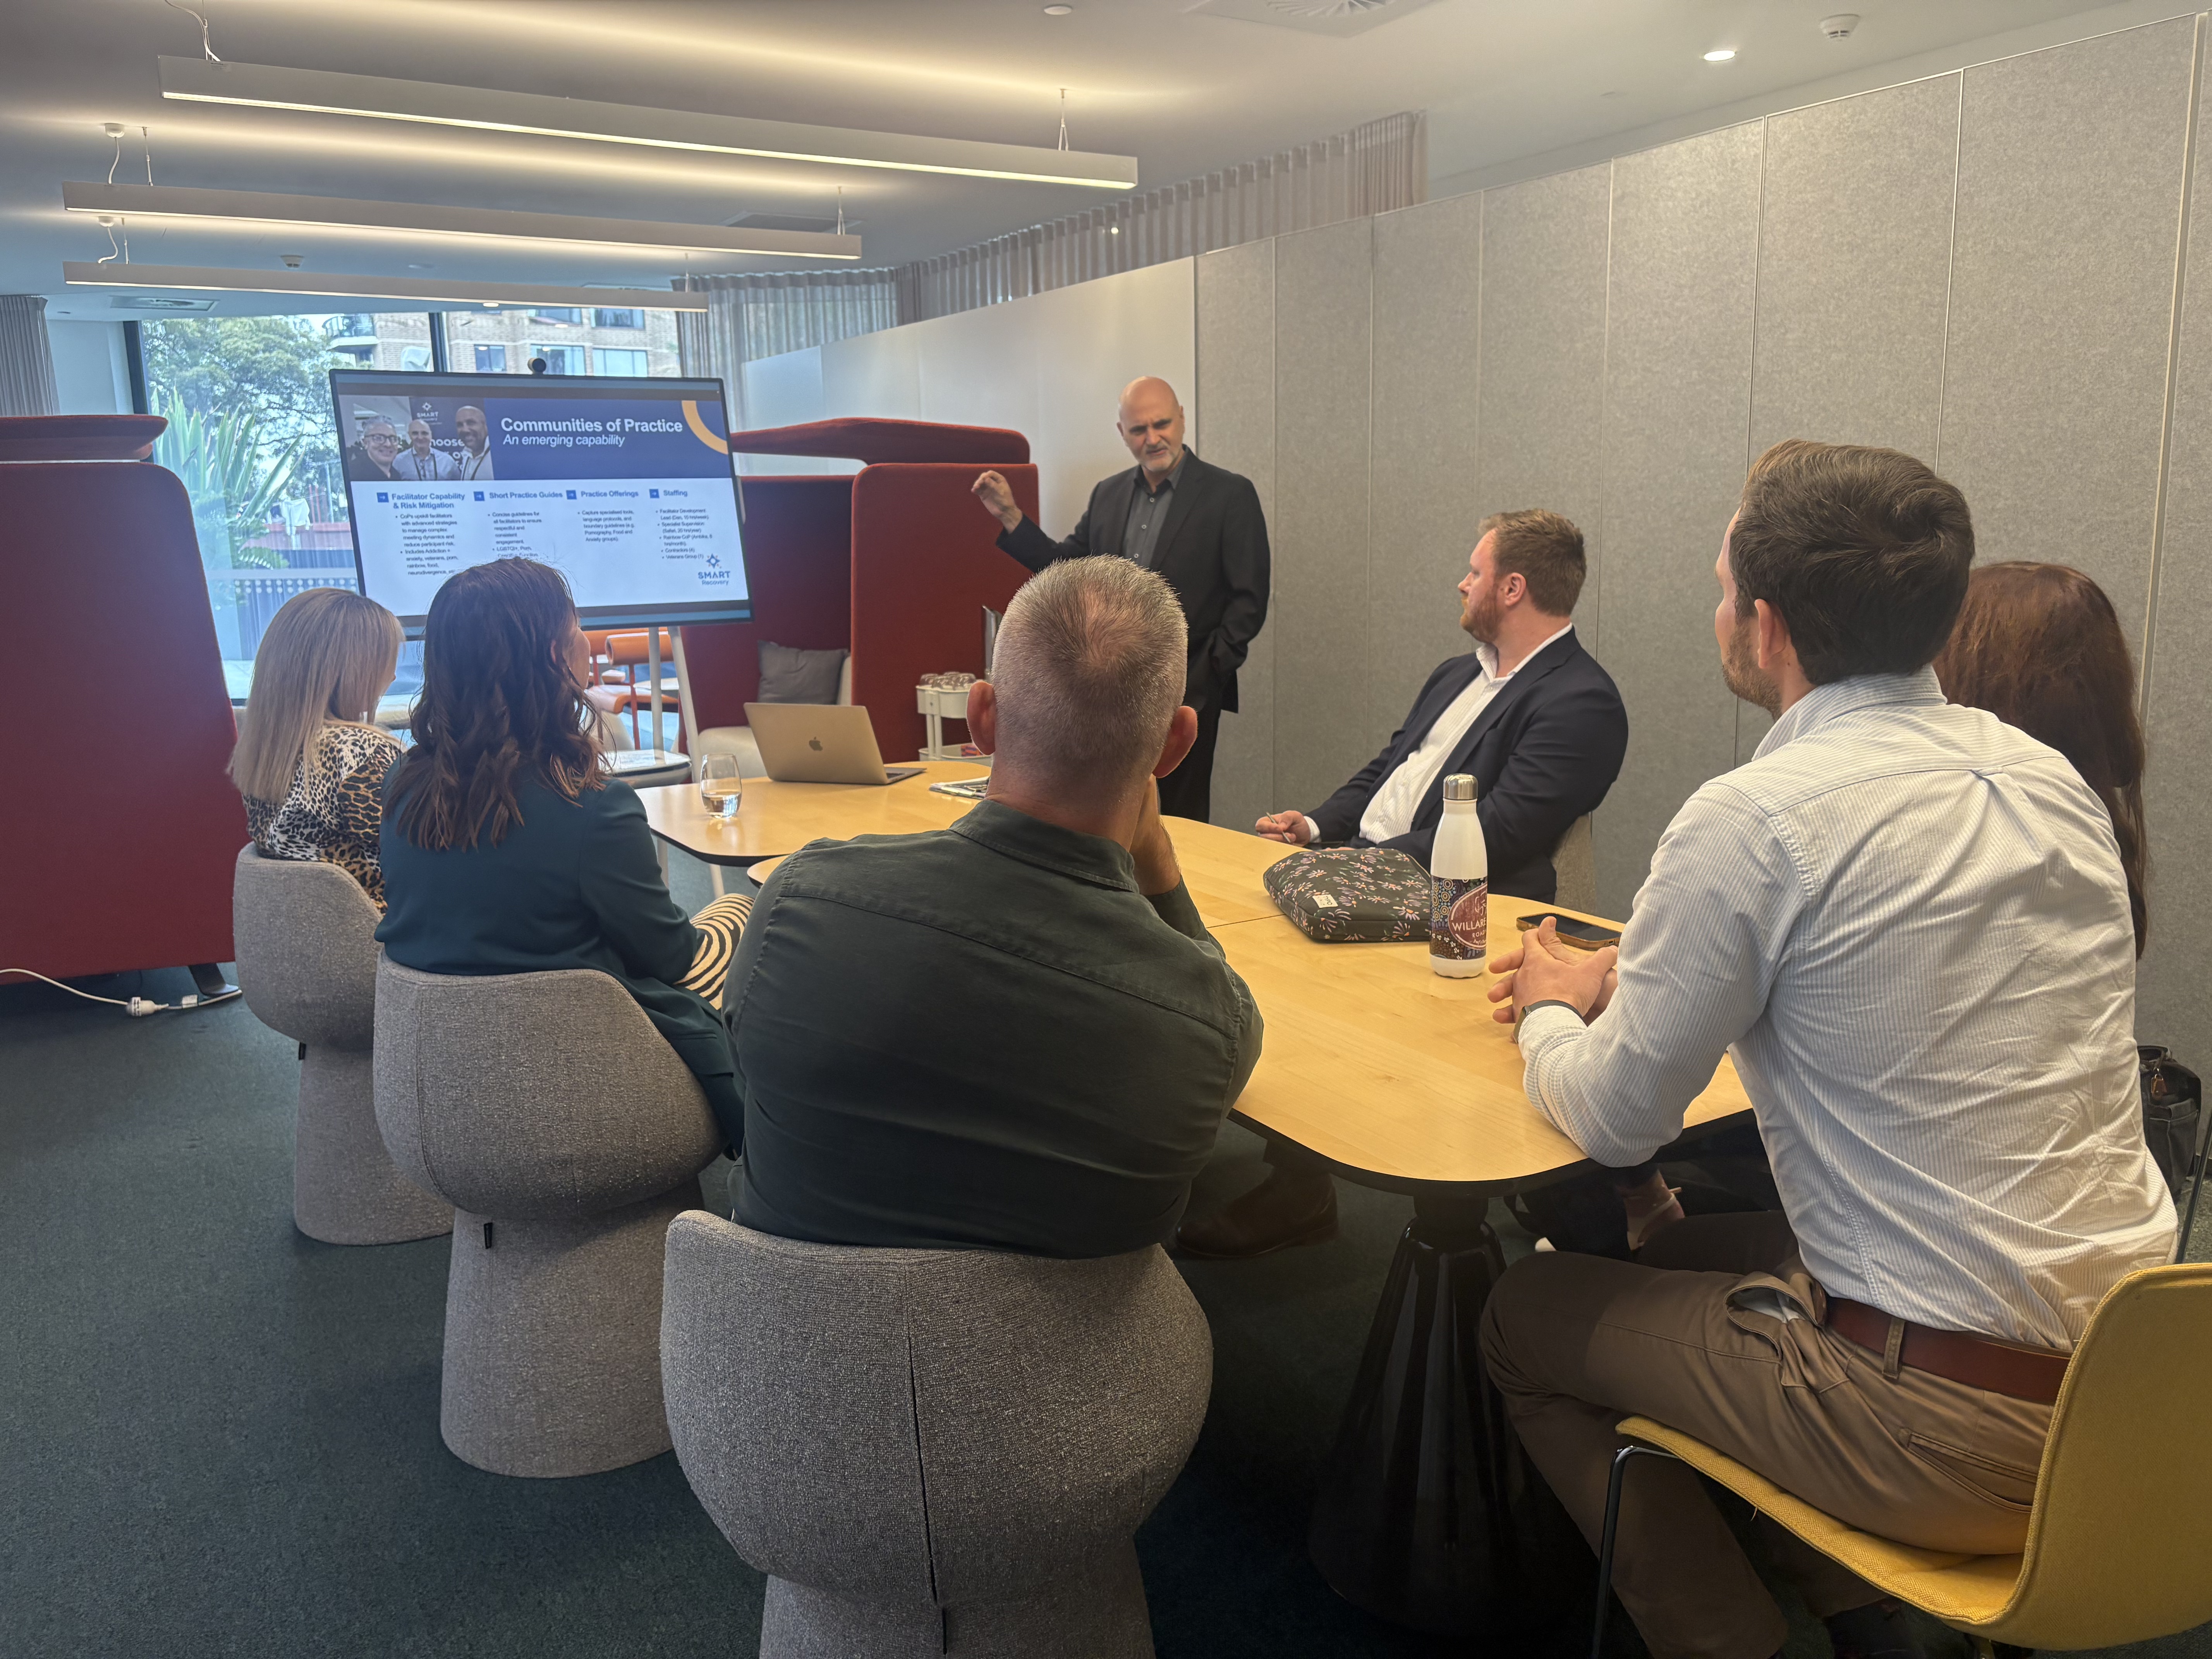
I”m very proud to have joined the board of SMART Recovery Australia with the mission to help people live a life beyond addiction through evidence-based, inclusive and empowering programs.

And no better way to start than with a strategy offsite bringing together fellow directors and the executive team for a day focusing on financial sustainability, AI governance, risk appetite and long-term impact measurement.

I look forward to contributing and applying my experience in board directorship, social impact measurement, AI in the not-for-profit sector, NFP governance, cybersecurity, strategy and leadership.
Security is a social design problem, not a tech one

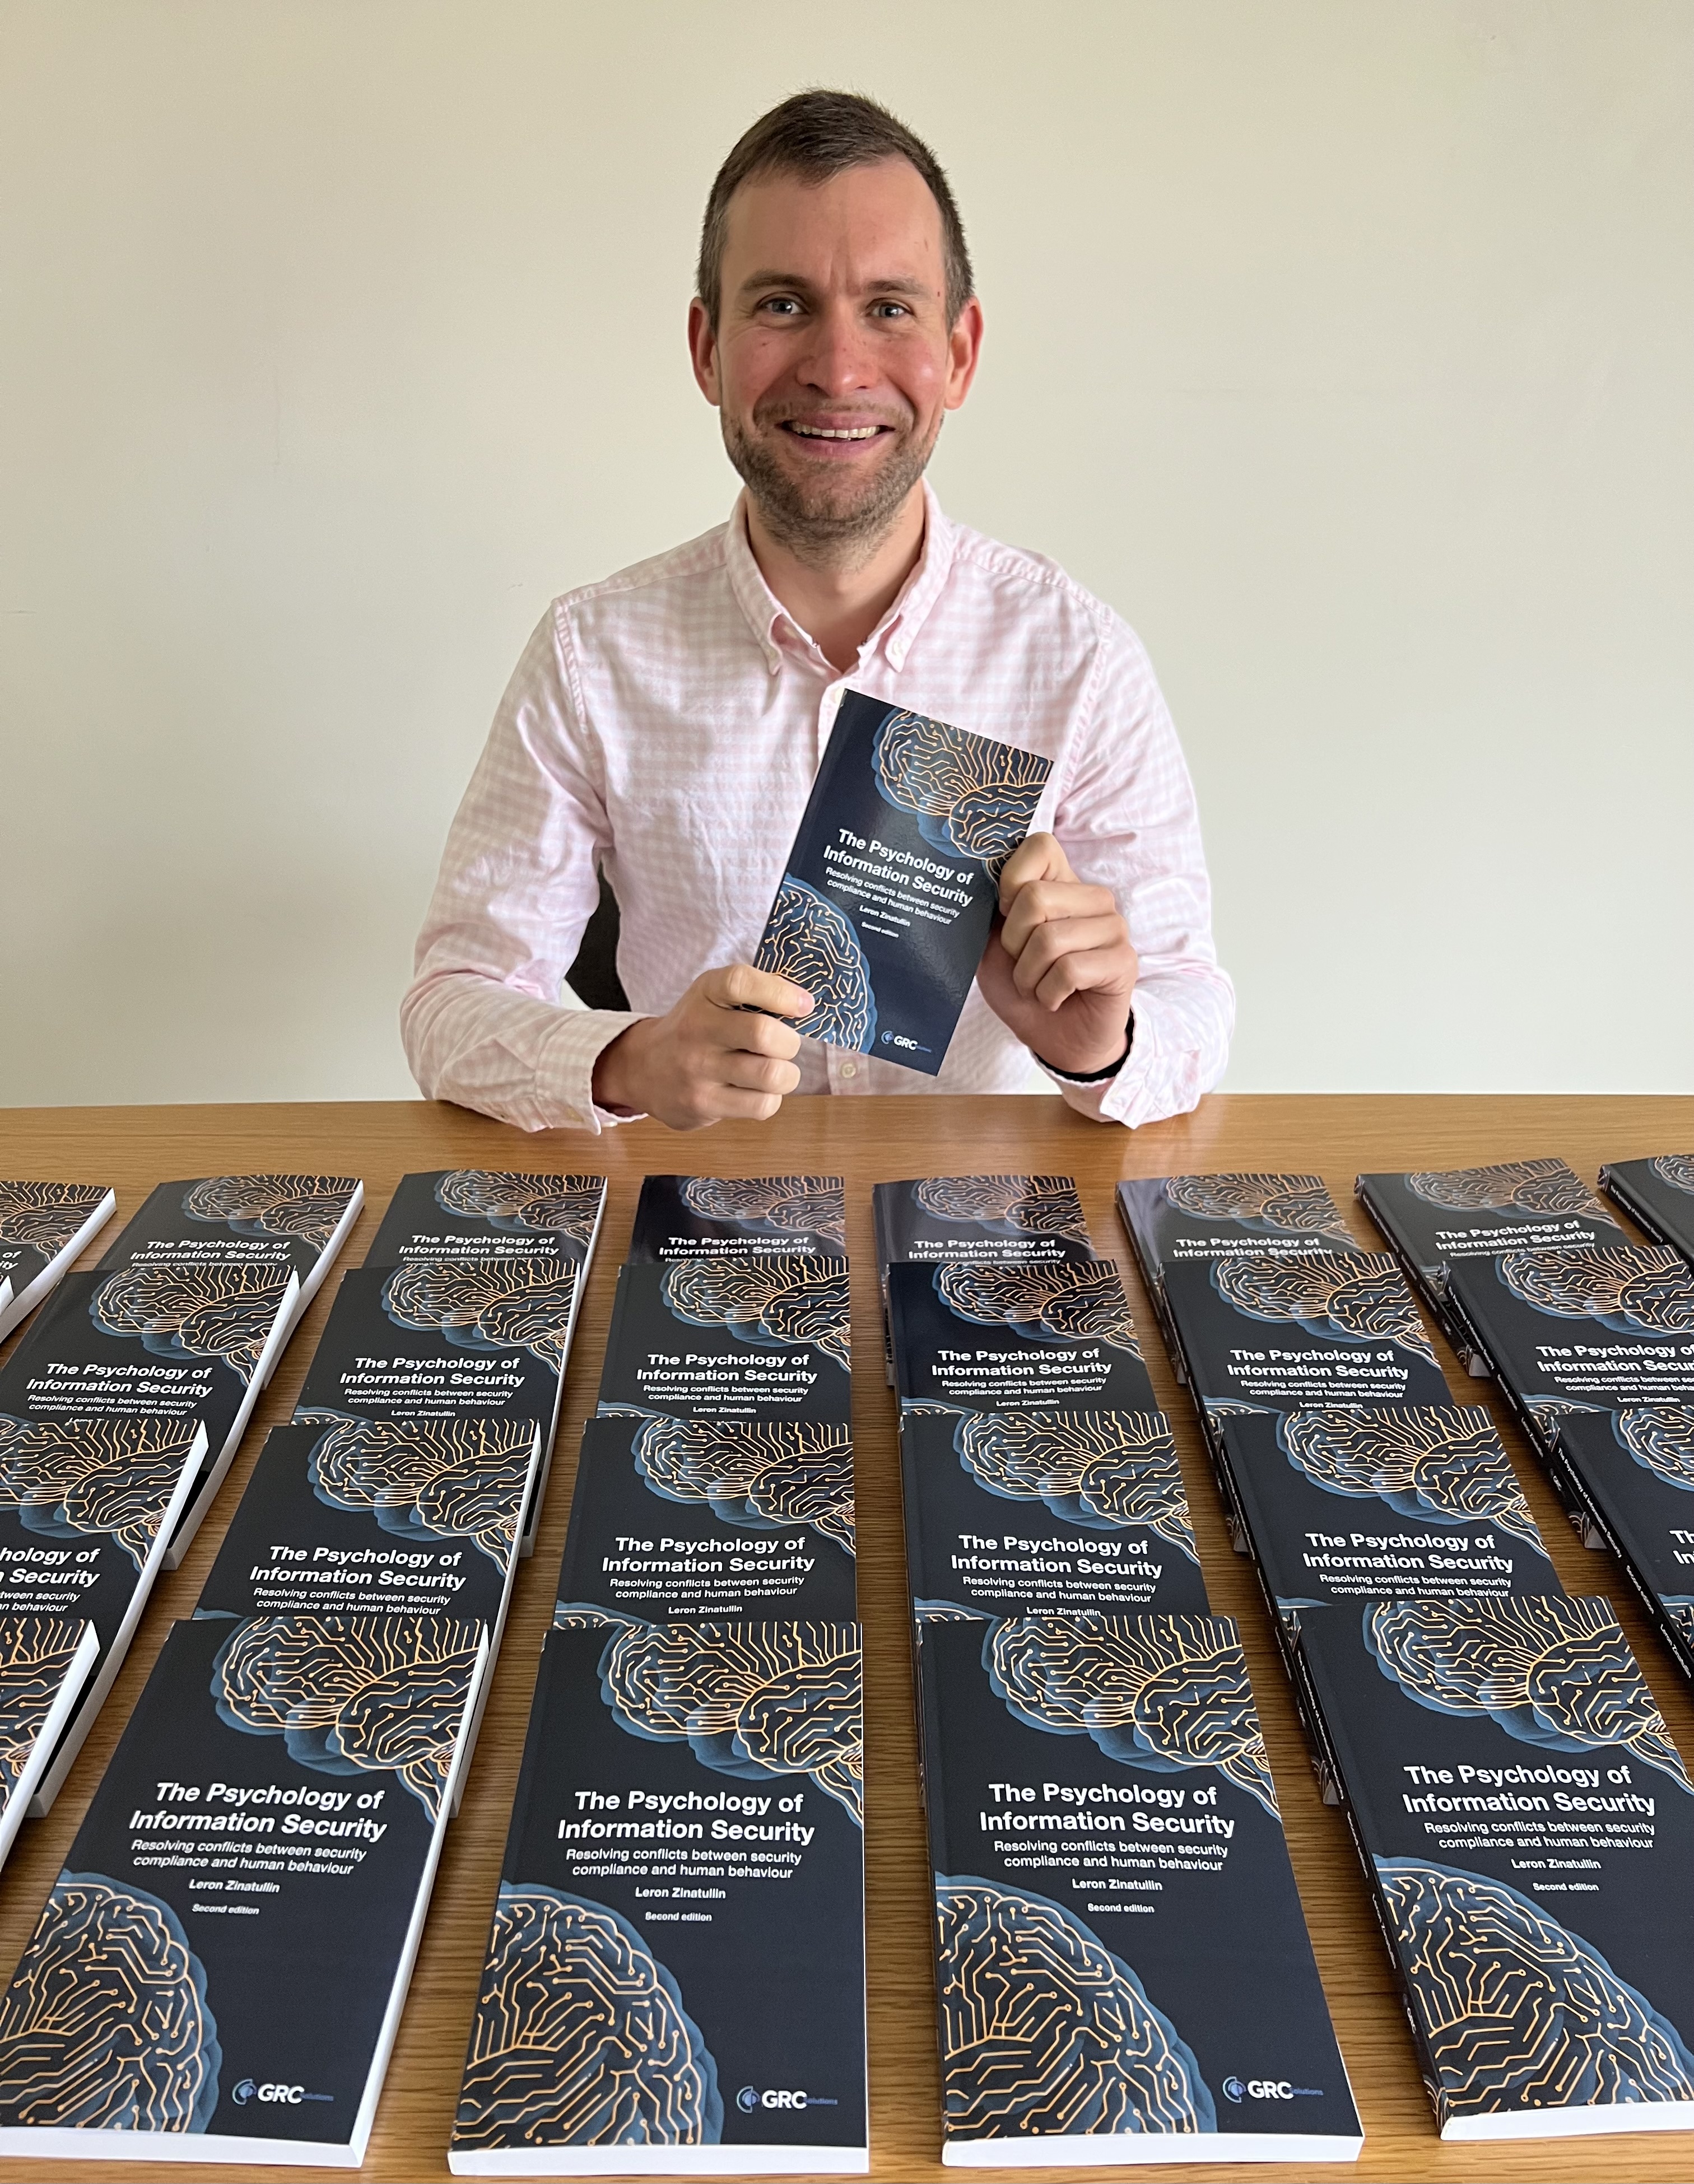
I’m super proud to have written this book. It’s the much improved second edition – and I can’t wait to hear what you think about it.

https://amzn.asia/d/9lr6Sd9

Please leave an Amazon review if you can – this really helps beat the algorithm, and is much appreciated!

AI guardrails and governance

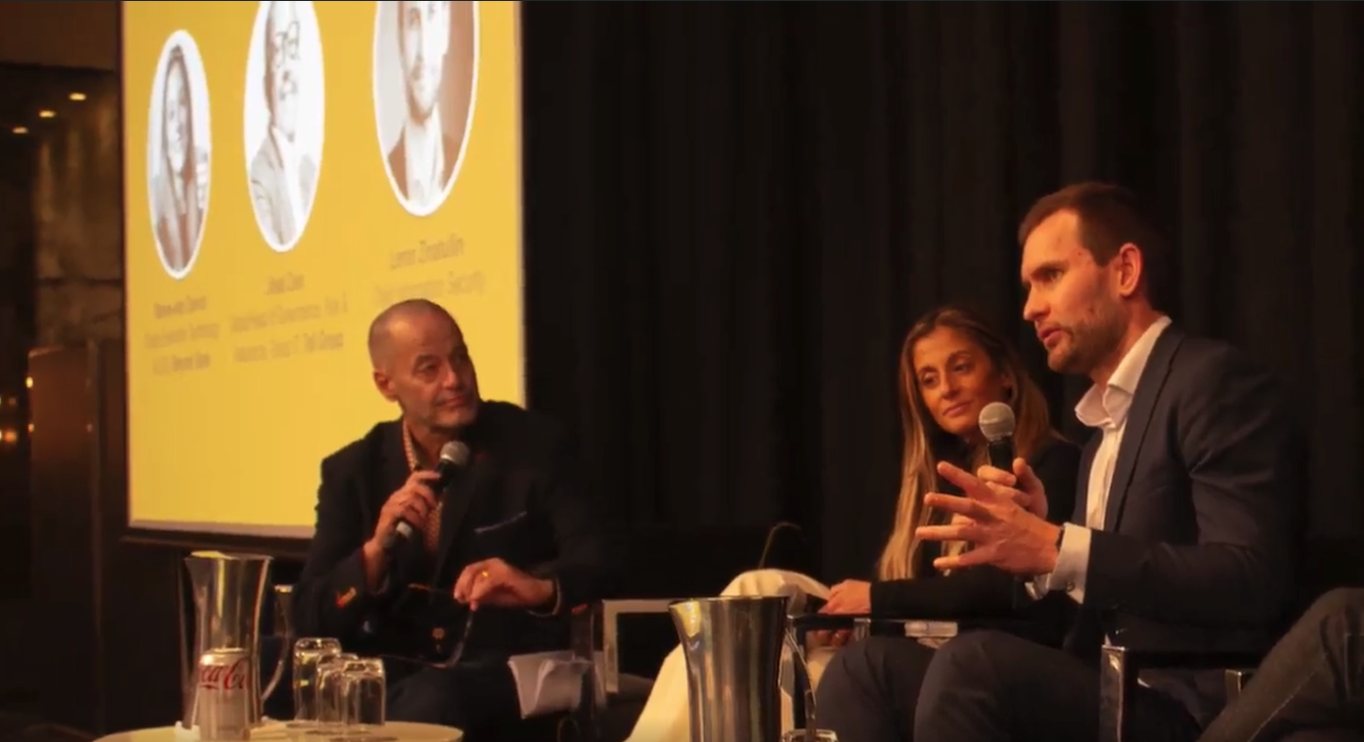
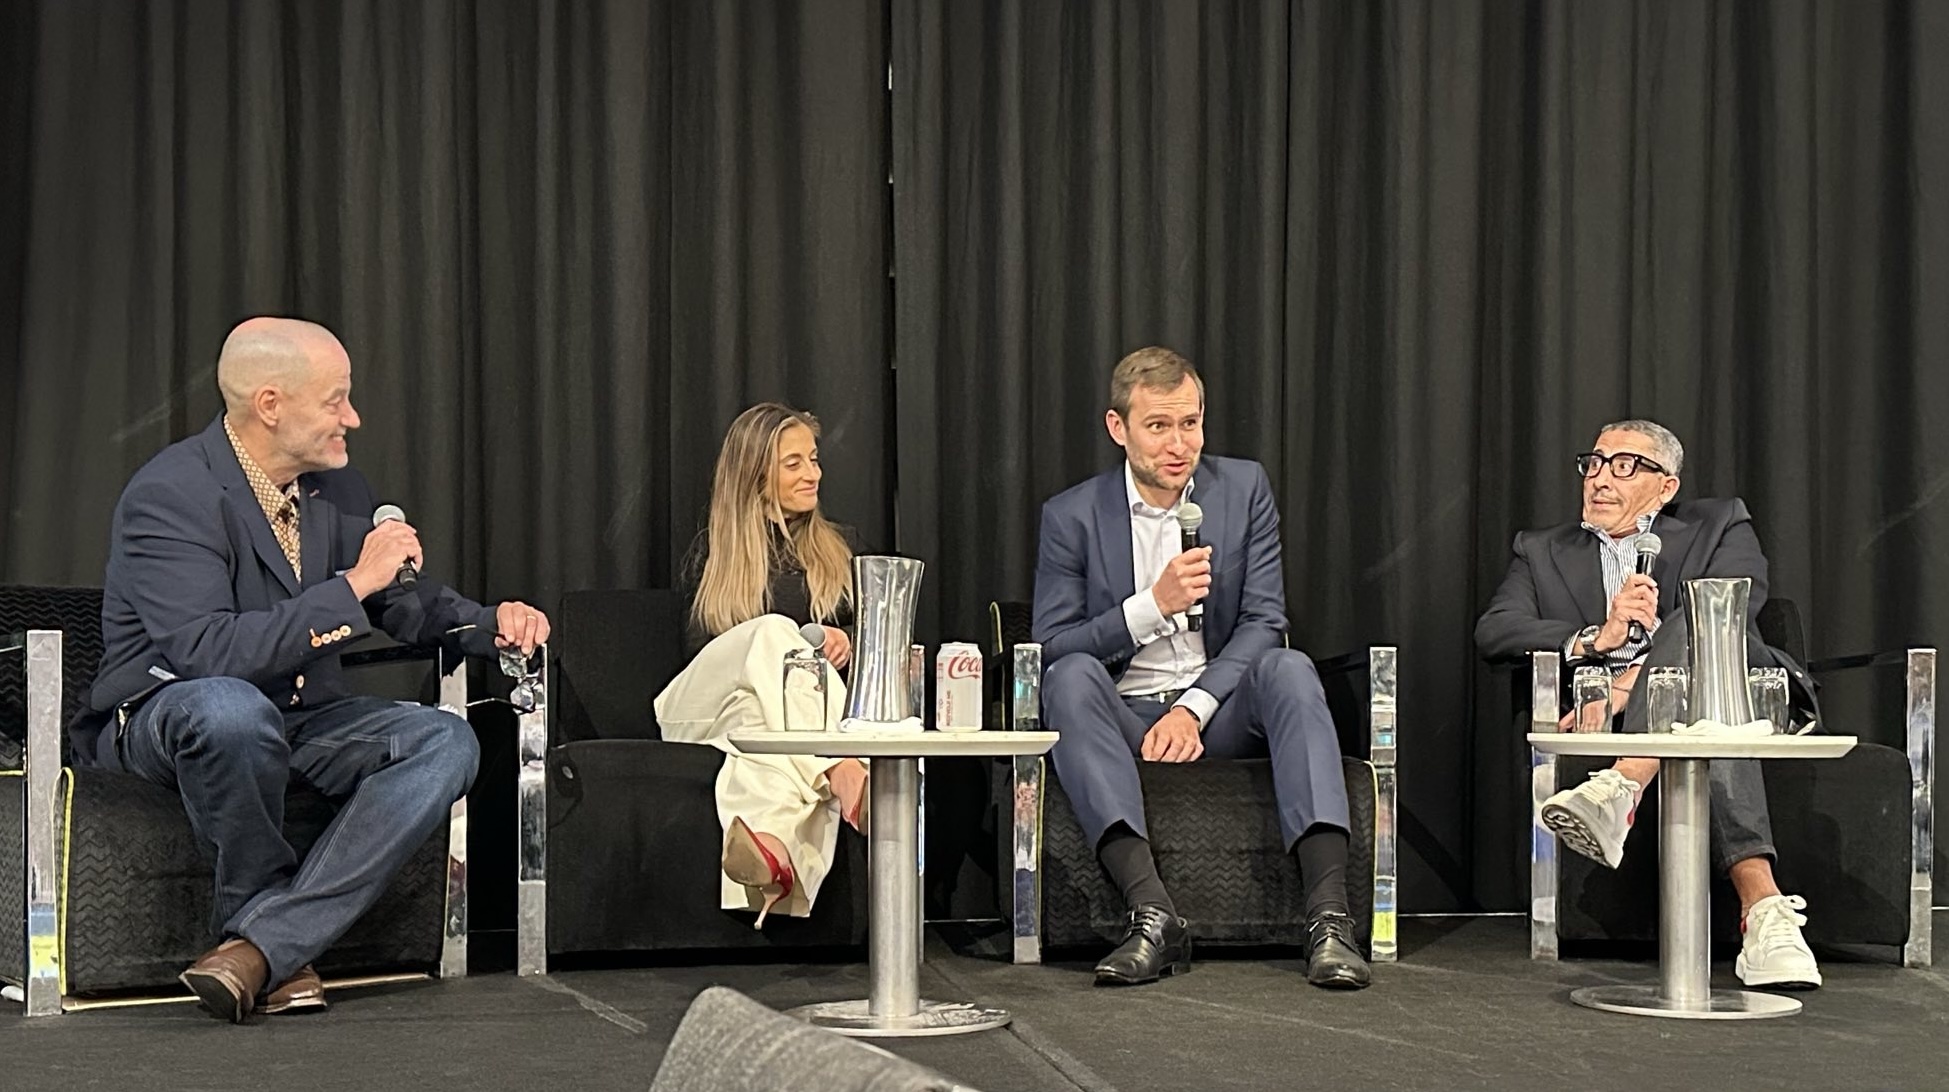
Just wrapped up an engaging panel on AI guardrails where we explored the shifting ground beneath enterprise AI adoption.

The best AI governance starts not with controls, but with culture. When people start asking not just ‘Can we do this?’ but ‘Should we?” that’s when you know you’re on the right path.

Secure by Design is a widely understood concept in cybersecurity, it can be extended to Ethics by Design when building and adopting AI capabilities. Ethical considerations should be embedded from the start, with continuous assurance throughout the lifecycle.

Navigating the endless sea of threats

Cyber security is a relentless race to keep pace with evolving threats, where staying ahead isn’t always possible. Advancing cyber maturity demands more than just reactive measures—it requires proactive strategies, cultural alignment, and a deep understanding of emerging risks.

I had an opportunity to share my thoughts on staying informed about threats, defining cyber maturity, and aligning security metrics with business goals with Corinium’s Maddie Abe ahead of my appearance as a speaker at the upcoming CISO Sydney next month.

More

Board directorship: mindset shift

I had a great week at the AICD’s Company Directors Course learning about governance, risk, strategy, legal environment, financial literacy, performance and achieving board effectiveness.

I particularly liked the interactive discussions and case studies to practice ethical decision making, applying concepts in practice and adopting the director mindset.

More

Volunteering with ISACA

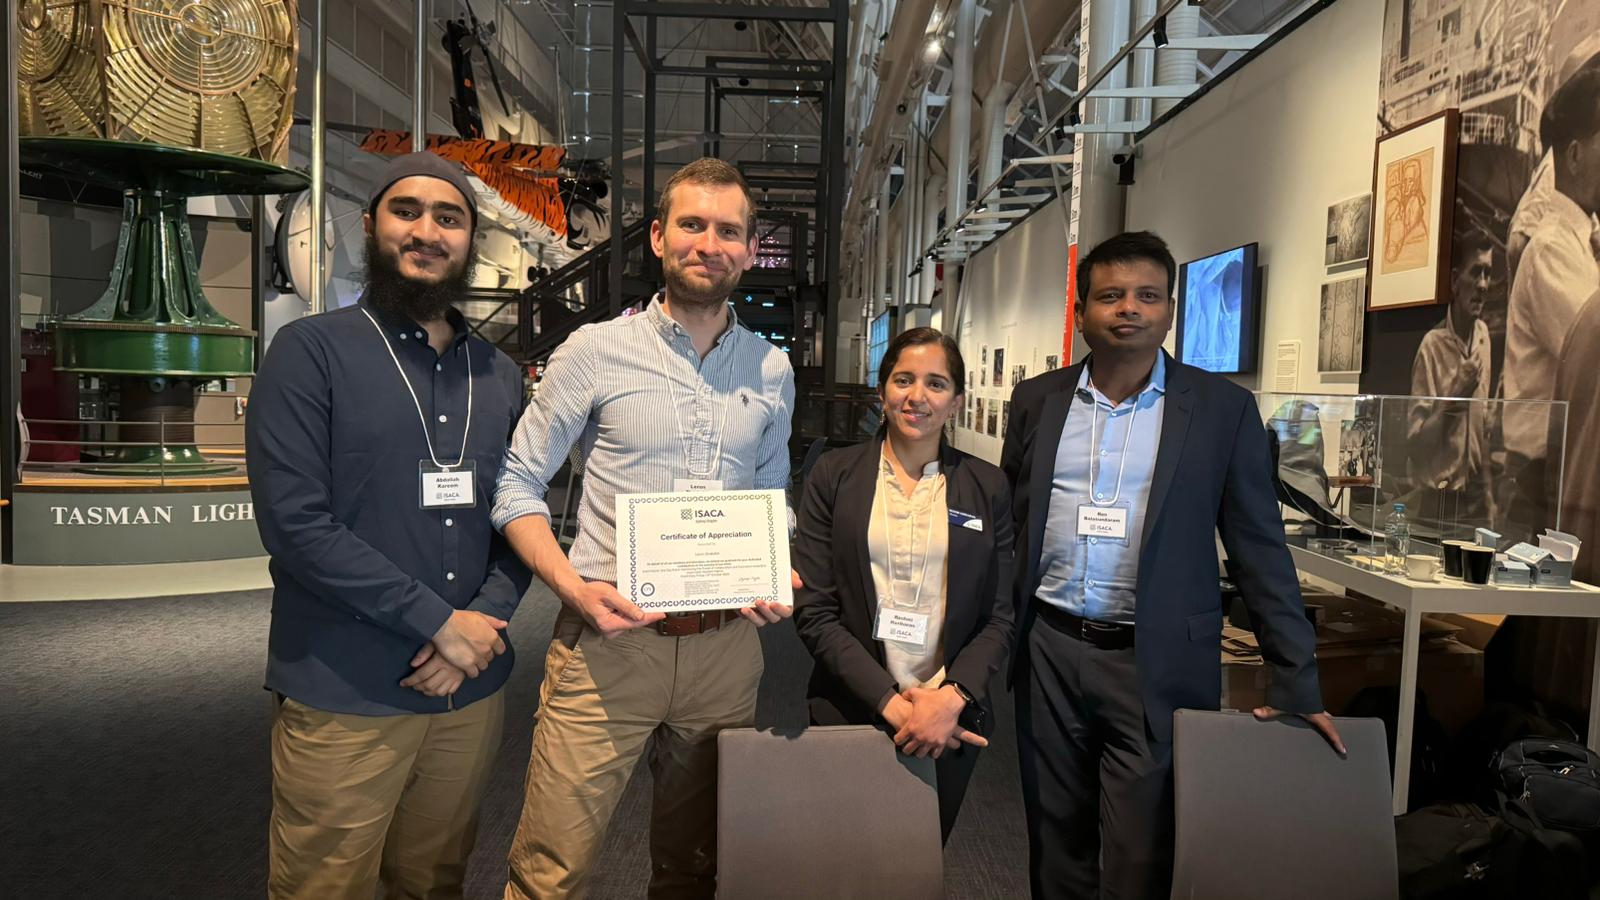
It’s been fantastic to have an opportunity to give back to the community and volunteer with ISACA this year.

The Sydney Chapter hosted a number of professional development events for cyber, risk, governance and IT professionals with a common objective of building digital trust and securing our interconnected world. I had a chance to support these initiatives, ranging from fundraising for a mental health charity to helping organise conferences.

I found this experience incredibly rewarding and made some good friends along the way.

How to achieve SOC 2 Type 2 attestation

As a CISO who recently led an organisation through successful SOC 2 Type 1 and Type 2 audits, I’d like to share some insights and steps to help others on their journey toward SOC 2 attestation.

SOC 2 may not be for everyone (refer to my blog on compliance frameworks), but it can be useful for organisations dealing with sensitive customer data, particularly in SaaS, as it demonstrates a commitment to security, privacy, and data integrity. The journey toward SOC 2 attestation can be complex, but with careful planning and the right strategies, it’s achievable.

More

How to adopt NIST CSF 2.0

CSF 2.0 Functions. Source: NIST

NIST released a new version of the Cybersecurity Framework with a few key changes:

  • It now can be applied beyond critical infrastructure, making it more versatile and straightforward to adopt.
  • It introduces a new core “Govern” function that includes categories from other sections, with increased focus on supply chain risk management and accountability.
  • It highlights synergies with the NIST Privacy Framework.

I often use this framework to develop and deliver information security strategy. Although, other methodologies exist, I find its layout and functions facilitate effective communication with various stakeholder groups, including the Board.

More

Developing effective negotiation skills

Negotiation is a core skill that can make or break your success as a CISO.

While technical expertise is important, it’s equally critical to recognise the value of negotiation skills in cyber security leadership. By developing and applying strong negotiation skills, you’ll be better equipped to lead your organisation in an increasingly complex and challenging cyber security landscape.

I recently completed a negotiations workshop by Filip Hron and highly recommend him as a facilitator and his book ‘Negotiations Evolved’. I particularly appreciate his focus on ethics and value creation.

In this blog, I outline how some of the skills can be applied to the cybersecurity context.

More