ISO 27001 Standard is high-level and provides only basic recommendations on implementation of security controls. This fact gives a security manager in a company a lot of flexibility in choosing particular information security policies.
When making a decision on the how to introduce new security controls to achieve compliance with the ISO 27001 standard, security managers lack a clear process and rely mostly on their past experience.
Such lack of a clear process and guidance from ISO 27001 may result in arbitrary implementation of information security controls, which will collide with the core business activities of users in the company.
This article presents a scenario of such implementation and provides specific examples of how those controls may affect users’ behaviour.
The company
Scrooge Bank is a global financial services firm, offering a range of solutions, including asset management, strategic advice, money lending, and risk management to clients in more than 100 countries.
From the organisational structure standpoint, Scrooge Bank consists of three departments in the business unit and three departments in the support unit.

The Chief Information Security Officer (CISO) reports directly to the Compliance and Risk Manager, and is responsible for ensuring legal and regulatory compliance, data loss prevention activities, and security incident management.
A decision taken by the CISO affects the whole organisation, including the analyst in the Investment Banking Department.
The business process
An analyst is a typical role in Scrooge Bank. He is involved in various business activities during the week.

On a weekly basis the analyst receives information from the client. There are several ways he can obtain this data: it might be copying information on a USB stick during a face-to-face meeting, or via e-mail as an attachment.
There are instances when the information received was exported from the client’s proprietary software products, which are not directly compatible with the widely used packages, such as Microsoft Excel, used by the analyst. Hence, the analyst was forced to use special data extracting software to access the data.
On a regular basis, the analyst needs search for additional information on the Internet to prepare a report for the client.
Once a week he runs data analysis software to analyse the potential risk for the client. This software is very powerful and commonly used in Scrooge Bank. However, it analyses vast amounts of data and consumes a lot of CPU time and memory.
When a report is finalised, the analyst exports it on a USB stick in order to present it to the Client.
Compliance requirements, controls implementation and impact on users’ behaviour
In order to more effectively protect against malicious code, Scrooge Bank decided to implement the ISO 27001 Standard. According to chapter 10.4.1 of the standard, “Controls against malicious code”, “detection, prevention, and recovery controls to protect against malicious code and appropriate user awareness procedures should be implemented.”
The ISO 27001 Standard suggests that “Precautions are required to prevent and detect the introduction of malicious code and unauthorized mobile code. Software and information processing facilities are vulnerable to the introduction of malicious code, such as computer viruses, network worms, Trojan horses, and logic bombs. Users should be made aware of the dangers of malicious code. Managers should, where appropriate, introduce controls to prevent, detect, and remove malicious code and control mobile code.”
The Standard also recommends the particular security controls to be implemented in order to protect against malicious code. In order to address the described issues and ensure formal compliance with the Standard, the security manger decides on the following implementation of the security controls. The following table also shows examples of how users in various departments of the company could potentially violate security policy, because it prevented them from perform their main business tasks
| ISO 27001 control implementation guidance | Context | Behavioral impact |
| Establishing a formal policy prohibiting the use of unauthorized software | Scrooge Bank’s CISO came up with a policy document, outlining a list of authorized software, which can be installed on users’ workstations according to principle of least privilege – users should only have access they require to perform their day-to-day activities and no more.Each department contributed to the policy, submitting a list of software which is essential to carrying out tasks by employees in this department.After finalizing this list, all users were denied access to install any new software without written permission from CISO. | John is performing an analysis of the company for the client. The deadline is fast approaching but there is still a lot of work to be done.The night before the deadline, John realizes that in order to finalize his analysis he requires a special data analysis tool, which was not included in the list of authorised software. He’s also unable to install it on his workstation, because he doesn’t have the required privileges to install new software.Getting the formal written approval from the CISO is not feasible, because it is going to take too long.John decides to copy sensitive information required for the analysis on his personal laptop using a USB flash drive to finish the analysis at home, where he can install any software he wants.
John understands the risk but he also wants to get the job done in order to avoid missing the deadline and get good performance review at the end of the year. Unfortunately he leaves his bag with the USB stick in the taxi on the way back home. He never tells anyone about this incident to avoid embarrassment. |
| Establishing a formal policy to protect against risks associated with obtaining files and software either from or via external networks, or on any other medium, indicating what protective measures should be taken | In order to prevent obtaining files and software either from or via external networks, or on any other medium, CISO established a policy restricting use of file sharing websites and limited access to CD/DVD and USB flash drives.According to the policy, if a user wants to obtain a specific file from the internet or from an external device, he has to file a written request to his manager, who will decide if this file is essential to perform his duty. After management’s approval, the Information Security Department employee will process this request, downloading this file or copying it from the external medium, using a special isolated PC with thorough antivirus checks. | Mary works closely with a client to finalise her report on risk analysis for an international energy company.She works directly with the CFO of this company who is very impatient and busy with other tasks.Mary doesn’t want to annoy him, because he may complain directly to her line manager and she can be disciplined, because this is a very important client, which brings millions to the company.The client is not aware of the new policy which was recently implemented by the CISO of Scrooge Bank and uploads important pieces of information to the file sharing website in form of the encrypted archive, because it is too big to transfer over the corporate e-mail.
He communicates the password to Mary over the phone and sends her the link. Mary was scared to explain the new policy to the client and right now she is unable to access this file to finalise her report. She decided to go to internet café during her lunch break and download the important file from there, understanding the risk, but realising that getting all necessary approvals may take way too long. At the internet café she not only downloads the encrypted file but also opens it on the local machine to check its integrity to avoid returning back, because she won’t have any breaks later in a day. Because the internet café is far from the office and she didn’t have her lunch yet, she hurries and forgets to delete the decrypted file from the machine in the internet café. She realizes her mistake when she’s back in the office but thinks that it is not a big deal and nothing bad can happen. |
| Conducting regular reviews of the software and data content of systems supporting critical business processes; the presence of any unapproved files or unauthorized amendments should be formally investigated | The CISO established a procedure of monthly checks of users’ workstations for presence of unauthorized data and software.If such data or software were be found, the employee would be given a warning. After three warnings he would be fired because of non-compliance with the security policies of the company. | Juliet uses data and files in her analysis, which she obtained from various sources, and she is not sure if it is approved or not. She’s afraid to clarify this situation with the CISO, because she’s afraid to be fired.In order to avoid being caught using such files, she decided to store this information on her personal laptop.But after a while she realised that it takes too long to copy and delete data from her corporate PC to personal laptop and vice versa, hence she decided to process all the information, including sensitive, on her personal computer.As always, she took her laptop with her on holiday, but it was stolen in a public place |
| Installation and regular update of malicious code detection and repair software to scan computers and media as a precautionary control, or on a routine basis; the checks carried out should include:1) checking any files on electronic or optical media, and files received over networks, for malicious code before use;2) checking electronic mail attachments and downloads for malicious code before use; this check should be carried out at different places, e.g. at electronic mail servers, desk top computers and when entering the network of the organization;3) checking web pages for malicious code; | The CISO implemented antivirus software on each workstation and configured automatic daily full machine scans to ensure that no malicious code was present on workstations.The CISO also established a formal policy, which requires every employee to run manual antivirus checks before opening e-mail attachments and using electronic or optical media. | Robin is a derivatives trader. Time and efficiency are critical success factors for him.Robin carries out thousands of deals per day using the electronic terminal on his PC.Introducing a new antivirus software slowed down his workstation performance, especially during full machine scans. This directly affects his job performance – he is unable to act as fast as before and misses many valuable opportunities.Robin understands the risk of malicious software but he is also frustrated by his inability to work as efficiently as before.
He finds a way to manually disable the antivirus agent on his PC. During the search for information on the internet he accidentally accesses a spoofed website and introduces a Trojan on his workstation. With no antivirus software to prevent malware from stealing sensitive information from his PC, it becomes a victim. |
| Defining management procedures and responsibilities to deal with malicious code protection on systems, training in their use, reporting and recovering from malicious code attacks | The CISO developed a set of procedures to prevent malicious code.According to these procedures, each head of a department is responsible for preventing malicious code attacks in his/her department.The CISO wants to raise awareness, train and educate users how to record, prevent and recover from malicious code attacks. He decided to run regular monthly workshops to achieve these goals. | Employees of the organization not showing up for the workshops and not paying attention, because CISO’s efforts driven mainly by corporate directives, rather than security needs. Moreover, programme is the same for everyone, regardless of roles and responsibilities and it doesn’t change year after year. |
| Preparing appropriate business continuity plans for recovering from malicious code attacks, including all necessary data and software back-up and recovery arrangements | The CISO developed appropriate plans identifying critical information assets, and gathering input from asset owners.The CISO also performs data back-ups on a regular basis and maintains recovery arrangements. | Scrooge Bank recently acquired a small company and all its IT infrastructure.Because the CISO failed to update the business continuity plan in a timely manner to include recent changes, the company was very inefficient to recover from a malicious code attack.Furthermore, employees weren’t familiar with what they should do in this situation due to a lack of education and involvement during plan testing. |
| Implementing procedures to regularly collect information, such as subscribing to mailing lists and/or checking web sites giving information about new malicious code | The CISO assigned regular collection of information about new malicious code to a member of Information Security Department in addition to the other tasks he performs. | An employee of Information Security Department receives too much information daily from antivirus vendors’ websites and mailing lists, so he started to ignore it and focus more on his main tasks (i.e. handling information security incidents) |
| Implementing procedures to verify information relating to malicious code, and ensure that warning bulletins are accurate and informative; managers should ensure that qualified sources, e.g. reputable journals, reliable Internet sites or suppliers producing software protecting against malicious code, are used to differentiate between hoaxes and real malicious code; all users should be made aware of the problem of hoaxes and what to do on receipt of them | The CISO wants to raise awareness of the employees on the issue of hoaxes.He decided to run regular monthly workshops to achieve this goal. | People don’t attend information security awareness training workshops, because they scheduled at the same day as an important meeting with the client. |
The table shows examples that regardless of the fact that the CISO developed a set of information security polices and implemented controls to ensure compliance with ISO 27001 Standard, users managed to find workarounds which negatively affected the company as a whole. In each and every case users violated security policy in in order to accomplish their main business tasks.
Additional security controls, which were added by the CISO, not only introduced additional cognitive burdens on the analyst, but also placed obstacles preventing him from performing his core business tasks.
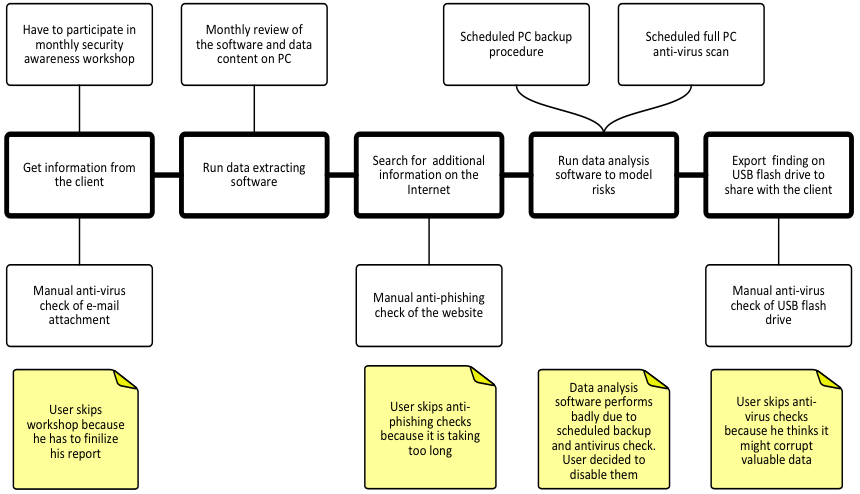
For example, the information security awareness training workshop was scheduled at the same day that the analyst has an important meeting with the client and he have to skip it in order to meet his deadline. Additionally, he managed to shut down the antivirus agent on his workstation because scheduled manual antivirus checks consume too many resources, which are needed to run his risk simulation and analysis software. The analyst also skips manual antivirus and anti-phishing checks either because they are too time consuming or because he is worried about the integrity of the data.
This chapter presented a scenario of a particular realistic implementation of security controls, which can lead to in huge numbers of collisions between security and business tasks.
This scenario emphasises the importance of making users part of the system when implementing security controls.