Security failures are rarely just a technology problem. They’re a design problem – a mismatch between how controls are built and how people actually work.
That was my message keynoting at CIO Leadership Live.
AI has amplified the security fundamentals.
☑️ Defaults beat persuasion: passkeys by default, automatic updates, SSO. The secure choice should be the easiest choice. ☑️ Shadow AI is a friction signal, not a compliance failure. If people are pasting data into unapproved chatbots, your sanctioned path is too slow. Give them a fast, safe alternative. ☑️ Build trust, not fear. Blameless reviews and visible leadership create the psychological safety people need to report incidents early.
The CIOs who win with AI won’t be the ones with the strictest rules but the ones whose guardrails make the secure way the easy way.
I had the pleasure of delivering a guest lecture on developing and implementing a cybersecurity strategy to students at the School of Information Systems and Technology Management, UNSW.
A security strategy is a set of decisions about what you will and won’t prioritise, made under real constraints – budget, headcount and a threat landscape that doesn’t wait for your roadmap to catch up.
Strategy starts with the business. If you can’t explain your security priorities in terms of what the organisation is trying to achieve, you won’t get the backing.
With AI, the fundamentals are still important, but the timelines are now compressed.
Thank you UNSW for the invitation, and to the students for the great discussion. This cohort is entering the field at a very interesting moment.
I enjoyed talking to students completing their Global MBA and MSc in Digital Transformation with the University of Hull Online about human-centered approaches to cyber security.
My lecture helped reinforce the idea that cyber security is a socio-technical challenge that has deep behavioural contingencies.
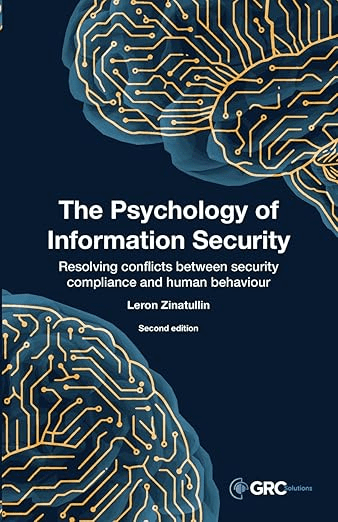
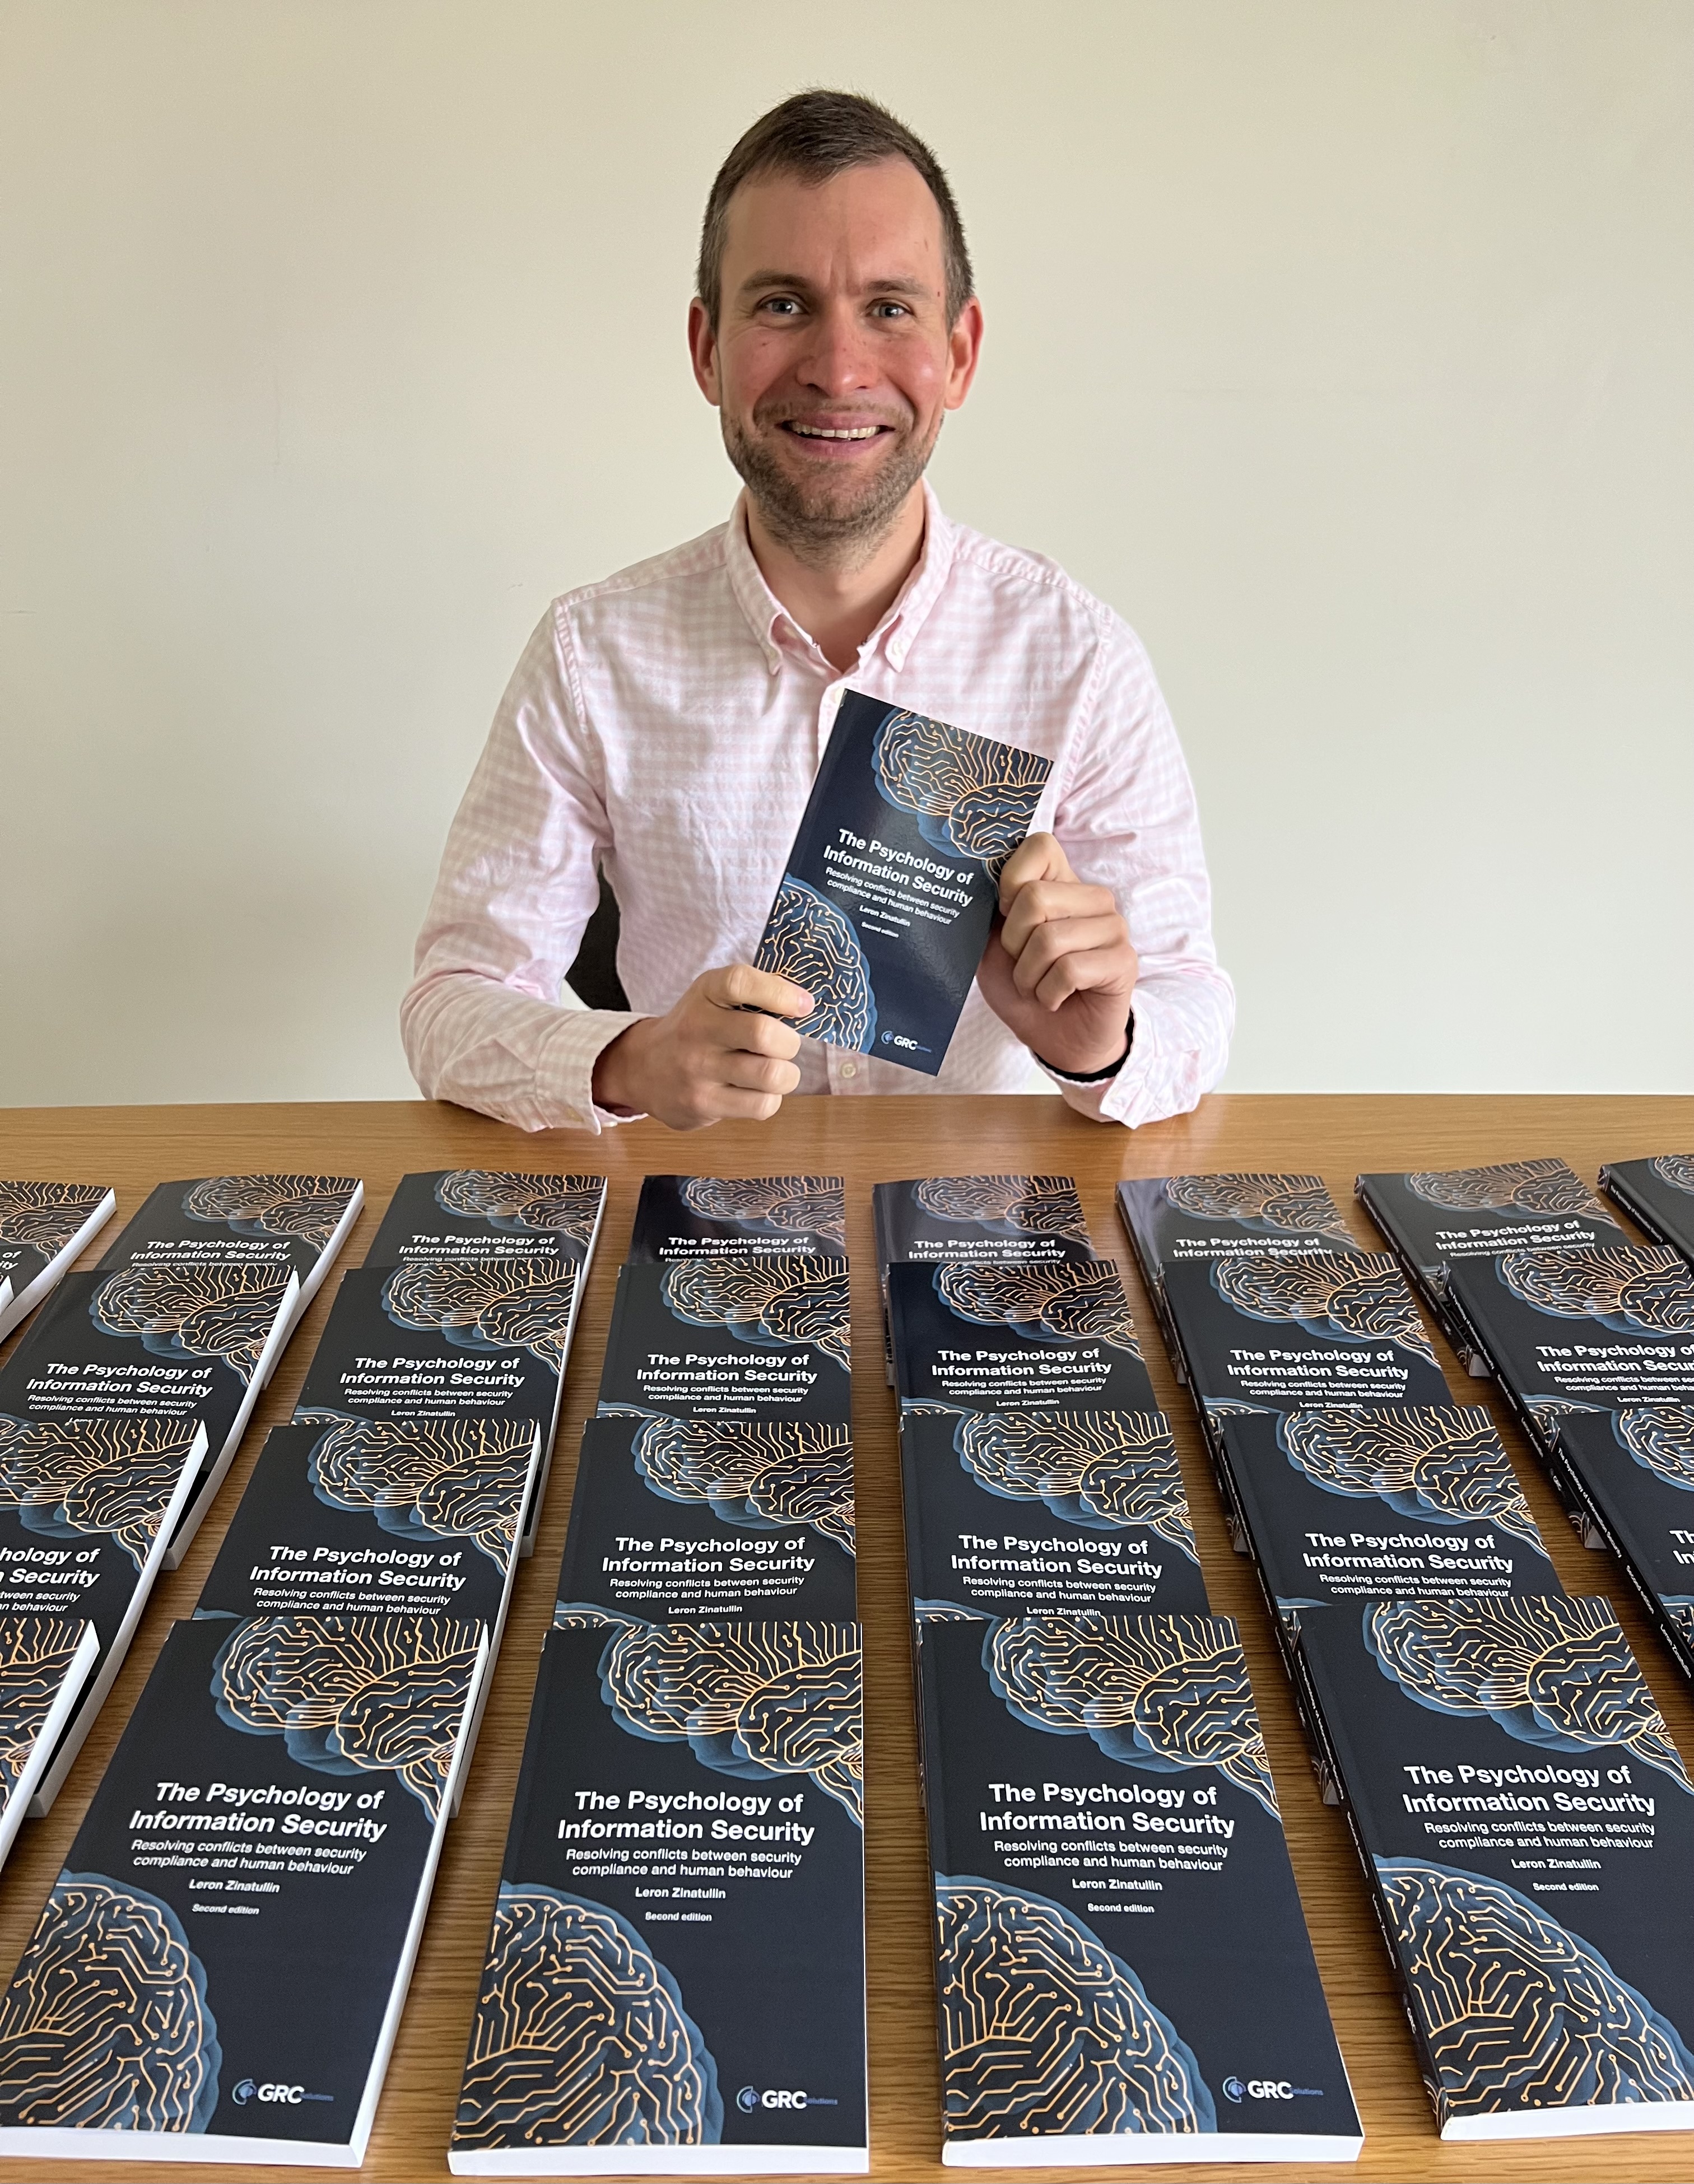
Cyber is a business risk and I’m glad it’s increasingly featured in business degree curriculums beyond computer science. My book, the Psychology of Information Security, helps bridge the gap between organisational and cyber strategy.
For about a decade, our industry has had a favourite phrase: people are the weakest link. I made the opposite case – that the people we’ve been blaming are the most capable security asset we have, and we’ve spent that decade building systems that fight them instead of fit them.
The talk covered why training and punishment don’t work, why every workaround is actually free user research, and how you design your way to secure behaviour by making the secure path the easy path. And of course, where AI fits into all of it.
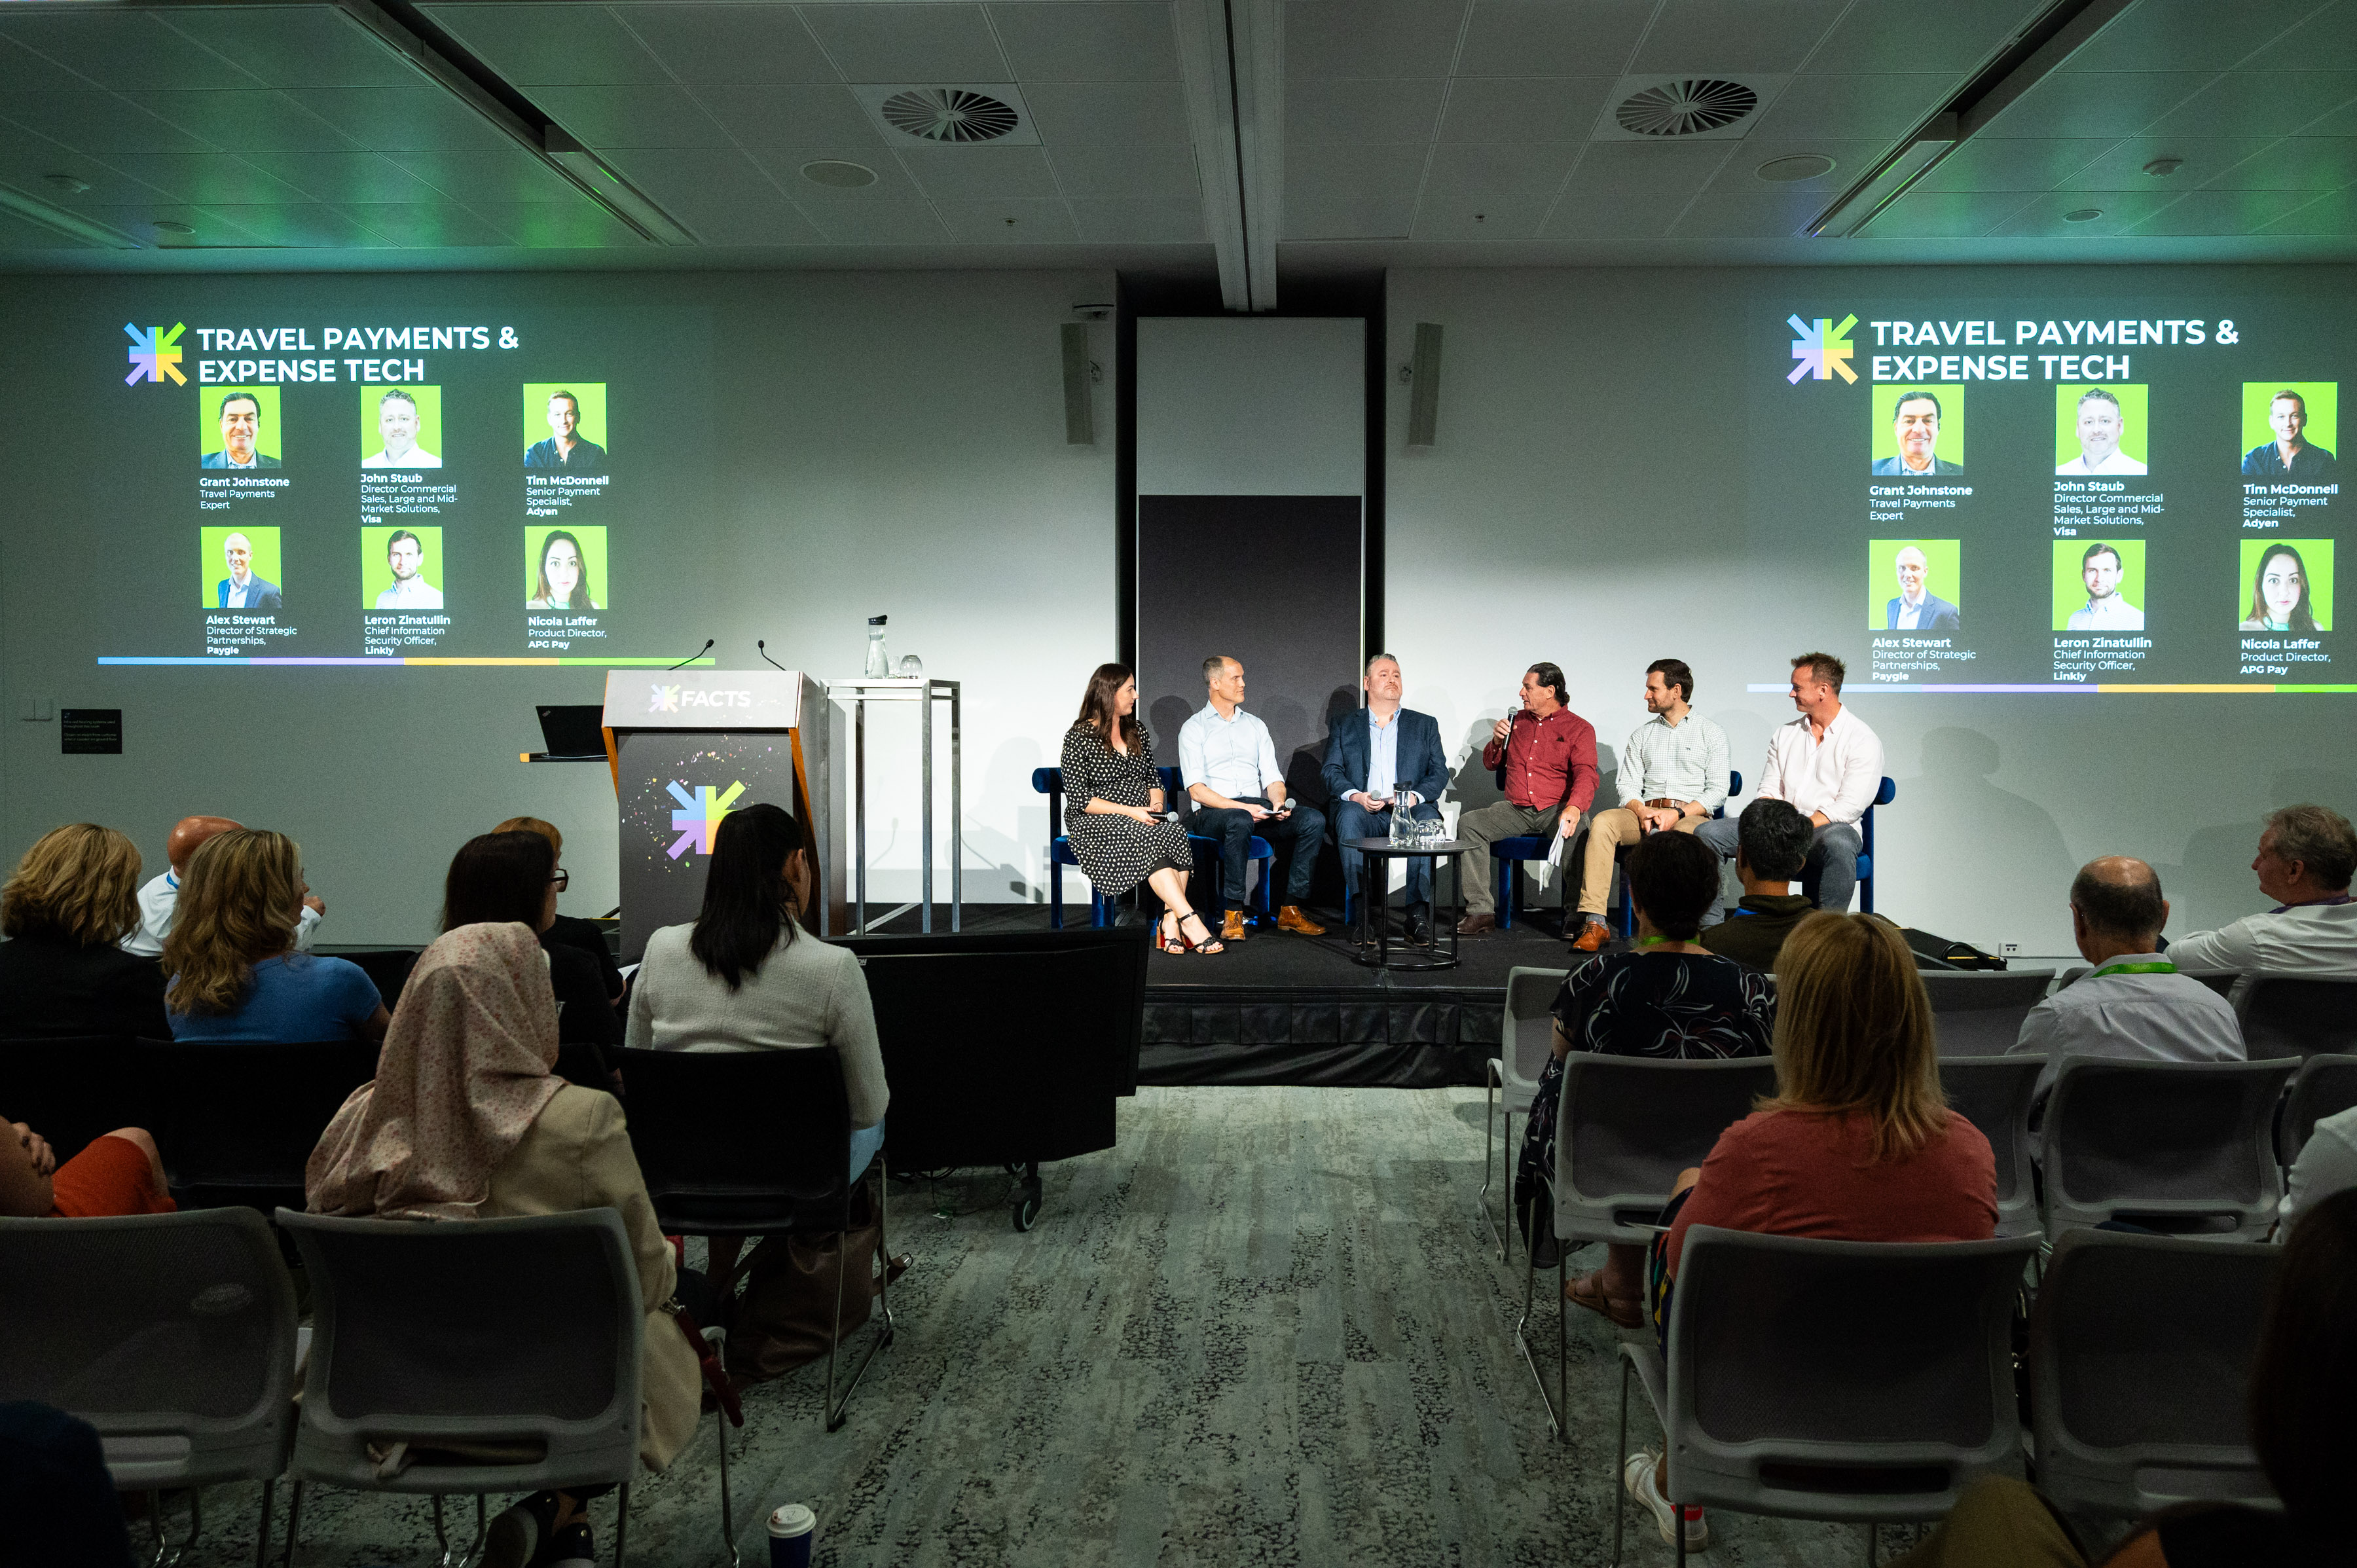
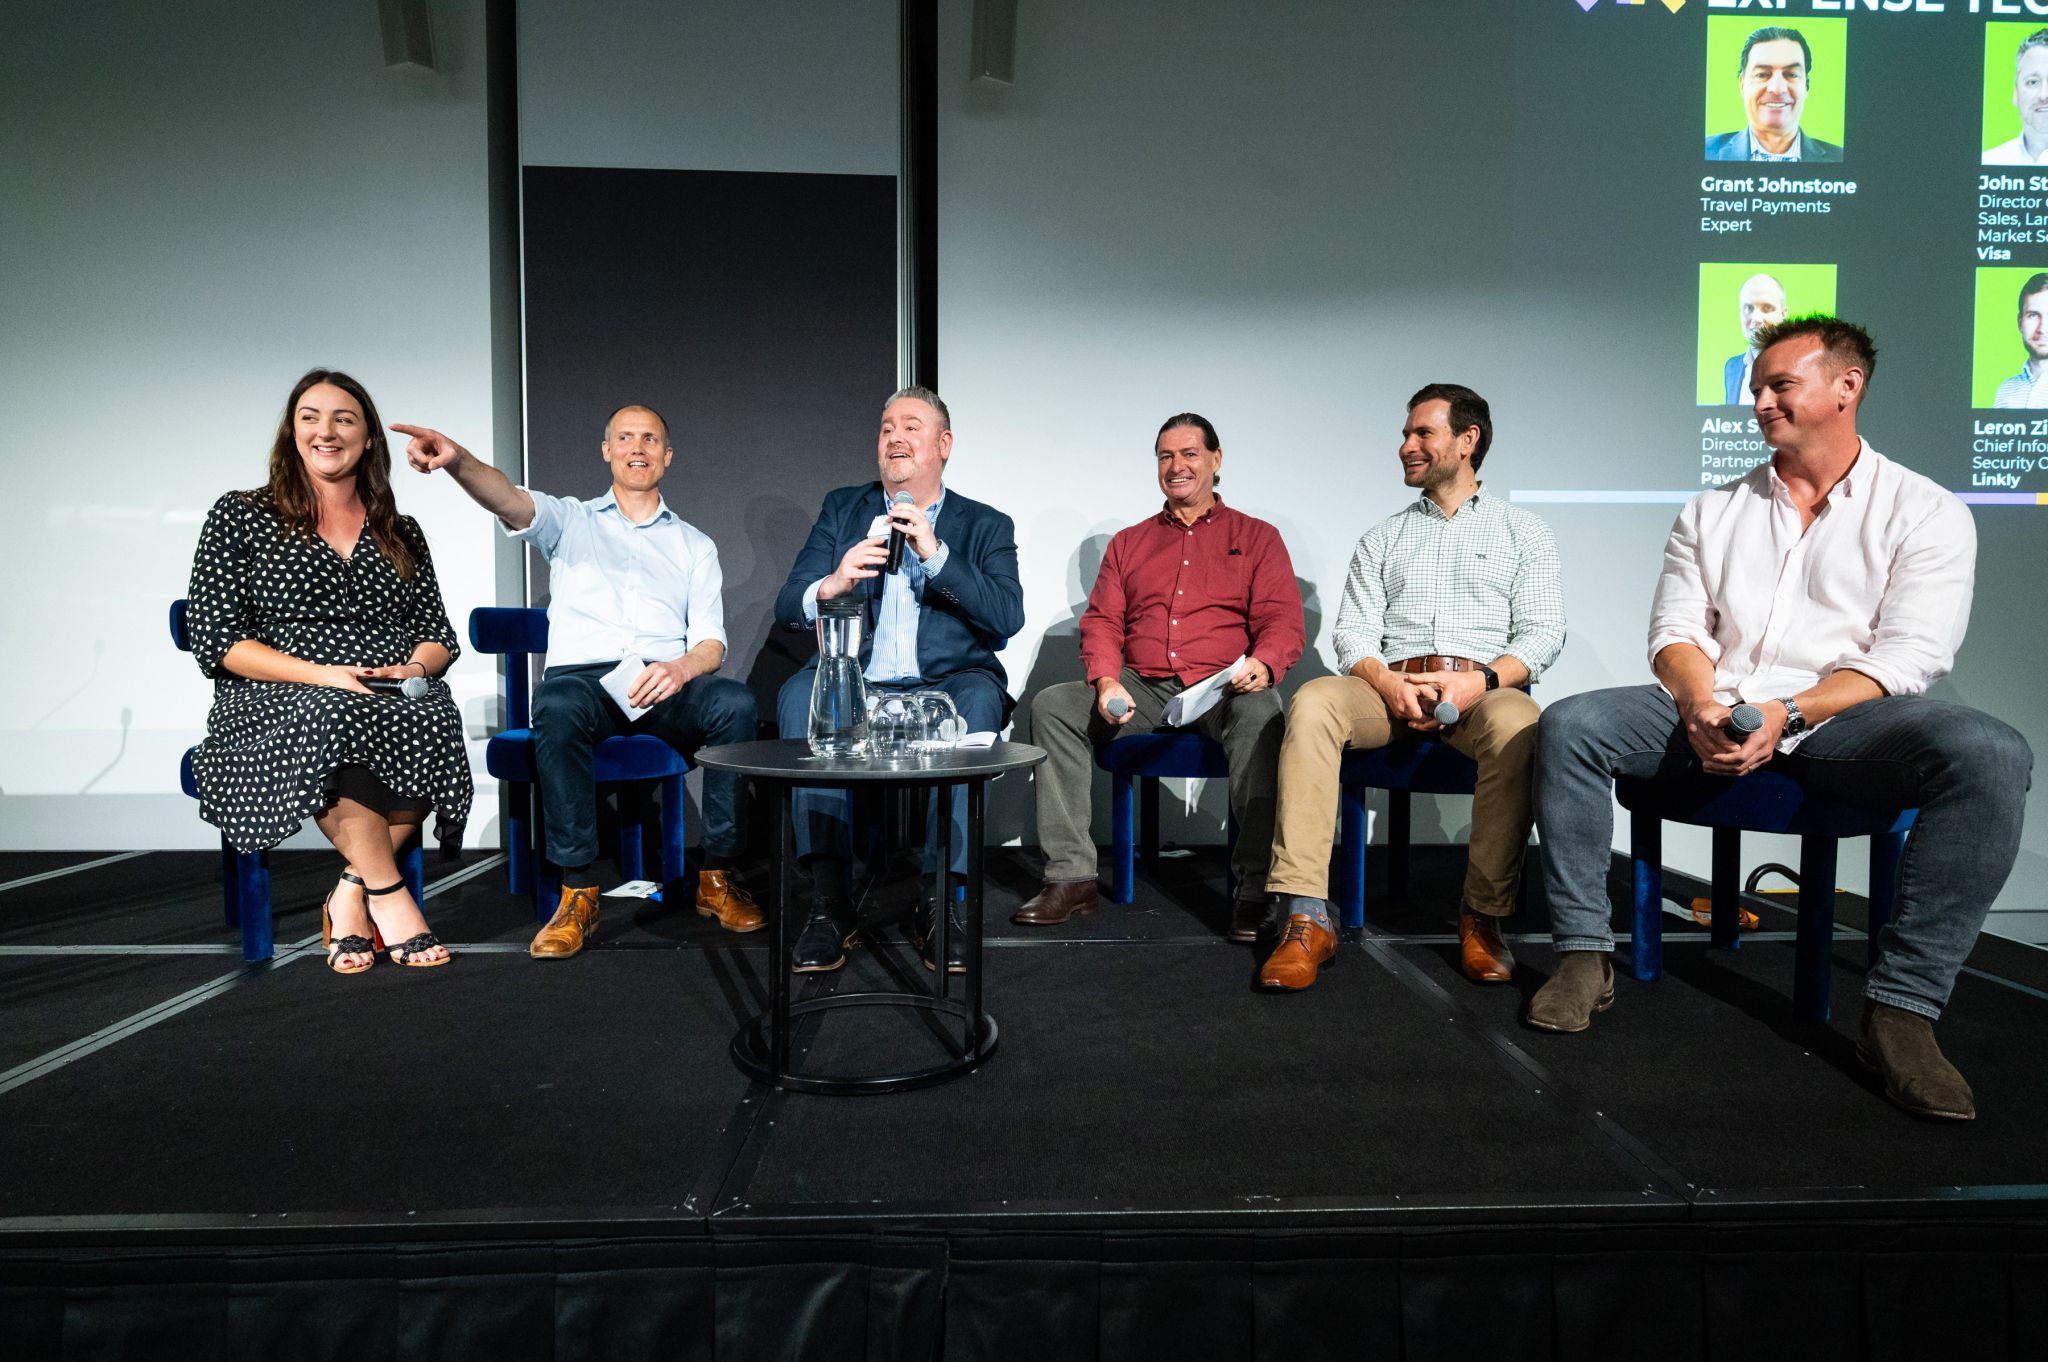
It was good to moderate a discussion on bridging the gap between strategy and execution. Great, candid conversation and plenty I’ll take back to the office.
Key takeaways:
☑️ Buy-in happens when you translate risk into business impact, work across functions and deliver early, visible wins.
☑️ Common pitfall: a glossy PowerPoint deck with no delivery plan. Convert vision into smaller, time-boxed outcomes with clear owners.
☑️ What makes the difference: realistic roadmaps, measurable OKRs (outcomes not activity), empowered teams and a steady governance cadence that removes blockers.
Thanks to the panelists and everyone in the audience who challenged orthodoxies – I learned as much as I hope I gave.
Security failures are rarely a technology problem alone. They’re socio-technical failures: mismatches between how controls are designed and how people actually work under pressure. If you want resilient organisations, start by redesigning security so it fits human cognition, incentives and workflows. Then measure and improve it.
Think like a behavioural engineer
Apply simple behavioural-science tools to reduce errors and increase adoption:
Defaults beat persuasion. Make the secure choice the path of least resistance: automatic updates, default multi-factor authentication, managed device profiles, single sign-on with conditional access. Defaults change behaviour at scale without relying on willpower.
Reduce friction where it matters. Map high-risk workflows (sales demos, incident response, customer support) and remove unnecessary steps that push people toward risky workarounds (like using unapproved software). Where friction is unavoidable, provide fast, well-documented alternatives.
Nudge, don’t nag. Use contextual micro-prompts (like in-app reminders) at the moment of decision rather than one-off training. Framing matters: emphasise how a control helps the person do their job, not just what it prevents.
Commitment and incentives. Encourage teams to publicly adopt small security commitments (e.g. “we report suspicious emails”) and recognise them. Social proof is powerful – people emulate peers more than policies.
Build trust, not fear
A reporting culture requires psychological safety.
Adopt blameless post-incident reviews for honest mistakes; separate malice investigations from learning reviews.
Be transparent: explain why rules exist, how they are enforced and what happens after a report.
Lead by example: executives and managers must follow the rules visibly. Norms are set from the top.
Practical programme components
Security champion network. One trained representative per team. Responsibilities: localising guidance, triaging near-misses and feeding back usability problems to the security team.
Lightweight feedback loops. Short surveys, near-miss logs and regular champion roundtables to capture usability issues and unearth workarounds.
Measure what matters. Track metrics tied to risk and behaviour.
Metrics that inform action (not vanity)
Stop counting clicks and start tracking signals that show cultural change and risk reduction:
Reporting latency: median time from detection to report. Increasing latency can indicate reduced psychological safety (fear of blame), friction in the reporting path (hard-to-find button) or gaps in frontline detection capability. A drop in latency after a campaign usually signals improved awareness or lowered friction.
Always interpret in context: rising near-miss reports with falling latency can be positive (visibility improving). Review volume and type alongside latency before deciding.
Inquiries rate: median number of proactive security inquiries (help requests, pre-deployment checks, risk questions). An increase usually signals growing trust and willingness to engage with security; a sustained fall may indicate rising friction, unresponsiveness or fear.
If rate rises sharply with no matching incident reduction, validate whether confusion is driving questions (update docs) or whether new features need security approvals (streamline process).
Confidence and impact: employees’ reported confidence to perform required security tasks (backups, secure file sharing, suspicious email reporting) and their belief that those actions produce practical organisational outcomes (risk reduction, follow-up action, leadership support).
An increase may signal stronger capability and perceived efficacy of security actions. While a decrease indicates skills gaps, tooling or access friction or perception that actions don’t lead to change.
Metrics should prompt decisions (e.g., simplify guidance if dwell time on key security pages is low, fund an automated patching project if mean time to remediate is unacceptable), not decorate slide decks.
Experiment, measure, repeat
Treat culture change like product development: hypothesis → experiment → measure → adjust. Run small pilots (one business unit, one workflow), measure impact on behaviour and operational outcomes, then scale the successful patterns.
Things you can try this month
Map 3 high-risk workflows and design safer fast paths.
Stand up a security champion pilot in two teams.
Change one reporting process to be blameless and measure reporting latency.
Implement or verify secure defaults for identity and patching.
Define 3 meaningful metrics and publish baseline values.
When security becomes the way people naturally work, supported by defaults, fast safe paths and a culture that rewards reporting and improvement, it stops being an obstacle and becomes an enabler. That’s the real return on investment: fewer crises, faster recovery and the confidence to innovate securely.
If you’d like to learn more, check out the second edition of The Psychology of Information Security for more practical guidance on building a positive security culture.
As AI adoption accelerates, leaders face the challenge of setting clear boundaries, not only around what AI should and shouldn’t do, but also around who holds responsibility for its oversight.
It was great to share my thoughts and answer audience questions during this panel discussion.
Governance must be cross-functional: security, risk, data and the business share accountability. I also reinforced the importance of guardrails, particularly forAgentic AI: automate low-risk work, but keep humans in the loop for decisions that affect safety, rights or reputation. Classify models and agents by impact and apply controls accordingly.
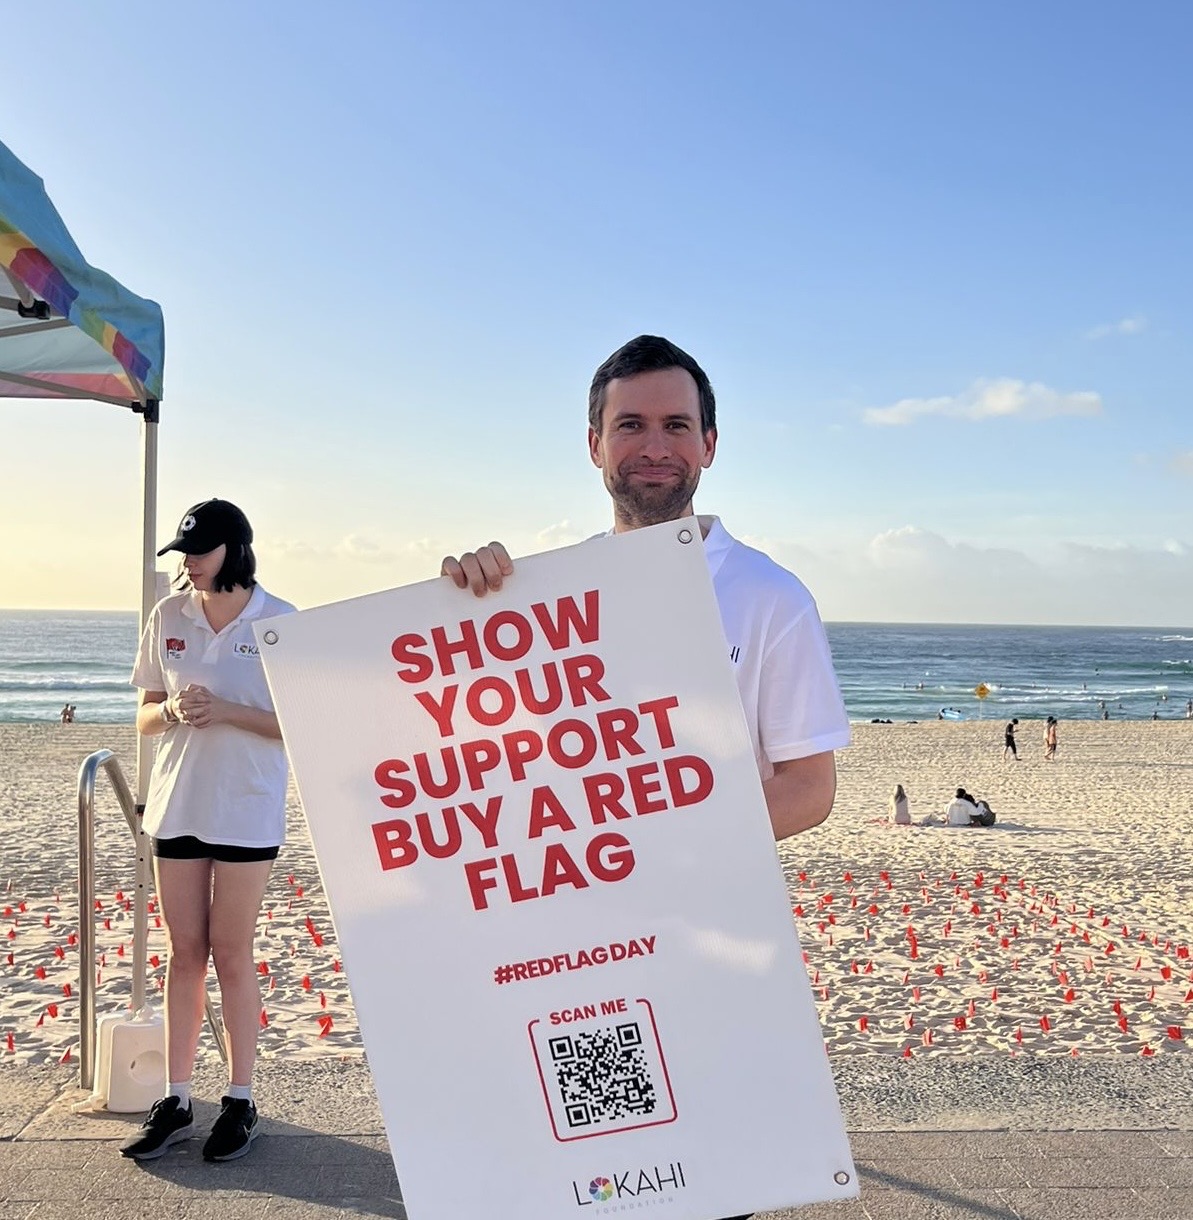
I’m finishing the year having completed The Observership Program as a Board Observer with the Lokahi Foundation, an experience that provided valuable insight into board governance.
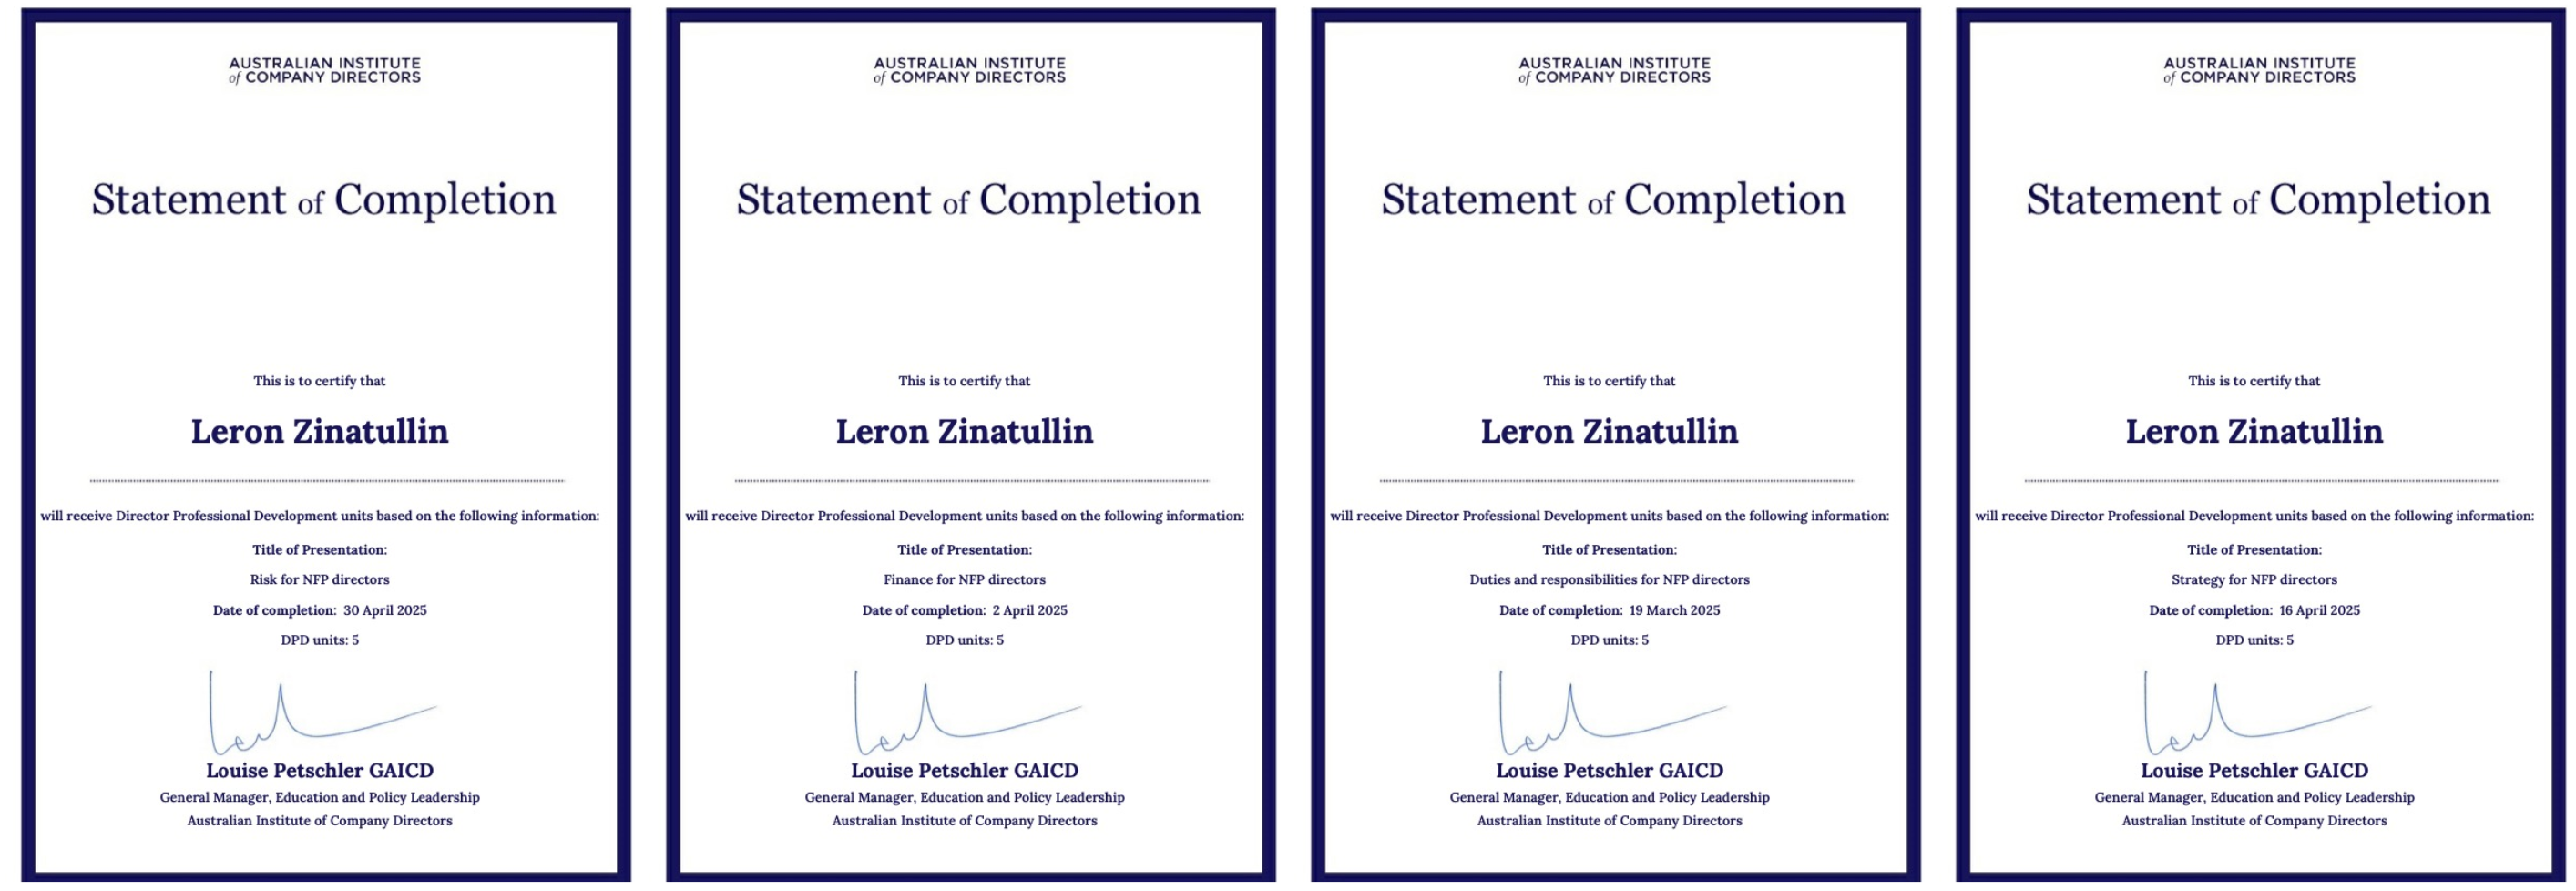
Alongside social impact and governance training from the Australian Institute of Company Directors, tailored to not-for-profit board directors, I spent twelve months observing a purpose-driven board and deepening my understanding of how decisions that matter are made.
Top takeaways:
• The art of questioning – how different types of questions shape discussion and drive clarity.
• Director responsibilities – the difference between reporting to a board and serving on one.
• Bringing stakeholders on a journey – effective communication, buy-in and sustained impact.
• Practical exposure to fundraising, strategy, marketing, sustainability and operations in the not-for-profit sector.
I had a chance to apply skills from my MBA and global corporate experience to support the board. I also drew on my domain expertise in cybersecurity, data protection, technology innovation, AI and impact measurement, particularly championing ethical data practices.
Thank you to the Lokahi Foundation board and the Observership Program for the opportunity to learn and give back. I’m excited to keep building these skills and to support future boardrooms.
I recently took the stage to talk about one of the most consequential inflection points facing FinTech: the rapid arrival of agentic AI – systems that plan, decide and act autonomously – and what it means for risk, reputation, regulation and customer trust. Below is a distillation of the talk: what agentic AI actually is, why FinTechs are racing to adopt it, the real cyber threats it brings, and a pragmatic playbook leaders can use today.