How employees react to security policies

8205162689_345cce5b75_o

Information security can often be a secondary consideration for many employees, which leaves their company vulnerable to cyber attacks. Leron Zinatullin, author of The Psychology of Information Security, discusses how organisations can address this.

First, security professionals should understand that people’s resources are limited. Moreover, people tend to struggle with making effective decisions when they are tired.

To test the validity of this argument, psychologists designed an experiment in which they divided participants into two groups: the first group was asked to memorise a two-digit number (e.g. 54) and the second was asked to remember a seven-digit number (e.g. 4509672).[1] They then asked the participants to go down the hall to another room to collect their reward for participating. This payment, however, could be only received if the number was recalled correctly.

While they were making their way down the corridor, the participants encountered another experimenter, who offered them either fruit or chocolate. They were told that they could collect their chosen snack after they finished the experiment, but they had to make a decision there and then.

The results demonstrated that people who were given the easier task of remembering a two-digit number mostly chose the healthy option, while people overburdened by the more challenging task of recalling a longer string of digits succumbed to the more gratifying chocolate.

The implications of these findings, however, are not limited to dieting. A study looked at the decision-making patterns that can be observed in the behaviour of judges when considering inmates for parole during different stages of the day.[2]

Despite the default position being to reject parole, judges had more cognitive capacity and energy to fully consider the details of the case and make an informed decision in the mornings and after lunch, resulting in more frequently granted paroles. In the evenings, judges tended to reject parole far more frequently, which is believed to be due to the mental strain they endure throughout the day. They simply ran out of energy and defaulted to the safest option.

How can this be applied to the information security context?

Security professionals should bear in mind that if people are stressed at work, making difficult decisions, performing productive tasks, they get tired. This might affect their ability or willingness to maintain compliance. In a corporate context, this cognitive depletion may result in staff defaulting to core business activities at the expense of secondary security tasks.

Security mechanisms must be aligned with individual primary tasks in order to ensure effective implementation, by factoring in an individual’s perspective, knowledge and awareness, and a modern, flexible and adaptable information security approach. The aim should therefore be to correct employee misunderstandings and misconceptions that result in non-compliant behaviour, because, in the end, people are a company’s best asset.

References:

[1] B. Shiv and A. Fedorikhin, “Heart and Mind in Conflict: The Interplay of Affect and Cognition in Consumer Decision Making”, Journal of Consumer Research,  1999, 278–292.

[2] Shai Danziger, Jonathan Levav and Liora Avnaim-Pesso, “Extraneous Factors in Judicial Decisions”, Proceedings of the National Academy of Sciences, 108(17), 2011, 6889–6892.

Photo by CrossfitPaleoDietFitnessClasses https://www.flickr.com/photos/crossfitpaleodietfitnessclasses/8205162689

To find out more about the psychology behind information security, read Leron’s book, The Psychology of Information Security. Twitter: @le_rond
Productive Security

500995147_5f56493a1e_z

The majority of employees within an organisation are hired to execute specific jobs, such as marketing, managing projects, manufacturing goods or overseeing financial investment. Their main – sometimes only – priority will be to efficiently complete their core business activity, so information security will usually only be a secondary consideration. Consequently, employees will be reluctant to invest more than a limited amount of effort and time on such a secondary task that they rarely understand, and from which they perceive no benefit.

Research[1] suggests that when security mechanisms cause additional work, employees will favour non-compliant behaviour in order to complete their primary tasks quickly.

There is a lack of awareness among security managers[2] about the burden that security mechanisms impose on employees, because it is assumed that the users can easily accommodate the effort that security compliance requires. In reality, employees tend to experience a negative impact on their performance because they feel that these cumbersome security mechanisms drain both their time and their effort. The risk mitigation achieved through compliance, from their perspective, is not worth the disruption to their productivity. In extreme cases, the more urgent the delivery of the primary task is, the more appealing and justifiable non-compliance becomes, regardless of employees’ awareness of the risks.

When security mechanisms hinder or significantly slow down employees’ performance, they will cut corners, and reorganise and adjust their primary tasks in order to avoid them. This seems to be particularly prevalent in file sharing, especially when users are restricted by permissions, by data storage or transfer allowance, and by time-consuming protocols. People will usually work around the security mechanisms and resort to the readily available commercial alternatives, which may be insecure. From the employee’s perspective, the consequences of not completing a primary task are severe, as opposed to the ‘potential’ consequences of the risk associated with breaching security policies.

If organisations continue to set equally high goals for both security and business productivity, they are essentially leaving it up to their employees to resolve potential conflicts between them. Employees will focus most of their time and effort on carrying out their primary tasks efficiently and in a timely manner, which means that their target will be to maximise their own benefit, as opposed to the company’s. It is therefore vital for organisations to find a balance between both security and productivity, because when they fail to do so, they lead – or even force – their employees to resort to non-compliant behaviour. When companies are unable to recognise and correct security mechanisms and policies that affect performance and when they exclusively reward their employees for productivity, not for security, they are effectively enabling and reinforcing non-compliant decision-making on behalf of the employees.

Employees will only comply with security policies if they are motivated to do so: they must have the perception that compliant behaviour results in personal gain. People must be given the tools and the means to understand the potential risks associated with their roles, as well as the benefits of compliant behaviour, both to themselves and to the organisation. Once they are equipped with this information and awareness, they must be trusted to make their own decisions that can serve to mitigate risks at the organisational level.

References:

[1] Iacovos Kirlappos, Adam Beautement and M. Angela Sasse, “‘Comply or Die’ Is Dead: Long Live Security-Aware Principal Agents”, in Financial Cryptography and Data Security, Springer, 2013, 70–82.

[2] Leron Zinatullin, “The Psychology of Information Security.”, IT Governance Publishing, 2016.

Photo by Nick Carter https://www.flickr.com/photos/8323834@N07/500995147/

Resistance to change

I’ve written about change management in my previous blog and wanted to tackle the topic from a different angle here. Let’s talk about change resistance.

According to Dannemiller, for a change to take place three factors not only must be present, but their sum must outweigh the resistance to change:

C = D × V × F > R

C – Change
D – Dissatisfaction with how things are now
V – Vision of what is possible
F – First concrete steps that can be taken towards the vision
R – Resistance

Meanwhile, the phenomenon of employees resisting organisational change is viewed as a widely accepted fact. But why is this the case? And, more importantly, what to do about it?

As with many things, the first step to solving this puzzle is to understand the root cause of it. Yes, it may appear on the surface that people may resist a new policy or technology. But look deeper: what do individuals value in the current state of affairs?

More ofter than not it’s their human relationships. Precisely the social element of the change; the change to these relationships that usually goes hand in hand with ‘technical’ change is something people resist the most.

Unpin the social interactions, pay attention to the moods and you might end up on the positive side of the Dannemiller’s equation.

The Psychology of Information Security – Resolving conflicts between security compliance and human behaviour

ITGP

In today’s corporations, information security professionals have a lot on their plate. In the face of constantly evolving cyber threats they must comply with numerous laws and regulations, protect their company’s assets and mitigate risks to the furthest extent possible.

Security professionals can often be ignorant of the impact that implementing security policies in a vacuum can have on the end users’ core business activities. These end users are, in turn, often unaware of the risk they are exposing the organisation to. They may even feel justified in finding workarounds because they believe that the organisation values productivity over security. The end result is a conflict between the security team and the rest of the business, and increased, rather than reduced, risk.

This can be addressed by factoring in an individual’s perspective, knowledge and awareness, and a modern, flexible and adaptable information security approach. The aim of the security practice should be to correct employee misconceptions by understanding their motivations and working with the users rather than against them – after all, people are a company’s best assets.

I just finished writing a book with IT Governance Publishing on this topic. This book draws on the experience of industry experts and related academic research to:

  • Gain insight into information security issues related to human behaviour, from both end users’ and security professionals’ perspectives.
  • Provide a set of recommendations to support the security professional’s decision-making process, and to improve the culture and find the balance between security and productivity.
  • Give advice on aligning a security programme with wider organisational objectives.
  • Manage and communicate these changes within an organisation.

Based on insights gained from academic research as well as interviews with UK-based security professionals from various sectors, The Psychology of Information Security – Resolving conflicts between security compliance and human behaviour explains the importance of careful risk management and how to align a security programme with wider business objectives, providing methods and techniques to engage stakeholders and encourage buy-in.

The Psychology of Information Security redresses the balance by considering information security from both viewpoints in order to gain insight into security issues relating to human behaviour , helping security professionals understand how a security culture that puts risk into context promotes compliance.

It’s now available for pre-order on the UK, EU or US websites.

Secure by design

V4tS8p5F_C0

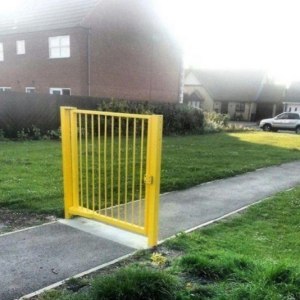
Have you seen security controls being implemented just to comply with legal and regulatory requirements? Just like this fence. I’m sure it will pass all the audits: it is functioning as designed, it blocks the path (at least on paper) and it has a bright yellow colour just as specified in the documentation. But is it fit for purpose?

It turns out that many security problems arise from this eager drive to comply: if the regulator needs a fence – it will be added!

Sometimes controls are introduced later, when the project is well passed the design stage. It might be the case that they just don’t align with the real world anymore.

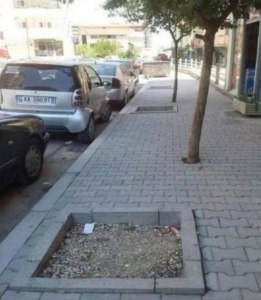
n0saycKzykM

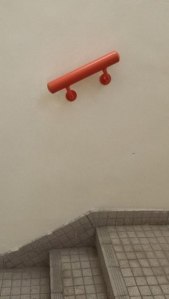
Safety measures, unfortunately, are no exception. The solution may be poorly designed, but more often, safety requirements are included later on with the implementation not fit for purpose.

IbHF452Usk0tuLB7kjBazs

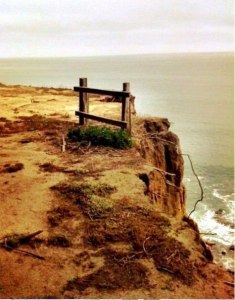
Same holds for privacy as well. Privacy professionals encourage to adopt the Privacy by Design principle. Is it considered on the image below?

2Tx1qKFQzfoB5nli4NoEG4

Change Management

Information security professionals not only have to deal with change, more often than not they represent change. It might be changing the way a company manages access to its systems, works with third-parties or anything else.

To be effective with the change management process, security professionals should work with the business, demonstrating the value of security.

John Kotter in his book Our Iceberg is Melting tells a story about a penguin colony, which demonstrates basic principles of successful change management:

  1. Establish a sense of urgency
  2. Create a guiding coalition
  3. Develop a change vision
  4. Communicate the vision for buy-in
  5. Empower broad-based action
  6. Generate short-term wins
  7. Never let up
  8. Anchor new approaches into the culture

Gamification for security

Oxford dictionary defines gamification as the application of typical elements of game playing (e.g. point scoring, competition with others, rules of play) to other areas of activity to encourage engagement with a product or service:

Bringing an element of fun helps to achieve lasting change in human behaviour, as demonstrated by The Fun Theory project. Here are some videos to get an idea how gamification can drive behavioural change to address social and business challenges:

Gamification can also be a powerful learning tool when applied to information security.

For example, CyberCIEGE enhances information assurance and cyber security education and training through the use of computer gaming techniques such as those employed in SimCity™. In the CyberCIEGE virtual world, users spend virtual money to operate and defend their networks, and can watch the consequences of their choices, while under attack.

In its interactive environment, CyberCIEGE covers  significant aspects of computer and network security and defense. Players of this video game purchase and configure workstations, servers, operating systems, applications, and network devices. They make trade offs as they struggle to maintain a balance between budget, productivity, and security. In its longer scenarios, users advance through a series of stages and must protect increasingly valuable corporate assets against escalating attacks.

CyberCIEGE includes configurable firewalls, VPNs, link encryptors and access control mechanisms.  It includes identity management components such as biometric scanners and authentication servers.   Attack types include corrupt insiders, trap doors, Trojan horses, viruses, denial of service, and exploitation of weakly configured systems.   Attacker motives to compromise assets differ by asset and scenario, thereby supporting scenarios ranging from e-mail attachment awareness to cyber warfare.

More information along with introduction and demonstration movies are also available on the official website.

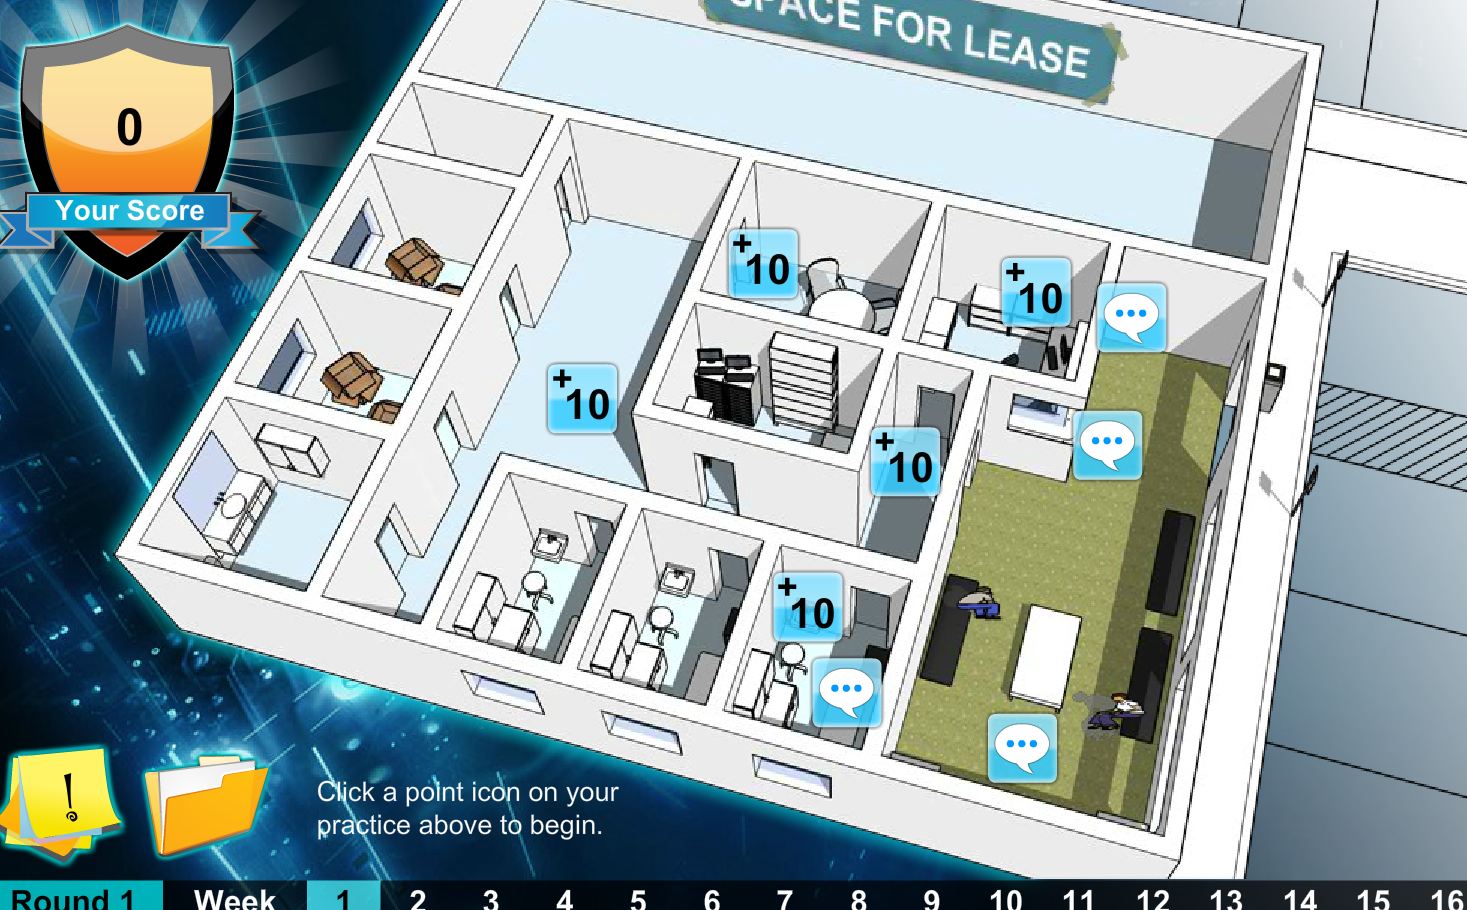
Cybersecure: Your Medical Practice is another example of using gamification to educate people but not in the context of the HIPAA regulation compliance.

hipaa

This web-based security training module uses a game format that requires users to respond to privacy and security challenges often faced in a typical small medical practice.  Users choosing the right response earn points and see their virtual medical practices flourish.  But users making the wrong security decisions can hurt their virtual practices.  In this version, the wrong decisions lead to floods, server outages, fire damage and other poor outcomes related to a lack of contingency planning.

Gamification can also be applied in user awareness training to change the behaviour of users in the organisation. One instance of this might be helping to recognize phishing links.

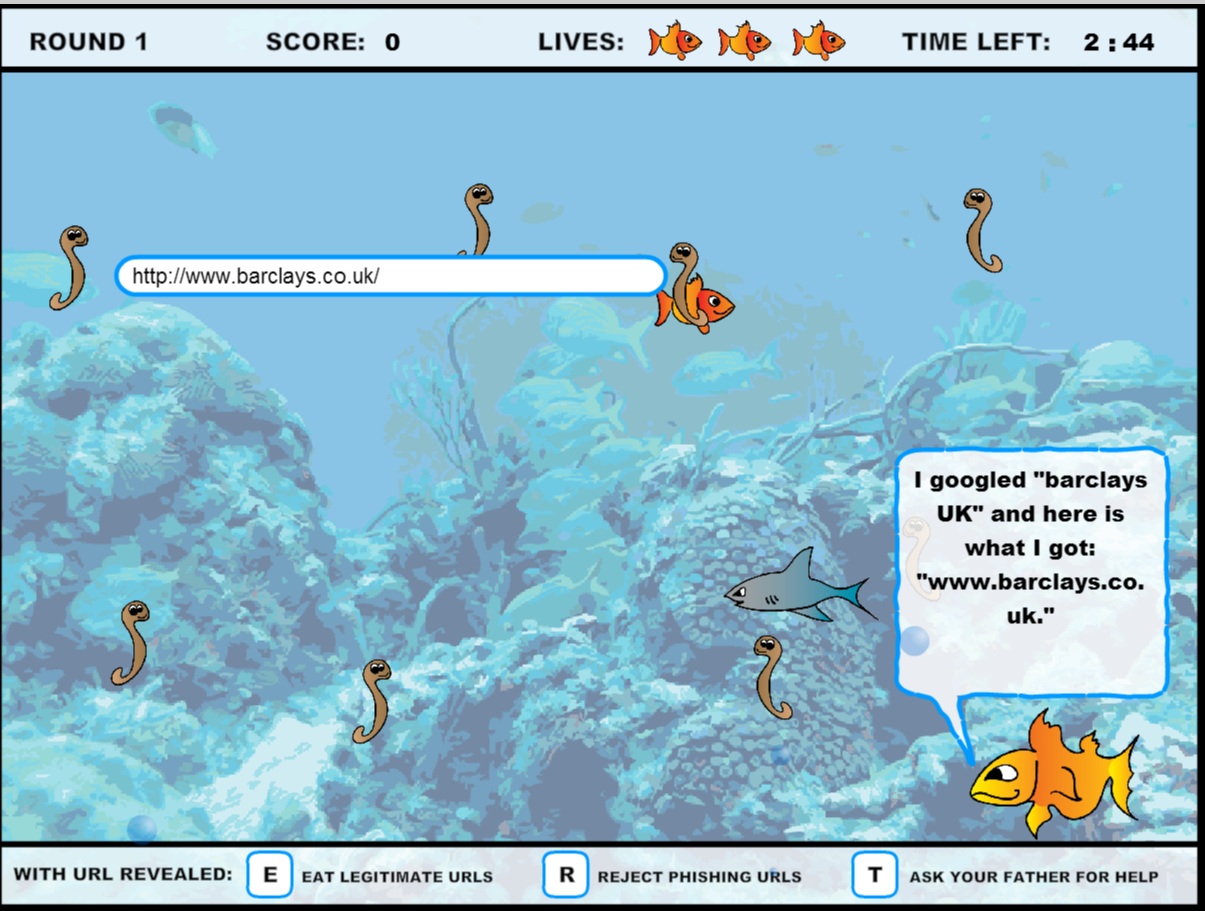
Anti-Phishing Phil is an interactive game that teaches users how to identify phishing URLs, where to look for cues in web browsers, and how to use search engines to find legitimate sites.

phil

User studies have found that user education can help prevent people from falling for phishing attacks. However, it is hard to get users to read security tutorials, and many of the available online training materials make users aware of the phishing threat but do not provide them with enough information to protect themselves. Studies demonstrate that Anti-Phishing Phil is an effective approach to user education.

Apozy and Wombat Security Technologies also focus on gamification in raising awareness about security risks.

There is a free online course on gamification available. This course will teach you the mechanisms of gamification, why it has such tremendous potential, and how to use it effectively.

Cake and Security

There is no doubt that security is necessary, but why is it so unpleasant to follow a security policy? Reminding yourself to stick to the rules feels like your partner telling you…. to eat your salad. You know they are right, but anticipating that bland taste and mindless chewing that awaits you simply puts you off. You decide to leave it for tomorrow, so much so that you never get to it.

Cakes, on the other hand, are yummy and require no effort whatsoever to indulge in our cravings for them. Nobody needs to force us to eat a piece.

In our day-to-day lives we prefer to do “cake” tasks without giving it a second’s thought. Things like storing confidential files on Dropbox or emailing them to our personal accounts…. you know, taking a little bite here and there. It’s “only for today”, “no biggie”… This one-time thing is so harmless, it’s like a comfort snack. We might later feel guilty that we bypassed a few “salad” controls. Maybe we used our personal USB drive instead of a company-issued encrypted one, but at the end of the day… who cares? Who will notice? As long as there is no dramatic impact on our health, a bite here or a bite there won’t cause any harm.

reward

And one day we realise that it’s not all rosy. The result of our laziness or lack of willpower eventually rears its ugly head when the doctor makes us stand on the scales and has a look at our blood pressure. So to add to your partner’s words of wisdom, is the doctor’s warning of an unhealthy present and a bleak future; something that would sound very similar during the company’s security audit.

“You have got to eat more salad and lay off the cakes!”

To make matters worse, even with our best intentions to have the salad at the office cafeteria, we discover that the one available is practically inedible. Pretty much like finding that the company’s secure shared drive doesn’t have the necessary space to store our files or that the encrypted pen drive is not compatible with the client’s Mac.

So if there are chefs coming up with ways to make salads more appealing, what can security professionals do to help us, the employees, maintain our “security diet”?

They could aim at making security more like a cake – effortless, even attractive, but still keep it as healthy as a salad. Sound simple? Perhaps not so much, but they should invest in usability studies to make sure that the secure solution is the easiest to use. It might involve discovering an entirely new culinary art on how to make a cake-tasting salad altogether. But if they fail to realise just how unpalatable the salads are to begin with, we should let them know. Security professionals need employees’ support.

Organisations are like families: everyone has to stay healthy, otherwise when a single member gets sick, the whole family is at risk of getting sick as well, whether it be catching an infectious disease or adopting an unhealthy lifestyle. It’s like having the slimmest, fittest family member refrain from adding biscuits to the grocery list in order not to tempt the couch-potatoes. It’s a team effort. In order for a company to stay healthy, everyone has to keep a healthy lifestyle of eating salad regularly, even when it is not that pleasant.

unpleasant but necessary measures

The whole company needs to know that security is important for achieving its goals -not as something that gets in the way-, just as we should all know that having a healthy diet of greens will guarantee a sound body. Employees contribute to the efficient operation of the business when they comply with security policies. Not only does security ensure confidentiality and the integrity of information, but it also guarantees that the resources are available for employees to complete their primary tasks.

We need to realise that we contribute to security; and we can inflict serious damage on a company when we don’t comply with security policies, no matter how insignificant or harmless they may seem. As employees, we are individually responsible for the organisation’s exposure to security risks just as we are responsible for exposing ourselves to illness. Our behaviour and daily regime significantly shape our quality of life, and our practices shape the quality of our business.

The health of the company is everyone’s business. Let’s all eat our salad while helping the security specialists to come up with better tasting ones.

Giving a talk on information security

Met

I delivered a talk at the London Metropolitan University today where I was invited to share my story and participate in the university’s mentoring scheme. Although there were many students from different fields present, I focused on the computer science and information security area.

I elaborated on the possible and the transferable skills that young students can develop and apply during their undergraduate and postgraduate programmes. We also talked about job search, the general application process and the various career paths available to students in the information security and computer science areas.

Giving a lecture at the Royal Holloway University of London

IMG_20141202_205219

I was invited by the RHUL Computing Society to give a lecture on human aspects of security.

After my presentation, I gave the students an exercise to help them understand the different perspectives on information security policies. As a result, they learned the importance of the role of information security in an organisation and it’s important enabling function.

It was really nice to get such an active participation on their behalf. After the talk we had an interesting conversations on current security research trends and opportunities.

IMG_20141202_205259