Productive Security

ID-100235520

Let’s see how some security controls might affect human behaviour in a company.

  • Restricting software installation on computers is in line with one of the main principles of information security – the principle of least privilege. That way a security manager can make sure that employees in his company don’t install unnecessary programs which may contain vulnerabilities. Such vulnerabilities can be exploited by a potential attacker. There are instances, however, when a user may require a piece of software to perform his productive tasks. Failure to install it quickly and easily may result in unnecessary delays.
  • Restricting access to file sharing websites helps to make sure that a company is not in violation of the data privacy regulation and users don’t store sensitive information in the insecure locations. However, it is important for a company to provide an easy-to-use, secure alternative to enable the business.
  • Restricting access to CD/DVD and USB flash drives. Personal USB flash drives can be a source of malware which users can introduce to the corporate network. Restricting access to CD/DVD and USB flash drives not only helps to prevent this threat, but also limits the possibility of sensitive data leaks. It is important to understand the core business processes in a company to make a decision on restricting the access. Sometimes drawbacks of such a policy may overshadow all possible benefits.
  • Regular full antivirus checks help to make sure that employees’ workstations are free from malware. However, the process of scanning a computer for viruses may take up a lot of resources and slow down the machine with the possible impact on productivity,
  • Awareness training can be a powerful measure to protect against a wide range of security threats, including social engineering (e.g. phishing). However, research shows that blanket awareness campaigns are ineffective and a better approach is needed to address this issue.

Image courtesy of renjith krishnan/ FreeDigitalPhotos.net

Mo Amin: You can transform technology but how do you transform people?

Mo Amin – Information Security Professional

Mo

Can you please tell us a little bit about your background?

Long ago in a galaxy far far…oh ok…ok…Just like a lot of people in IT I got asked the same question “My PC has died, can you help me?” When you say yes to one person it’s a downward spiral…and before you know it you’re THE computer guy! Even now I (depending on my mood) will help out. So this was my first real experience in building rapport with clients, charging for my time and to a certain extent being held accountable for the service I provided.

I taught me a lot and was a catalyst in helping me to land my first role in desktop support. I was part of a small team which allowed me to get involved in some network and application support too. Whilst doing my day role I was involved in a couple of investigations, which got me interested in information security and through a few lucky breaks I slowly moved into the field. I’ve been lucky enough to have worked in a number of areas ranging from operational security through to consultancy. However, I’ve always intrinsically enjoyed the awareness and education side of things.

What is it that you are working on at the moment?

I am working with Kai Roer of The Roer Group to help develop the Security Culture Framework. Essentially, the framework aims to help organisations to build a security culture within their business, as opposed to simply relying on topic based security awareness. Making sure that organisations begin to build a security culture into their business is something I believe in strongly. So when Kai asked if I’d like to help I was more than happy.

Let’s talk for a moment about information security in general. What do you think are the biggest challenges that companies are facing at the moment?

I think that one of the biggest challenges is educating staff on the risks that the business faces and getting people to understand and relate to why it is that we are asking them to adopt secure practices. The problem revolves around changing the attitude and overall culture of an organisation. In my humble opinion, this is the biggest challenge. The difficulty lies in changing behaviour because you can change technology but how do you positively change the behaviour of people?

What is your approach or proposed solution to this challenge? What should companies do?

I’ve always learned by seeing something in action or by actually doing it. Obviously, within the context of a busy organisation this isn’t easy to do.  However, as information security practitioners, professional or however we label ourselves we need to be more creative in our attempts to help those that we work with – we need to make awareness more engaging. I think it’s important to have workshops or sessions in breakout areas where staff can come along see how quickly weak passwords are cracked, what can happen if you click on that dodgy but enticing looking attachment. It’s about visualising and personalising threats for people, for example, if you plan your awareness programme carefully you could map your corporate security messages for the home environment and provide your staff with a “Top 10 of do’s and dont’s” Make it creative and engaging and the messages that you give for their home environment they will begin to bring them back to the office.

Lots companies offer security awareness training, which doesn’t seem to have much of an impact. What do you think about these trainings? Should they be changed in some way in terms of targeting, or accounting for individuals’ particular needs, or focusing on behaviour?

The problem is that most of this is simply topic based awareness, in that it’s not seeking to change behaviour. There seems be to be a lot of generic content that applies to everyone in an organisation. Sadly this is a tick-box exercise for the purposes of compliance. Awareness should be unique to your organisation where you cater for different personality types as best you can.  Some people actually like reading policies where as some prefer visual aids, so the ways that individuals learn needs to be better understood. The process of educating your staff should be a sustained and measured programme; it needs to be strategic in its outlook.

What about communication?

Better engagement with the business is what we need to be doing. Our relationships with the likes of legal, HR, finance, marketing, PR should be on an everyday basis not only when we actually need their expertise. These departments usually already have the respect from the business. Information security needs to be seen in the same light.

How do you identify the relevant stakeholders and establish communication with them, and further propagate the whole process of communication within the organisation?

Grab a copy of the organisation chart and start from there. Your job is to introduce yourself to everyone. In my experience doing this over a coffee really helps and preferably not in a meeting room, because it is better to create a new business relationship in a social context, wherein the other person gets to understand you, firstly as a human being and secondly as a work colleague. Most importantly, do this at the beginning and not two months down the line. Building relationships at the very beginning increases your chances of being in the position of asking for last minute favours and paves the path for easier collaboration, as opposed to having to ask for people’s help when they don’t even know you. Usually people are open and honest. They may have a negative image of information security, not because they don’t like you, but most likely because of the interaction they’ve had in the past.

So let’s say that you have joined a new organisation that has a very negative preconception of information security because of a bad previous experience. Once you have already identified all the key people you have to work with, how do you fight this negative perception?

You need to find out what was done previously and why the outcome was negative in the first place. Once you’ve established the actual problem, you have to diffuse the situation. You need to be positive, open and even simple things like walking around and talking to people – show your face. Visit different departments and admit any failings, you need to do a PR and marketing exercise. In a previous role I’ve actually said

“I know what went wrong the last time, I know we screwed up. I want to ask you what you want to see from the information security department from now on.”

People are ready to engage if you are, be personable and be professional. It’s surprising how much positive and usable feedback you actually get.

The majority of the time, people will tell you,

“I just want to be able to do my job without security getting in the way”.

Once you have these sorts of conversations going you begin to understand how the business actually functions on a day-to-day basis. It’s at this stage where you can be influential and change perception.

Modern security professionals while fighting cyber threats also have to take human behaviour into account

In today’s corporations, information security managers have a lot on their plate. While facing major and constantly evolving cyber threats, they must comply with numerous laws and regulations, protect the company’s assets, and mitigate risks as best as possible. To address this, they have to formulate policies to establish desired practices that avoid these dangers. They must then communicate this wanted behavior to the employees so that they adapt and everything can go according to plan. But is this always the case?

Security managers often find that what they put on paper is only half of the story. Getting the corporation to “cooperate” and follow the policy all the time can be far more challenging than it seems. So why do employees seem to be so reluctant?

Are we even asking the right question here?

The correct question is: do security managers know what imposing new rules means to the average employee within the company?

People’s behavior is goal-driven. If processes are imposed on them, people will usually follow them, as long as they still allow them to achieve their goals. If they come across situations where they are under pressure, or they encounter obstacles, people will cut corners, break rules and violate policies.

So why should the behavior of a corporation’s employees be an exception? They will usually follow the rules willingly while trying to comply with the security policy, but, at the end of the day, their objective is simply to get their work done.

Yes., there are cases of employees who have a malicious goal of intentionally violating security policies, but research shows that policy violations will most likely result from the controls implementation that prevented people from performing their tasks.

What happens to an organization when honest workers can’t achieve their goals because of poorly implemented security controls? What happens on the security manager’s end and on the employees’ end that leads to this scenario? A short survey I performed in 2013 shows that there is a huge gap between the employees’ and the security managers’ perceptions of security policies; and it’s this discrepancy that negatively impacts the organization as a whole. Security managers, on their side, assume that they have made all the relevant considerations pertaining the needs of the employees. However, the fact is that they rarely speak directly to the employees to familiarize themselves with their tasks, their needs, and their goals. It is therefore usual to hear employees complain about how security controls hinder or impede their performance.

Let’s consider the following scenario:

In an investment bank, a security manager comes up with a policy document, outlining a list of authorized software which can be installed on computers, according to the principle of least privilege: people can only have the access they require to perform their day-to-day activities and no more. All employees are denied access to install any new software without written permission from the security manager.

John is writing a report for the client. The deadline is fast approaching but he still has a lot of work ahead of him. The night before the deadline, John realizes that in order to finish his work, he requires a special data analysis software which was not included in the list of authorized programs. He is also unable to install it on his workstation, because he doesn’t have the required privileges. Getting the formal written approval from the security manager is not feasible, because it is going to take too long. John decides to copy the sensitive information required for the analysis on his personal computer, using a flash drive, to finish the work at home, where he can install any software he wants. He understands the risk but he also wants to get the job done in order to avoid missing the deadline and get good performance review. Unfortunately, he leaves his bag with the flash drive in the taxi on the way back home. He never tells anyone about this incident to avoid embarrassment or a reprimand.

The security manager in this scenario clearly failed to recognize the employee’s needs before implementing the controls.

A general rule of thumb to never forget is that employees will most likely work around the security controls to get their work done regardless of the risks this might pose, because they value their main business activities more than compliance with security policies.

To address this, security managers should consider analyzing security controls in a given context in order to identify clashes and resolve potential conflicts adjusting the policy. They should also communicate the value of security accordingly. Scaring people and imposing sanctions might not be the best approach. They should instead demonstrate to the employees that they contribute to the efficient operation of the business when they comply with security policies. Not only does security ensure confidentiality and the integrity of information, but it also makes sure that the resources are available to complete their primary tasks.

Employees need to understand that security is something that important for achieving the company’s goals, not something that gets in the way. To achieve this, the culture of the organisation must change.

Jitender Arora: The key to success is to approach any change from human psychological perspective

Interview with Jitender Arora – Information Security & Risk Executive (Financial Services)

Arora

Could you please start by telling us about your background?

I am a Computer Science and Engineering graduate, with Masters Degree in Consultancy Management. I had been a very technical, hands-on person from the very beginning of my career. I spent the first two years building firewalls, proxy servers and hardening UNIX servers. After few years, I was presented with an opportunity to move into information security and risk. At the time, I was working for Wipro Technologiesand they were building a Security Consultancy Practice, which would be front-ending with their customers, and working on the projects. The organisation was recruiting for this practice from other parts of the organisation so I decided to move into this new practice which proved to be a very exciting and challenging assignment. That’s where my journey in terms of “information security and risk”started from. Later, I had leadership roles in organisations like Adobe Systems and Agilent Technologies. I moved to the UK around 8 years ago, and that’s when my journey began working in the financial services sector.

What do you do now?

Around four years ago, I decided to quit my job and start my own small consulting firm with two friends I had met at RBS. We did a good job for two years, and build a good profitable business. Unfortunately, due to some unavoidable circumstance the partnership didn’t work out and we decided to amicably part ways. After that, I didn’t want to jump into the first thing that came along, and so I focused on my independent journey as Interim Executive in leading business transformation and change programs that address governance, risk and compliance problems faced by my client organisations. My engagements are outcome oriented to deliver the specific outcome for the client organisation. Over the last 3 or 4 years, I have built a strong reputation of being an outcome-oriented management consultant.

You are a very well known speaker within the industry. What made you decide to engage in this sort of activities as well? 

It was not an intentional choice. I was once having a conversation with my best mate, Javvad Malik, around the need for new speakers at conferences who are able to present a different point of view. In a way, Javvad encouraged (or should I say pushed, Thank You Jav) me to go ahead and speak at conferences. At that point, I wasn’t too keen on it because I have always felt anxious about speaking in a public forum. Additionally, English is not my first language, which represented another barrier. But I decided to face my fear, and just go along with it. When I actually started speaking, I received an encouraging response from the audience and attendees liked my take on topics which they said provided a unique perspective. Being a very pragmatic consultant, I usually have a different point of view, as opposed to being a paranoid view. I approach security & risk problems and issues as a business person which provides a different perspective, so that’s where I think I got some good recognition from the market, especially in the speaking circuit. I believe speaking engagements not only present an opportunity for building your own personal brand but also helps sharpen your selling and marketing skills. The way you approach people, build their perception of you, sell yourself and your ideas, it’s a very good skill to have which is not generally taught in school or at university. Now, I encourage my colleagues and professionals to speak at events.

Returning to what you were saying about being an outcome oriented consultant, could you please elaborate on how changes can be implemented within organisations when these changes involve people and their behaviour? How do you address the people aspect of security?

As a security professional, when you implement a new security control, you are usually changing the way people are operating. A very simple example would be when implementing a control in terms of how people access production system. So if you go into an organisation in which their practices have been acceptable for the past 10 years, and you suddenly tell them that they can no longer follow same practice, you are, in a way, taking a privilege away from them and they will react accordingly. The analogy that I usually use for this is if I suddenly tell my son, who normally watches 1 hour of T.V. a day for the past several years, that he cannot watch it without taking permission every time and not more than 30mins from now on. He will not like it and will most likely rebel and show his displeasure.

As security professionals we try to change the process, and we want to introduce a certain level of governance on top of it. It’s very important to manage the people aspect of implementing such changes for security. You need to get people on your side before you actually implement these controls. It is a lot about socialising, and communicating, which brings me back to the point on selling and marketing. You have to package, sell and market these changes by conveying the message that “even though we are taking this privilege away from you by implementing these controls, we are going to give you something in return: We will guarantee that you run your business in a compliant manner and do not get audit findings or regulatory issues in which you will have to invest to address them”. So returning to the original example, it’s about establishing a secure way of accessing production systems which, although might be different from existing methods and might involve a little extra work, will ensure that everybody can continue to do their job while being compliant. We will create a robust production access environment: “So let’s be proactive and address this situation together before someone else comes and asks us to fix it.”

There are some of security professionals who scare the clients and users as a strategy for avoiding unwanted behaviour, by telling them, for example, that they might even risk getting fired. What is your opinion on this approach?

If you scare people too much, they will be scared as long as you are in front of them, but the behaviour won’t change. The objective should be to change the behaviour, and when we say “behaviour”, we are referring to the way people operate on a day-to-day basis. Make sure that they don’t see this as a temporary situation, but as a routine. A very simple example for this would be physical security guards. We have security guards in all the office buildings who are standing on the side, observing people, looking for individuals who may seem malicious or suspicious. But they don’t intimidate people around them. You might even be able to approach them for directions and they will kindly answer if they can help. But the moment they detect somebody suspicious, they will intervene. Now let’s imagine that instead of having these friendly security personnel, we had big bouncers who are aggressive. Would you feel okay approaching them? Sometimes security in our context operates like those big nightclub bouncers, because it is intimidating. So business people stop inviting you as a security professional to their business initiatives because they see security as the big intimidating bouncer: as a problem. For them, if you bring security in, you are bringing a problem in. That needs to change, and it largely depends on relationships and how you manage those relationships, how you come across in your meetings with them, and what they main message of your proposition is: “we are not taking anything away from you, we are going to help implementing new controls that will allow you to run your business in a secure and compliant manner meeting legal and regulatory obligations.”So it’s a trade-off and it’s a lot about perception, so the scaring tactic I don’t think works for too long.

You have come up with a way of selling all of your services to the executives and they understand the value of them. What about the actual people who use the service?

I think of executives as the same as the end-users, so the methods I use to sell security doesn’t change at for different levels. It’s the way you deliver message and what message you deliver has to be adapted for different levels. Business executives will normally focus on how you are going to solve the problems that will allow the business to address the compliance issues and meet regulatory requirements. They are the ones that get chased around by the auditors and the regulators. But for the end-users, compliance is not their problem. They never get to own or see these auditing issues. From their perspective, they have a business to do, a server to manage, an infrastructure to run, they want to operate the way they have done so far. So if bringing in new security controls doesn’t mean making life difficult, they are happy to participate. As a security professional, that’s the message that you can give: “we are not here to make your life difficult, but to make sure you have the right tools to do your job effectively in a secure and compliant manner.”

As a preliminary step to implementation, would you have to first understand what it is people normally do on a day-to-day basis?

Absolutely. The very first thing I like to do is to see these users or consumers of these controls as my key stakeholders. One thing I always do in any of these change programmes is approach stakeholders including user groups in their working environment, and make them feel comfortable. Ask them, listen to them and understand what their problems are. What is it that they like that they would like to keep, and what they don’t like that they would like to have changed, and what is it that they might have seen somewhere else and might be a good thing to include as part of this change. Key benefit from being in listening mode is that people become part of the journey because they have largely contributed to the creation and design of these new controls. The key to success is to approach any change from human psychological perspective and engaging them by asking, listening and taking their feedback on board. Another thing that I always make sure to do is to fix the things they don’t like in the existing environment. Listen to people; understand what they like, what they don’t like, make sure you can fix their problems, and if they want something else, try to help them get it: get them on your side. Make them feel like they are part of this journey and also give them credit for their contribution to the success.

Let’s imagine that a security manager decides to implement a security policy in any given company. Let’s say that they take a standard framework like, say, ISO 27001, they tweak it a bit and apply it into the company’s environment. Do you see any potential problems with this?

Frameworks are a good start. But what lots of organisations do is that they lift the framework as is and if you look at the policies in most of them, there is not much difference. But if you think of different types of organisations like the financial services, investment banking, or law firms, you have many different environments: you have different drivers and they come with a very different set of challenges. A lot of professionals, who write policies, do so in isolation. They don’t spend time understanding how a specific organisation carries out its business. An interesting question would be, once a policy is written, whom do you want to be the target audience? Is the policy being written by security people, to be interpreted by security people? Or is a policy being written by security people, to be understood by security people, when in reality it is supposed to be meant for business people? In one of my previous engagements, I had security experts writing the policy, and I then hired a technical writer to review, proof-read and rewrite the policy. The end products between the policy written by the security experts and by the technical writer were completely different: the latter was much more understandable by the business community. We don’t realise that, unless an external person comes along and starts asking questions –“oh, what do you mean by this?”- that the language is not easily understandable for everyone. So I believe that every organisation should hire competent technical writers to translate their security policy, standards and guidance from specialised security jargon into a language that is understandable for business people.

So once your policy is written in understandable terms for everyone, how do you make people read it and comply?

The first thing I do in any organisation is that I visit their homepage and type in “information security”. If the policy doesn’t come up as the first search result, something is wrong. If people can’t find the security policy, how can you expect them to read it? How can you expect them to comply?

Another thing that I have done in few organisations is to conduct a simple survey, by asking three simple questions to business community:

  1. Do you know that we have an information security department?
  2. Do you know services this department has to offer?
  3. Do you know how to contact them if you need it?

It’s very eye-opening and you get lots of strange responses from the business people. Many times they do not know how to contact the security department or what services they provide. If they don’t know you exist, how can they possibly approach you? We can have a fantastic policy embedded in some website, but nobody is looking at it nor reading it.

Another problem is that security policies are long documents: They are not exciting, they are not novels. So I wouldn’t expect business people to read each and every bit and understand it. The probability to succeed can increase if you can provide them a platform where they are able to search when they need to and know where to go and look for answers when they need it. And this touches the point of approachability and availability of the policy and guidance.

But lets focus on the policy itself. How many policies do we have in a typical regulated organisation that we expect employees to read and comply with? E.g. security, anti-money laundering, acceptable use, expenses, travel and anti-bribery policy etc: it’s a huge list. Think about how long it takes an individual to read those policies, understand, remember and follow them. We’re human, it’s not possible. What’s important is that on a day-to-day basis there are some aspects that you need to demonstrate and follow as a normal business user and whenever in doubt go and seek answers. I like to refer to this as “acceptable behaviour”, not only in terms of privacy and security but overall behaviour.

You can take key messages from all of your relevant policies, and communicate them in friendly, simplistic and interesting terms linking it back to acceptable behaviour. It’s not the computer-based training (CBT) that can change human behaviour, but human-to-human interaction. It’s about helping people understand how to do what they do on a day-to-day basis, how to make their daily life easier and making the information accessible if they need to know more.

To wrap it up, you have mentioned previously that it is important to build a good security culture within the organisation. How do you define a good security culture?

A good analogy for this would be our behaviour regarding airport security, what we know we can do and what not to do, as well as reporting anything that may look suspicious. We are generally aware of our surroundings, especially when we are in an unknown territory. This is very natural to us in the physical world where we can see, hear and touch things in our surroundings. The challenge now is that we are spending so much of our time in this virtual world, where our senses can’t be used in the same way. We have to ask ourselves what key risk indicators in this virtual world are. How should we conduct ourselves in this virtual world? This is the kind of awareness that needs to be built into people’s behaviour. I think this journey should start from earlier stages in life, when people are being schooled. When I was in school, when I was growing up, my parents used to tell me: don’t talk to strangers, don’t accept anything from strangers, don’t give away your personal information to people you don’t know well, and so on. It’s an advice on how to conduct yourself safely in the physical world. Now, those messages have to change. You need to build a culture into the newer generations who are now and will be spending so much of their time in the virtual world. The definition of stranger in the virtual world is different from that in the physical world. The definition of “acceptable behaviour”in this virtual world has to be different from physical world. The definition of those risk indicators haven’t changed. One cannot expect behaviour to change on the first day a person joins the workforce, because by that time, behaviours are already formed.

The moment people become security aware, they become security advocates who can help spread this awareness on behalf of the security department. The organisations have to start a chain-reaction by making a few people security-aware and sending the message across the organisation. Everybody becomes self-aware at some point and starts thinking on his/her own about what is right and wrong. But this doesn’t happen because of computer-based training or policies. It is the change in human behaviour that is required in the long-term.

Thank you Jitender

Yousef Syed: Most people understand security from the real world

Interview with Yousef Syed – Enterprise Security Architect at Bayvision Limited
Syed

Let’s start with the basics. How did you start your journey in information security?

Back in 1998 I graduated with a BSc in Computer Science and chose to focus on Object Oriented Analysis & Design and Java. In September 1999 I started contracting in the telecom industry in Netherlands. It was a unique, pre-dotcom-crash situation. A brand new multi-billion-dollar joint venture between two telecom groups – loads of money, starting from scratch with next to no infrastructure – really brilliant place for a relatively new graduate to come in to. A start-up with loads of money! While, officially regarded as a “Web Developer”, since they had no developer PCs, no servers, no DEV/TEST/Prod, no source-control, no standards, no policies, no DMZ; I ended up being involved in everything – and it was great! Set up policies, set up development standards, and specifying and ordering the PCs and software for the developers; specifying the servers for the website/database, and then being in meetings with the networking people to define what the firewall rules were going to be, and what we needed to do. Basically, doing everything!

A year later, I began a contract in Munich working as a secure Java developer using the new JAAS (Java Authentication and Authorisation Service) API in an Agile/Extreme programming team. So back in 2000 I was exposed to security and ever since I’ve kind of been in-and-out, either just doing application development or some other branch of security.

Then, in 2005 while I was working permanently with Accenture and I was exposed to identity management as a specific field –Thor Xellerate (later to become Oracle Identity Manager). Working on various client sites, I found identity management very interesting because it cut across every part of the business. Everybody in the business needs access to multiple, different systems, and the IDM provisions and de-provisions the users with the appropriate level of access, for all users.

Very interesting. What are you working at the moment?

In January, I was contacted by a cloud-based accountancy firm regarding a cyber-security voucher that the government was funding to encourage Small and Medium sized firms and Sole-traders to improve their cyber security stance.

It was one of the more enjoyable projects I’ve been involved in. Compared to working in a large faceless organisation, or government department, where you might disappear in amongst thousands of other small cogs, and your influences is small; here, you get to make an impact. When you are working in a smaller organisation of about 50 people or up to 200 people; your influence and impact is clear to see and is appreciated by the client. More over, since I’m communicating directly with the business leaders, the security serves the business needs instead of just an individual department’s needs.

Why do you think this is important? What is the main difference between working for a small company compared to a big one?

I believe you are going to understand their business better, so you can give genuinely relevant advice. You don’t need to worry about keeping your consultancy/employer or specific business-unit happy.  You just need to focus on the business, and on giving them the best advice for them.

I hope to keep doing this for the foreseeable future, because it is easy to get bored of working in big companies. I mean, big organisations are nice because you get exposed to good technology, complex problems and huge projects etc., but as far as getting return for your work where you actually see results there and then; then you can’t beat the immediacy of an SME. You don’t need permission/sign-off from a dozen different stakeholders before you update that policy document. You change that policy or that you give them a piece of advice that has changed their focus to create a secure coding development platform; how to improve testing on that; you’ve given them access to resources they didn’t even know about, and you’ve given them new ideas and new perspectives.

And you’ve also shown them how they can actually improve themselves. So if they go for ISO 27001, that might be a differentiator between themselves and their competitors, and it’s also something that they can tell their customers: “We value your data privacy seriously, we have these standards in place, and we’re looking after you.”

When you work in security, you take a lot of things for granted. But then you go to some small or medium-sized companies, and they’ve been so focused on building their small business and delivering new functions, security is way back in their list of priorities. Now you get to raise that up and show them that it not only benefits them on the compliance side of things, but that the benefit also lies in their knowing where their data is, who has access to their data, they know when they have access to it. And you can put all sorts of different levels of controls onto things and give them a far greater peace of mind about how they are dealing with things internally to their company and how they are dealing with things with regards to their product. So delivering this cyber-security voucher to SMEs is something that I’m pursue with a lot more zeal at the moment, because I never knew about it before, and I know it can make a big difference to all of them. £5K is pretty meaningless to your average Fortune 500 company, but to an SME it is a pretty big deal.

What in your opinion is the main obstacle in implementing a similar approach in large corporations?

One of the problems with large corporations, and the same thing in government, is that each separate individual department has a budget. And they need to work to that budget, and they need to ensure that they are doing enough so that they get the same budget or more next year. And it gives a very narrow view to what they are doing. For me the best security (and IT investment in general) is when it is applied at the enterprise-level, across all of the various business units, and considers how we can make all of these people work well together. There is no point in having a really strong security in your finance department, when another department isn’t even talking to them, and they are doing similar work but on different platforms. On the one hand, you are wasting money, because they are duplicating work, they are duplicating data, they are duplicating the risks involved: in fact they are not even duplicating, they are making the risks much wider, because they may not be tracking where the data is going, and on another platform; its going all over the place.

[So if one department has Oracle DB, another is running Sybase and another small team has MS Access; a) You have the cost of the separate platforms; b) separate licensing for same task; c) you need to harden each platform separately; d) you need define a mechanism to share the data across the systems to maintain the integrity of the data; e) you need to support and patch separate systems etc. Conversely, the enterprise could have defined a single Database platform that all departments to use thus saving a world of pain.]

And while the ISO 27001 and various other standards out there will give you a kind of check-box compliance, “yes, we did this, we did this,” it doesn’t give you the kind of thing to say, “I feel comfortable about this.” Yes, you might feel comfortable about it if the legal department comes and questions you about it, but do you feel comfortable enough about it to be able to say that we have done a good job here, and we have delivered something to the client that actually works for them?

What about the security culture?

Yes, one of the things that I kept on stressing to one of my clients was: “you have a culture here that works for you. You have a very nice environment because everybody knows what’s going on here. If you are a developer, you know everybody in marketing, you know everybody in sales, and everybody knows you. And you have very free-flowing information going on, and it helps a great deal in how you operate. So when you are adding security controls, you don’t want to break what’s already working. You want to make sure it becomes better”.

Can security awareness training help to resolve this?

There is a problem with awareness training and educating users. If you are like me, I come from a technical background, you become very narrow-minded thinking: well I find technology very easy, why can’t you work it out? “Well, because I work in marketing!”

I don’t know anything about marketing so why should they know anything about technology?

There is a certain level of arrogance that we in technology developed about other people: in fact, there is a massive amount of arrogance, you come up with all kinds of deprecating or dismissive terms like “problem exists between keyboard and chair (PEBKAC)” or other phrases, just because they just don’t understand. Why don’t they understand? Because they are qualified for something completely different, something which you don’t understand.

So one should stop being so arrogant, step into their shoes, and understand them or try to find a way to translate what you do into terms that they will understand.

So what is the solution?

For me, I always go back to real world examples. Most people understand security from the real world. We are used to carrying five or six different keys for different things. But on the Internet, people only use one key; they only use one password. And they use it everywhere. So when it gets lost, people have access to everything that they own.

In the real world, I have a separate key for my car, a separate key for my home, a separate key for the main door vs. a separate key for my own apartment, and we are used to this kind of thing. But trying to explain to a user why it is that we use a password manager, we have to explain it to them in terms that they will actually understand, and actually take time for them to join the dots within their brain. “So that’s why I should have a different password. That’s why I should make my password really difficult.” Until they put two and two together, they are going to go for whatever is easiest.

So there are a lot of places where not only security people, but technology people in general need to learn to meet the end user halfway and make security transparent and ubiquitous: make security a layer that they don’t necessarily need to think about so much. But from our side, we need to make our code secure, we need to make our cloud system interactions secure, and we need to make our data policies and the implementation of our data policies secure.

Can you elaborate on security policies? Do you see any problems with them?

There’s no point in writing something in your policy that everyone is ignoring. There was a company a few years ago with the policy that nobody was allowed to use Microsoft Messenger. Everyone was using Microsoft Messenger! Your policy says this, and everyone is doing something different. So why is it written in your policy? Either train your people to not use it, and give them a valid, relevant, genuine alternative that they can use, or don’t put it in your policy.

And there are loads of things in the policy documents to please the auditors and to please the compliance team. But that is not how you do security. It in fact makes security worse because it gives the illusion to management that all these things are in place, when all the while the users are bypassing or ignoring it.

How security professionals can help the management in this case?

You need to give them the tools that help. If they are carrying client-data upon which they need to write reports, they need to do some data classification, state who should have access to it and how valuable things are. So if you have classified data, how should you encrypt it, how should you store it, how should you transfer it. So, for argument’s sake, buy a set of encrypted USB keys. If you know that people are working off of their laptops, get something like TrueCrypt or something else that encrypts their laptop, so that their laptop is encrypted if their laptop goes missing or something, you’re safe. Institute Two-Factor-Authentication. And, educate the user: you make sure they understand.

Are there any problems with implementation of such solutions?

Big corporations get these things, they throw loads of money at it, but they don’t look at it from the perspective of how does a business actually use this.

So one of the things which I was saying was that yes you can buy a really cool firewall and IPS system, but you can also do a simple hardening of your database, of your OS, of your application server, close down all of the open ports, close down all of the services that shouldn’t be on, and lets do some monitoring on some user behaviour, on how people are accessing your system. That will give you, for much cheaper, a whole load of control and peace of mind.

What the possible solution might be then?

From the technology and security side, you need to be aware of the business, and what are the drivers of this business, where do they make their money, where is the “data gold”, and what do they need to protect, and how they are going to protect that, and remain operational. You’ve got data which is very valuable to the company because it’s being used. If they can’t use that data, it’s worthless to them. So if you lock it down too much, or you prevent it from moving around to certain people, then you’re preventing the company from doing business. So until you actually understand that, you can’t put in the relevant controls to allow them to use their data and have a level of security.

You’re never going to be 100% secure, so trying to dream that you are going to be 100% secure is a waste of time, trying to do it by way of fear and scaring your client into doing things is a completely wrong way of doing things, because when you are in a state of fear, your judgment is so far off the mark, that it’s ridiculous. Whereas in the case of “I understand what I’m doing over here. Yes, there are some dangers in this. But we understand it.“

Can you give an example?

It is all about risk management – don’t be afraid of them; simply understand them and manage accordingly.

I’m a snowboarder, and last winter I did an avalanche skills training certification course. The way they manage risk is very similar to how we in security do many things (In many respects they are better because lives depend on it). They have to look at a lot of different things that can trigger an avalanche –current weather conditions, weather over the preceding weeks, terrain, different types of snow; which places you are in danger of being in an avalanche, and there are various trigger points and safety concerns (yes, it gets complicated). You don’t live in fear of avalanches because you saw something in some crappy disaster movie. Instead you live in awareness of it and manage your safety. It’s called awareness training, as opposed to a “you’ll magically be safe from an avalanche by doing this.” It’s a case of saying: right, these are different factors that can trigger an avalanche and these are different things that can make you safer from an avalanche.

So if you have had a lot of snowfall in the preceding days followed by a rapid thaw, then it is very likely that some areas on the mountains will have avalanches. So under those circumstances, you don’t go out into very steep slopes, you stay on the slopes that are shallower, or in the treeline. Yes, you may not have as much fun, but you live to play another day.

Before you go out, there are a few things that you are supposed to do. You’re supposed to notify people that this the zone that we are going to, you define a leader of the group, you take all the various precautions that you have all the avalanche transceivers, probes and shovels, and all these kind of things so that, if the worst happens, you are prepared to dig someone out, and that kind of stuff.

Are there any issues applying the same principles to security?

When you go to have your tyres changed, you don’t need to tell the mechanic to make sure to pump up the tires to the correct pressure. They do it automatically. But for us in IT, we need to stipulate this bunch of standard documents and requirements, and we have this non-functional sets that put these standards in place, “you will make sure that you are using this framework” to prevent SQLi attacks. People should be doing this automatically in our industry (it should be part of our quality process), but we don’t do it.

And there is a lot on our side to blame, because we don’t communicate properly, we don’t talk to the right people. And we also have a tendency to think: I told you once, how come you haven’t changed it?

We want it instantly, or at the latest, tomorrow. No, it’s going to take them time to learn, it’s going to take them time to step up their game to the correct level. And you need to be appreciative of this.

What is your approach?

There’s no one magic bullet that will solve this problem, since it is spread across so many systems and every business is different.

For a previous client, following initial meetings, I setup multiple security roadmaps for them in the three areas that we chose to focus on: business continuity planning; software development and data privacy.

How was this to be achieved? What steps must we take in the next week, month, quarter and where do we expect to be in six months from now. The steps we take must be measureable to some degree. This allowed us to apply a maturity model to it.

It involved some technology, some education, and a lot of communication across business domains and teams to ensure we were serving the business.  It also involved the flexibility to acknowledge what isn’t working and change accordingly.

So we have a way of setting these things up so that we can track how well are we doing and where we are, and then you’ve got the ways for them, for the technical team to give feedback back to management, to say that “we’ve added this, and this has given us this additional benefit”.

Thank you Yousef. A few final words of wisdom, please.

You need to be honest with your customer. Sometimes they are not going to listen and you are going to have to do what they want you to do, and that’s part of the business. But you need to understand what the business is, and not just the department that you are being called into. You need to explore what is going on at an enterprise level.

Giving a seminar at the University of East London

Poster

This morning I delivered a seminar for a group of graduate students at the University of East London. An enriched mix of participants from various degrees, including information security, forensics, and IT law made the classroom discussions very interesting.
I was very glad to see that students were very eager to learn more about the subject and were willing to share their ideas and experience.  We were even able to managed to identify new research opportunities in the field of economics of information security.
East London small
After the presentation, I facilitated a workshop which was designed based on a case study around USB drive encryption. This exercise helped the students to understand the perspective of both a security manager and an end-user on the same problem.

Image courtesy of Stuart Miles / FreeDigitalPhotos.net

Information security policy compliance, business processes and human behaviour

This article aims to review the literature on information security policy compliance issues and their relation to core business processes in the company and users’ behaviour. It also provides an insight into particular implementation examples of the ISO 27001 Standard, and methods of analysis of the effectiveness of such implementations.

Information security

Information security issues in organisations have been brought up long before the rapid development of technology. Companies have always been concerned with protecting their confidential information, including their intellectual property and trade secrets. There are many possible approaches to addressing information security. Wood [30] points out that security is a broad subject including financial controls, human resource policies, physical protection and safety measures. However, Ruighaver et al. [23] state that information security is usually viewed as a purely technical concern and is expected to have the same technical solution. On the other hand, Schneier [25], Lampson [17], and Sasse and Flechais [24]  emphasise the people aspect of security, and people play crucial role as they use and implement security controls.

As stated by Anderson [3], it is essential to properly define information security in order to pay merit to all these aspects.

The Standard for Information Security Management ISO 27001 [32] defines information security as “the protection of information from a wide range of threats in order to ensure business continuity, minimize business risk, and maximise return on investments and business opportunities.”

Dhillon [10] states security issues in organisations can arise due to absence of an information security policy. One of the ways to implement such a security policy is to take ISO 27001 standard as a framework.

ISO 27001 Standard

ISO 27001 Standard which is a member of the ISO 27000 standards family evolved from British national standard BS7799 [31]. It aims to provide guidance on managing the risk associated with threats to confidentiality, integrity and availability of organisation’s assets. Such assets, as defined in ISO 27001 [32] include people, software, hardware, services, etc.

Doherty and Fulford [11], Von Solms [28], and Canavan [8] all came to the conclusion that well-established standards such as ISO 27001 might be a stepping-stone to implementing good information security programs in organisations.

However, Anttila and Kajava in their study [4] identify the following issues with ISO 27001 Standard:

–       The standard is high-level and basic concepts are not presented consistently in the standard.

–       It is hard to measure business benefits from implementing this standard.

–       Presented process management is not fully supporting current business practices.

–       The standard struggles to recommend solutions to contemporary business environments.

Neubauer et al. [19] in their research states that the main problem with security standards, including ISO 27001 is their “abstract control definition, which leaves space for interpretation”. Furthermore, the authors suggest that companies focus on obtaining formal certification and often do not to assess and put in place the adequate security controls according their main business goals. Ittner et al. [14] support this point, adding that organisation also fail to estimate the effectiveness of the investments in such initiatives.

According to Sharma and Dash [26], ISO 27001 does not provide detailed guidance requires substantial level of expertise to implement. Moreover, the authors claim that “If risk assessment is flawed, don’t have sufficient security and risk assessment expertise, or do not have the management and organizational commitment to implement security then it is perfectly possible to be fully compliant with the standard, but be insecure.” Results of their study suggest that the organizations, which participated in the study implemented information security mainly to comply with legal and regulatory requirements. The consequence of that was low cost-effectiveness of such implementations. However, the researcher don’t analyse the level of users’ acceptance of implemented controls. The authors also fail to recommend an approach which would support security manager’s decision-making process in implementing ISO 27001 Standard controls.

Karabacak and Sogukpinar in in their paper [16] present a flexible and low-cost ISO 17799 compliance check tool.  The authors use qualitative techniques to collect and analyse data and sate that “the success of our method depends on the answers of surveyors. Accurately answered questions lead to accurate compliance results.” However, the researchers stop short of analysing the impact of compliance with security policy on users’ behaviour. The authors do not consider the issue that a security manager’s decisions regarding a particular implementation of security policy affects that organisation as a whole and may introduce additional cognitive burdens to users. These issues in extreme cases (e.g. obstructing core business processes) may result in non-compliance as users prioritise their primary task.

Vuppala et al. their study [29] discuss their experience from implementing ISO27001 information security management systems. One of the most important lessons learnt was developing an understanding of the role of users’ behaviour in this process. The authors recommend to “not make drastic changes to the current processes; this will only infuriate the users. Remember, users are an important, if not the most important, part of the overall security system.”

Human behaviour

Johnson and Goetz in [15] conducted a series of interviews with security managers to identify main challenges of influencing employees’ behaviour. The results of this study revealed that security managers rely extensively on information security policies, not only as a means of ensuring compliance with legal and regulatory requirements, but also to guide and direct users’ behaviour.

To explore the question of the impact on users’ behaviour while implementing security policies, the following theories were researched:

1. Theory of Rational Choice – a framework, which provides insight into social and economic behaviour. It implies that users tend to maximise their personal benefits [13]. Beautement et al. in their paper [6] uses this theory to  build a foundation explaining how people make decisions about whether to comply or not to comply with any particular information security policy.

Herley [12] suggests that it is rational for users not to comply with security policy, because of the perceived risk reduction is lower than the effort needed.

2. Protection Motivation Theory – a theory which describes four factors that individuals consider when trying to protect themselves [22]:

–       perceived severity

–       probability of the adverse event

–       efficiency of the preventive behaviour

–       self-efficiency

Siponen builds on this theory to gain an understanding of the attitude of individuals towards compliance with security policies. Siponen refers to it in order to study the impact of the punishment on the actual compliance and on intention to comply [27], [20].

3. The Theory of General Deterrence – this suggests that users will not comply with the rules if they are not concerned with punishment [1].

4. Theory of Planned Behaviour – this suggests that subjective norms and perceived behavioural controls influence individuals’ behaviour [2]. Siponen [27] and Pahnila [20] discovered that social norms play a significant role in users’ intention to comply.

These theories suggest that to effectively protect a company’s assets, the security manager should develop and implement security policies not only to ensure formal compliance with legal and regulatory requirements, but also to make sure that users are considered as a part of the system. Policies should be designed in a way that reduces the mental and physical workload of users [1], [6].

Business process visualisation and compliance

It is important to consider information security compliance and users’ behaviour in the context of a company. Users in organisations involved into activities, which could be presented as business processes.

Business process is defined as a set of logically related tasks (or activities) to achieve a defined business outcome [9].

The continuous monitoring of their business processes is essential for any organisation. This can be achieved by visualisation of business processes [21]. However, they are usually complex, due to number of different users or user roles in large companies [7]. Barrett [5] also argues that it is essential to create a “vision of the process” to successfully reengineer it.

Namiri and Stojanovic in their paper [18] present a scenario demonstrating a particular business process and implement controls necessary to achieve compliance with regulatory requirements. The authors separate business and control objectives, introducing two roles: a business process expert, who is motivated solely by business objectives, and a compliance expert, who is concerned with ensuring compliance of a given business process.

References

[1]        Adams, A. and Sasse, M.A. 1999. Users are not the enemy. Commun. ACM. 42, 12 (Dec. 1999).

[2]        Ajzen, I. 1991. The theory of planned behavior. Organizational Behavior and Human Decision Processes. 50, 2 (Dec. 1991).

[3]        Anderson, J.M. 2003. Why we need a new definition of information security. Computers & Security. 22, 4 (May 2003).

[4]        Anttila, J. and Kajava, J. 2010. Challenging IS and ISM Standardization for Business Benefits. ARES  ’10 International Conference on Availability, Reliability, and Security, 2010 (2010).

[5]        Barrett, J.L. 1994. Process Visualisation: Getting the Vision Right Is Key. Information Systems Management. 11, 2 (1994).

[6]        Beautement, A. et al. 2008. The compliance budget: managing security behaviour in organisations. Proceedings of the 2008 workshop on New security paradigms (New York, NY, USA, 2008).

[7]        Bobrik, R. et al. 2005. Requirements for the visualization of system-spanning business processes. Sixteenth International Workshop on Database and Expert Systems Applications, 2005. Proceedings (2005), 948–954.

[8]        Canavan, S. 2003. An information security policy development guide for large companies. SANS Institute. (2003).

[9]        Davenport, T.H. and Short, J.E. 2003. Information technology and business process redesign. Operations management: critical perspectives on business and management. 1, (2003), 1–27.

[10]     Dhillon, G. 2007. Principles of information systems security: text and cases. John Wiley & Sons.

[11]     Doherty, N.F. and Fulford, H. 2005. Do Information Security Policies Reduce the Incidence of Security Breaches: An Exploratory Analysis. Information Resources Management Journal. 18, 4 (34 2005).

[12]     Herley, C. 2009. So long, and no thanks for the externalities: the rational rejection of security advice by users. Proceedings of the 2009 workshop on New security paradigms workshop (New York, NY, USA, 2009).

[13]     Herrnstein, R.J. 1990. Rational choice theory: Necessary but not sufficient. American Psychologist. 45, 3 (1990).

[14]     Ittner, C.D. and Larcker, D.F. 2003. Coming up short on nonfinancial performance measurement. Harvard business review. 81, 11 (2003), 88–95.

[15]     Johnson, M.E. and Goetz, E. 2007. Embedding Information Security into the Organization. IEEE Security Privacy. 5, 3 (2007).

[16]     Karabacak, B. and Sogukpinar, I. 2006. A quantitative method for ISO 17799 gap analysis. Computers & Security. 25, 6 (Sep. 2006).

[17]     Lampson, B.W. 2004. Computer security in the real world. Computer. 37, 6 (2004), 37–46.

[18]     Namiri, K. and Stojanovic, N. 2007. Pattern-based design and validation of business process compliance. On the Move to Meaningful Internet Systems 2007: CoopIS, DOA, ODBASE, GADA, and IS. Springer. 59–76.

[19]     Neubauer, T. et al. 2008. Interactive Selection of ISO 27001 Controls under Multiple Objectives. Proceedings of The Ifip Tc 11 23rd International Information Security Conference. S. Jajodia et al., eds. Springer US. 477–492.

[20]     Pahnila, S. et al. 2007. Employees’ Behavior towards IS Security Policy Compliance. 40th Annual Hawaii International Conference on System Sciences, 2007. HICSS 2007 (2007).

[21]     Rinderle, S.B. et al. 2006. Business process visualization-use cases, challenges, solutions. (2006).

[22]     Rogers, R.W. 1975. A Protection Motivation Theory of Fear Appeals and Attitude Change1. The Journal of Psychology. 91, 1 (1975).

[23]     Ruighaver, A.B. et al. 2007. Organisational security culture: Extending the end-user perspective. Computers & Security. 26, 1 (Feb. 2007).

[24]     Sasse, M.A. and Flechais, I. 2005. Usable Security: Why Do We Need It? How Do We Get It? Security and Usability: Designing secure systems that people can use. L.F. Cranor and S. Garfinkel, eds. O’Reilly.

[25]     Schneier, B. 2003. Beyond Fear: Thinking Sensibly About Security in an Uncertain World. Springer.

[26]     Sharma, D.N. and Dash, P.K. 2012. Effectiveness Of Iso 27001, As An Information Security Management System: An Analytical Study Of Financial Aspects. Far East Journal of Psychology and Business. 9, 5 (2012), 57–71.

[27]     Siponen, M. et al. 2010. Compliance with Information Security Policies: An Empirical Investigation. Computer. 43, 2 (2010).

[28]     Solms, R. von 1999. Information security management: why standards are important. Information Management & Computer Security. 7, 1 (Mar. 1999).

[29]     Vuppala, V. et al. Securing a Control System: Experiences from ISO 27001 Implementation.

[30]     Wood, M.B. 1982. Introducing Computer Security. National Computing Centre.

[31]     BS, BS7799 – Information Technology – Code of practice for information security management, London: BS, 1995.

[32]     ISO/IEC, ISO/IEC 27001 – Information technology – Security techniques – Information security management systems – Requirements, Geneva: ISO/IEC, 2005 and Draft for the new revision ISO/IEC JTC 1/SC 27 N10641, 2011.

Comparing views on security compliance behaviour in an organisation

The purpose of this post is to provide a comprehensive analysis of the data collected from the survey and semi-structured interviews to compare views on information security activities from security managers’ and users’ viewpoints.

Methodology

Survey

A survey was developed to collect information from a broad sample on attitudes of the users’ towards information security policies in their organisations in general, and how compliance with information security policies affects their behaviour in particular. It was quantitatively analysed.

Method

The main goal of the survey was to assess the attitude of the end-users towards information security policies in their companies and measure the level of dissatisfaction with security tasks. Prior to the questions, all participants were shown a page with the explanation of the purpose of the study, approximate time to complete the survey, the researcher’s contact information, and their rights to withdraw their answers at any time. After getting participants’ consent by clicking the “Next” button, they were asked to answer the eleven multiple-choice questions. The first four questions were designed to gather demographic information about the participants for future analysis: participants were asked to provide information on their gender, age, the number of years of work experience, and the industry sector. The subsequent seven questions were aimed at gathering insight on users’ attitude towards information security policies in their companies and the way they make their compliance decisions. Participants were asked to:

  1. Indicate their attitude towards security policy in their company.
  2. Assess the effectiveness of implementation of the security policy in their company.
  3. Estimate the approximate time they spend weekly on various security activities, such as password changes, antivirus checks, anti-phishing checks, awareness training, encryption, etc.
  4. Indicate their attitude towards the impact which security activities have on their overall performance: respondents were presented with a statement “I believe security activities negatively affect my overall performance” and were asked to choose one of the following four answers: “strongly agree”, “agree”, “disagree”, and “strongly disagree”.
  5. Assess the degree of concern of the security manager in their company with users’ main business goals and tasks.
  6. Assess the frequency of the prevention of security controls from accomplishing their main business tasks.
  7. Indicate their attitude towards the possibility of violation of the security policy if it prevented them from accomplishing their main business activities.

The survey was advertised on social networks (LinkedIn, Facebook) to recruit participants for the survey. A sample of specific interest was created to include people with relevant job experience.

Results

This section presents detailed end-users’ survey findings. Results are described in the order of their appearance in the survey. 64 responses were collected.

End-users’ demographic characteristics

Results show that the majority of the sample (40 out of 64 participants) were male. They also illustrate that 32 out of 64 participants are in the 18 to 24 age group, and that 29 out of 64 are in the 25 to 34 age group. A relatively small number of participants (only 3 people) are older than 35 years. The members of the most populated group (22 out of 64 participants) are in the beginning of their careers and have less than one year worth of work experience. The following figure presents the distribution of respondents by industry sector.

Distribution

Distribution of respondents by industry sector

Attitude towards security policy in the company

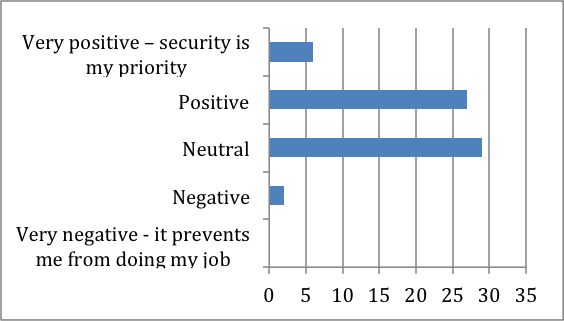
The results of the survey show that 51% of participants share a positive outlook towards information security in the company (6 have chosen “very positive” option and 27 “positive”). 29 respondents share a neutral attitude towards information security in the organisation. Only 2 participants indicated a negative attitude.

Attitude

Attitude towards security policy

View on the implementation of the security policy in the organisation

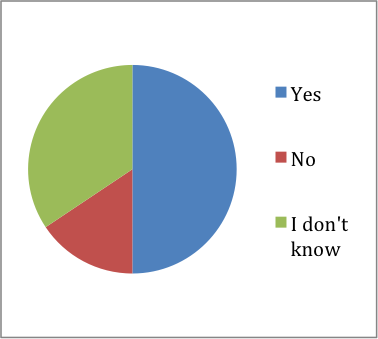
50% of participants think that information security policy is effectively implemented in their compamy. However, 34% of the population struggled to provide an opinion on this matter.

Effectivness

Effectiveness of implementation of the security policy

Time spent by users on security activities

A large majority (80%) feel that they spend less than 30 minutes per week in total on security tasks. However, there are 4 respondents that share the perception that they have spent over an hour on security activities in the course of the past week.

 time

Time spent by users on security activities

Impact on users’ overall performance

37 participants disagree with the statement that security negatively impacts their overall performance and 12 participants strongly disagree with it, although, there is 1 respondent who strongly agrees.

 Impact

Impact on users’ overall performance

Assessing the degree of concern of the security manager in the company with users’ main business goals and tasks

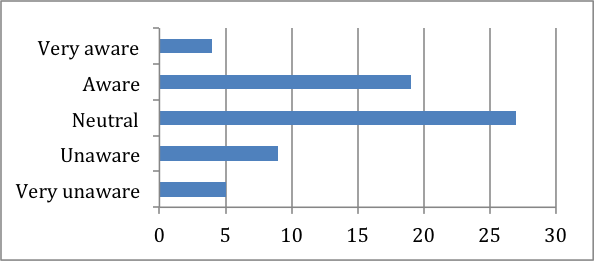
Most of the participants (27 out of 64) believe that their security manager is rather neutral towards users’ business activities. 19 participants feel that their security manager is aware of their day-to-day tasks.

 Degree

Degree of concern of the security manager in the company with users’ main business goals and tasks 

Instances of obstructing core business processes

30 respondents cannot recall any instances in which security controls obstructed their business activities. On the other hand, the results of the survey show more than 50% experienced problems at least once a year, and in many cases more regularly because of the security policy.

 Instances

Instances of obstructing core business processes

Information security policy violations

Results show an almost equal split between people when faced with the statement “I would violate security policy if it prevents me from accomplishing my main business tasks” who are willing to violate security policy in order to get their job done and those who make the decision to comply even in this case.

 violations

Information security policy violations

Discussion

Individual response analysis shows that some people can’t recall situations whereby security policy prevented them from accomplishing their core business activities, however they still perceive security as something that hinders their performance. Other participants also didn’t indicate such instances more frequently than approximately once every three months

frequency

Frequency of collisions in relation to perception of negative impact on users’ performance

Individual response analysis also allowed revealing the fact that there is a person, who strongly agrees that security tasks affect his/her performance. This individual’s answer of the question on the perceived number of instances when security policy prevented him/her from accomplishing their main business task shows that he/she experiences difficulty performing business activities on a daily basis. The anonymous nature of the survey didn’t allow the researcher to conduct a follow up interview to gain an insight on this particular case. Moreover, high number of responses “I don’t know” to the question regardless the effectiveness of implementation of the security policy may indicate that the criteria for effectiveness were not clearly defined. Furthermore, using social networks as a sample to survey users negatively affected the researcher’s ability to generalise the results. The presented sample contains mostly young people with relatively small amount of work experience. This fact makes it difficult to drive conclusions, because perception of the employees towards security task may change with time in the job. Given the limitations, results show that more than 23% of participants believe that security tasks negatively affect their overall performance. This outlines the major concern for the organisations, because it directly affects company’s ability to generate revenue. According to the survey results, 20% of participants responded that they spend approximately one hour per week on various security tasks.

Interviews

The second stage was conducted as an exploratory study with five information security experts. This section presents a descriptive analysis of the semi-structured interviews with information security experts.

Method

The main goal of the semi-structured interviews was to gather an insight on information security manager’s awareness of the fact that his decisions on particular implementation of security controls affect organisation as a whole, and that his actions may negatively impact users’ performance in core business activities. The interview questions were designed to gather information on security manager’s ability to distinguish between instances of malicious non-compliance and instances when security controls obstruct users’ main business tasks was gathered. All information security experts selected to participate in the study have seven or more years of work experience in the field of information security and are currently holding managerial positions in their companies. Materials and feedback from the two pilot interviews, which were not included in the current project, were then used to refine the questions and procedures for the following interviews, so that they focus more on relevant topics and group them into categories. When patterns started to emerge, the data were then evaluated. The Grounded Theory analysis revealed that the most common codes: –       Security manager’s decision-making process on particular implementation of security controls –       Relation between business and security goals –       Detection of instances of non-compliance –       Reaction to instances of non-compliance –       Security manager’s awareness of how security policy implementation affects users’ behavior –       Difficulties in measuring impact of users’ behaviour. –       Security manager’s awareness of users’ typical business activities –       Effect of understanding of users’ business activities on security manager’s decision-making process

Results

Results are grouped into codes, which were developed in line with the Grounded Theory: – Security manager’s decision-making process on particular implementation of security controls: Interview results suggest that 4 out of 5 interviewed security managers use their past experience when implementing security policy. One security manager suggested that security policy was already implemented in his organisation. – Relation between business and security goals: all security managers understand the role of information security as a supporting process. – Detection of instances of non-compliance: all interviewed experts rely on both formal and informal channels of detecting instances of non-compliance. – Reaction to instances of non-compliance Interview results suggest that 4 out of 5 interviewed security managers tend to try to understand the root cause of the problem first. One security manager indicated that he is not directly involved into investigation of such incidents. – Security manager’s awareness of how security policy implementation affects users’ behaviour: 4 out of 5 security managers believe that they aware of the impact of security controls on users’ behaviour. One security manager suggested that he doesn’t have resources for that. – Difficulties in measuring the impact of users’ behaviour: all experts experience some difficulties in assessing the impact on users’ behaviour. – Security manager’s awareness of users’ typical business activities: 4 out of 5 security managers indicated their awareness of users’ day-to-day tasks. One security manager mentioned that he doesn’t have enough time for this. – Effect of understanding of users’ business activities on security manager’s decision-making process: all of the interviewed experts agree that it is beneficial to understand users’ business tasks.

Discussion

This section presents a discussion of interview findings.

Security manager’s decision-making process on particular implementation of security controls

Interview data reconfirms that security managers mostly use their own judgment and past experience when making a decision on particular implementation of information security controls. As explained in a quote: “When I’m making a decision to implement ISO 27001 standard in my organization, half of that decision is what the particular policies would actually look like. Because ISO 27001 is very high-level and it is by all means not a policy in itself, it just gives you one or two criteria or one or two suggestions how your security policies should look like. Because of this freedom of implementation, you actually have to write these policies yourself.”

Relation between business and security goals

Interviewed security experts also understand the role of involving the business management in the process of implementing security controls. For example, one security manager mentioned: “If there is no benefit to the business – you don’t do it.” Another expert reinforces his point by saying: “Get the people who these controls directly affect. You should start with the business. Get their buy-in; although they might view it as an additional workload, hence most people involved in this security initiative might produce sub-standard work.“ Interviewed security managers also think that business objectives should always be the priority. For example, one expert commented: “Many security managers think that security is the most important thing. I personally don’t think so. Paying shareholders is the most important. Inhibiting those activities or encouraging dangerous activities because of what you are doing you are making the situation worse.” The results illustrate that interviewed security managers understand that their decisions affect the whole organisation.

Detection of instances of non-compliance

Participants of the interview are aware of various methods to detecting non-compliance. For example, one expert mentioned: “I walk around this building on occasion and I wiggle doors and I check workstations for locked screens. The other way you find out is by rumours or chatting with people.” The results revealed that security experts rely on both formal (e.g. periodic security reviews) and informal (e.g. rumours, complains) channels of detecting non-compliance.

Reaction to instances of non-compliance

Most interviewed security managers agree that you should not punish users for non-compliance right away. You have to first understand the root cause of the problem. For instance, one expert suggested: “You don’t react on non-compliance with anger. You try to find out why it happened, rather than the fact that it has failed. Moreover, you can use it as a possibility for education and awareness and possibility for improvement.” Another expert reinforces this point saying: “At the end of the day it failed because with high probability you implemented it badly, because you forced some particular way of working or method which they can’t use, so they worked around it.” According to the results, understanding the reason behind the non-compliance is important for most of the interviewed experts.

Security manager’s awareness of how security policy implementation affects users’ behaviour

Most of the interviewed security experts believe that they are to a certain degree aware of the impact of the security policy on users’ behavior. One security manager said: “Yes, I think I’m aware of that, because when it affects it in a negative way – we hear about it. There are lots of complains.” Some participants backed-up their statements with examples. One security manager mentioned: “When users want to look at Excel spreadsheet or use an application using iPad but they can’t, because security controls don’t allow access to the business applications via an iPad. So they have to use a laptop rather than device of their own choice. So yes, we are aware of that tension, but we tend to enable people to do what they need to do.” Interview results suggest that such awareness is in the direct relation to the number of users’ complains. However, nobody mentioned proactive way of assessing this impact.

Difficulties in measuring impact of users’ behaviour.

Several security experts stated that it is difficult to assess the impact of security controls on users’ behaviour. For example, one mentioned: “We never measured it. We don’t have a way of measuring it. So we don’t know.” Another expert agrees with him: “One thing is putting controls in place and the other is measuring effectiveness. Around users it is very difficult. Because they are not like a server, where you can say here is CPU optimisation.” However, one security expert strongly disagrees with the fact that he should take behavioural impact into consideration. He said that: “Why should I care? Why this is relevant to my job – caring about users is not part of my job responsibilities. I have limited resources to ensure compliance – how am I going to stretch that to areas outside of my direct responsibility?”

Security manager’s awareness of users’ typical business activities

Some security experts, who participated in the interviews, mentioned that they are aware of the users’ business task to the degree which is required to successfully manage projects. Once a security manager stated that: “At a high level we are aware. At the detailed process level really only when we are doing a project in that department. When we need to understand the process within the project.” Another expert provides an example supporting the same argument: “When we do a particular project on a new system. Say, for instance, it’s a new credit card system being implemented we work through the user’s role, we work through the general data storage, so we become familiar with that particular department’s user activities.” The results show that some interviewed security managers believe that they are capable of understanding of users’ day-to-day business activities and that they make their decisions on the particular implementation of security controls according to this knowledge.

Effect of understanding of users’ business activities on security manager’s decision-making process

All of the interviewed experts agree that knowledge of what users in their company are doing can help them in better implementation of information security policy. One security manager shared an example of that: “For instance we worked with our studio manager and looked at the process of data transfer to the client. We have chosen one particular brand of encrypted USB keys, we believe that adoption would be very high, because they are great looking devices. It feels good for our creative workers to give it to the client with our logo on it, rather than sharing data using cheap plastic USB stick – there is no story, there is no sort of emotional attachment, which is so particularly important for creative workers. But in order for us to come with such a decision we actually spend some time observing and understanding our users.”

Conclusion

The results show that the majority of security managers, who participated in the survey, understand the importance of making the user part of the system and assessing possible impact on users’ behaviour when deciding on implementation of particular security controls. However, they agree on that their awareness of users’ business activities is reactive and based mainly on the users’ complains. Small number of interviewed security experts makes it problematic to generalise the results. Moreover, all of the interviewed security managers have substantial amount of work experience (they were chosen to have minimum seven, however some of them have more than twenty years of experience), which may affects the results. Those security experts tend to work in the companies with mature information security processes in place. Interviewing expects with less amount of experience may yield different results.

Discussion

Results of this section provide an insight on how security managers and users view the importance of compliance behaviour in organisations. Analysis of the interview and survey results show that presented method is capable of identifying the existence of the problem: there is a huge gap between perception of security policy by users and security managers, which negatively impacts the organisation as a whole. Most of the interviewed security managers think that they consider users part of the system and aware of the impact of their action on users’ behaviour. However, survey results indicate that more that 23% users believe that security negatively affects their performance. Moreover, 20% of participants spend approximately one hour weekly on various security activities. Current interview and survey data suggests a difference in the perception of the users and security managers exists due to the differing opinions presented, but doesn’t prove this is the case and the information comes from different contexts. Running the study inside an organisation would overcome this limitation. The issue the difference in the perception of the users and security managers should be studied more thoroughly. The study should be conducted in one company to directly compare the view of managers and users from the same organisation, which is critical to showing if a difference in opinion really exists. Moreover, the research should be conducted with a broader and better-quality sample to ensure that the results could be generalised. More participants from various backgrounds should form the sample.

Security compliance behaviour conflicts resolution model

This article presents the model for analysis and visualisation of a company’s security policy building on the example scenario in relation to productive business activities.

The model aims to provide the means of comparing the perception of security tasks from both users’ and security managers’ points of view and optimising security activities in the company.

A guide for the security manager

On the one hand, violation of compliance requirements may result in significant losses for an organisation. On the other hand, poorly implemented security policies may obstruct users’ goal-driven behaviour and may result in non-compliance.

The scenario suggests that the CISO takes ISO 27001 as a framework and then makes a decision on a particular implementation based on his knowledge and past experience. As illustrated by the scenario lack of clear guidance in this decision-making process may result in the situation in which a company is formally compliant with the standard but users perform their core business activities inefficiently and/or are forced to violate poorly implemented security policies.

By directly comparing security requirements and business processes, the security manager can analyse ISO 27001 policy compliance controls and their consequences in terms of affecting user behaviour.

In order to ensure that users in the organisation will comply with security policies, the security manager should broaden his perspective and make users a part of the system. It is important to differentiate between malicious non-compliance and cases when security policy obstructs core business process.

Policy compliance
Yes No
Primary task optimised Yes V (X)
No (V) X

Relation between policy compliance and optimisation of the primary task

“V” – CISO is satisfied with users’ compliance efforts.

“X” – CISO is not satisfied with users’ compliance efforts.

“(X)” – the case when users perform their tasks efficiently, but not compliant with security policy.

“(V)” – the case when users are formally compliant with security policy, but it prevents them from carrying out their tasks efficiently.

The table emphasises the fact that regardless of formal compliance, users’ perform their core business activities in the inefficient manner due to poorly implemented security controls. The security manager also should pay attention to cognitive burdens and availability aspects of recommended solutions.

In order to mitigate the risk of poor implementation of security controls, the security manager should follow clear processes when implementing ISO 27001 controls.

process

Such guidance supports the security manager’s decision-making process. This method also gives the security manager an opportunity to reflect on his policy implementation in the context of the particular scenario.

Going beyond formally ensuring compliance, this method presents two rounds of compliance checks:

–       Check if organization is compliant (formal box-ticking exercise)

–       Check for collisions with core users’ tasks.

Visualisation technique

In order to minimise the probability of repeating scenario the security manager should pay more attention to users’ day-to-day business activities.

As a first step of the process, the security manager should gain an insight on users’ typical business activities. After understanding typical business activities, the security manager could visualise them for example in form of the workweek schedule.

main_BP

User’s main business process

For instance, the security manager finds out that the analyst runs data analysis software to model risks on Thursday to include this data in his report, which he usually presents at the end of each week to the client.

Furthermore, by gathering information on users’ manual security tasks, the information security manager estimates current users’ workload.

manual

User’s manual security tasks

The information security manager identifies unique security tasks that users undertake during the week and use this information to make those tasks invisible to user. In this case, users would feel less obstructed in completing business tasks. But those activities are still taking place in the background. Only by identifying them, mapping them, and prioritising them could the security manager then do something about them.

Next, as a part of security pre-implementation process of security controls, the security manager looks at scheduled security activities, such as periodic security awareness workshops, review of software and data on users’ workstations or full machine antivirus scans.

scheduled

Scheduled security activities

Merging all these diagrams together helps the security manager to understand total users’ workload and come up with a more effective implementation of security controls, which will not introduce collisions with core security tasks.

total

Total user’s workload

In order to make a decision on a particular implementation of security controls, the security manager should identify how users in his company perceive their security workload and which security tasks they carry out already.

At the moment, there is a possibility to of misconception of perceptions of security tasks of security managers and users. Developed model addresses this issue and helps the CISOs to manage their decision-making process more effectively. Moreover, comparing the security manager’s and users’ perceptions helps to uncover a number of unique security activities, and the amount of time users spend on them.

Validation of the model

The purpose of this section is to validate the model and gather relevant feedback from information security experts.

Method

An interview questionnaire was developed to interview information security experts and collect their opinion on the developed model.

Written consent was collected prior to the interview to explain ethical and privacy points. Additionally, permission to use voice-recording device was obtained for future analysis.

Information, regarding interview procedure, intended questions and brief overview of the study were sent to all participants in advance via e-mail. At least 2 days were allowed for participants to examine the materials and prepare for the interview.

Five interviews were conducted out with information security experts. Every interview took place at participant’s office and at convenient time.

Feedback, provided by information security experts was documented and analysed according to grounded theory method. The following codes were identified:

–       Degree of realistic implementation

–       Potential benefits

–       Business advantages

–       Practical implementation

–       Impact on security manger’s decision-making process

–       Other ways of dealing with the similar issues

–       Drawbacks of the model.

Results

Information in this section is presented according to codes, which were discovered during interview process and further data analysis.

  1. Degree of realistic implementation: all security managers agree that developed model is realistic and can be implemented in the real-world company.
  2. Potential benefits: all interviewed experts believe that the model is beneficial to their organizations.
  3. Business advantages: 3 out of 5 security experts were able to name possible economic advantages of implementing the model.
  4. Practical implementation: 2 out of 5 interviewed security managers agreed to run pilot testing of the model in their organisation.
  5. Impact on security manager’s decision-making process: 4 out of 5 interviewed experts stated that presented model changed their attitude towards compliance behaviour issues. One security manager commented that this model doesn’t affect his decision-making process.
  6. Other ways of dealing with the similar issues: no other ways of dealing with issues of impact of users’ behaviour in a proactive manner were presented.
  7. Drawbacks of the model: all interviewees agree that implementation of the model might be time- and resource-consuming.

Discussion

This section presents a discussion of interview findings.

Degree of realistic implementation

All the interviewed experts agree that the model could be implemented in the real-world scenario, but commented that it should be refined and validated with the real data. For example, one security manager said:

“I think the approach is sound and it’s realistic, but needs validation with the real data. And in the absence of the real data it’s got rather limited value.”

Another expert commented:

“I think that’s all sounds very interesting. You are definitely on the right track, but you need to collect more data to validate this model.”

Another security manager said:

“I believe it is realistic if it works, it will be relevant to any business. I don’t think many have considered practically addressing this dimension of security in their organisations.”

Potential benefits

Security experts can see the potential benefits of implementing developed model in their companies. For instance, one expert said:

“I think that issue of usability and security is really important. Understanding where those tensions are and then represent those tensions might in some way help us to understand the cost associated with mitigating the risk.”

Another security manager commented:

“This model might help us to highlight where we can be creative and do something slightly different to make it easier for users to do what they want to do and do it in the default secure way. So yes, anything that can help us shed light on that going to be beneficial.”

One expert said:

“I think it’s beneficial, because it allows you to channel these thought about users’ workflow versus your workflow. How we squeeze security tasks all together with business activities.”

Business advantages

According to the experts, developed model yields some direct economic benefits for the company. For example, one security manager suggested:

“It is a very relevant model also from resource management perspective. How is my staffs’ time being utilised? Am I utilising my staff for the best? ”

One security expert suggested, that presented model can help him to make better decisions regarding risk assessment and investments in information security controls:

“It can be very valuable input into our risk assessment process and into our security investment decision-making process. Do we want to invest in one security tool or the other? Your model can provide means to compare security investment opportunities.”

Another expert agrees:

“You can understand what the business process is and what security solution would fit the best in order to maximise value.”

Another security manager’s quote supports the same point:

“Security really struggles to justify return on investment. What you could do is if you actually will break it down, saying that during the day typical user spends thirty minutes doing security activities. That cost, say 2 million pounds for a user. Does this security control bring 2 million worth saving in a year? If yes, or more, then it worth it. If no, then maybe you are doing the wrong controls. When maybe you should accept the risk. For example, yes maybe USB stick may introduce a virus to the system. Fine, but don’t spend five minutes every time scanning it.”

Practical implementation

Some security managers agreed to run a pilot test in his company. One expert commented:

“It provided a different prospective on security – we have not considered how specific security controls may affect user behavior and productivity. I would be happy enough to run it as a small pilot to see if it yields promised results.”

Another said:

“If it could be used as a means to ensure greater user efficiency/reduced non-compliance, we could consider including it in our security review.”

This indicates that the model could be implemented in the real-world companies for the future analysis.

Impact on security manger’s decision-making process

The majority of security mangers mentioned that presented model made them realise the impact of their actions on users and how they might struggle with particular security controls they implemented in the company.

Some security mangers came up with particular scenarios of how they would now make decision on implementation of security controls: On expert said: 

“As a result you can make a decision to implement a technology solution that going to scan all the USB sticks in the background, rather than making each and every user do it manually. The cost of such implementation would be justified by you model. It will save user’s time and you can get security benefit as well.”

However, one security manager confessed that this model would not change the way he makes decision on security policy implementation:

“If it ain’t broken – don’t fix it! If the process we have in place is already compliant, I will not risk changing it just to satisfy the users who are not complaining anyway.”

The results imply that developed model helped most of the security managers to change their attitude towards compliance behaviour in their companies.

Other ways of dealing with the similar issues

All of the interviewed security managers agree that they are not actively dealing with issues of negative impact of security controls on users’ performance. One expert said:

“It’s very passive. The impact on users is important but it’s not the issue I spend a lot of time thinking about.  Our approach is more reactive. The model presented, on the other hand, is more proactive technique.”

Another commented:

“Very informally. We don’t really draw on a real data. I think, having a framework of some description would be very useful. Something that focuses that kind of thinking.“

One security manager said that he never considered users being part of the system, hence never used any techniques, as mentioned in the following quote:

“We never considered user compliance from this perspective before – so have not considered / applied alternative principles.”

Drawbacks of the model

All interviewees agree that implementation of the model might be time- and resource-consuming. One expert commented:

“You need an easier way to implement it – that’s the biggest challenge. Because you need to come up with all users’ business tasks, then all security tasks, and then map them all together. All these things have to also be categorised and measured. And humans a very difficult to measure.”

Another manager mentioned:

“Getting it implemented I see as a big challenge. But once it’s implemented you can get a really good value.”

Another commented:

“The method is very good, but it takes a lot of effort to compile this.”

Despite identified possible benefits, the model is considered to be difficult to implement. Cost-benefit analysis could be performed to support the decision on the implementation of the model.

Conclusion

According to the security experts, the model can yield additional benefits to the company, such as optimisation of security activities, cost reduction, and information security projects investment justification.

The interview results reveal the main benefit of the model: it points a security manager in the direction of a better understanding of the users in his company.  It provides the means to gain an insight into users’ core business activities and reflect on how they relate to the security tasks. This can help security managers to come up with more usable security policies and reduce the number of potential complaints, and instances of violation of security policy.

As some of the interviewees suggested, the security manager can implement this model in any company: all he has to do is to pick a process, pick a regulation and then apply the model.  Moreover, this model can help the security manager to understand how much time users in his company spend on various security activities. This information can be used to make better investment decisions, and help in security policy optimisation. Additionally understanding that the security manager’s compliance decisions affect the whole organisation may result in cost savings from pre-implementation security analysis and its relation to main business processes of the company.

Despite the potential benefits, the model has drawbacks. Interview results suggest that implementation of the model might be cost- and resource-consuming. To assess the degree of such problem, real-world data should be collected. Moreover, as one expert mentioned, the model has limited value in the absence of the real data. The limited time scope of the current project didn’t allow the validation of the model with such data. Furthermore, access to the real data was restricted due to protective attitude of the companies who don’t want to be seen in bad light.

Attitudes towards information security policy and its effect on users’ business activities should be measured before and after implementing the model in the company in order to assess the effectiveness of the model.