Security and Usability

Many employees find information security secondary to their normal day-to-day work, often leaving their organisation vulnerable to cyber attacks, particularly if they are stressed or tired. Leron Zinatullin, the author of The Psychology of Information Security, looks at the opportunities available to prevent such cognitive depletion.
2141071329_9097e63c06_o

When users perform tasks that comply with their own mental models (i.e. the way that they view the world and how they expect it to work), the activities present less of a cognitive challenge than those that work against these models.

If people can apply their previous knowledge and experience to a problem, less energy is required to solve it in a secure manner and they are less mentally depleted by the end of the day.

For example, a piece of research on disk sanitisation highlighted the importance of secure file removal from the hard disk.[1] It is not clear to users that emptying the ‘Recycle Bin’ is insufficient and that files can easily be recovered. However, there are software products available that exploit users’ mental models. They employ a ‘shredding’ analogy to indicate that files are being removed securely, which echoes an activity they would perform at work. Such an interface design might help lighten the burden on users.

Security professionals should pay attention to the usability of security mechanisms, aligning them with users’ existing mental models.

In The Laws of Simplicity,[2] John Maeda supports the importance of making design more user-friendly by relating it to an existing experience. He refers to an example of the desktop metaphor introduced by Xerox researchers in the 1980s. People were able to relate to the graphical computer interface as opposed to the command line. They could manipulate objects similarly to the way they did with a physical desk: storing and categorising files in folders, as well as moving or renaming them, or deleting them by placing them in the recycle bin.

Using mental models

Building on existing mental models makes it easier for people to adopt new technologies and ways of working. However, such mappings must take cultural background into consideration. The metaphor might not work if it is not part of the existing mental model. For instance, Apple Macintosh’s original trash icon was impossible to recognise in Japan, where users were not accustomed to metallic bins of this kind.

Good interface design not only lightens the burden on users but can also complement security. Traditionally, it has been assumed that security and usability always contradict each other – that security makes things more complicated, while usability aims to improve the user experience. In reality, they can support each other by defining constructive and destructive activities. Effective design should make constructive activities simple to perform while hindering destructive ones.

This can be achieved by incorporating security activities into the natural workflow of productive tasks, which requires the involvement of security professionals early in the design process. Security and usability shouldn’t be extra features introduced as an afterthought once the system has been developed, but an integral part of the design from the beginning.

Security professionals can provide input into the design process via several methods such as iterative or participatory design.[3] The iterative method consists of each development cycle being followed by testing and evaluation and the participatory method ensures that key stakeholders, including security professionals, have an opportunity to be involved.

References:

[1] S. L. Garfinkel and A. Shelat, “Remembrance of Data Passed: A Study of Disk Sanitization Practices”, IEEE Security & Privacy, 1, 2003, 17–27.

[2] John Maeda, The Laws of Simplicity, MIT Press, 2006.

[3] For iterative design see J. Nielsen, “Iterative User Interface Design”, IEEE Computer, 26(11) (1993), 32–41; for participatory design see D. Schuler and A. Namioka, Participatory Design: Principles and Practices, CRC Press, 1993.

Image by Rosenfeld Media https://www.flickr.com/photos/rosenfeldmedia/2141071329/


To find out more about the psychology behind information security, read Leron’s book, The Psychology of Information Security. Twitter: @le_rond
How employees react to security policies

8205162689_345cce5b75_o

Information security can often be a secondary consideration for many employees, which leaves their company vulnerable to cyber attacks. Leron Zinatullin, author of The Psychology of Information Security, discusses how organisations can address this.

First, security professionals should understand that people’s resources are limited. Moreover, people tend to struggle with making effective decisions when they are tired.

To test the validity of this argument, psychologists designed an experiment in which they divided participants into two groups: the first group was asked to memorise a two-digit number (e.g. 54) and the second was asked to remember a seven-digit number (e.g. 4509672).[1] They then asked the participants to go down the hall to another room to collect their reward for participating. This payment, however, could be only received if the number was recalled correctly.

While they were making their way down the corridor, the participants encountered another experimenter, who offered them either fruit or chocolate. They were told that they could collect their chosen snack after they finished the experiment, but they had to make a decision there and then.

The results demonstrated that people who were given the easier task of remembering a two-digit number mostly chose the healthy option, while people overburdened by the more challenging task of recalling a longer string of digits succumbed to the more gratifying chocolate.

The implications of these findings, however, are not limited to dieting. A study looked at the decision-making patterns that can be observed in the behaviour of judges when considering inmates for parole during different stages of the day.[2]

Despite the default position being to reject parole, judges had more cognitive capacity and energy to fully consider the details of the case and make an informed decision in the mornings and after lunch, resulting in more frequently granted paroles. In the evenings, judges tended to reject parole far more frequently, which is believed to be due to the mental strain they endure throughout the day. They simply ran out of energy and defaulted to the safest option.

How can this be applied to the information security context?

Security professionals should bear in mind that if people are stressed at work, making difficult decisions, performing productive tasks, they get tired. This might affect their ability or willingness to maintain compliance. In a corporate context, this cognitive depletion may result in staff defaulting to core business activities at the expense of secondary security tasks.

Security mechanisms must be aligned with individual primary tasks in order to ensure effective implementation, by factoring in an individual’s perspective, knowledge and awareness, and a modern, flexible and adaptable information security approach. The aim should therefore be to correct employee misunderstandings and misconceptions that result in non-compliant behaviour, because, in the end, people are a company’s best asset.

References:

[1] B. Shiv and A. Fedorikhin, “Heart and Mind in Conflict: The Interplay of Affect and Cognition in Consumer Decision Making”, Journal of Consumer Research,  1999, 278–292.

[2] Shai Danziger, Jonathan Levav and Liora Avnaim-Pesso, “Extraneous Factors in Judicial Decisions”, Proceedings of the National Academy of Sciences, 108(17), 2011, 6889–6892.

Photo by CrossfitPaleoDietFitnessClasses https://www.flickr.com/photos/crossfitpaleodietfitnessclasses/8205162689

To find out more about the psychology behind information security, read Leron’s book, The Psychology of Information Security. Twitter: @le_rond
The Psychology of Information Security – Resolving conflicts between security compliance and human behaviour

ITGP

In today’s corporations, information security professionals have a lot on their plate. In the face of constantly evolving cyber threats they must comply with numerous laws and regulations, protect their company’s assets and mitigate risks to the furthest extent possible.

Security professionals can often be ignorant of the impact that implementing security policies in a vacuum can have on the end users’ core business activities. These end users are, in turn, often unaware of the risk they are exposing the organisation to. They may even feel justified in finding workarounds because they believe that the organisation values productivity over security. The end result is a conflict between the security team and the rest of the business, and increased, rather than reduced, risk.

This can be addressed by factoring in an individual’s perspective, knowledge and awareness, and a modern, flexible and adaptable information security approach. The aim of the security practice should be to correct employee misconceptions by understanding their motivations and working with the users rather than against them – after all, people are a company’s best assets.

I just finished writing a book with IT Governance Publishing on this topic. This book draws on the experience of industry experts and related academic research to:

  • Gain insight into information security issues related to human behaviour, from both end users’ and security professionals’ perspectives.
  • Provide a set of recommendations to support the security professional’s decision-making process, and to improve the culture and find the balance between security and productivity.
  • Give advice on aligning a security programme with wider organisational objectives.
  • Manage and communicate these changes within an organisation.

Based on insights gained from academic research as well as interviews with UK-based security professionals from various sectors, The Psychology of Information Security – Resolving conflicts between security compliance and human behaviour explains the importance of careful risk management and how to align a security programme with wider business objectives, providing methods and techniques to engage stakeholders and encourage buy-in.

The Psychology of Information Security redresses the balance by considering information security from both viewpoints in order to gain insight into security issues relating to human behaviour , helping security professionals understand how a security culture that puts risk into context promotes compliance.

It’s now available for pre-order on the UK, EU or US websites.

Secure by design

V4tS8p5F_C0

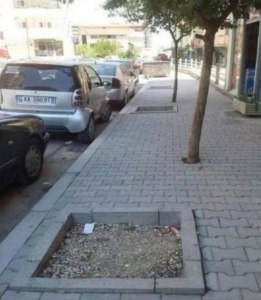
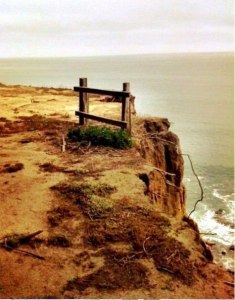
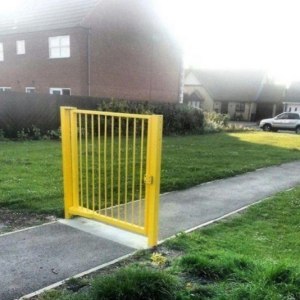
Have you seen security controls being implemented just to comply with legal and regulatory requirements? Just like this fence. I’m sure it will pass all the audits: it is functioning as designed, it blocks the path (at least on paper) and it has a bright yellow colour just as specified in the documentation. But is it fit for purpose?

It turns out that many security problems arise from this eager drive to comply: if the regulator needs a fence – it will be added!

Sometimes controls are introduced later, when the project is well passed the design stage. It might be the case that they just don’t align with the real world anymore.

n0saycKzykM

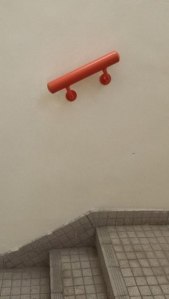
Safety measures, unfortunately, are no exception. The solution may be poorly designed, but more often, safety requirements are included later on with the implementation not fit for purpose.

IbHF452Usk0tuLB7kjBazs

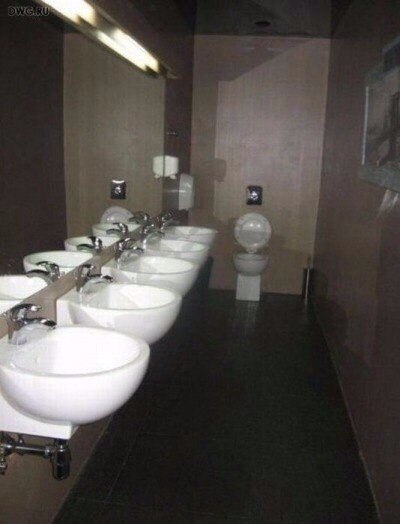
Same holds for privacy as well. Privacy professionals encourage to adopt the Privacy by Design principle. Is it considered on the image below?

2Tx1qKFQzfoB5nli4NoEG4

Database Security Project

ID-100187848

A company experienced a significant data breach from a malicious source which led to the loss of strategically sensitive information. I was called in to manage a security remediation project. Given that data at rest is a critical asset, remediating and hardening the company’s business critical databases was a key component of this program.

The client designed a solution for database security but was struggling to implement it and gain the required stakeholder buy-in. Furthermore, the client’s business critical landscape was highly dispersed – with application management spread across multiple business units based out of a number of countries and database management was overseen by third-party IT vendor.

I was a part of the project management team, which was established to coordinate multiple stakeholders in order to implement the end-to-end solution for database security consisting of monitoring, reporting and remediation of business critical databases.

I identified that the most significant obstacle was business application owner understanding of the system, the processes, and the benefits of implementation. I initially engaged in extensive stakeholder communication and business change management to ensure the required buy-in.

I drove the progress of system implementation through stakeholder management, delivery management, information gathering and providing technical expertise and management reporting. I worked within the client’s project management methodology whilst leveraging my experience and expertise in project management to ensure timely delivery.

As a result, the business critical databases in scope were brought into the known state of compliance, drastically reducing the attack surface. Moreover, awareness of the importance of application security and secure behaviours to support databases was raised significantly.

I embedded the processes to implement the system into the client’s run and maintain activities, ensuring that future changes to their business critical landscape do not introduce new database vulnerabilities. I also developed an asset inventory for business critical databases which improved upon any previous client efforts.

Image courtesy ddpavumba / FreeDigitalPhotos.net

PCI Data Security Standards Rock

The PCI Security Standards Council is an open global forum, launched in 2006, that is responsible for the development, management, education, and awareness of the PCI Security Standards, including the Data Security Standard (PCI DSS), Payment Application Data Security Standard (PA-DSS), and PIN Transaction Security (PTS) requirements.

The PCI Security Standards Council also develops and manages a number of programs to build awareness and to train, test, and qualify organizations and individuals to assess and validate adherence to PCI Security Standards.

They put together a short video explaining the basic principles.

Cake and Security

There is no doubt that security is necessary, but why is it so unpleasant to follow a security policy? Reminding yourself to stick to the rules feels like your partner telling you…. to eat your salad. You know they are right, but anticipating that bland taste and mindless chewing that awaits you simply puts you off. You decide to leave it for tomorrow, so much so that you never get to it.

Cakes, on the other hand, are yummy and require no effort whatsoever to indulge in our cravings for them. Nobody needs to force us to eat a piece.

In our day-to-day lives we prefer to do “cake” tasks without giving it a second’s thought. Things like storing confidential files on Dropbox or emailing them to our personal accounts…. you know, taking a little bite here and there. It’s “only for today”, “no biggie”… This one-time thing is so harmless, it’s like a comfort snack. We might later feel guilty that we bypassed a few “salad” controls. Maybe we used our personal USB drive instead of a company-issued encrypted one, but at the end of the day… who cares? Who will notice? As long as there is no dramatic impact on our health, a bite here or a bite there won’t cause any harm.

reward

And one day we realise that it’s not all rosy. The result of our laziness or lack of willpower eventually rears its ugly head when the doctor makes us stand on the scales and has a look at our blood pressure. So to add to your partner’s words of wisdom, is the doctor’s warning of an unhealthy present and a bleak future; something that would sound very similar during the company’s security audit.

“You have got to eat more salad and lay off the cakes!”

To make matters worse, even with our best intentions to have the salad at the office cafeteria, we discover that the one available is practically inedible. Pretty much like finding that the company’s secure shared drive doesn’t have the necessary space to store our files or that the encrypted pen drive is not compatible with the client’s Mac.

So if there are chefs coming up with ways to make salads more appealing, what can security professionals do to help us, the employees, maintain our “security diet”?

They could aim at making security more like a cake – effortless, even attractive, but still keep it as healthy as a salad. Sound simple? Perhaps not so much, but they should invest in usability studies to make sure that the secure solution is the easiest to use. It might involve discovering an entirely new culinary art on how to make a cake-tasting salad altogether. But if they fail to realise just how unpalatable the salads are to begin with, we should let them know. Security professionals need employees’ support.

Organisations are like families: everyone has to stay healthy, otherwise when a single member gets sick, the whole family is at risk of getting sick as well, whether it be catching an infectious disease or adopting an unhealthy lifestyle. It’s like having the slimmest, fittest family member refrain from adding biscuits to the grocery list in order not to tempt the couch-potatoes. It’s a team effort. In order for a company to stay healthy, everyone has to keep a healthy lifestyle of eating salad regularly, even when it is not that pleasant.

unpleasant but necessary measures

The whole company needs to know that security is important for achieving its goals -not as something that gets in the way-, just as we should all know that having a healthy diet of greens will guarantee a sound body. Employees contribute to the efficient operation of the business when they comply with security policies. Not only does security ensure confidentiality and the integrity of information, but it also guarantees that the resources are available for employees to complete their primary tasks.

We need to realise that we contribute to security; and we can inflict serious damage on a company when we don’t comply with security policies, no matter how insignificant or harmless they may seem. As employees, we are individually responsible for the organisation’s exposure to security risks just as we are responsible for exposing ourselves to illness. Our behaviour and daily regime significantly shape our quality of life, and our practices shape the quality of our business.

The health of the company is everyone’s business. Let’s all eat our salad while helping the security specialists to come up with better tasting ones.

Cyber Insurance: Managing the Risk

ID-100178628

Cyber insurance is a hot topic of many debates today. It is believed to be the long-awaited cure for high-impact security risks, especially in light of constantly evolving privacy legislation and disclosure obligations. But what actually is it?

Simply put, cyber insurance is a tool intended to mitigate the loss from information security incidents.  The decision to use it, however, should be based on rigorous risk management. Firstly, a company performs a risk assessment, during which information security risks are identified and logged. This can help the business to prioritise from a cost-benefit perspective. The company can then choose a risk treatment option: it can decide to accept, mitigate, avoid or transfer the risk.

Mitigation and acceptance are quite common approaches in the information security domain. Security professionals can implement a countermeasure to reduce the likelihood and impact of the threat. However, if it is not feasible to do so for economic reasons then the risk can be accepted. In the case of avoidance, businesses can decide not to perform the activity that exposes them to the risk. Lastly, information security risk can be transferred to a third party. This is where cyber insurance can be useful.

The ownership of risk, however, can’t be transferred fully. In the case of cyber insurance, it is more about risk sharing. Both parties should understand their accountability, liability and risk allocation.

Cyber insurance should be cost-effective. But how can one calculate the cost of such product?  To understand this, we might want to look how insurance brokers work in more traditional areas. Insurance companies rely heavily on historical data, demographics and averages. The car insurance industry, for example, has evolved over many years to collate accurate statistics of the frequency of accidents per driver based on age, season, car type, country etc. in order to predict the likelihood and cost impact on a case by case basis.

For cyber insurance, however, historical data is not always readily available. Understanding the business becomes key to determining the cost. There are many parameters which can define the premium: size, territory, type of business, human errors and other unknown factors can all contribute to the price. Premiums rely on the maturity of the information security programme.

But is it possible to reduce this cost?

Yes, there are many ways to achieve cost reduction. In general, it is required for the business to demonstrate that some measures have already been taken to reduce the likelihood and impact of a potential cyber security incident. Certifications, such as ISO 27001 can be one of the ways to do so. Or for instance, having an incident response team can drive the premium down. Otherwise the insurer would have to provide its own service, hence charge the client extra. In a nutshell, premiums are never fixed. It has to be a dialogue between the company and the insurance broker. If a company adequately understands its risk, the insurance premium can and should be negotiated.

It is important to mention the importance of a holistic approach to risk treatment. Implementing controls to prevent security incidents and purchasing cyber insurance are not mutually exclusive strategies. If cost-effective, risk management and treatment should be a combination of both methods. Consider health and safety policies as an example. Safety coordinators invest in fire extinguishers minimise the impact of fire. Just like information security professionals deploy firewalls to keep malicious intruders out of the company’s network. Additionally, the building is also almost always insured. Maybe it is time to consider a similar approach to information systems.

Image courtesy of Stuart Miles / FreeDigitalPhotos.net

Presenting at the ISACA London Chapter event

Goal

I shared some research findings with the ISACA London Chapter members at the November event. We discussed resolving conflicts between security compliance and human behaviour. The talk was followed by a panel discussion with other presenters, where I answered questions regarding human aspects of information security.

During the networking session after the presentation I’ve had many other interesting conversations with the participants. People were sharing their stories and experiences implementing and auditing security controls.

The video of the talk is available on the ISACA London Chapter website.

Find out how security controls affect productivity in your company


speedometer

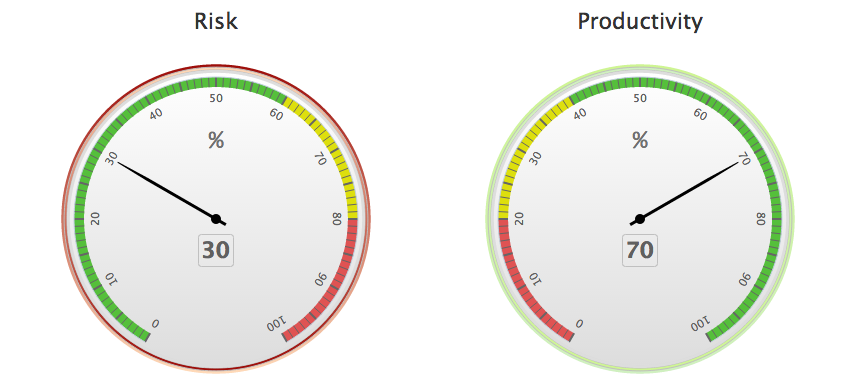
To expand on my research on the human aspect of security, I created a simplified model to highlight the relationship between productivity and security. The main hypothesis, is that there is a productivity cost associated with the security controls.

The interactive simulation was created to allow users to implement their own security policies and observe the relationship between risk reduction and impact on productivity cost. Easy to understand visual feedback is available immediately for the users. This helps to understand security managers’ perspective when implementing security controls in a company.

The creation of the model was inspired by research conducted by Angela Sasse and her colleagues at the University College London.

Please get in touch if you have any feedback or would like to discuss the underlying research findings.