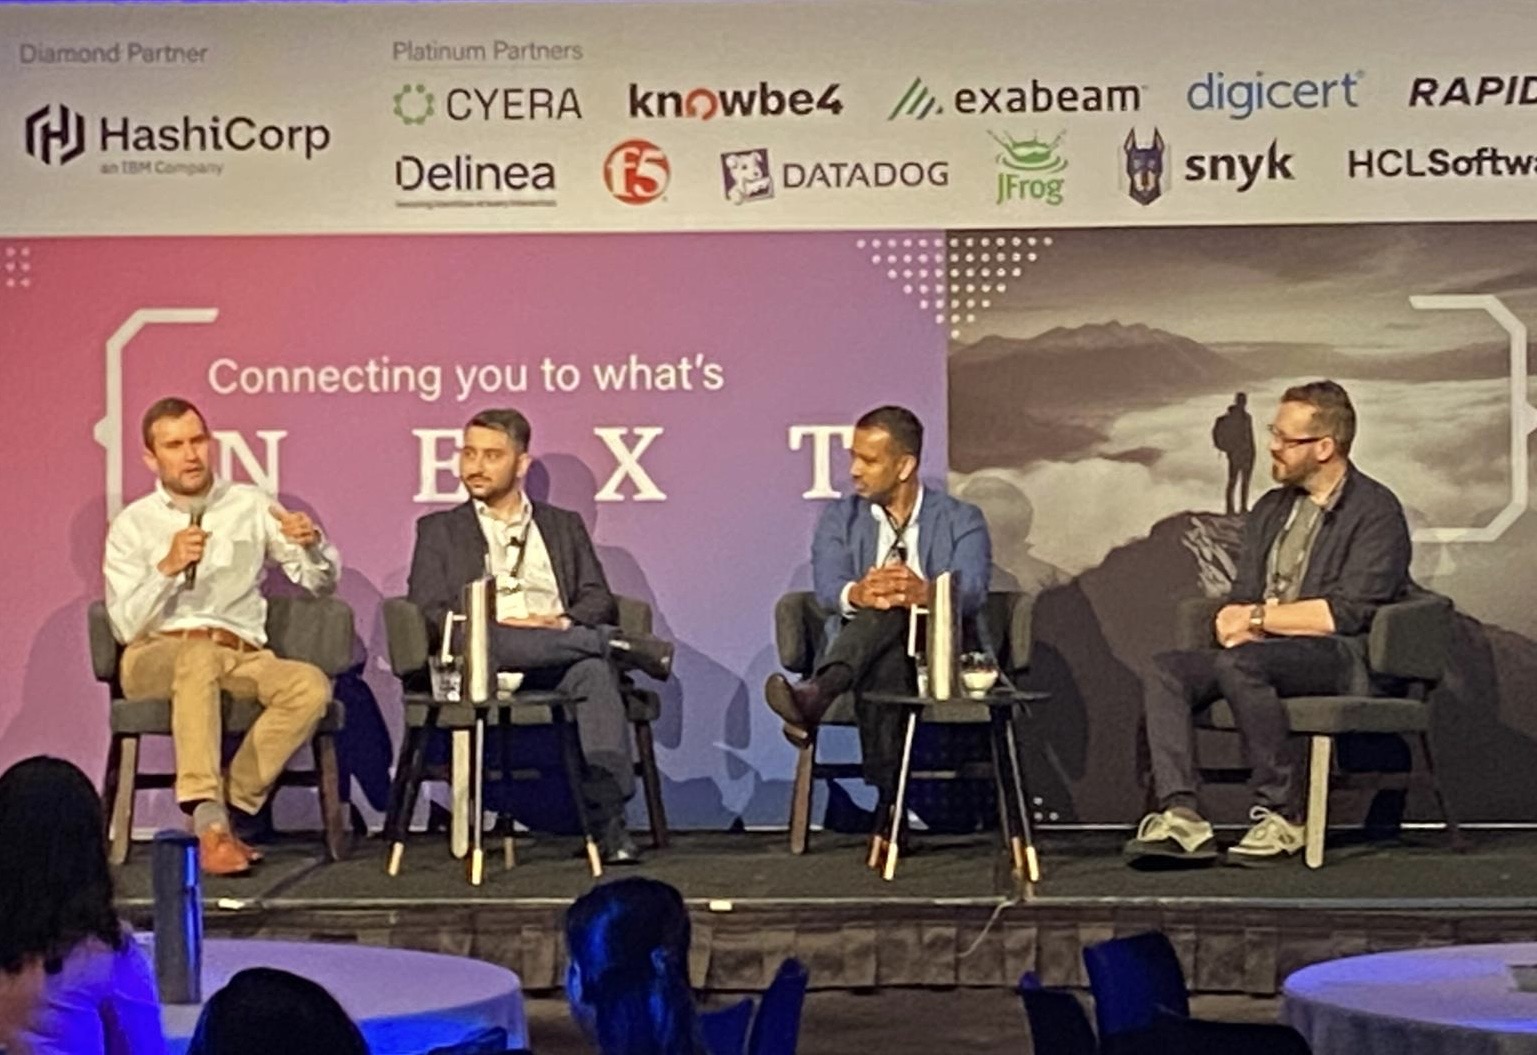
Governing AI – where should we draw the line?

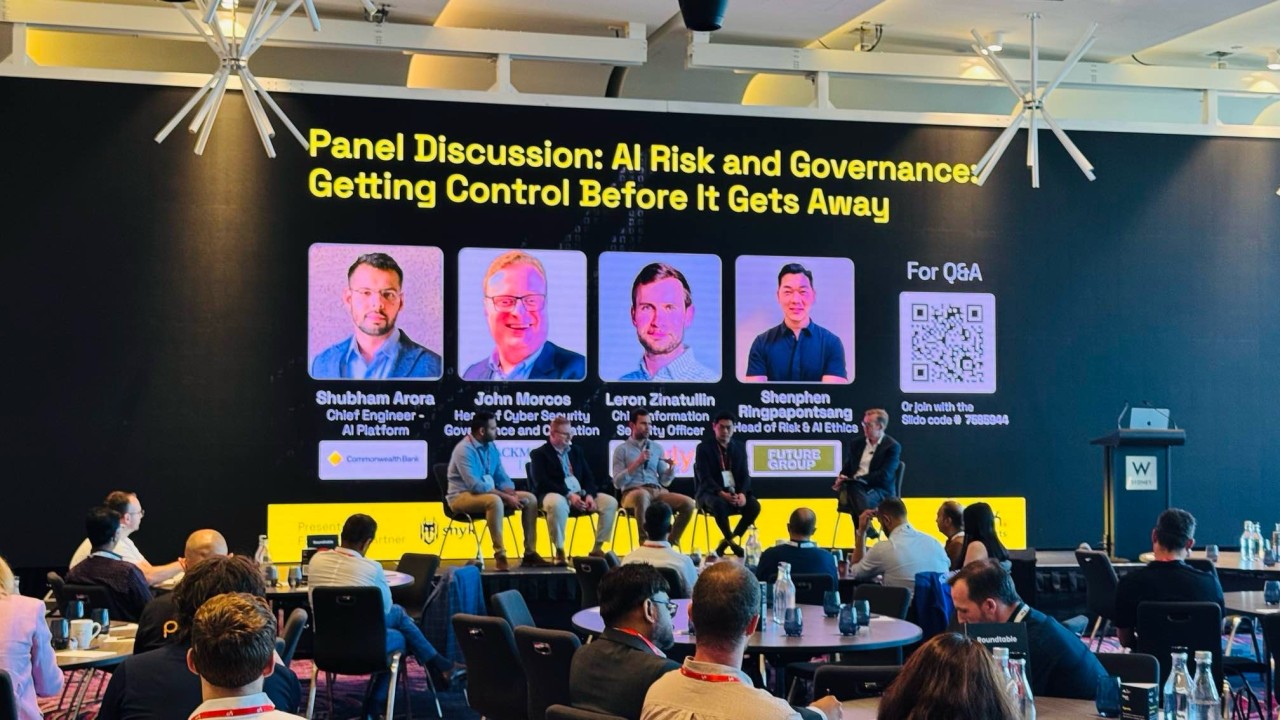
As AI adoption accelerates, leaders face the challenge of setting clear boundaries, not only around what AI should and shouldn’t do, but also around who holds responsibility for its oversight.

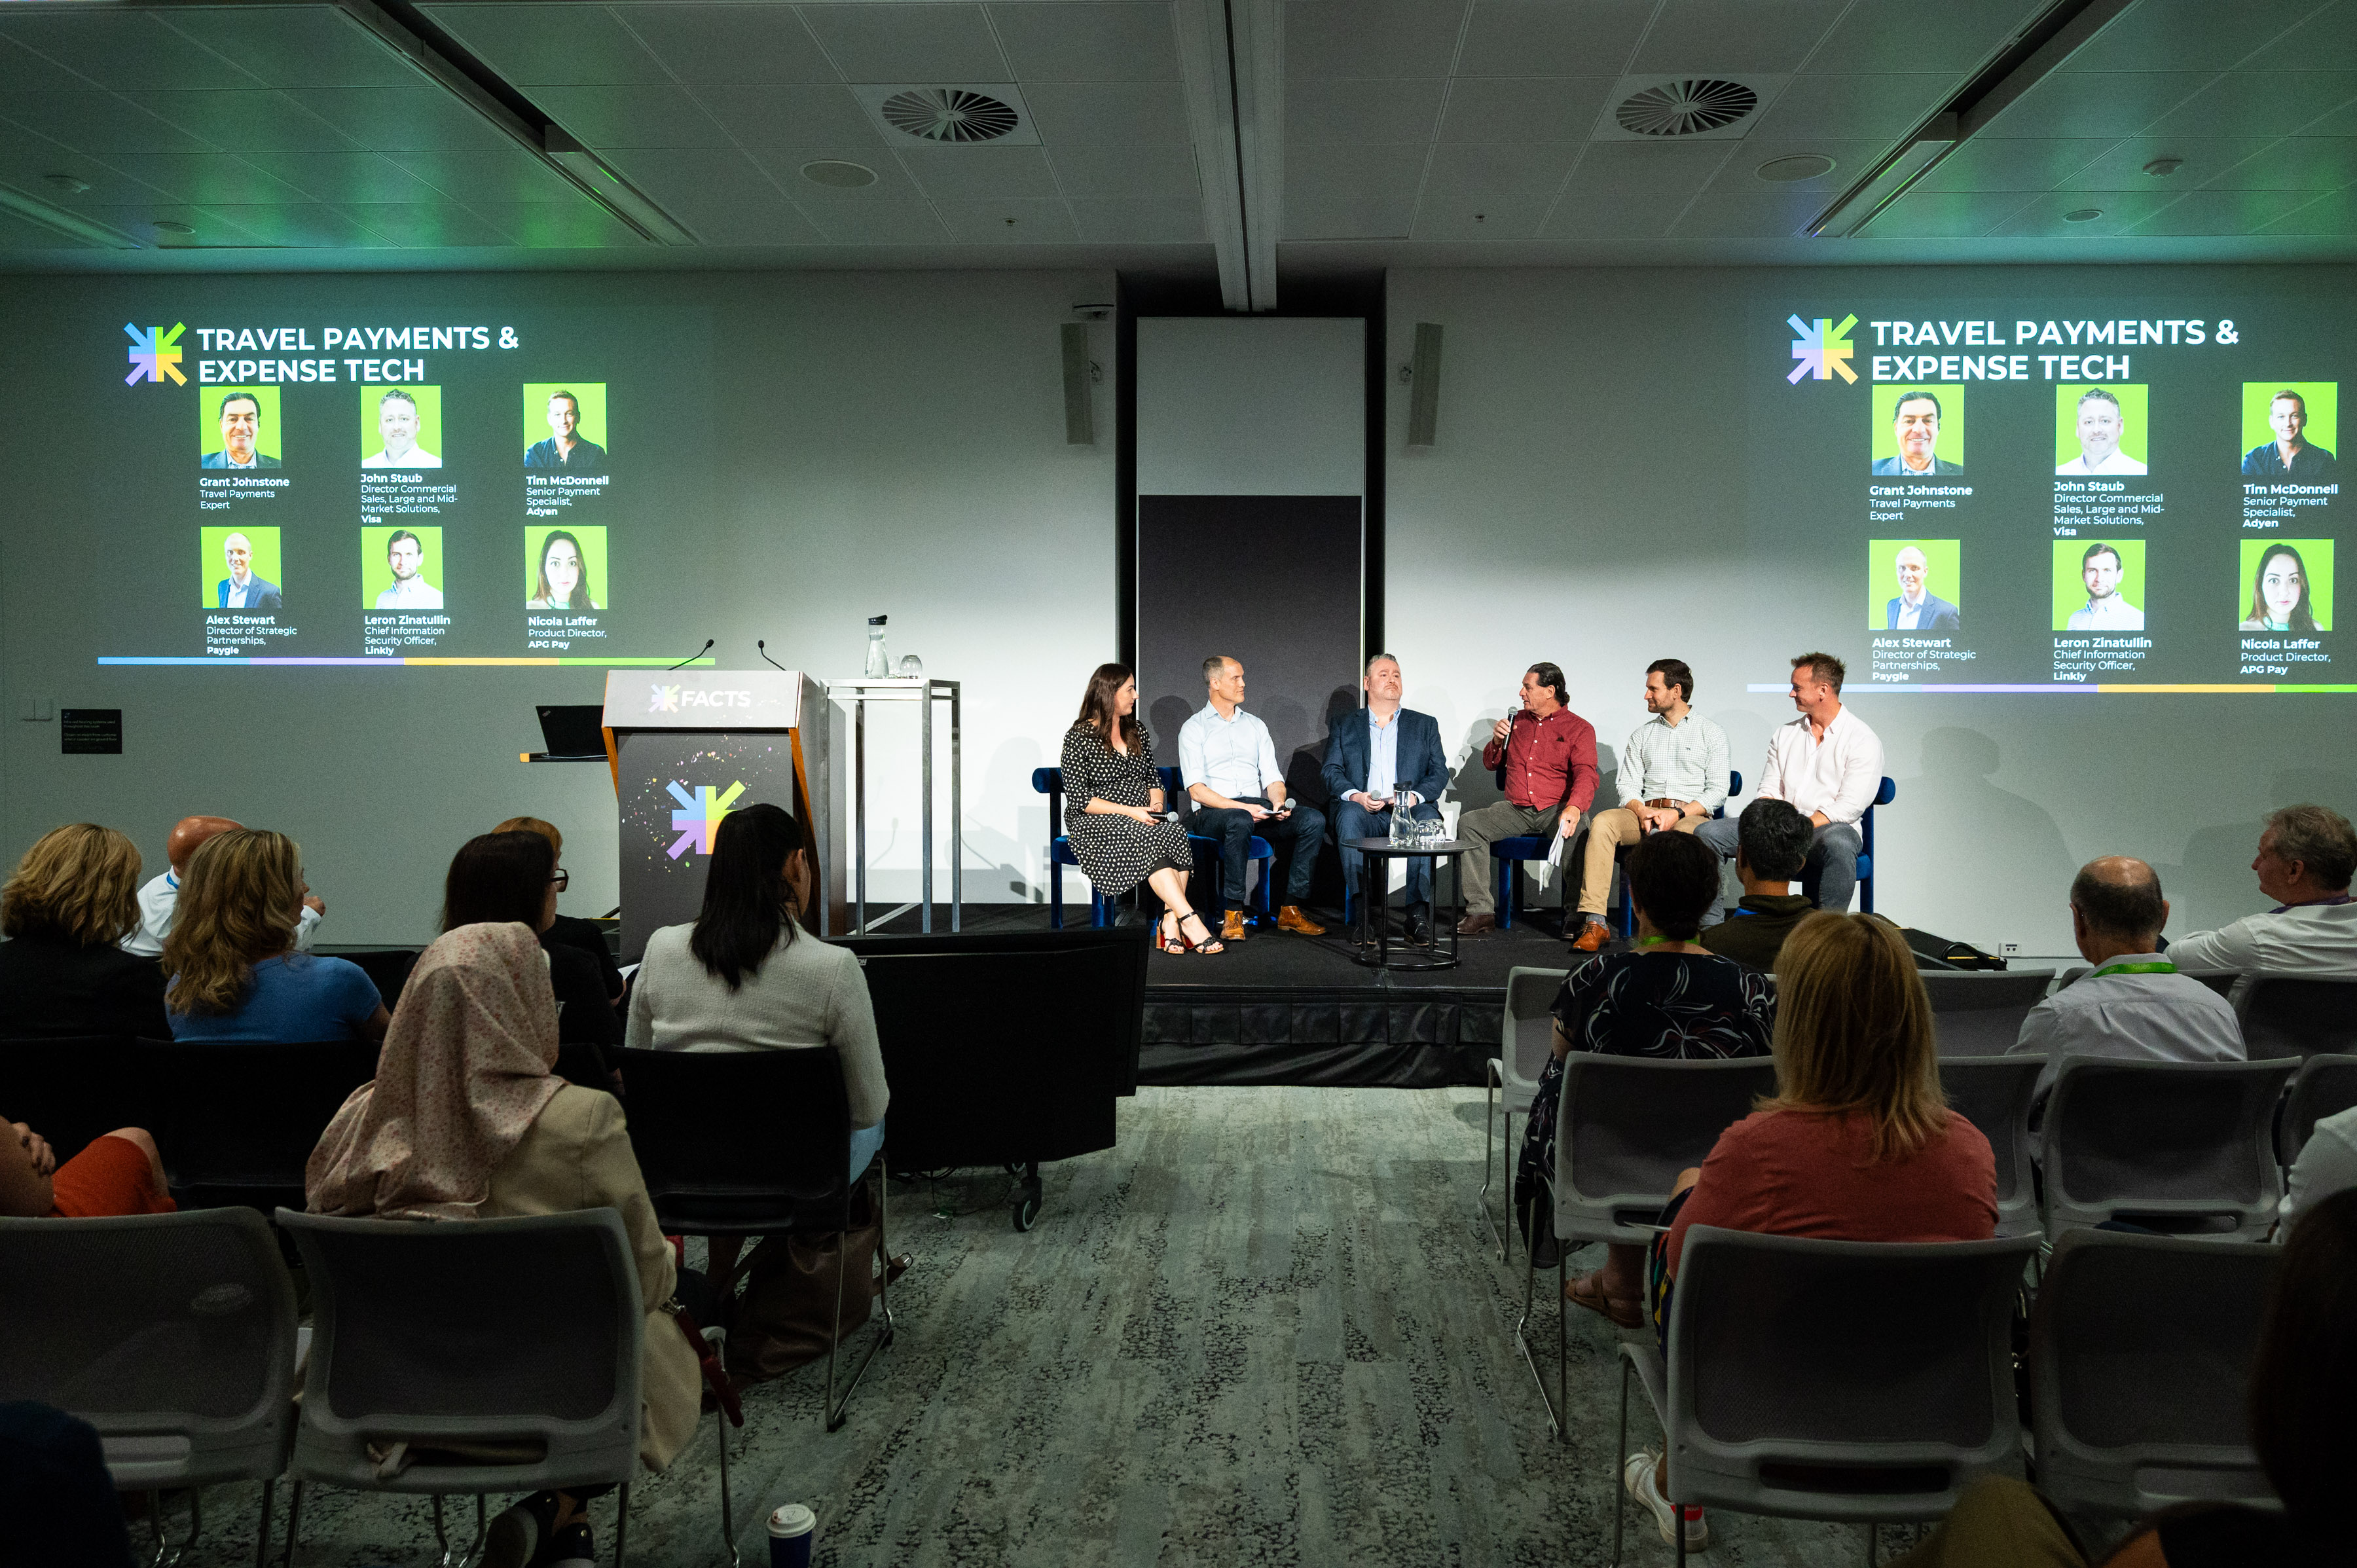
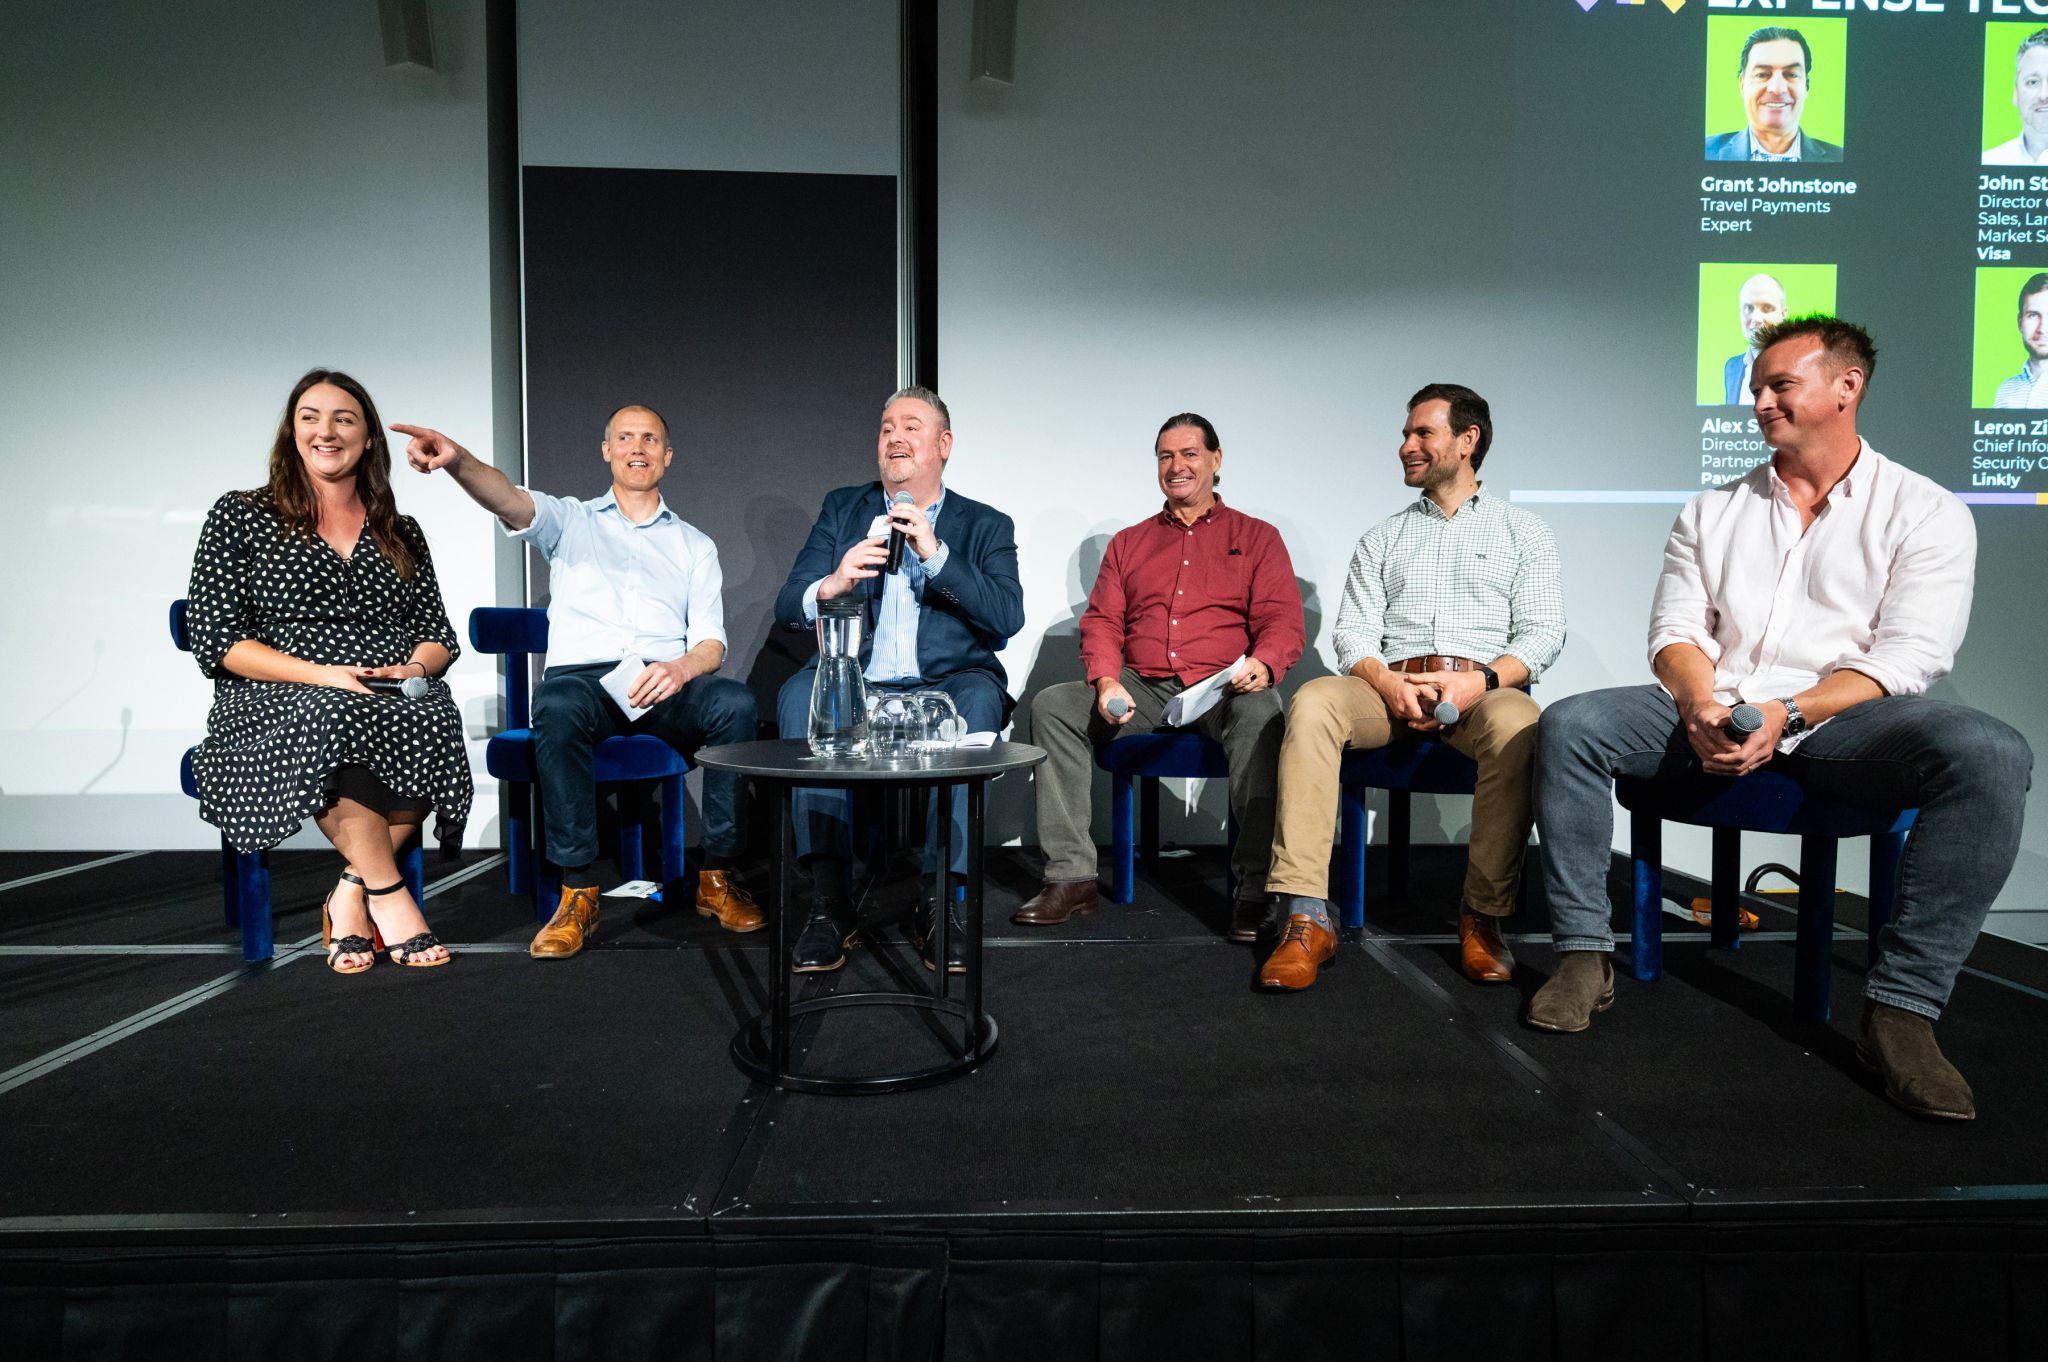
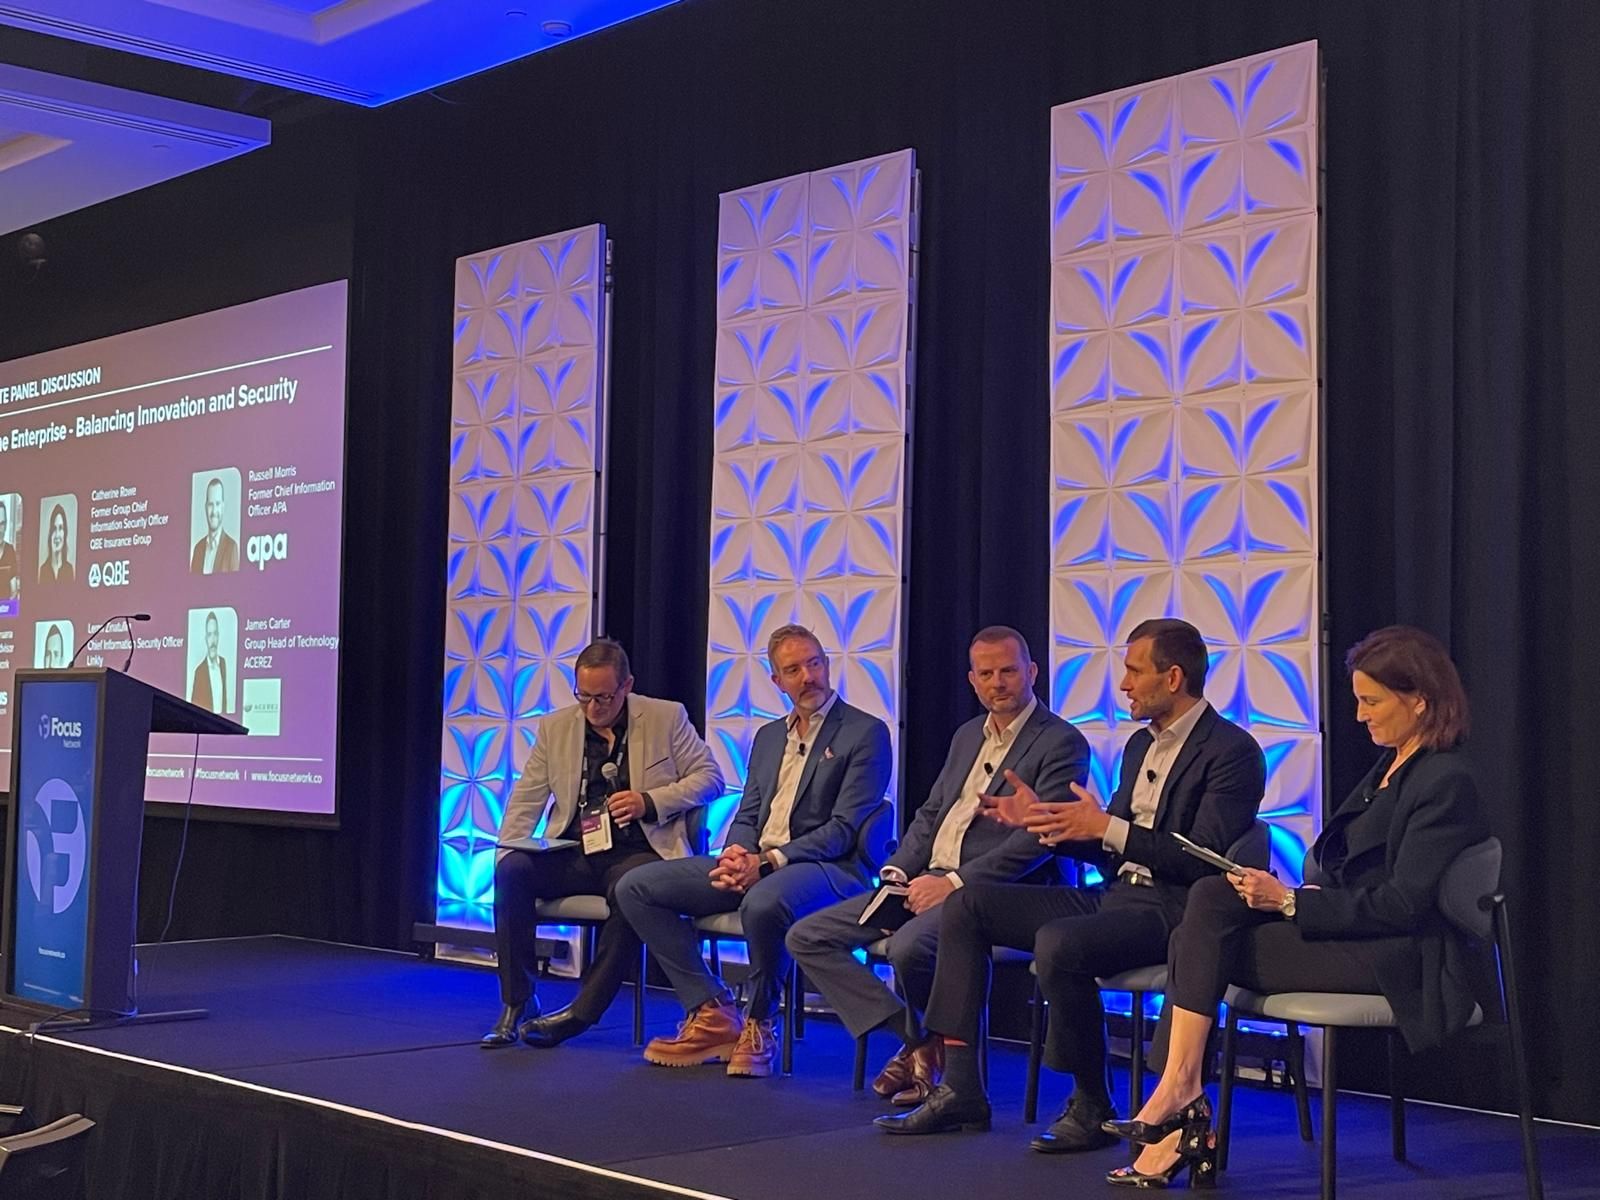
It was great to share my thoughts and answer audience questions during this panel discussion.

Governance must be cross-functional: security, risk, data and the business share accountability. I also reinforced the importance of guardrails, particularly forAgentic AI: automate low-risk work, but keep humans in the loop for decisions that affect safety, rights or reputation. Classify models and agents by impact and apply controls accordingly.
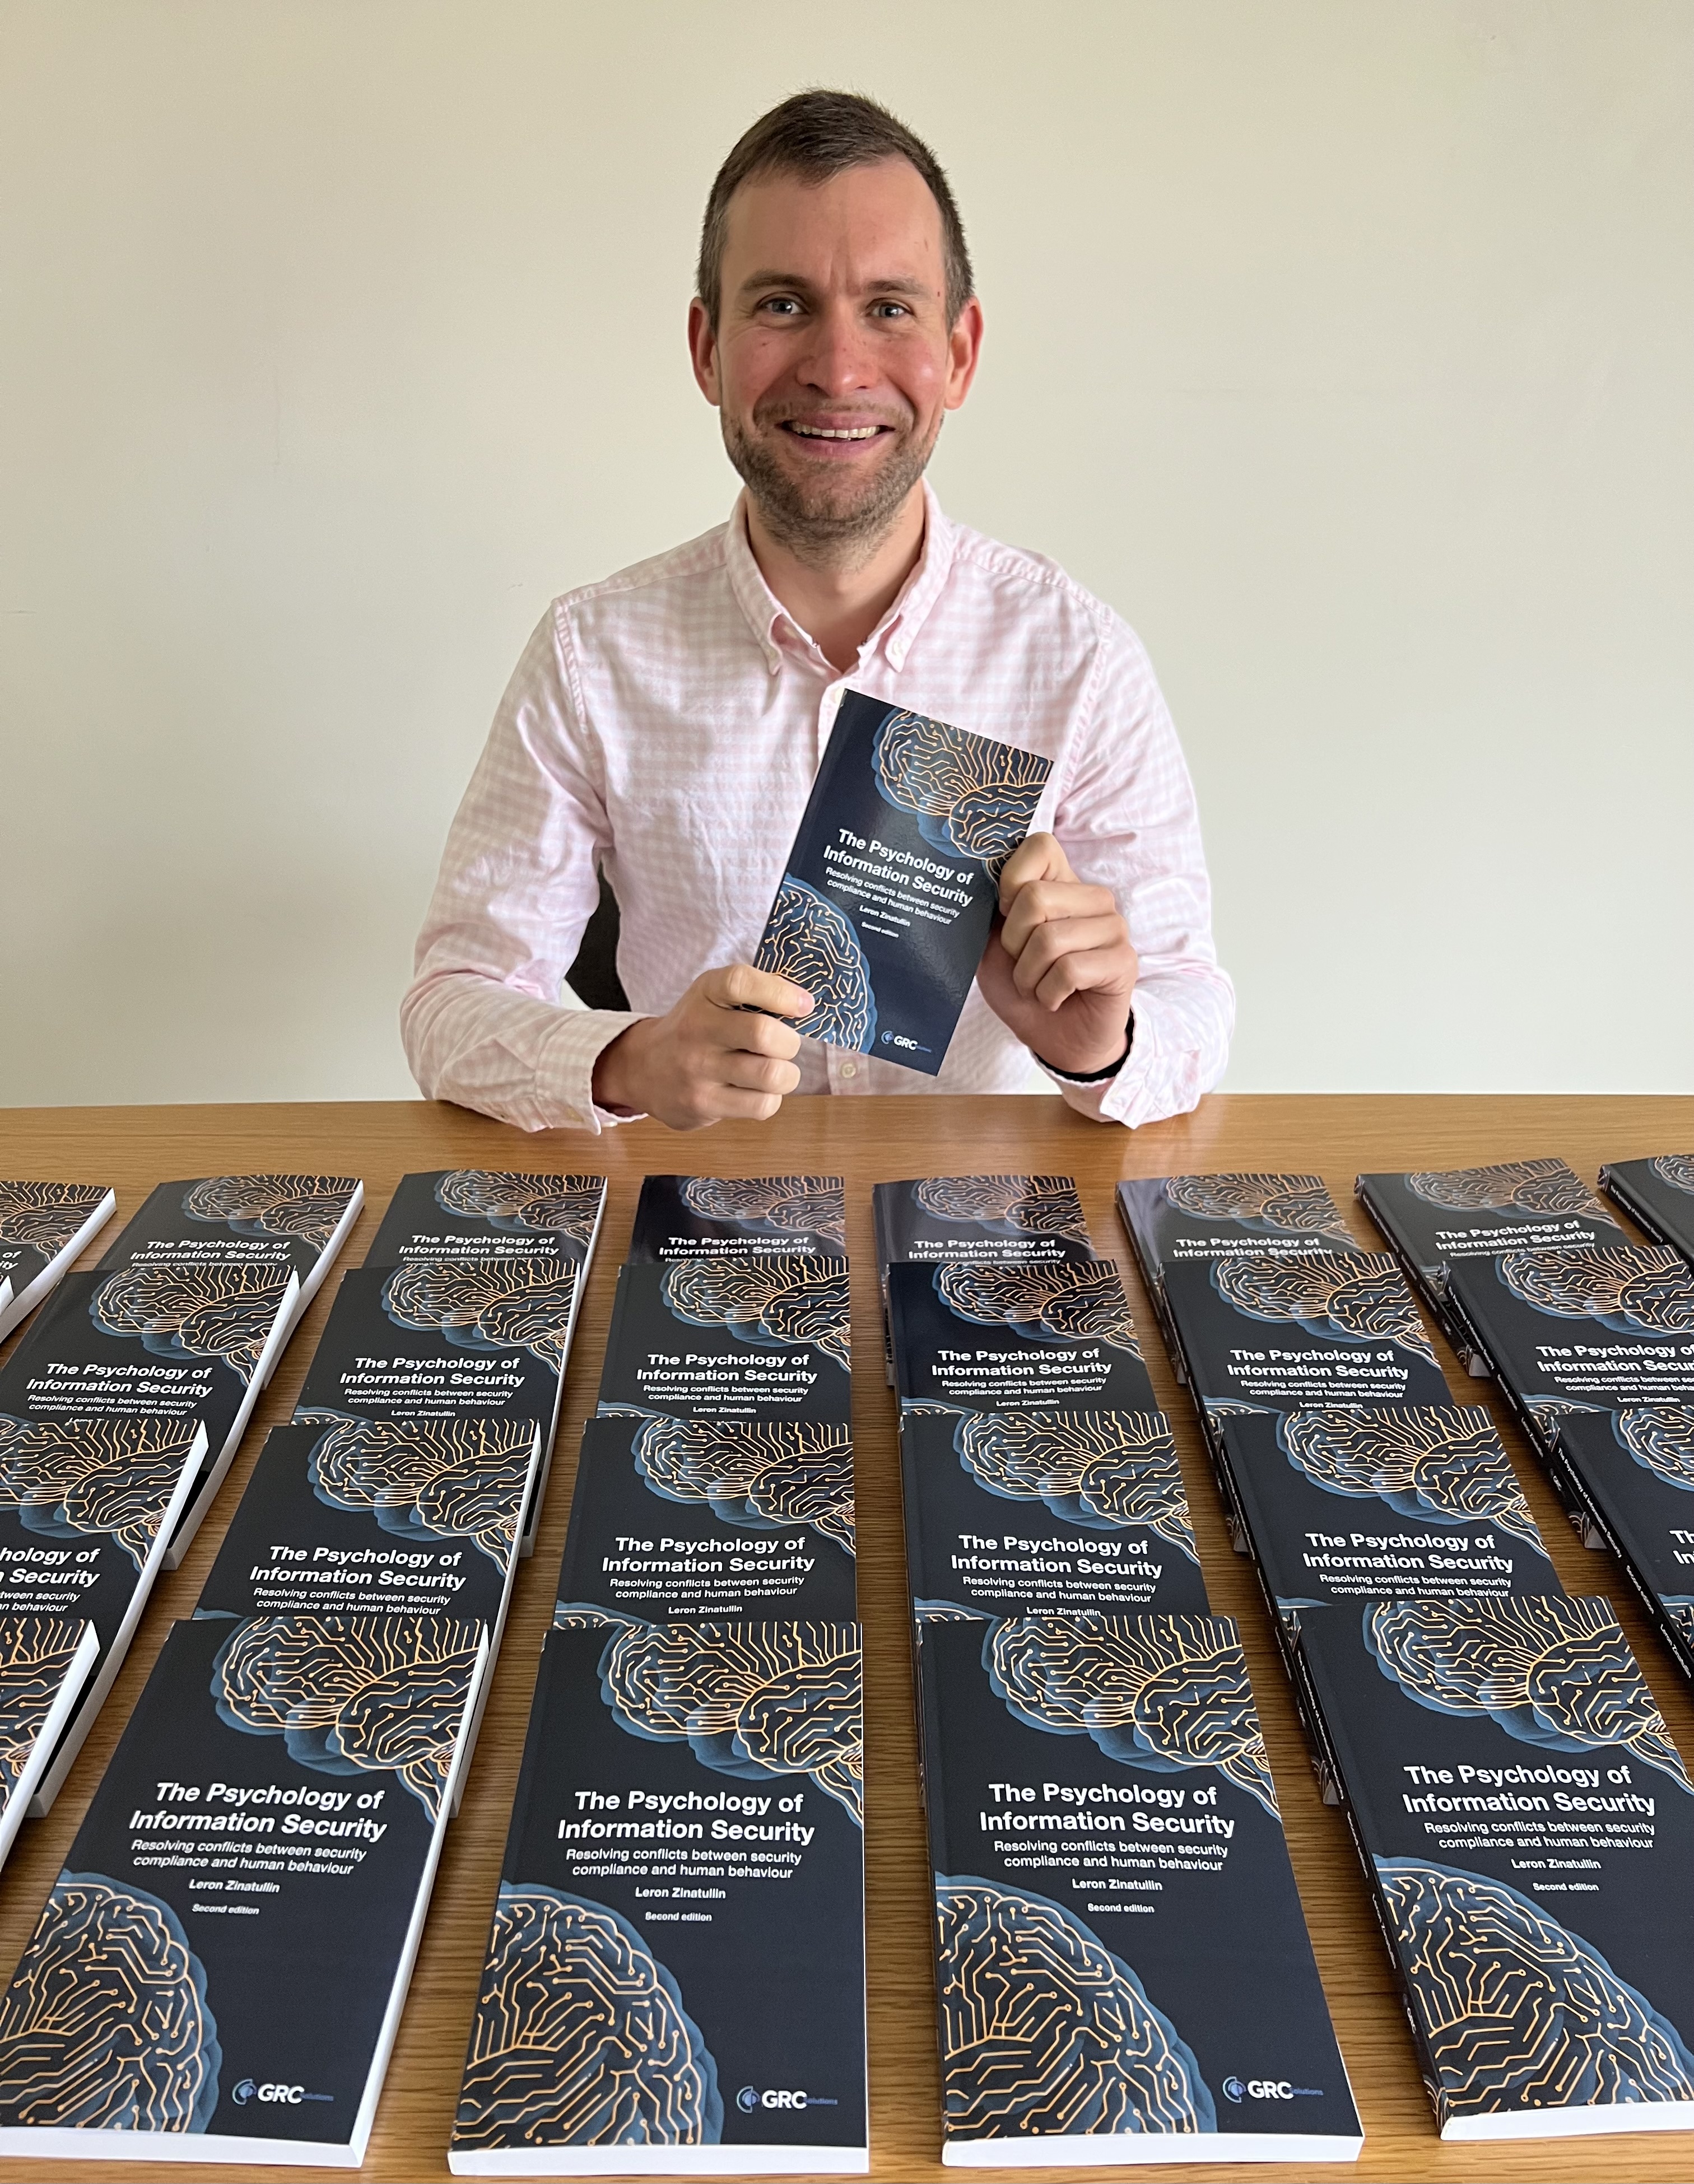
Security is a social design problem, not a tech one

I’m super proud to have written this book. It’s the much improved second edition – and I can’t wait to hear what you think about it.

https://amzn.asia/d/9lr6Sd9

Please leave an Amazon review if you can – this really helps beat the algorithm, and is much appreciated!

Governing AI Agents

Introduction to Agents (Google)

As organisations accelerate AI adoption, a familiar pattern is emerging: security teams – often the CISO – are increasingly asked to own or coordinate AI governance. That outcome is not an accident. Security leaders already operate across departmental boundaries, manage data inventories, run cross-functional programs and are trusted by executives and boards to solve hard, systemic problems. AI initiatives are inherently cross-disciplinary, data-centric and integrated into product and vendor ecosystems, so responsibility naturally flows toward teams that already do that work. This operational reality creates an opportunity: security can (and should) move from firefighting to shaping safe adoption practices that preserve value and reduce harm.

In this blog I outline key strategies on how to be successfully in leading AI governance initiatives in your organisation.

More

AI Agents and Security

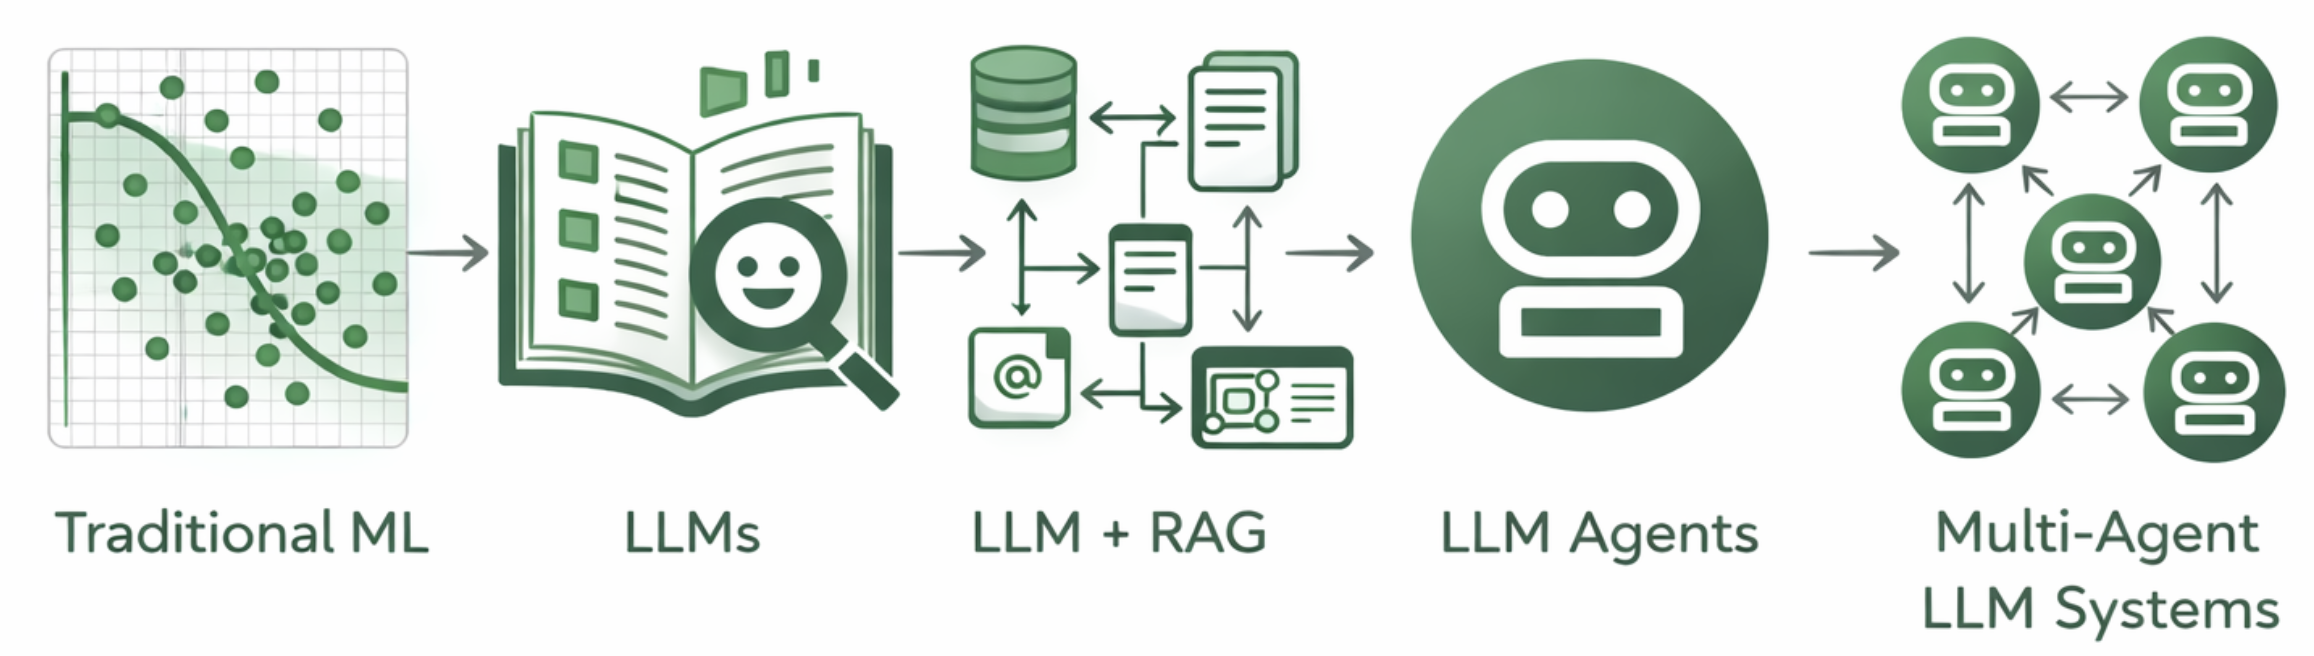
We are entering the agentic era – an inflection point defined by AI systems that can reason, plan and take action autonomously. This shift may be among the most consequential technological transformations of our generation, and it carries an equally significant obligation: to ensure these systems are designed, governed and deployed in ways that earn and sustain trust.

I completed a 5-Day AI Agents Intensive Course where we dove deep in Google’s open source Agent Development Toolkit. In this blog, I’ll share key takeaways and practical suggestions so you can navigate this shift and learn to build AI agents of your own.

More

FinTech, AI and Cyber

I recently took the stage to talk about one of the most consequential inflection points facing FinTech: the rapid arrival of agentic AI – systems that plan, decide and act autonomously – and what it means for risk, reputation, regulation and customer trust. Below is a distillation of the talk: what agentic AI actually is, why FinTechs are racing to adopt it, the real cyber threats it brings, and a pragmatic playbook leaders can use today.

More

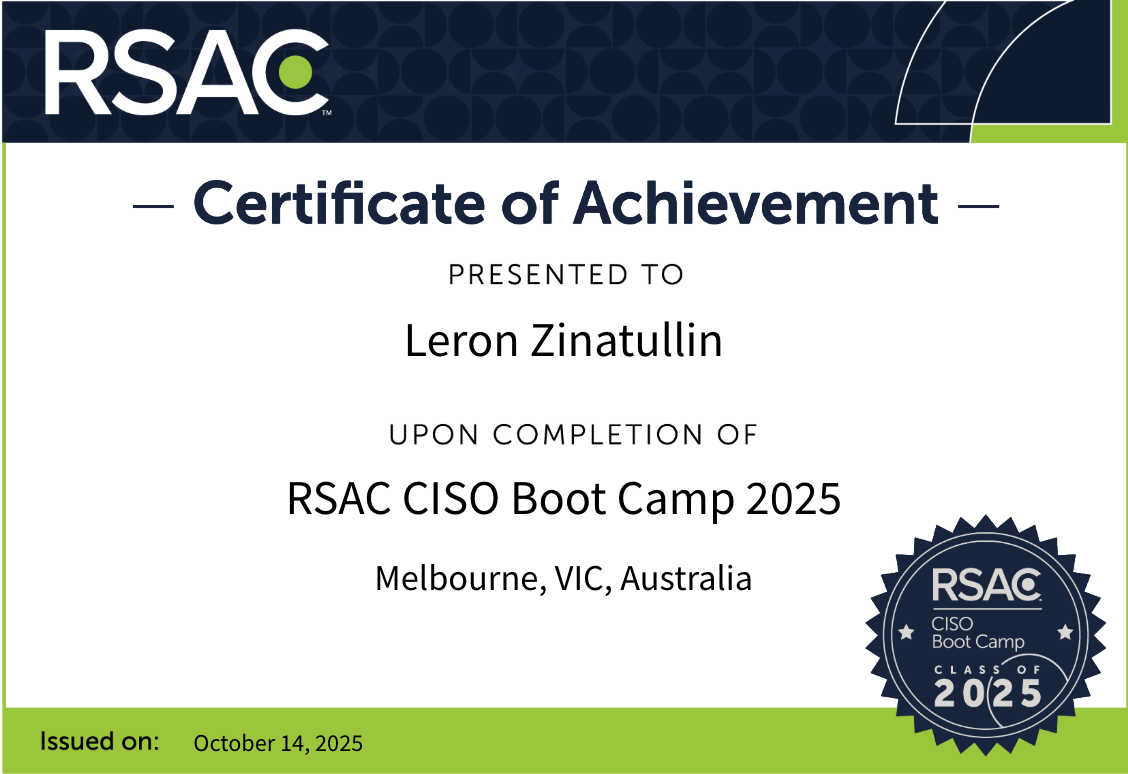
RSAC CISO Bootcamp 2025

It was so good to attend the RSAC CISO Bootcamp at CyberCon Melbourne – a practical session for CISOs.

Highlights that stuck with me:
💡 A conversation with Brian Krebs on AI security and organised cybercrime: attackers are tooling up fast; our defences must keep pace.
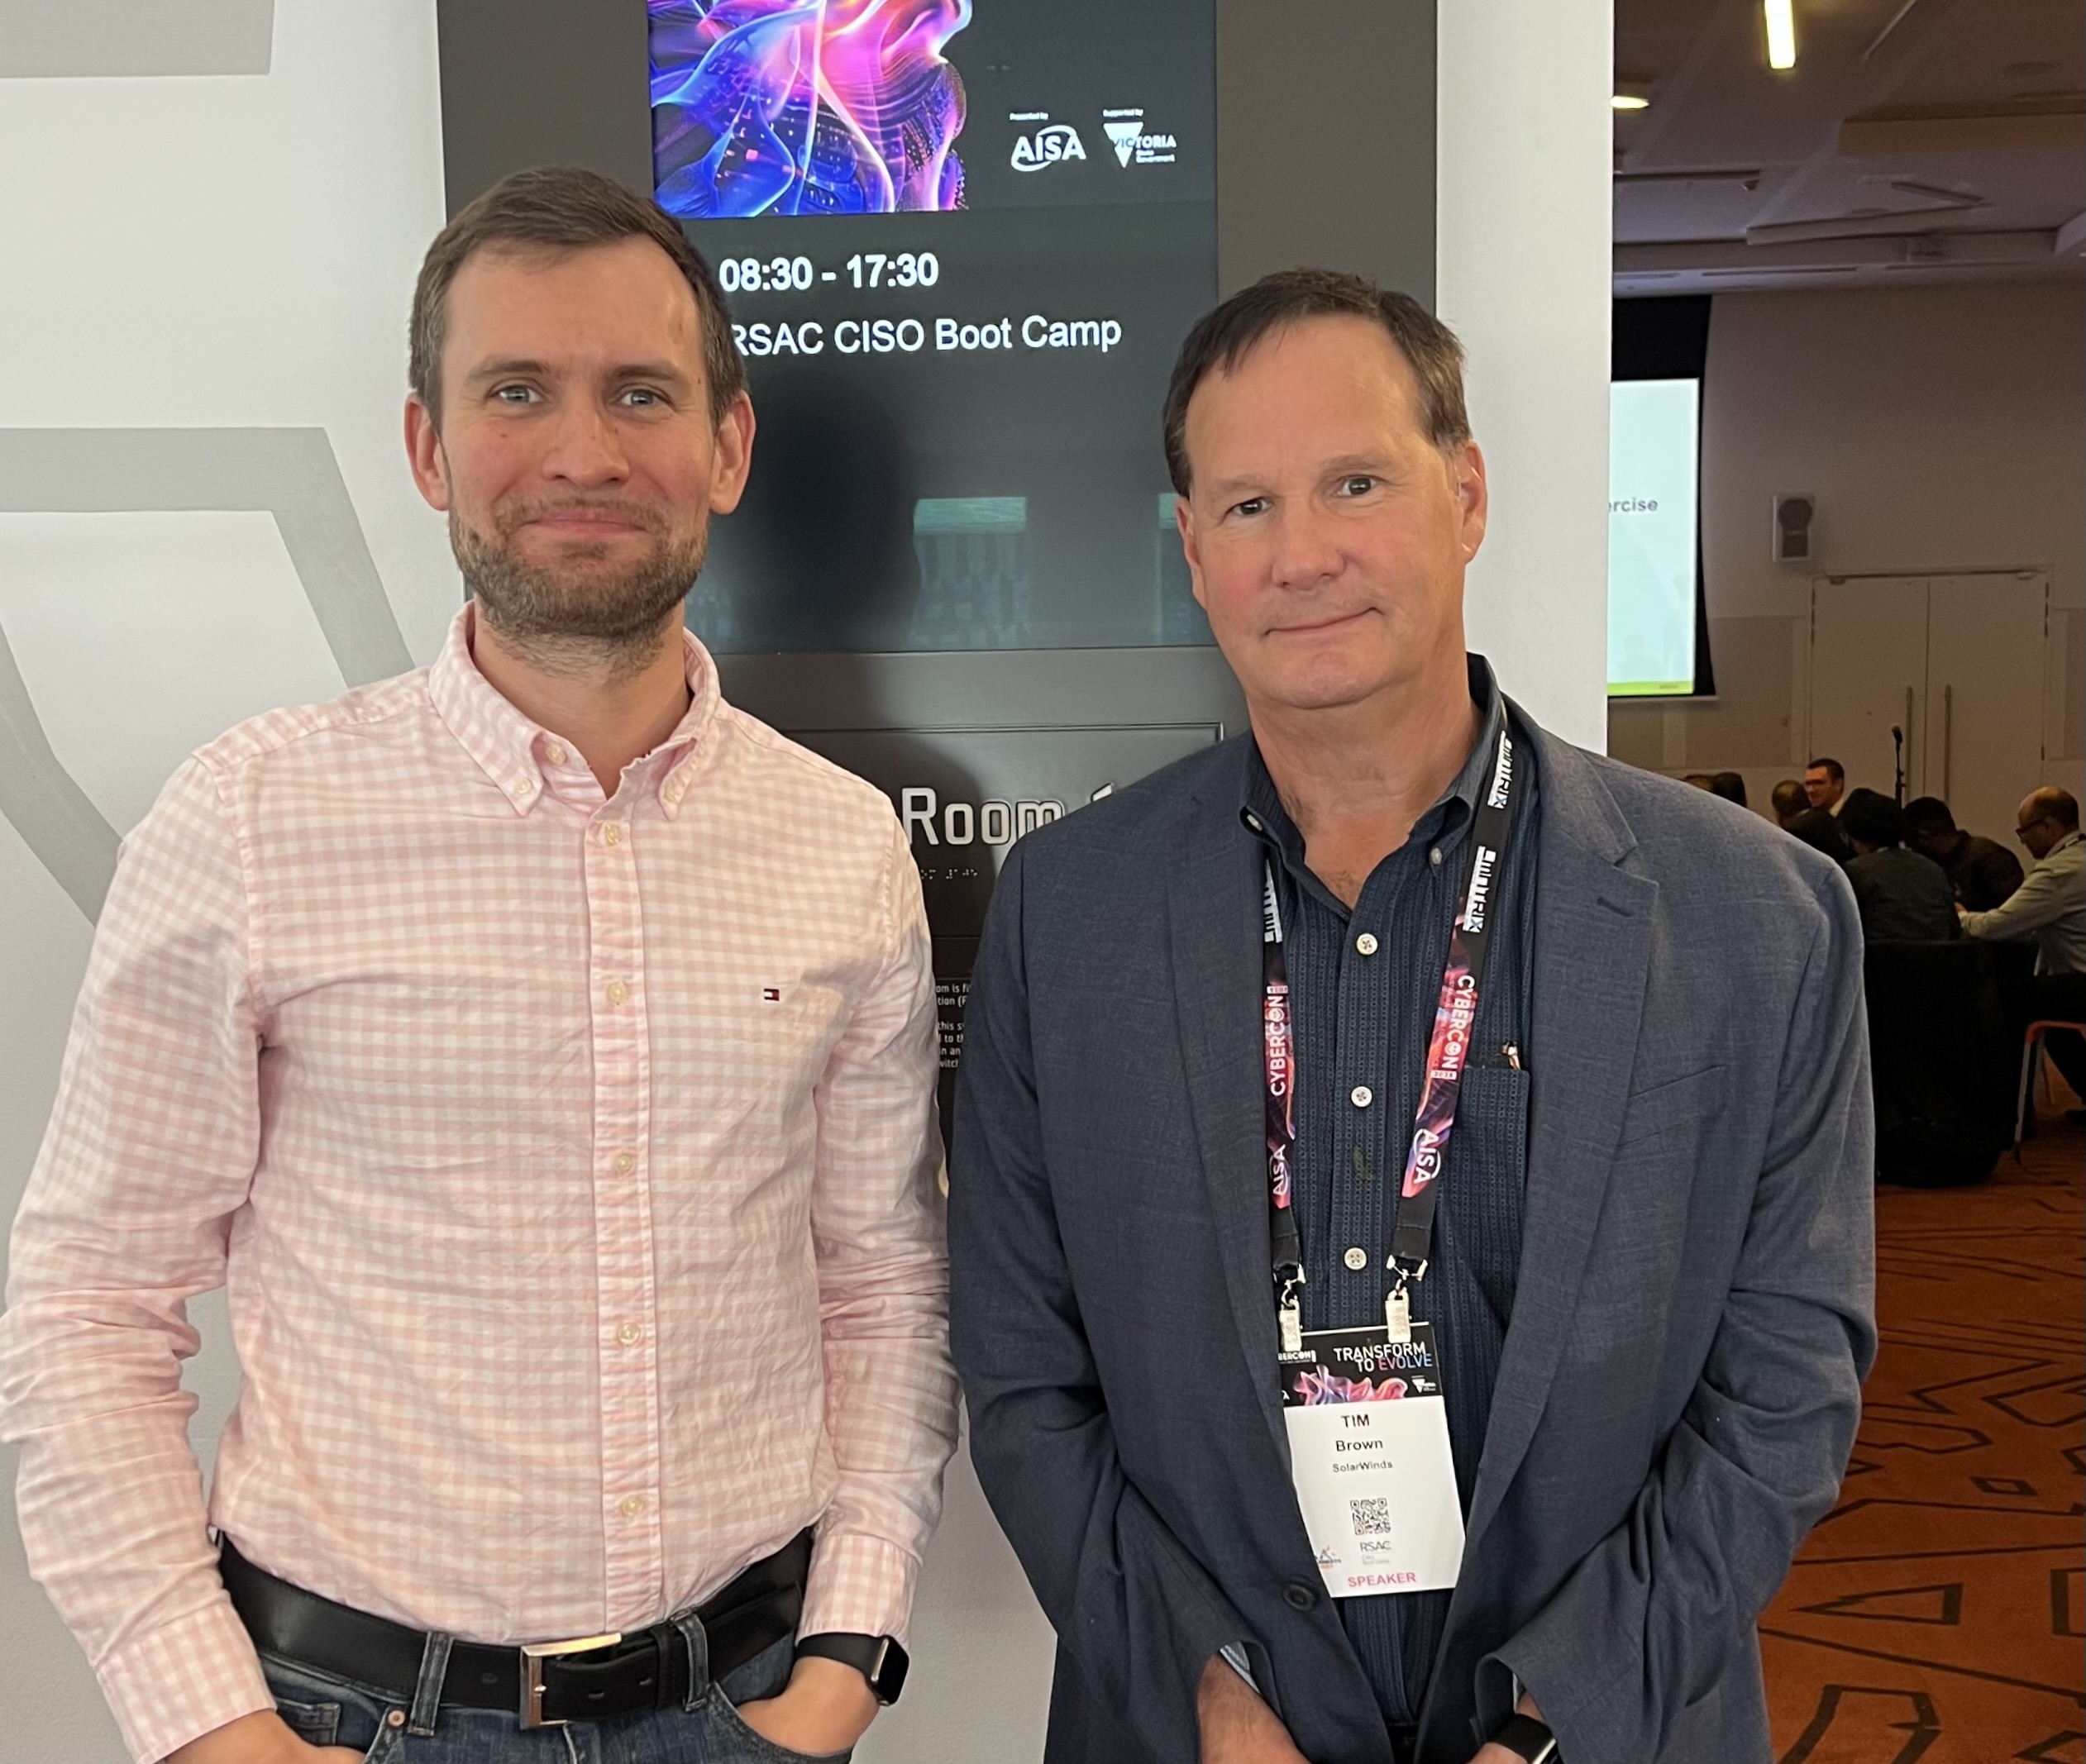
💡 A candid, closed-door session with Tim Brown, CISO of SolarWinds, about crisis response: execution matters, but so does the personal toll on teams and leaders.
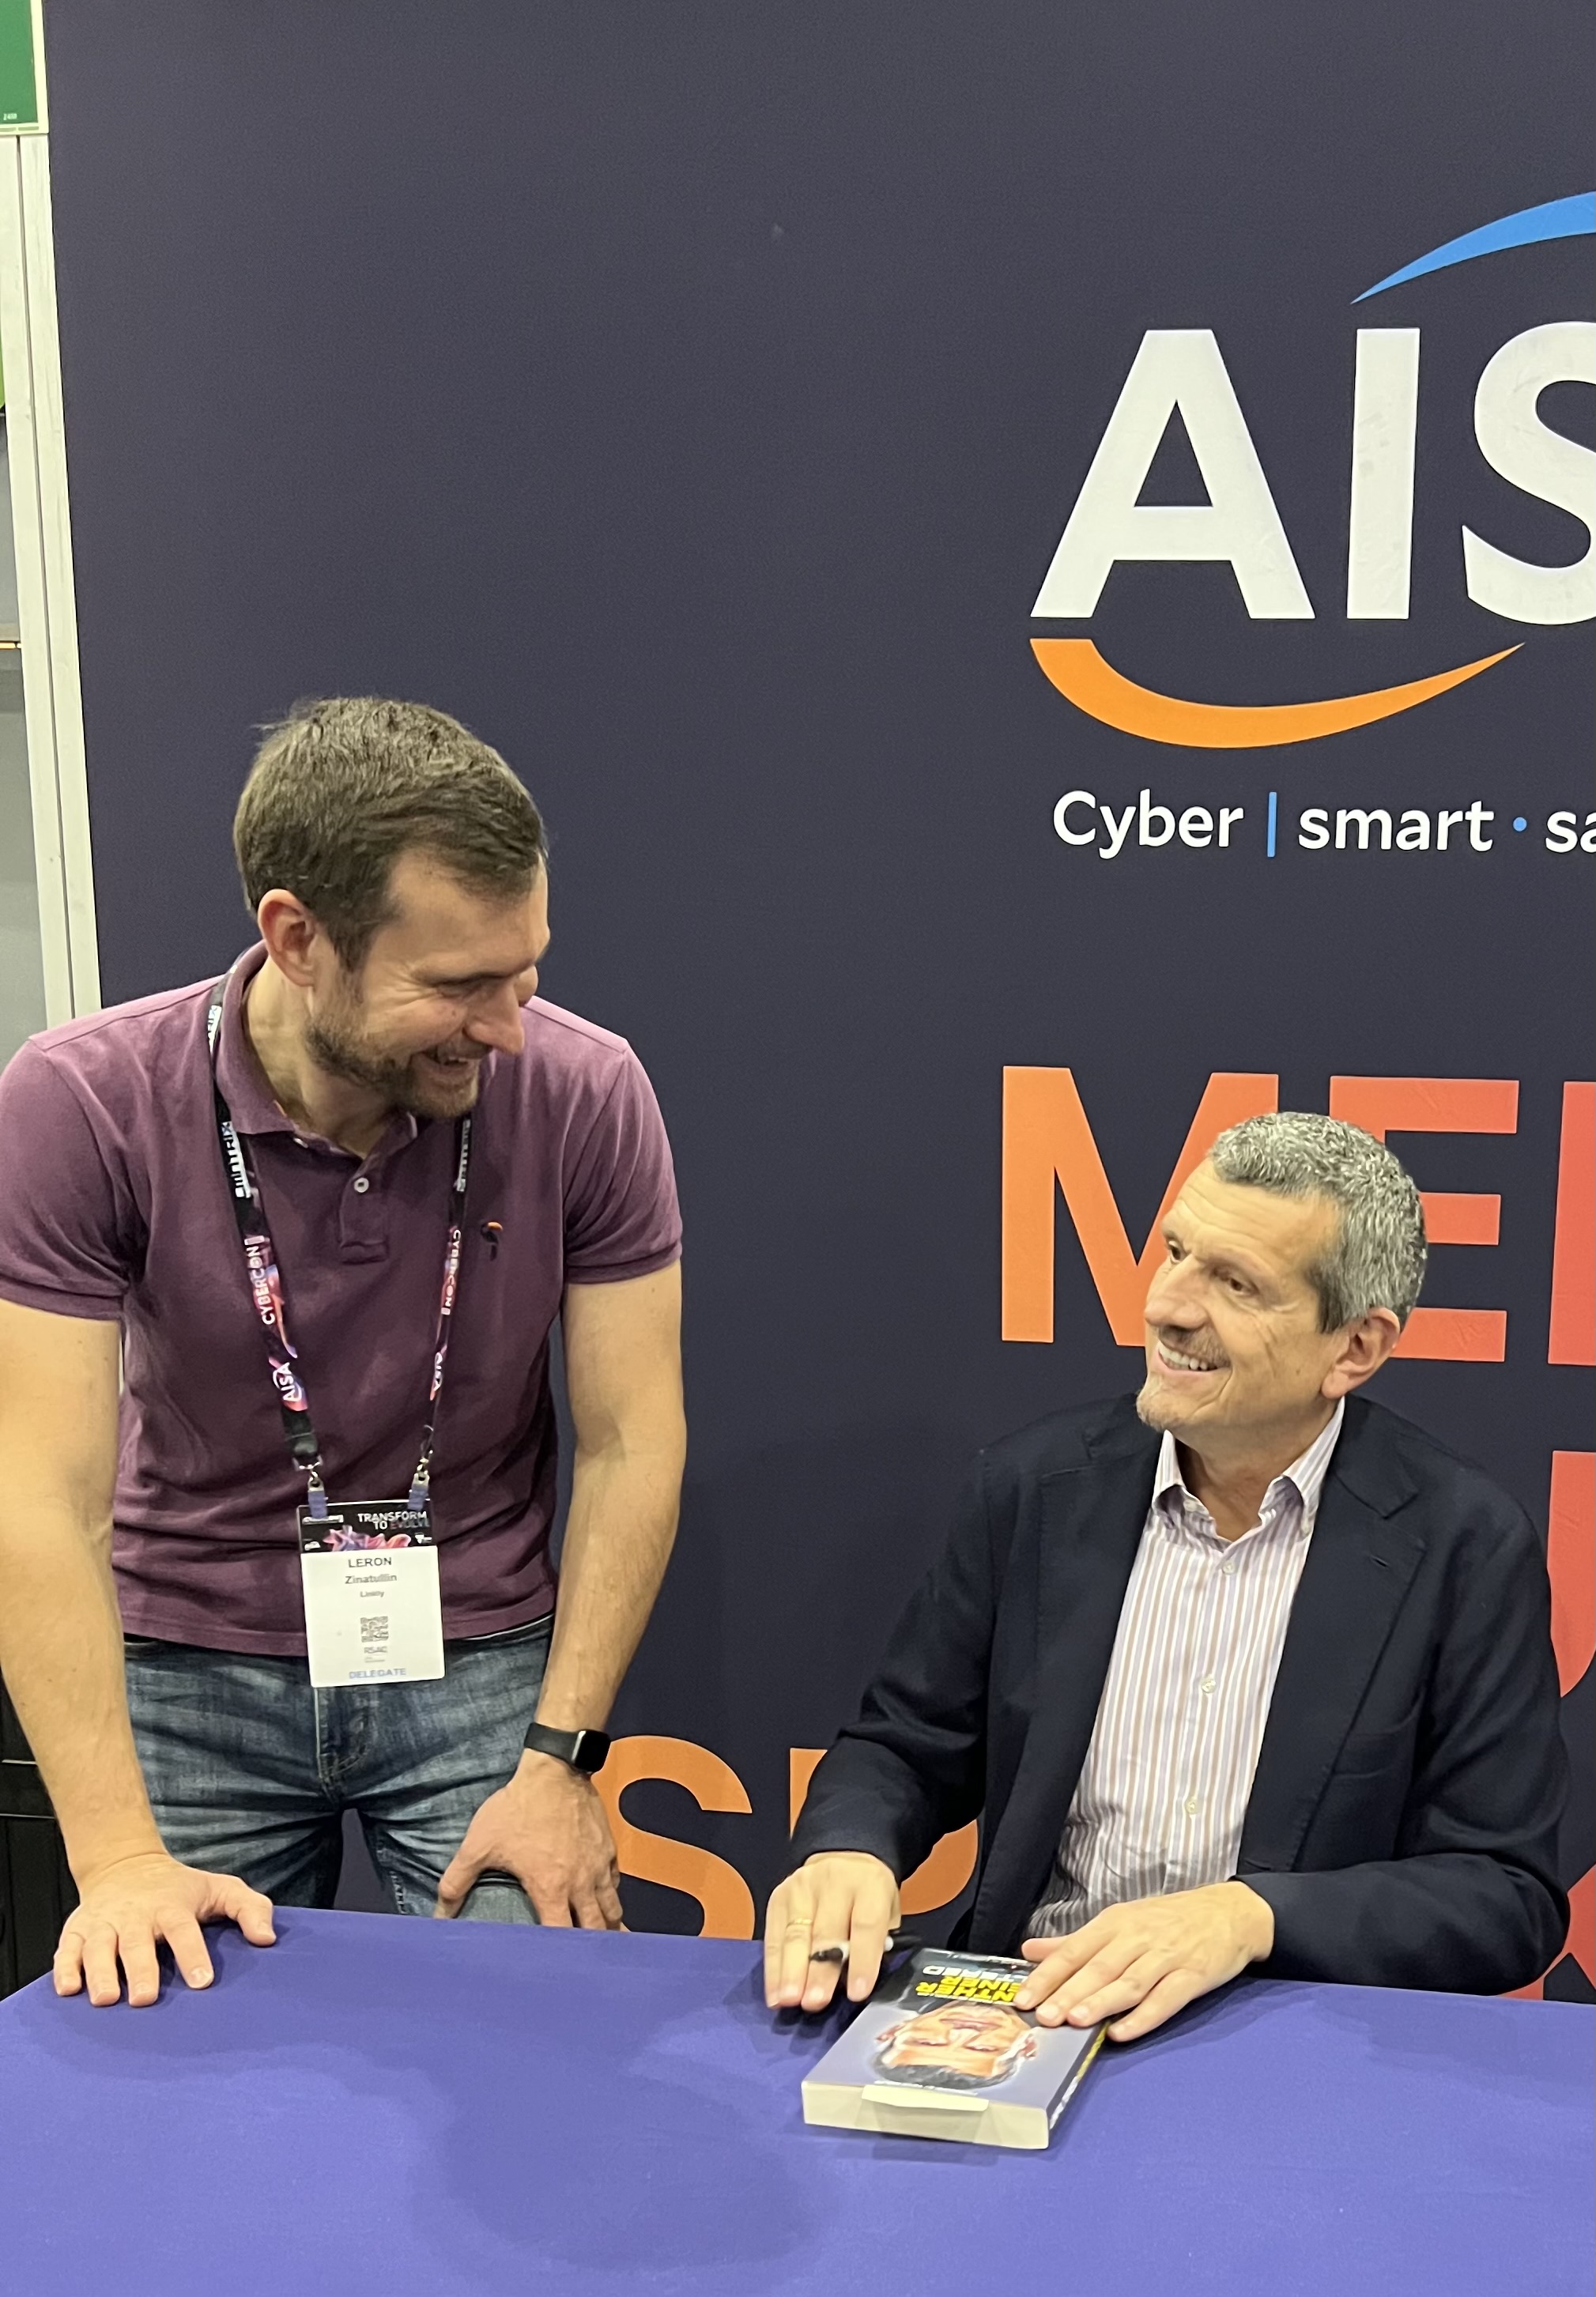
💡 A chat with F1’s Guenther Steiner on teamwork and resilience in high-pressure environments.

Events like this remind me how much strength there is in our community. I’m proud to contribute and be part of it. You don’t need a challenge coin to get help – if you want to compare notes or need a sounding board, reach out.

Redefining business and technology in Australia

I’m proud to be featured on Moxie Top Minds, joining the most influential figures redefining business and technology in Australia.

It’s always great to collaborate with industry leaders from all aspects of the ecosystem: CEOs, CIOs, CTOs, CDOs, CISOs and Founders.

I look forward to setting the market pace by sharing insights, shaping research data and collaborating among executive networks.

AI in the Enterprise: Balancing Innovation and Security

It was great to have a debate on balancing innovation and security keynote panel, where we dug into both the promise and the perils of AI adoption from the CISO and CIO perspectives.

Your biggest AI risks really depend on where and how you’re using it. I recommend reviewing your product roadmap for AI-powered features to anticipate potential gaps.

Map out whether AI is home-grown, vendor-sourced or embedded. When it comes to governance, we can borrow from what we learned with BYOD, cloud and shadow IT. Extend existing security reviews, supply-chain checks and third-party assessments into your AI program. For quick wins, manage it like a SaaS risk: think privacy controls and boundaries around sensitive data.