Back to School

IMG_4243

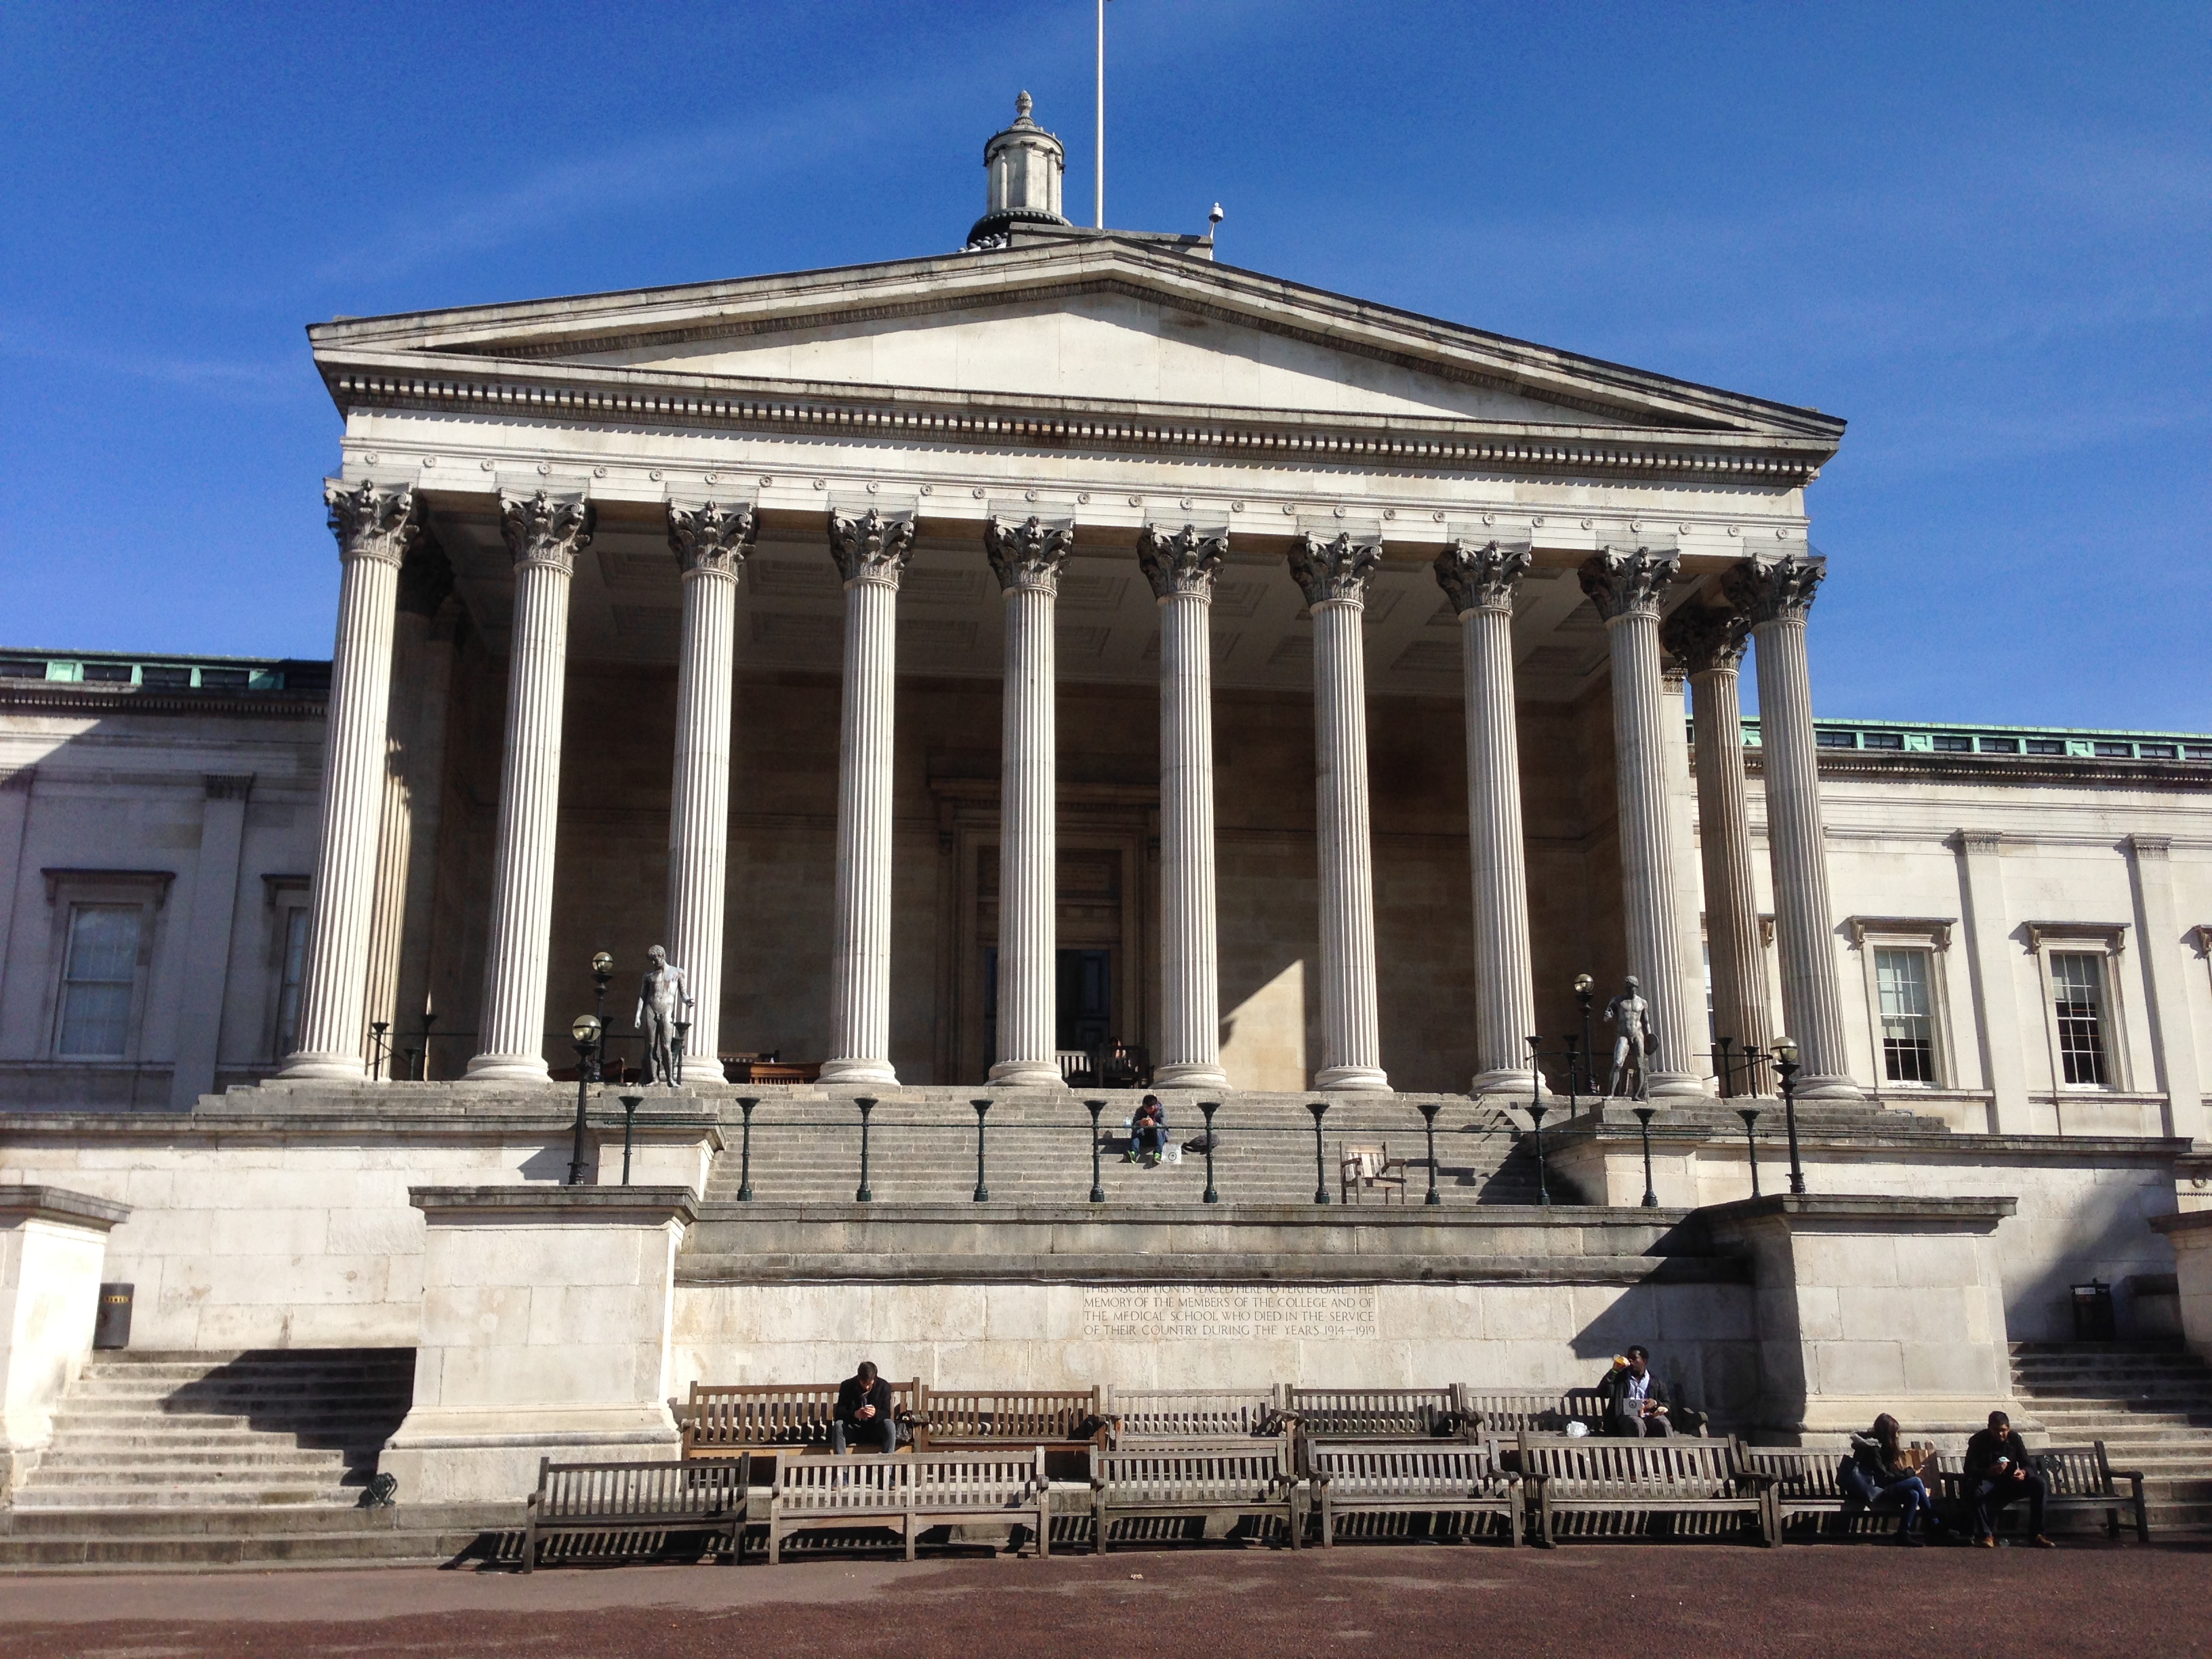
This week I was really happy to be back at the University College London where I got a degree in Information Security from. I was invited to the Technology & Entrepreneurial Start Ups Insight session organised by the Management Science & Innovation Department. I met many bright students interested in technology, including current MSc Information Security students. It was very interesting to find out how the curriculum changed to address modern industry trends and needs.

UCL

The day after I was proud to represent KPMG at the UCL IT and Technology Careers Fair. It comes as no surprise that there were many students interested in starting a career in the information security field. I was happy to help out with some suggestions, especially remembering that I attended the very same event some years ago.

NextSec Conference: The Changing Face of Cyber Security

NextSec

I am delighted to invite you to the NextSec Cyber Security Conference ‘The Changing Face of Cyber Security’ on 11 December 2014 at EY, 1 More London Place, SE1 2AF, London.

The conference will provide an opportunity for you to hear senior cyber security leaders, from a range of industries, share their cyber security experiences and insights through presentations following three main themes:
1) the changing cyber threat landscape,
2) the diverse techniques that have been adopted in response to the threat, and
3) the range of cyber security roles across different sectors.

The second half of the conference will address the changing dynamics required for leadership in cyber security including gender diversity and inclusiveness.

An open Q&A panel discussion will close the conference sessions.

Event Details:

  •  Date:           11 December 2014
  • Time:            5.00pm – 8.30pm followed by networking and drinks
  • Location:     Mulberry Restaurant, EY, More London Place

 Chairs

  • Cheryl Martin, Partner, EY
  • Leron Zinatullin, NextSec Committee Member and Information Security Advisor, KPMG

Confirmed speakers and panellists:

  • Cheryl Martin, Partner, EY
  • Sian John, Security Futurologist, Symantec
  • Robert Coles, Chief Information Security Officer, GlaxoSmithKline
  • Elena Cinquegrana, Associate Director, Navigant
  • Lucy Chaplin, Assistant Manager, KPMG
  • Freddie Hult, Senior Cyber Resilience Adviser, Cyber Resilience Ltd

Please visit the website to register for free.

NextSec is a networking group of young professionals working in cyber security and information risk management in the UK. The group exists since January 2012 and currently has over 290 members. These 290 members work for over 59 organisations in the UK. We have a diverse representation of young professionals working in financial services, oil and gas industry, industrial goods and retail, marketing, telecommunications, software, technology, professional services, and public sector. For more information about NextSec, please visit our website and LinkedIn group.
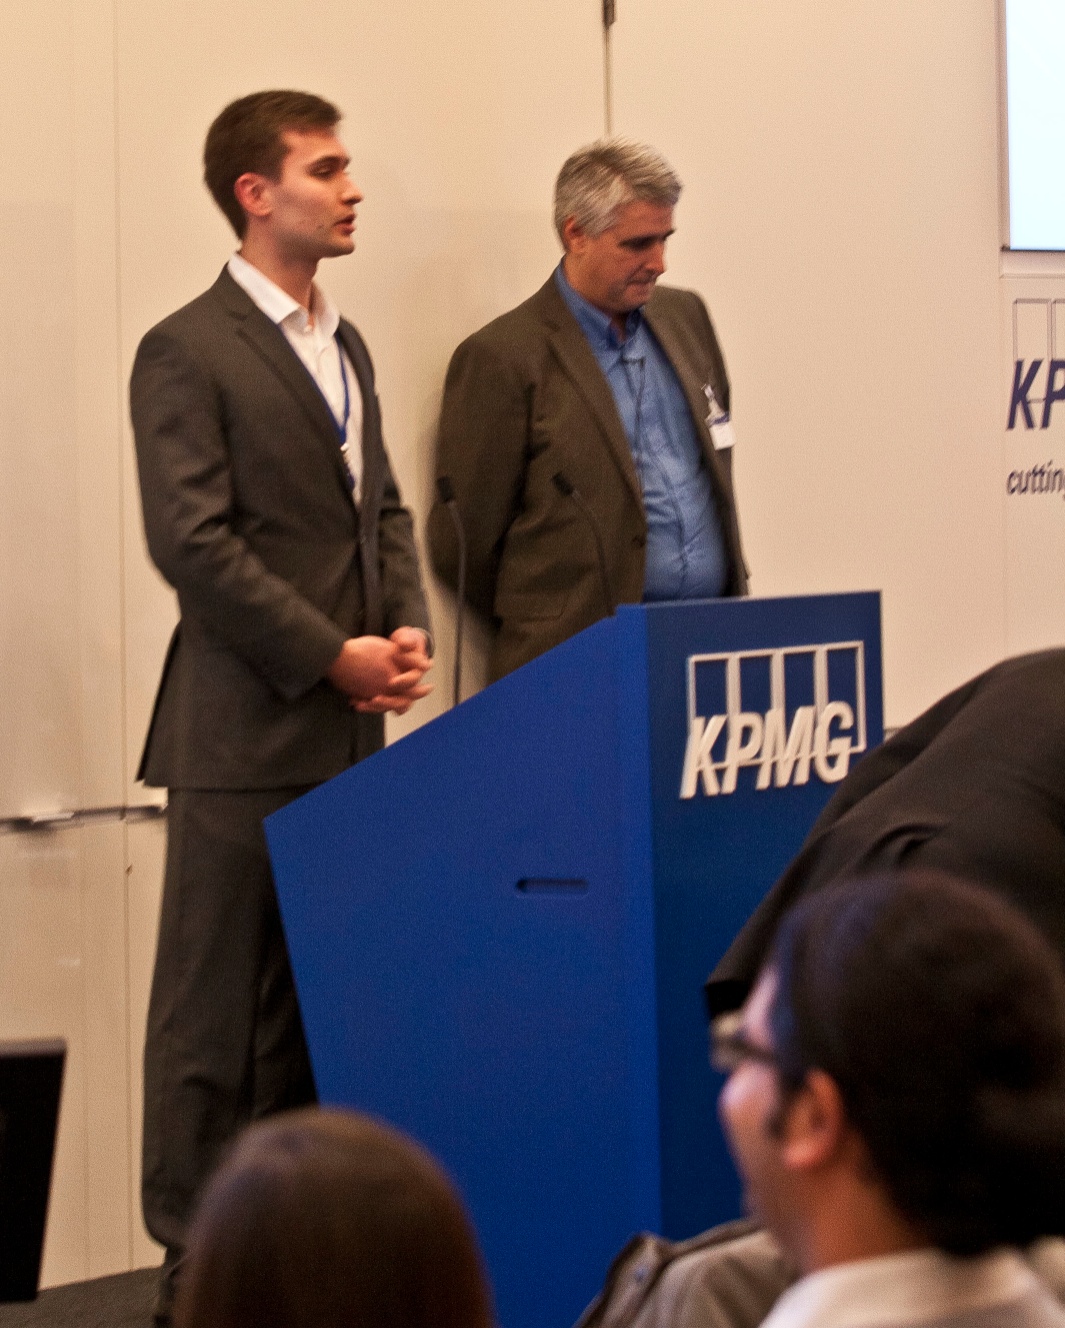
Teaching Information Security Concepts at KPMG

KPMG1

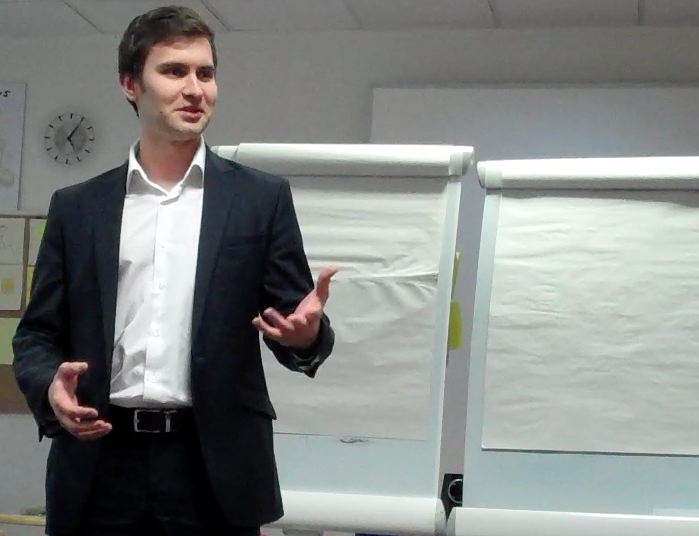
I delivered a 1,5-day Information Security Concepts course at KPMG UK.

We covered a wide range of topics, including information security risk management, access control, threat and vulnerability management, etc.

According to the feedback I received after the course, the participants were able to understand the core security concepts much better and, more importantly, apply their knowledge in practice.

Leron is very engaging and interesting to listen to
Leron has the knowledge and he’s very effective making simple delivery of a complex topic
Leron is an effective communicator and explained everything that he was instructing on in a clear and concise manner

There will be continuous collaboration with the Learning and Development team to deliver this course to all new joiners to the Information Protection and Business Resilience team at KPMG.

Discussing Human Aspects of Information Security

June 11 (1)

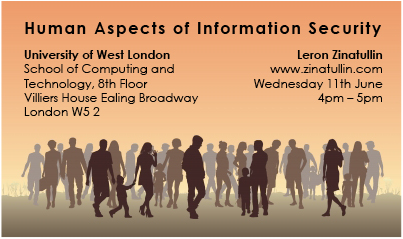
I delivered a seminar on the human aspects of information security at the University of West London. We discussed conflicts between security and productivity in companies and possible solutions. Research students with different backgrounds helped to drive the debates around usability, awareness and policy design.

We also talked about the practical applications of behavioural theories, where I shared my views on user monitoring and trust in organisations within the context of security culture.

Daniel, one of the participants, summarised his experience in his blog.

Image courtesy of Vlado / FreeDigitalPhotos.net

Delivering a Seminar at the London Metropolitan University

RIG (1)

I was invited to give a talk on industrial systems security at the London Metropolitan University.

The seminar was intended for academic staff to discuss current problems in this field. We managed to cover a broad range of issues regarding embedding devices and network and IT infrastructure in general.

The professors shared their perspective on this subject.  This resulted in the  identification of several research opportunities in this area.

Image courtesy of Vlado / FreeDigitalPhotos.net

Delivering a Seminar at the IT Security & Computer Forensics Pedagogy Workshop

HIGHER EDU

I presented at the HEA STEM Workshop on human aspects of information security.

The aim of the workshop is to share, disseminate and stimulate discussions on: the pedagogy of teaching subjects related to IT security and computer forensics, and issues relating to employability and research in these areas.

During the workshop the speakers presented topics that focus on: delivery of innovative practical tutorials, workshops and case studies; course design issues; demand for skills and employment opportunities; countering the “point & click” approach linked to vendor supplied training in industry; and current research exploring antivirus deployment strategies.

Presenting on Industrial Control Systems Security at the University of Westminster

SCADA WESTMINSTER

I delivered a seminar to a group of students at the University of Westminster on industrial control systems security. We discussed the history of these systems, current developments and research opportunities in this area. There was some debate around the hypothesis that these systems weren’t designed to be secure and the trade-offs between confidentiality, integrity and availability helped the participants to better understand modern challenges. Practical recommendations were given pertaining the areas of risk management, disaster recovery, and resilience.

I also facilitated a workshop, where I divided the audience into several groups representing various stakeholders within the company: shareholders, process engineers, and security managers. This helped to drive further discussion regarding different points of view, priorities, and the complexity of communication.

Giving a talk at the University of Greenwich

presentation

I was invited to the University of Greenwich to discuss career opportunities in the information security field. We had a productive discussion with the young people who are finishing their degree in Computer Security and Forensics. After the presentation I was introduced to several PhD students who are currently researching various issues around privacy and social media. I’m very happy that people are becoming more interested in solving information security and privacy issues.