RSA CISO Bootcamp

I had the privilege to join a brilliant cohort of CISOs at the RSA Conference CISO Bootcamp. It was an energising experience, where seasoned experts and emerging leaders in cybersecurity came together to tackle our industry’s most pressing challenges.

The bootcamp was more than just a learning experience; it was a platform for sharing personal insights, gaining fresh perspectives and engaging in a thought-provoking debate.

From discussing emerging threats to exchanging strategies for resilience, it was a reminder of the power of community in cybersecurity. A huge thanks to all organisers and speakers for creating a space where we can grow together and tackle our industry’s biggest challenges.
Collaborating with the enemy: key lessons for cyber security

In cybersecurity, collaboration is essential. With growing complexity in the threat landscape, leaders often find themselves working with parties they may not fully align with—whether internal teams, external stakeholders, or even rival firms.

Adam Kahane’s book Collaborating with the Enemy: How to Work with People You Don’t Agree with or Like or Trust outlines principles for collaborating effectively, especially in challenging environments where trust and agreement are minimal. Kahane’s “stretch collaboration” approach can transform the way cybersecurity leaders address conflicts and turn rivals into partners to meet critical security goals. In this blog, I’ll share my key takeaways.

More

Change management and cyber security

Adapted from Kotter, J. 2007, ‘Leading change: Why transformation efforts fail’, Harvard Business Review, vol. 73, no. 2, pp. 1–10.

Cyber security leaders have to be effective change agents to be successful. Cyber capability uplift and risk reduction initiatives often require significant transformation in the organisation. In this blog, I’ll introduce a tried and tested change management framework and demonstrate its application to cyber security in an illustrative case study.

More

CyberPeace Institute’s Volunteer of the Month

I’m proud to be named CyberPeace Institute‘s Volunteer of the Month.

A big shoutout to CyberPeace for this awesome recognition! It’s been such a rewarding experience to help them in their mission to make the digital world safer for everyone.

The CyberPeace Institute is a non-profit focused on reducing the harm caused by cyberattacks to individuals and communities. Through their CyberPeace Builders program, they offer free cybersecurity support to organisations that need it most, especially those where cyber threats can have a serious impact.

As a volunteer, I’ve had the chance to help for-purpose organisations respond to cyber attacks, develop incident response plans, run security awareness training, perform dark web monitoring and craft essential policies and procedures. Plus, I’ve provided general cyber advice along the way. It’s been an incredible journey being part of a team that’s making a real difference.

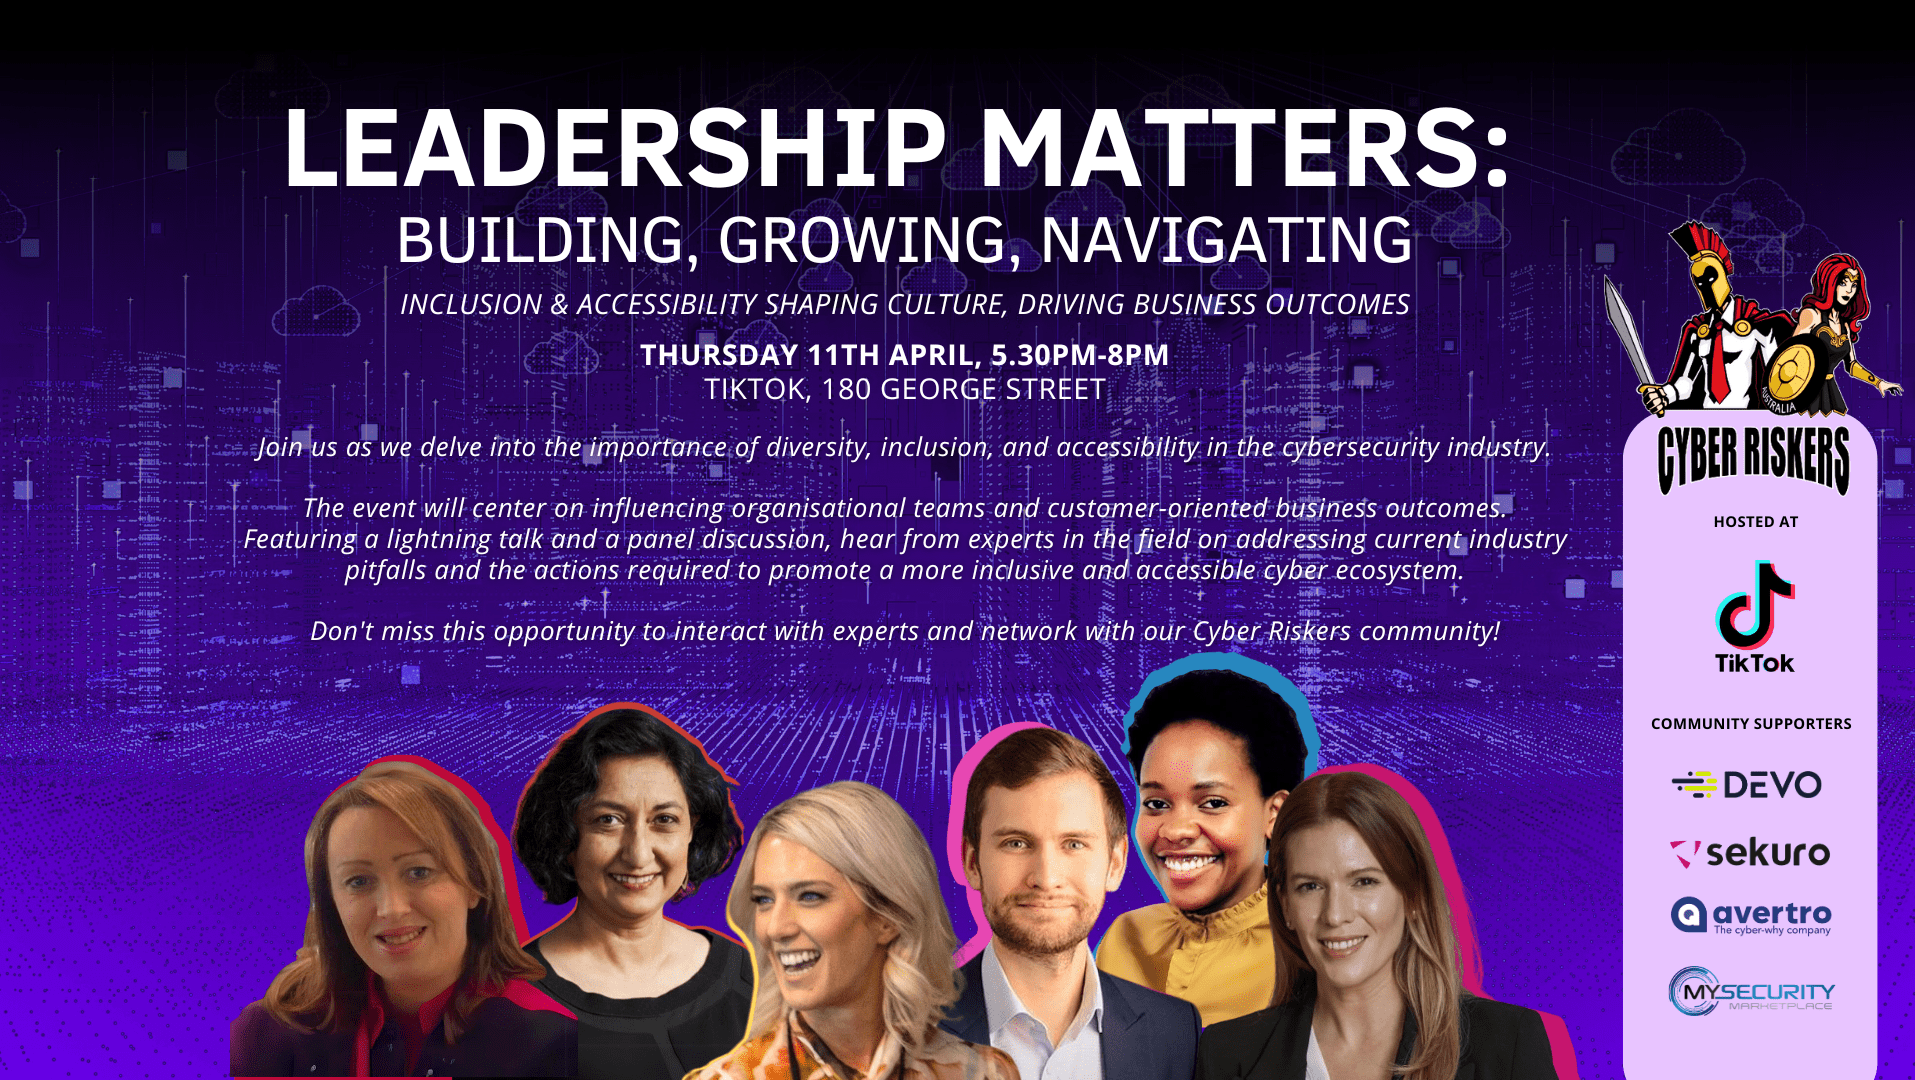
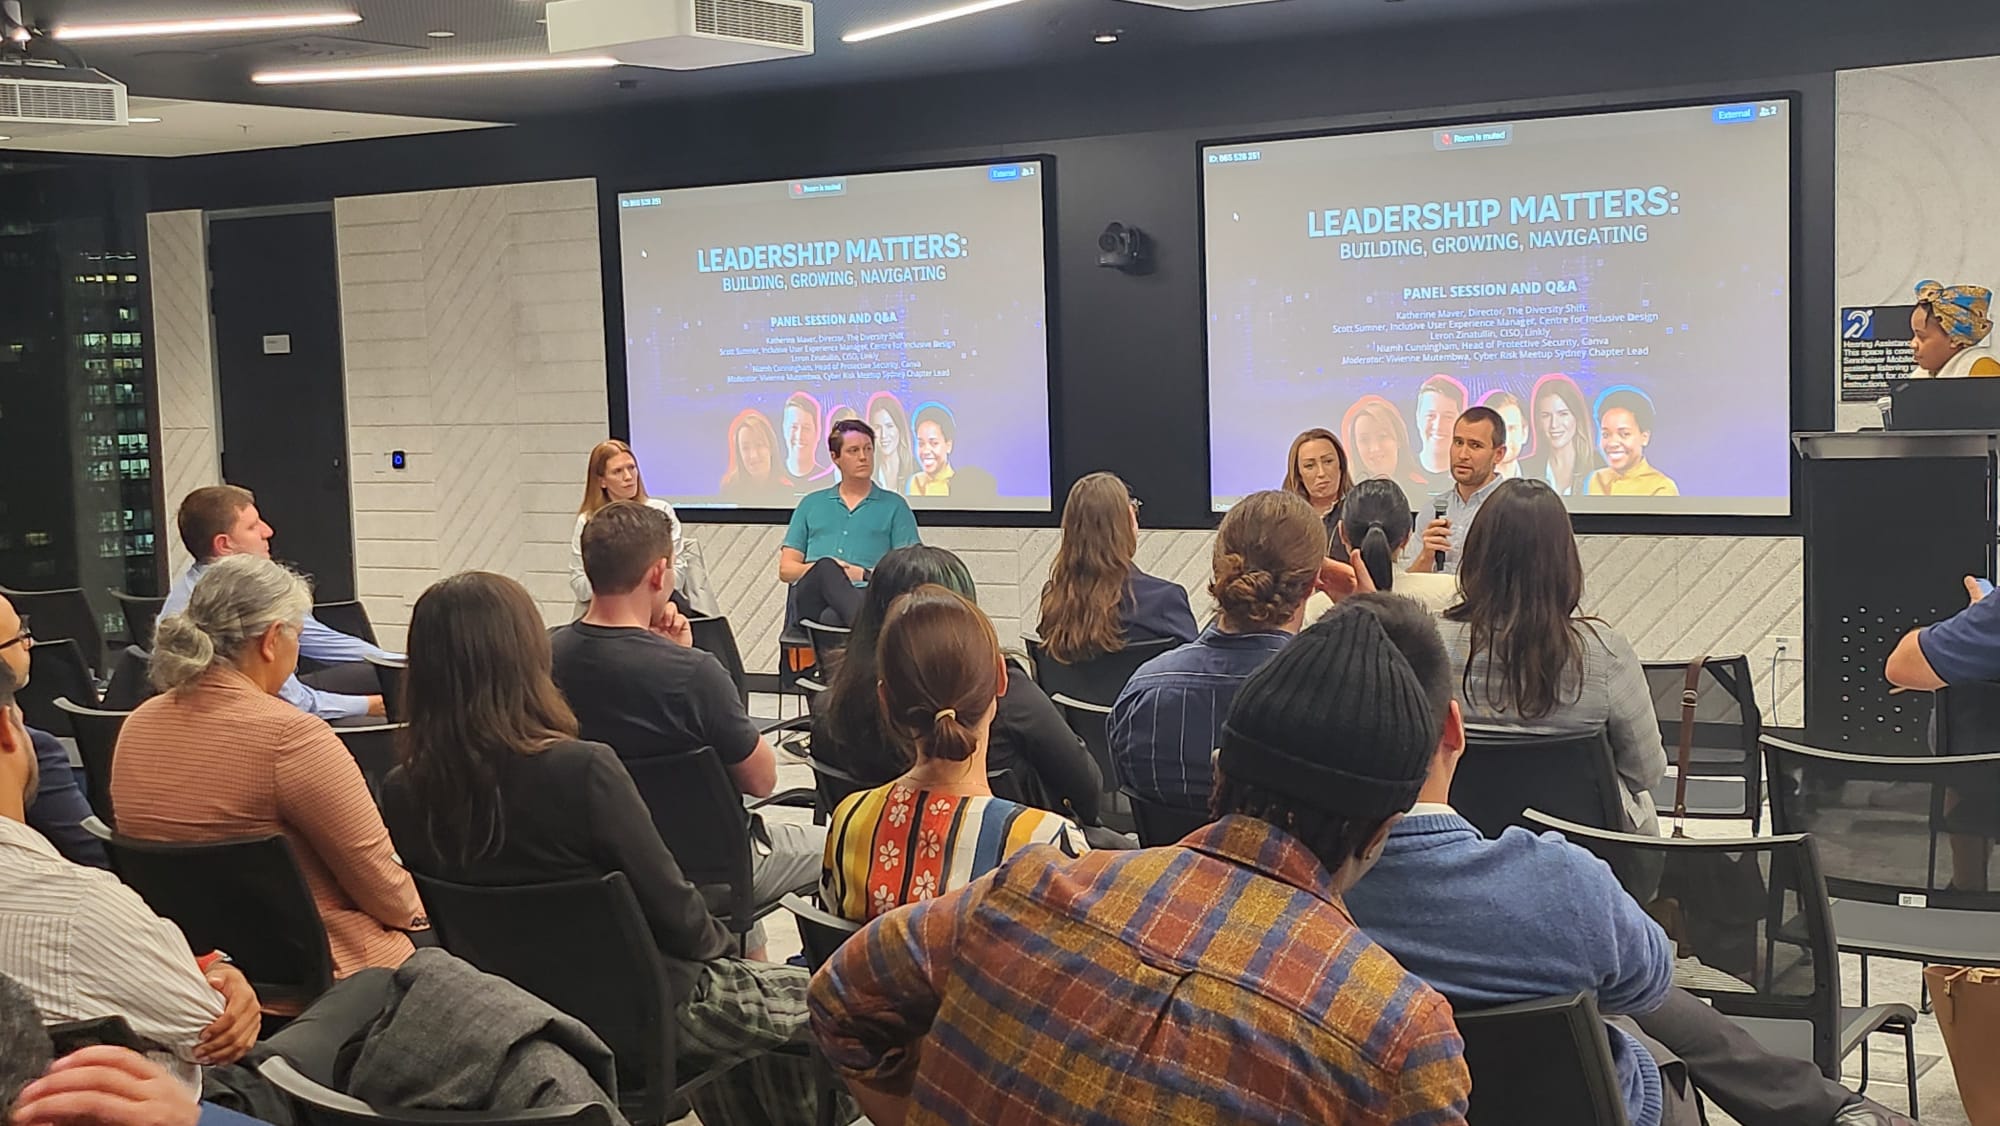
Inclusion and accessibility: shaping culture and driving business outcomes

I’m grateful to have had an opportunity to continue to learn and contribute to the important discussion on building the culture of diversity, inclusion and accessibility in cyber security.

I like being on panels like this because it gives me an opportunity to share my views and continue to educate myself not only through research but also through lived experiences.

I believe shaping the inclusive culture begins with creating awareness about the barriers to diversity and inclusion. Accessibility is an important consideration. Testing new systems and processes with people with accessibility needs is key to discovering where issues may exist.

The best way to make security more accessible is to engage with the people who interact with it. Treating usability and accessibility together with other security requirements rather than a separate item is useful to ensure it gets built-in from the start.

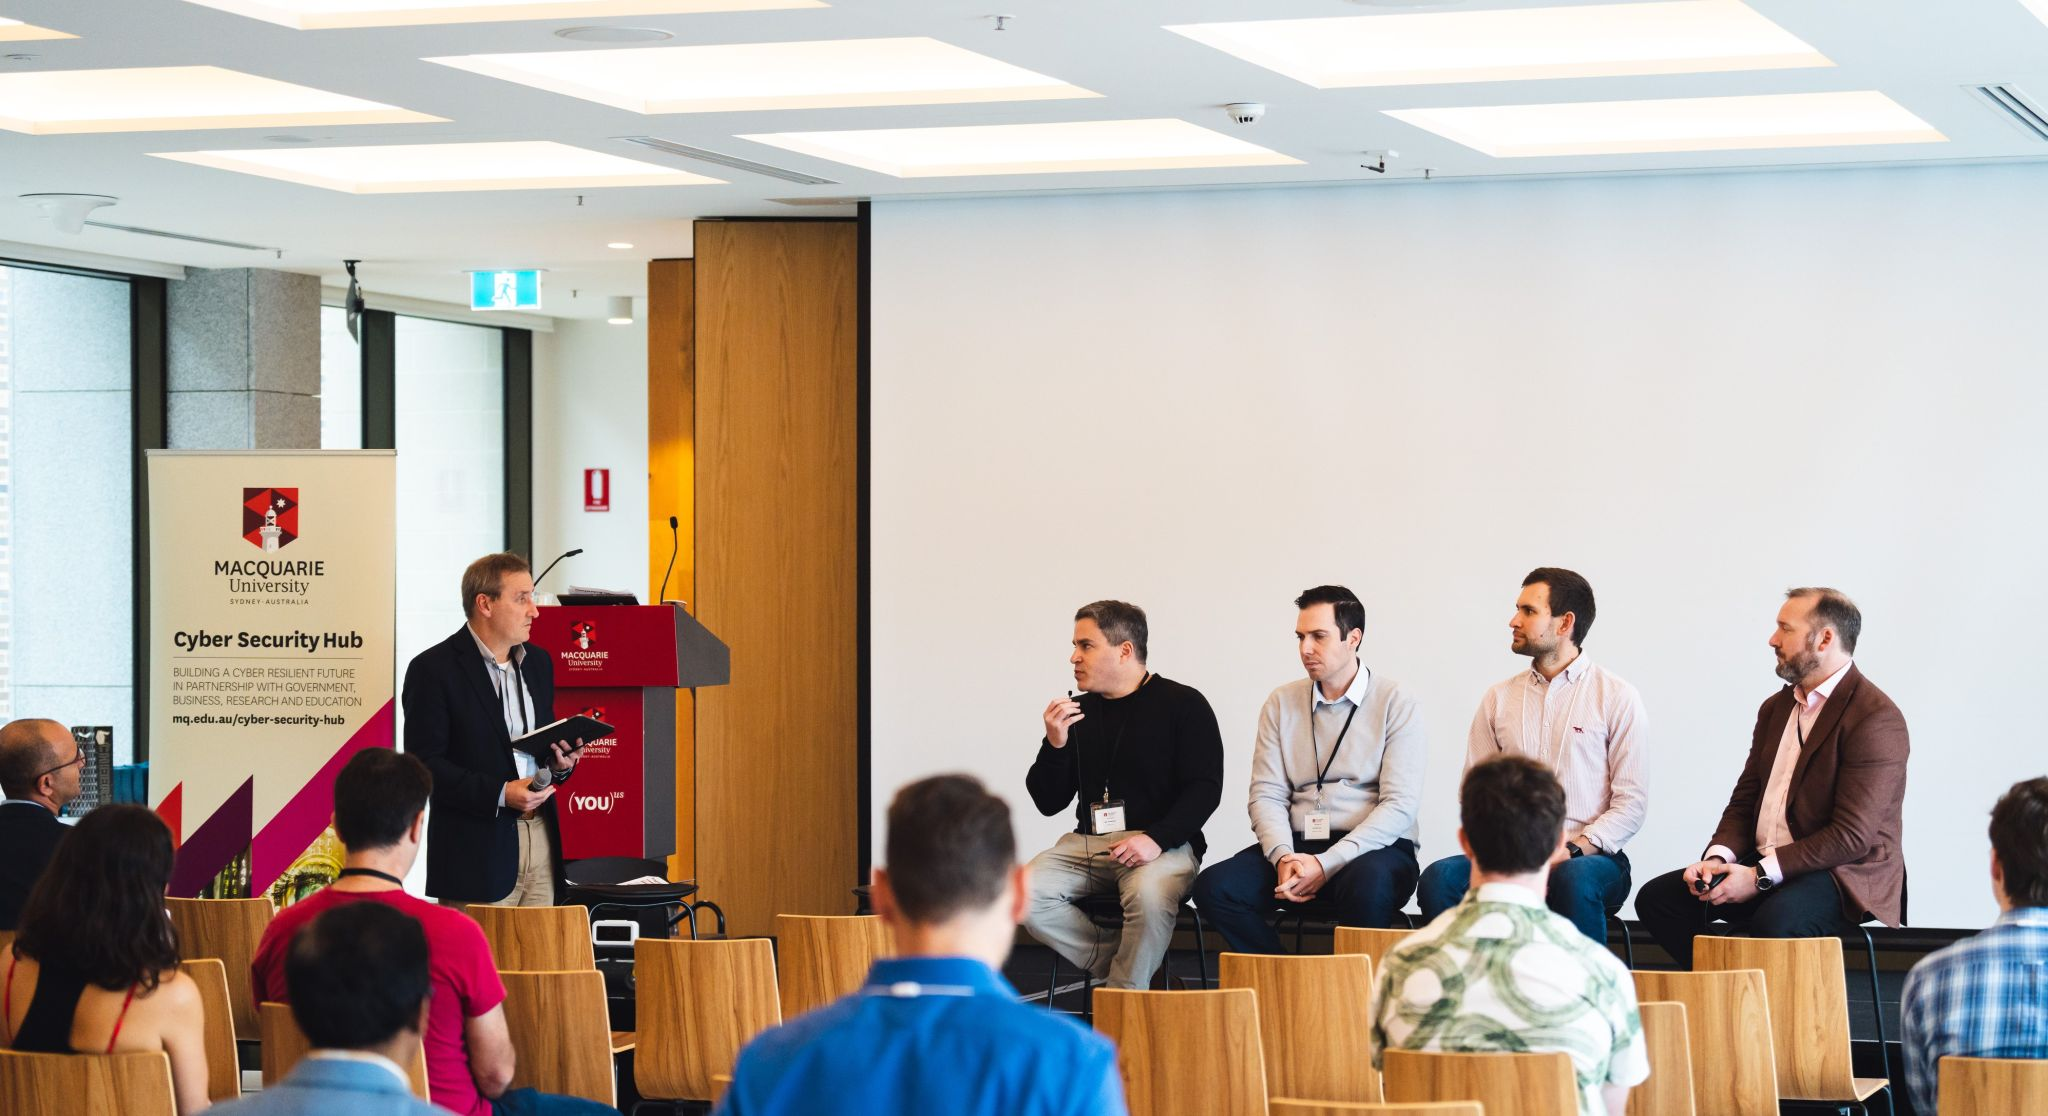
Trust in People: Macquarie University Cyber Security Industry Workshop

I’ve been invited to to share my thoughts on human-centric security at the Macquarie University Cyber Security Industry Workshop.

Drawing on insights from The Psychology of Information Security and my experience in the field, I outlined some of the reasons for friction between security and business productivity and suggested a practical approach to a building a better security culture in organisations.

It was great to be able to contribute to the collaboration between the industry, government and academia on this topic.

Ethical cyber security leadership

Picture an easy Sunday morning. It’s sunny and quiet with only birds chirping outside. You make yourself a cup of coffee and sit on the sofa to catch-up on what’s happening in the world. You open your favourite news site and here it is – first story of the day in large font.

Breaking news: massive data breach! It’s your company in the headline.

This is the modern reality, cyber attacks are becoming increasingly common and it’s no longer a matter of if but when.

How do you manage this PR nightmare? What do you tell the media? Can you regain the trust of your customers and partners?

These are not the questions you want to be thinking about in the middle of a crisis. The real story begins way before that. It starts with responsible data management practices and securing people’s information.

More