Cybersecurity Board reporting – CISO Executive Network

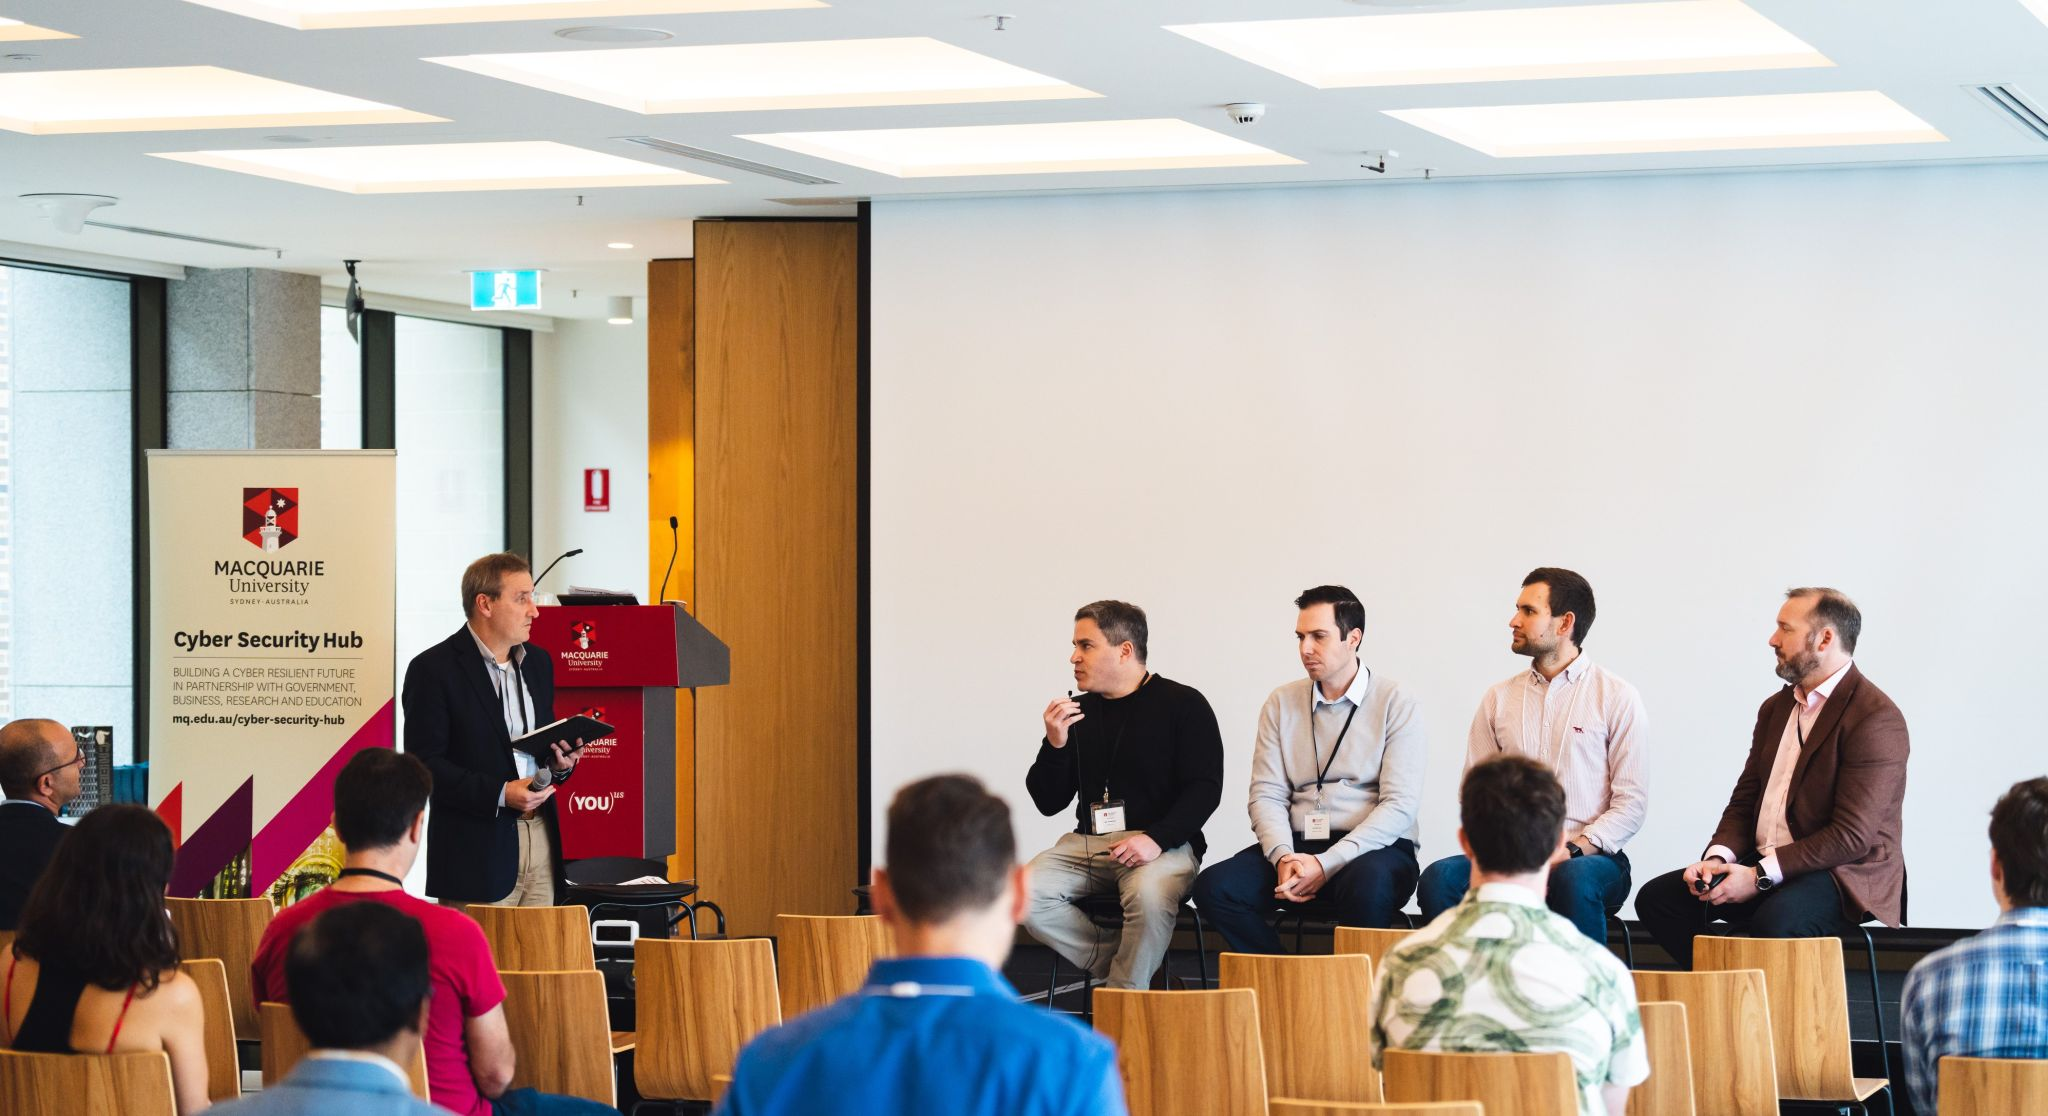
I had a pleasure to participate in the keynote panel discussion on cyber security Board reporting at the CISO Executive Network event in Sydney. It was an insightful discussion where I had a chance to share my views on aligning on Board expectations, developing relationships and tailoring your message for maximum impact.

We also covered common challenges and strategies for winning the Board over as well as good practices for reporting. It was a great opportunity to contribute to the community and learn from my peers in the industry.

Applying AI and ML techniques to combat scams and social engineering

I’m happy to share that after a long review process, our paper on identifying and extracting scam stages and scripts is finally published.

It’s been a great collaboration with Macquarie University to analyse scammers’ strategies that built a foundation for developing a Conversational AI bot that wastes scammers’ time.

Read full paper here: https://arxiv.org/abs/2307.01965

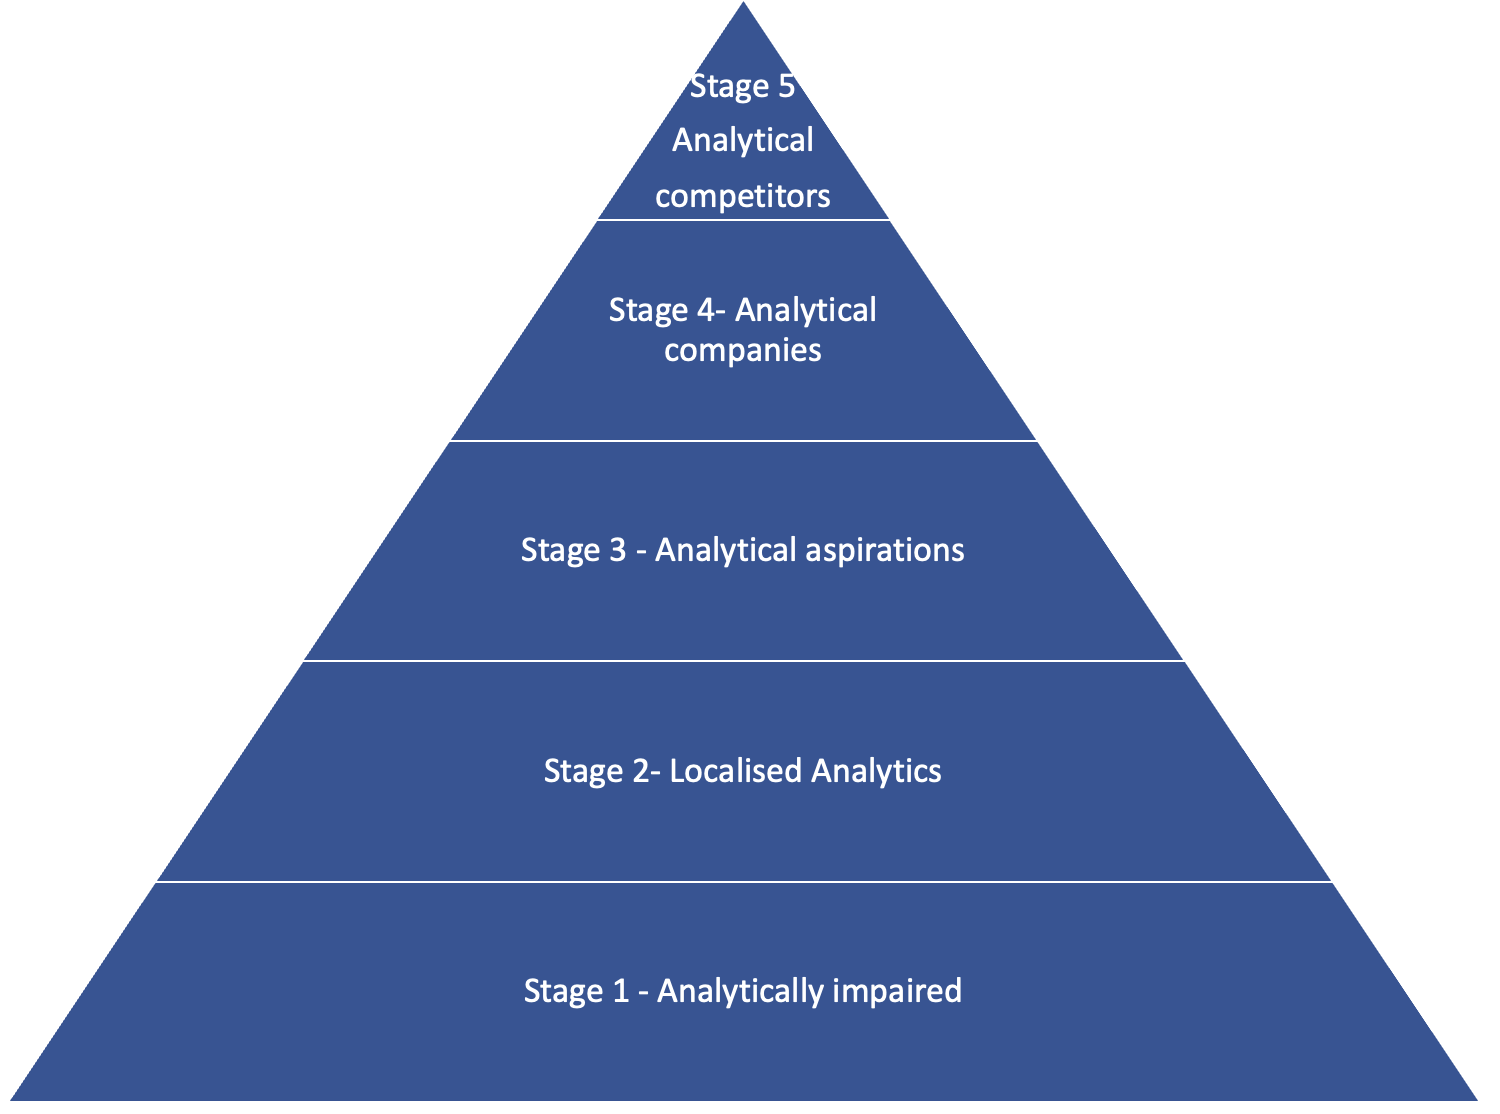
How to uplift your data analytics capability

Source: adapted from Davenport and Harris (2017)

Data strategy begins with an understanding of your business goals. What capabilities do you need to develop to realise your strategic objectives? In this blog I continue to build on the data analytics concepts to outline how to improve the analytics capability in your organisation.

More

Trust in People: Macquarie University Cyber Security Industry Workshop

I’ve been invited to to share my thoughts on human-centric security at the Macquarie University Cyber Security Industry Workshop.

Drawing on insights from The Psychology of Information Security and my experience in the field, I outlined some of the reasons for friction between security and business productivity and suggested a practical approach to a building a better security culture in organisations.

It was great to be able to contribute to the collaboration between the industry, government and academia on this topic.

Scuba diving and cyber security

During one of my dives I pondered if there are any parallels we can draw between scuba diving and cyber security. They may seem like vastly different activities, but they share many important similarities. Both are dealing with unknown and often rapidly changing environments, where careful preparation, attention to detail and a focus are critical for success. I list some themes in this blog, feel free leave a comment to add your own.

More

CISO’s perspective: a guest lecture at UNSW

As technology becomes increasingly integrated into our daily lives, the importance of cyber security cannot be overstated. Cyber attacks are becoming more sophisticated, and the costs associated with them are rising. This is why it is crucial for businesses and organisations to have a robust cyber security strategy in place.

Recently, I had the opportunity to deliver a guest lecture at the University of New South Wales as part of the Cybersecurity Management and Governance course.

I discussed the importance of having a clear understanding of cyber security threats. I emphasised that cyber threats are constantly evolving, and businesses need to stay vigilant and adapt their security measures accordingly. This means that cyber security is not a one-time fix; it requires continuous effort.

I also spoke about current challenges and opportunities in the field and what skills and ways of thinking are particularly useful. It was a fantastic experience, and I appreciated the chance to share my insights with a group of future cyber security professionals.

Ethical cyber security leadership

Picture an easy Sunday morning. It’s sunny and quiet with only birds chirping outside. You make yourself a cup of coffee and sit on the sofa to catch-up on what’s happening in the world. You open your favourite news site and here it is – first story of the day in large font.

Breaking news: massive data breach! It’s your company in the headline.

This is the modern reality, cyber attacks are becoming increasingly common and it’s no longer a matter of if but when.

How do you manage this PR nightmare? What do you tell the media? Can you regain the trust of your customers and partners?

These are not the questions you want to be thinking about in the middle of a crisis. The real story begins way before that. It starts with responsible data management practices and securing people’s information.

More