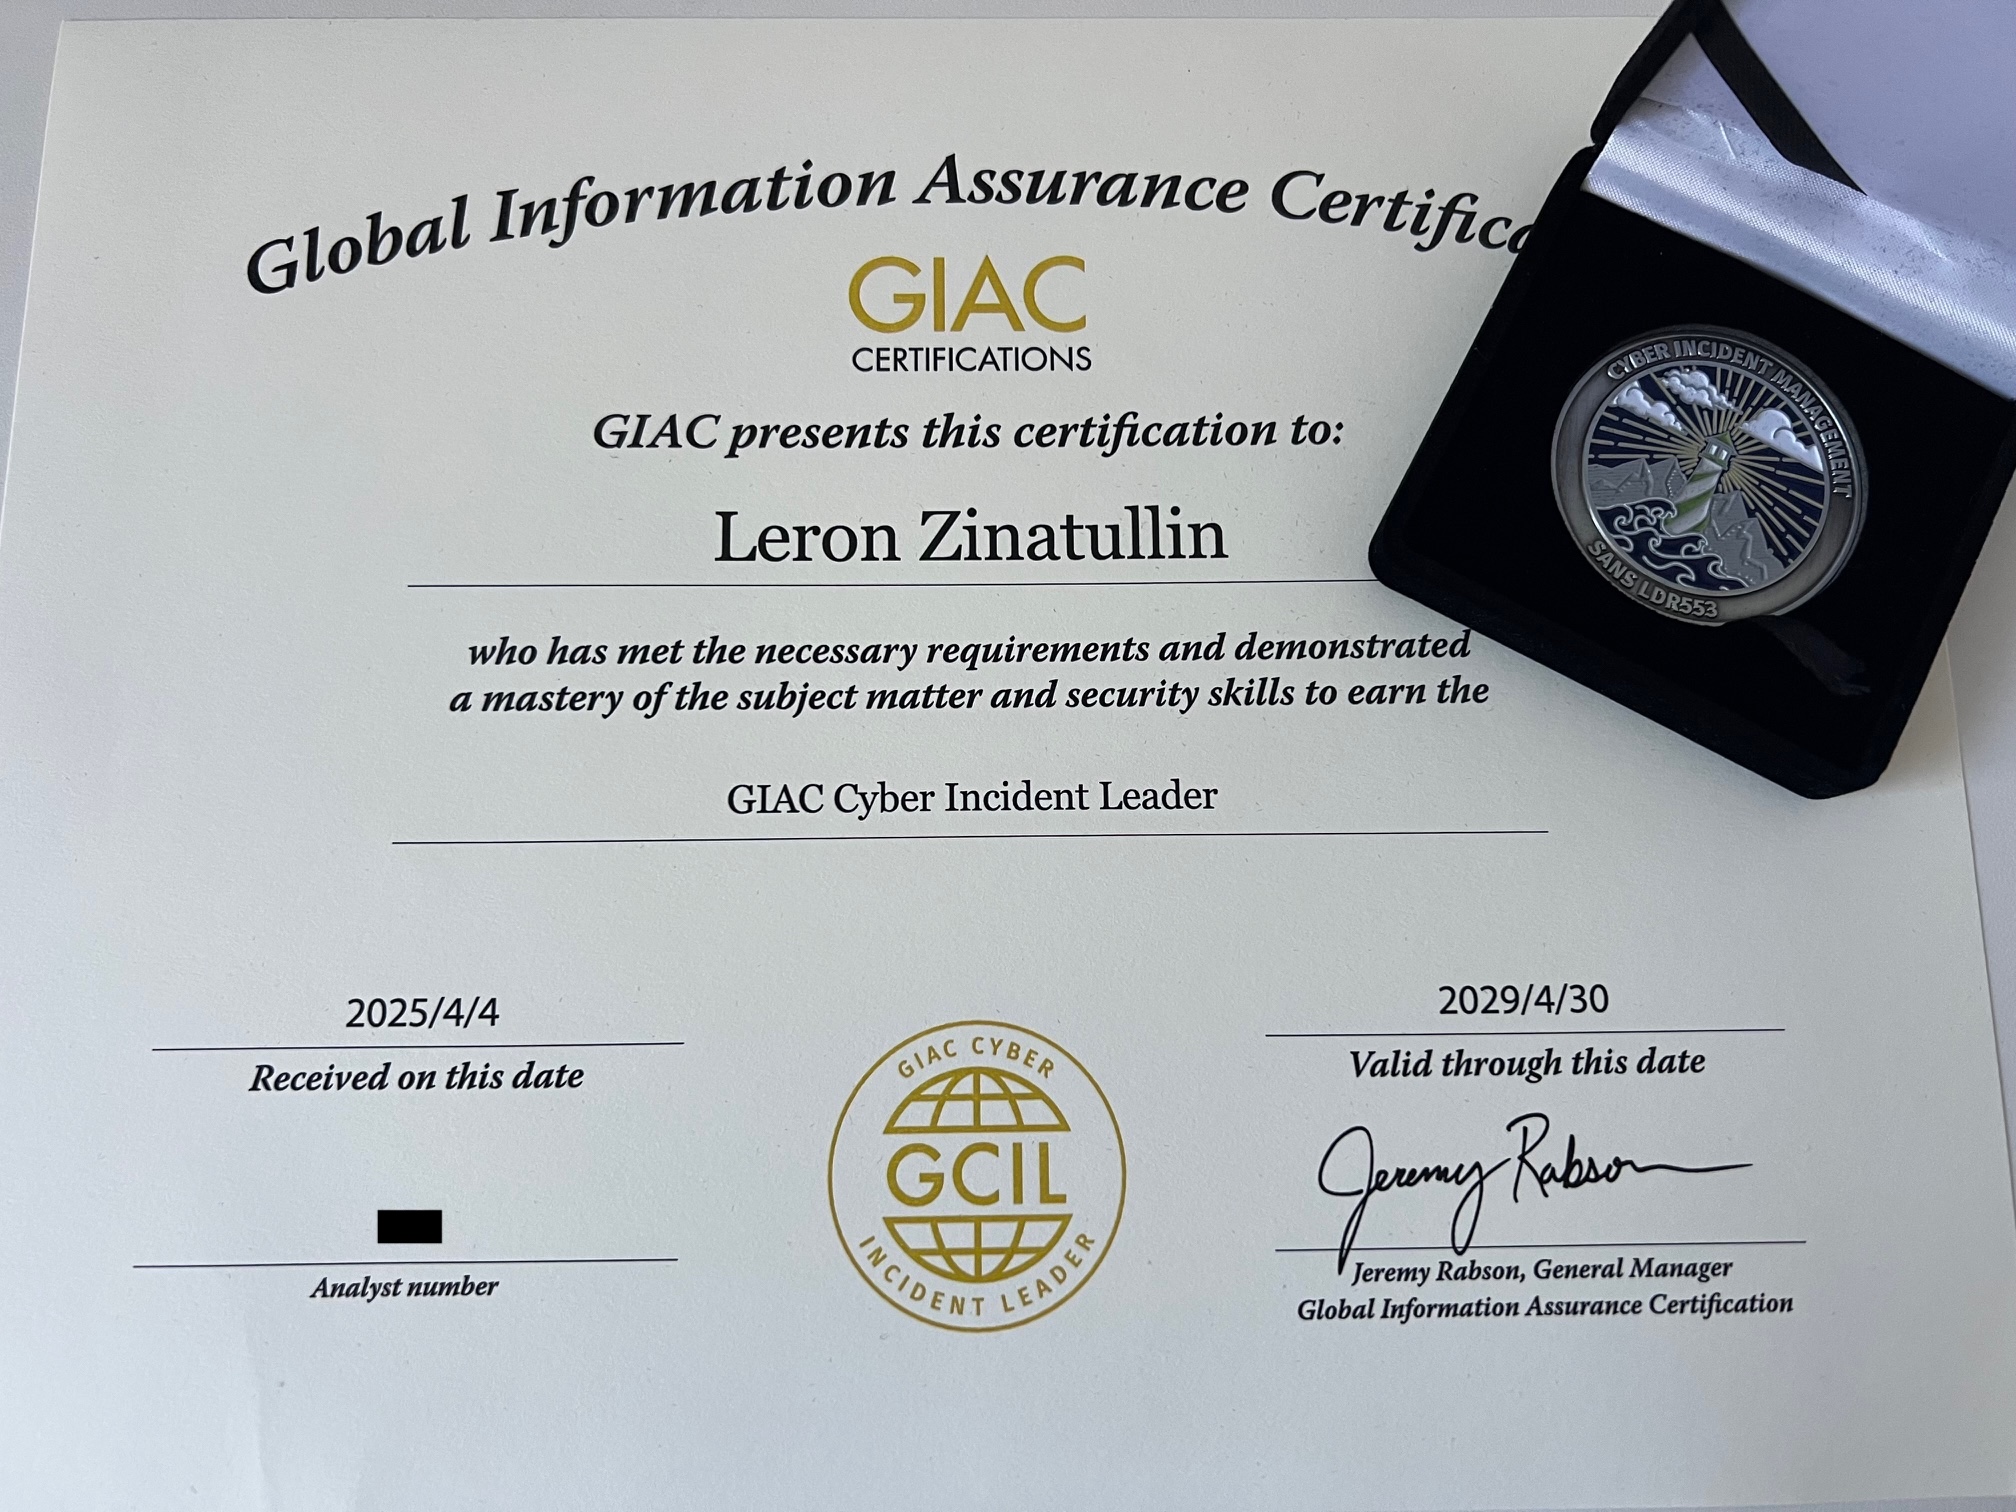
I’m proud to share that I’ve completed SANS’s LDR553: Cyber Incident Management hands-on training and earned the GIAC Cyber Incident Leader (GCIL) certification.
This course sharpened my ability to guide teams through every stage of a breach. I was awarded a challenge coin for the top score in the final capstone project.
I’m thrilled to share that I’ve recently earned the GIAC Strategic Planning, Policy, and Leadership (GSTRT) certification- a milestone that validates my ability to architect and sustain cybersecurity programs with a sharp focus on business value and executive alignment.
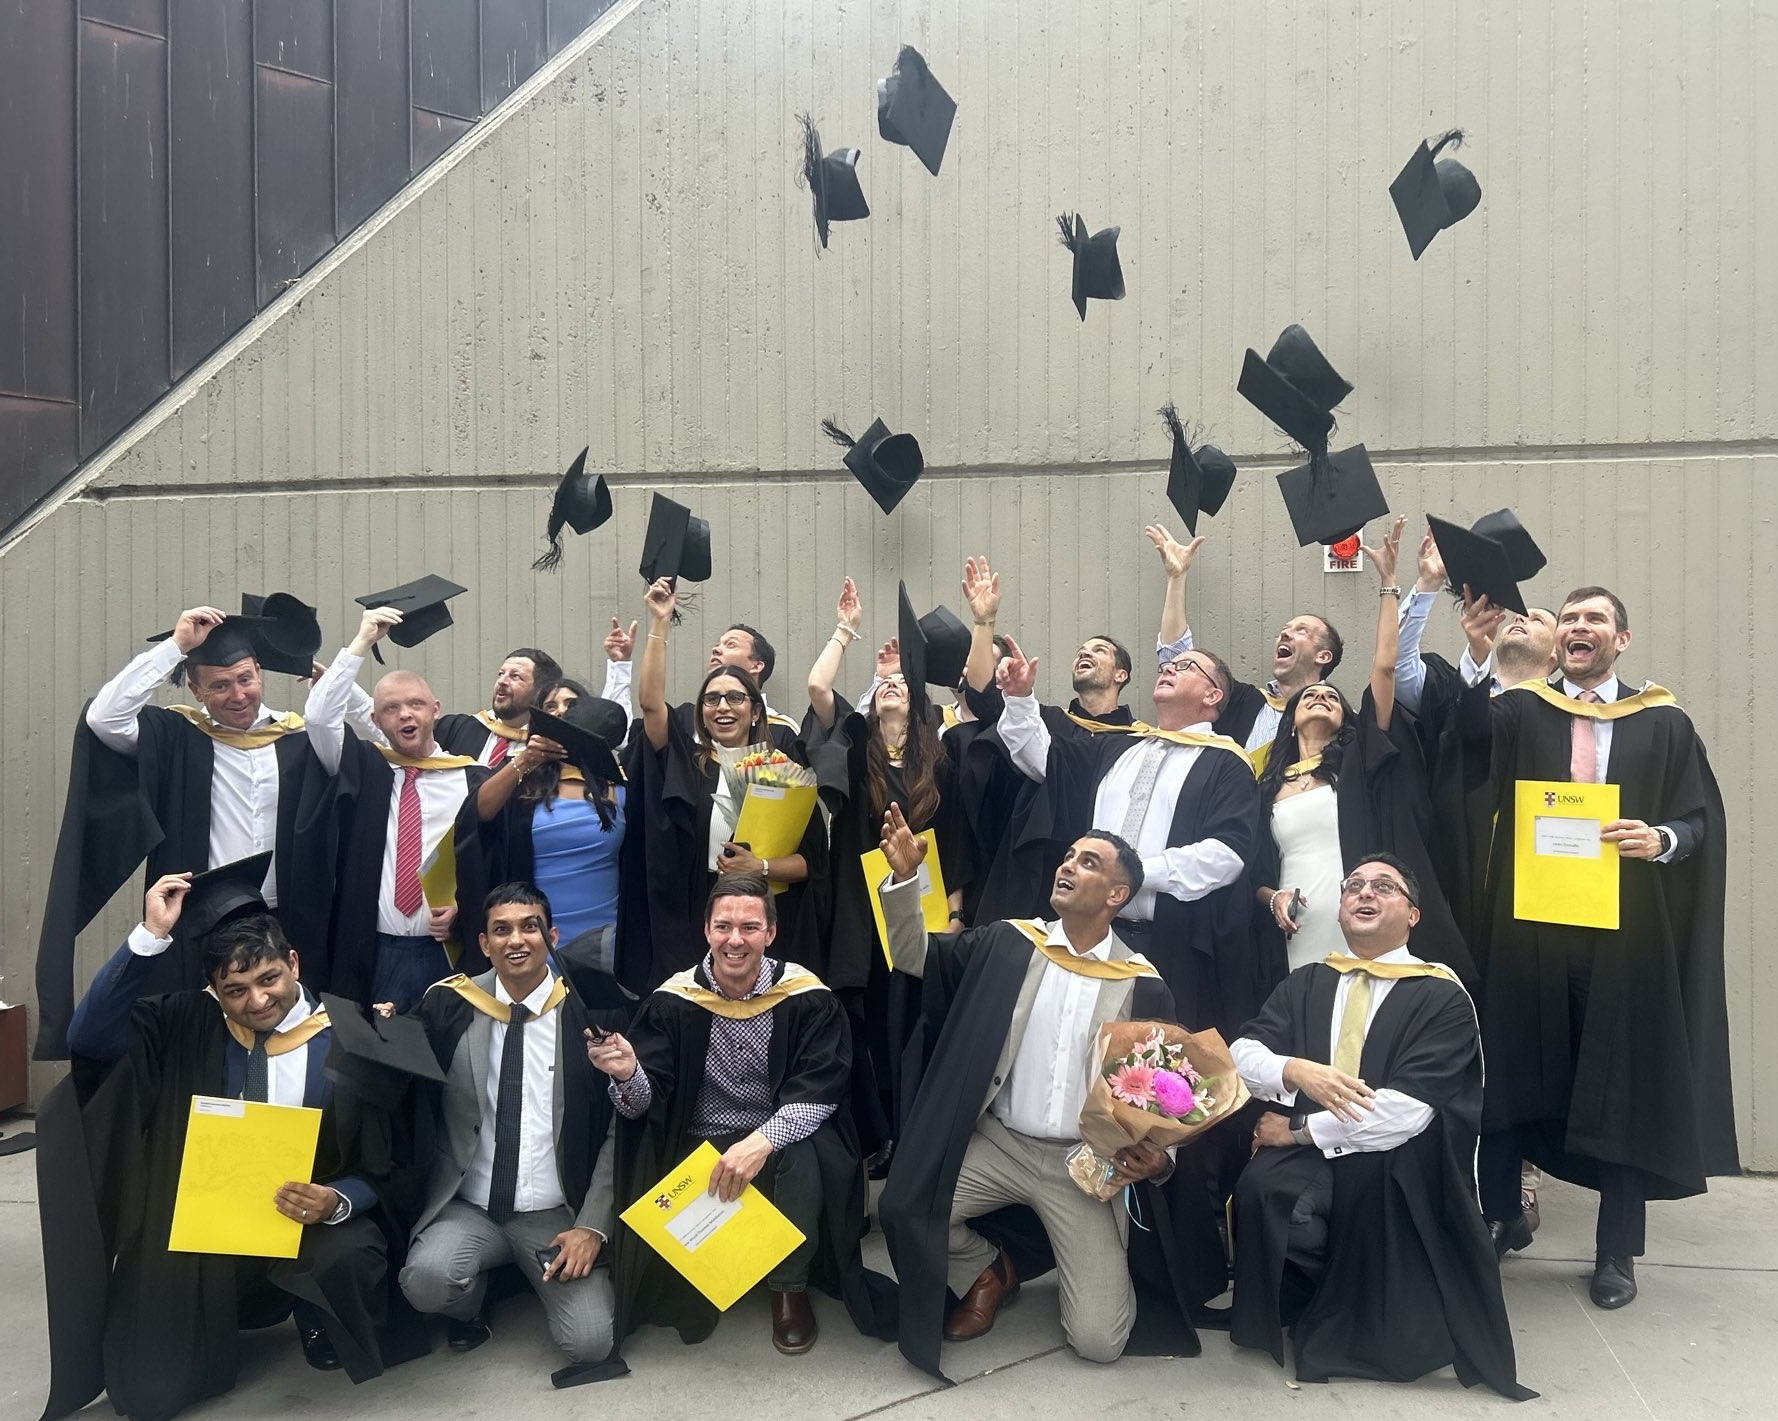
I’m excited to share that I have graduated with Excellence from the Executive MBA program at AGSM UNSW Business School. This transformative 2-year journey has been as challenging as it has been rewarding, redefining my approach to strategy, leadership and execution.
Throughout the program, I had an incredible opportunity to bring theory into practice – collaborating with a diverse cohort of leaders to work on real-world challenges across Australian industries such as technology, manufacturing, financial services and retail. These experiences not only honed my analytical skills but also deepened my appreciation for applying business concepts in evolving fields like cybersecurity and AI.
The international exchanges were equally transformative. Spending time in Shanghai at Fudan University and completing a semester at Yale School of Management allowed me to engage with global leaders, enhancing my understanding of cross-cultural leadership. The practical case studies and strategic projects I completed in these environments reinforced the significance of a global mindset in today’s interconnected world.
With courses ranging from accounting and marketing to negotiations, I am grateful for every lesson learnt, every challenge overcome and every connection made along the way. I look forward to leveraging these insights to drive innovation, inspire ethical leadership and create meaningful impact.
This recognition reflects the hard work and dedication of my incredible team, as well as the support from colleagues, partners and the wider community.
Cybersecurity is a collective effort and I’m grateful to contribute to an industry that plays such a vital role in keeping organisations and people safe.
A huge thank you to everyone who has been part of this journey – I couldn’t have done it without you. And congratulations to all the finalists!
Cyber security is a relentless race to keep pace with evolving threats, where staying ahead isn’t always possible. Advancing cyber maturity demands more than just reactive measures—it requires proactive strategies, cultural alignment, and a deep understanding of emerging risks.
I had an opportunity to share my thoughts on staying informed about threats, defining cyber maturity, and aligning security metrics with business goals with Corinium’s Maddie Abe ahead of my appearance as a speaker at the upcoming CISO Sydney next month.
In this blog, I’m going to expand on my observations from working with Indigenous communities in Australia. I’ll adopt a more structured approach to reflective practice to crystallise the insights from my final project and the entire MBA journey.
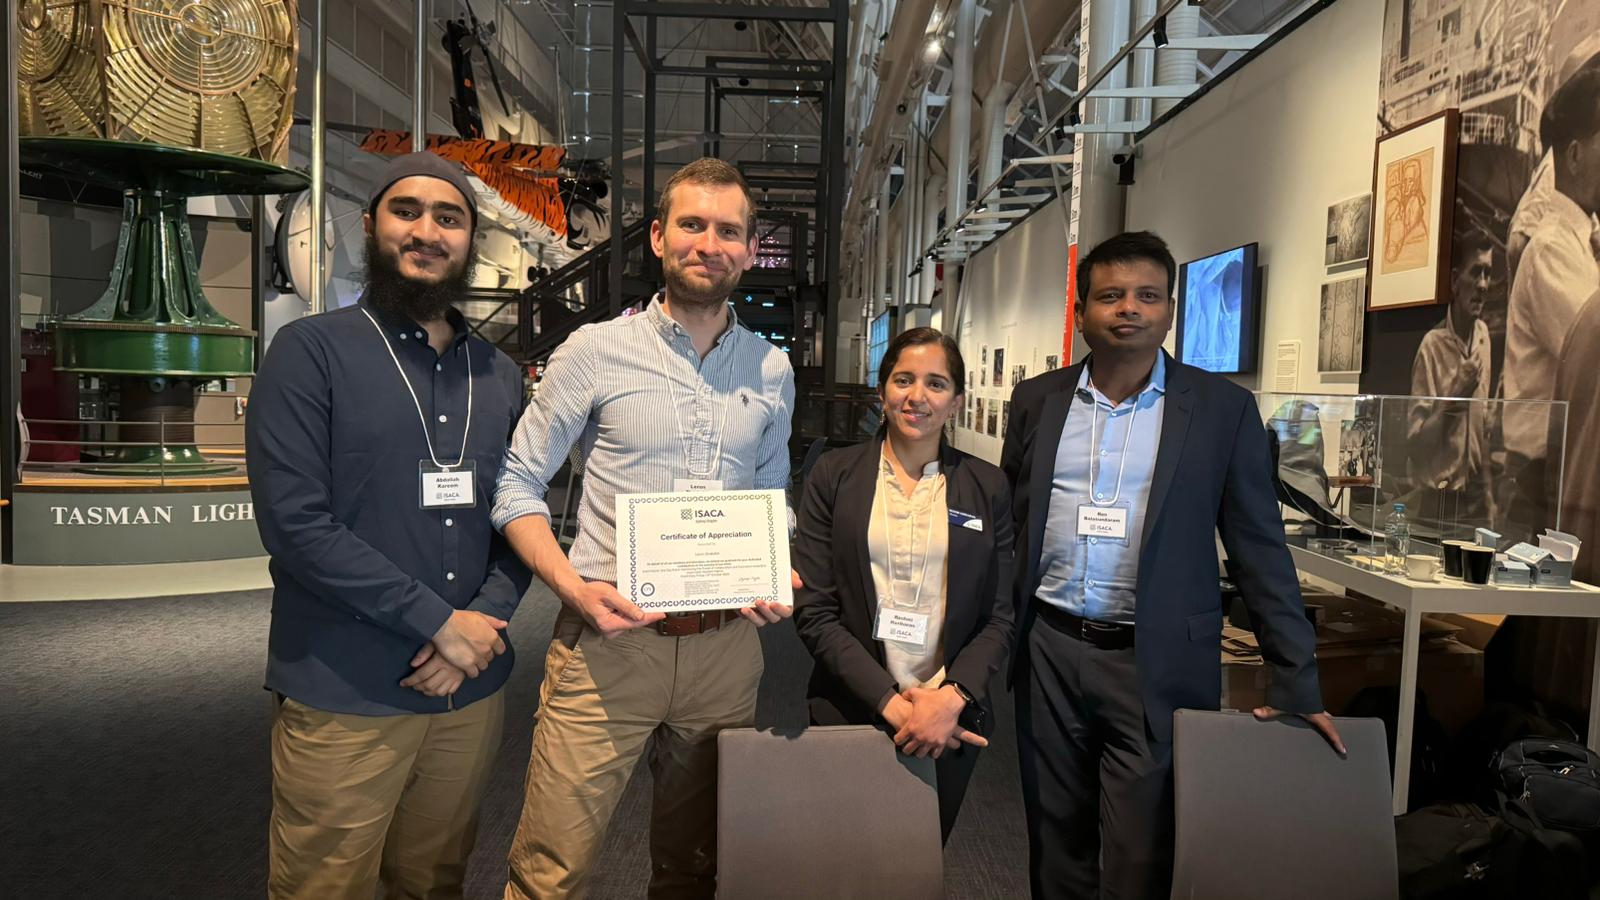
It’s been fantastic to have an opportunity to give back to the community and volunteer with ISACA this year.
The Sydney Chapter hosted a number of professional development events for cyber, risk, governance and IT professionals with a common objective of building digital trust and securing our interconnected world. I had a chance to support these initiatives, ranging from fundraising for a mental health charity to helping organise conferences.
I found this experience incredibly rewarding and made some good friends along the way.
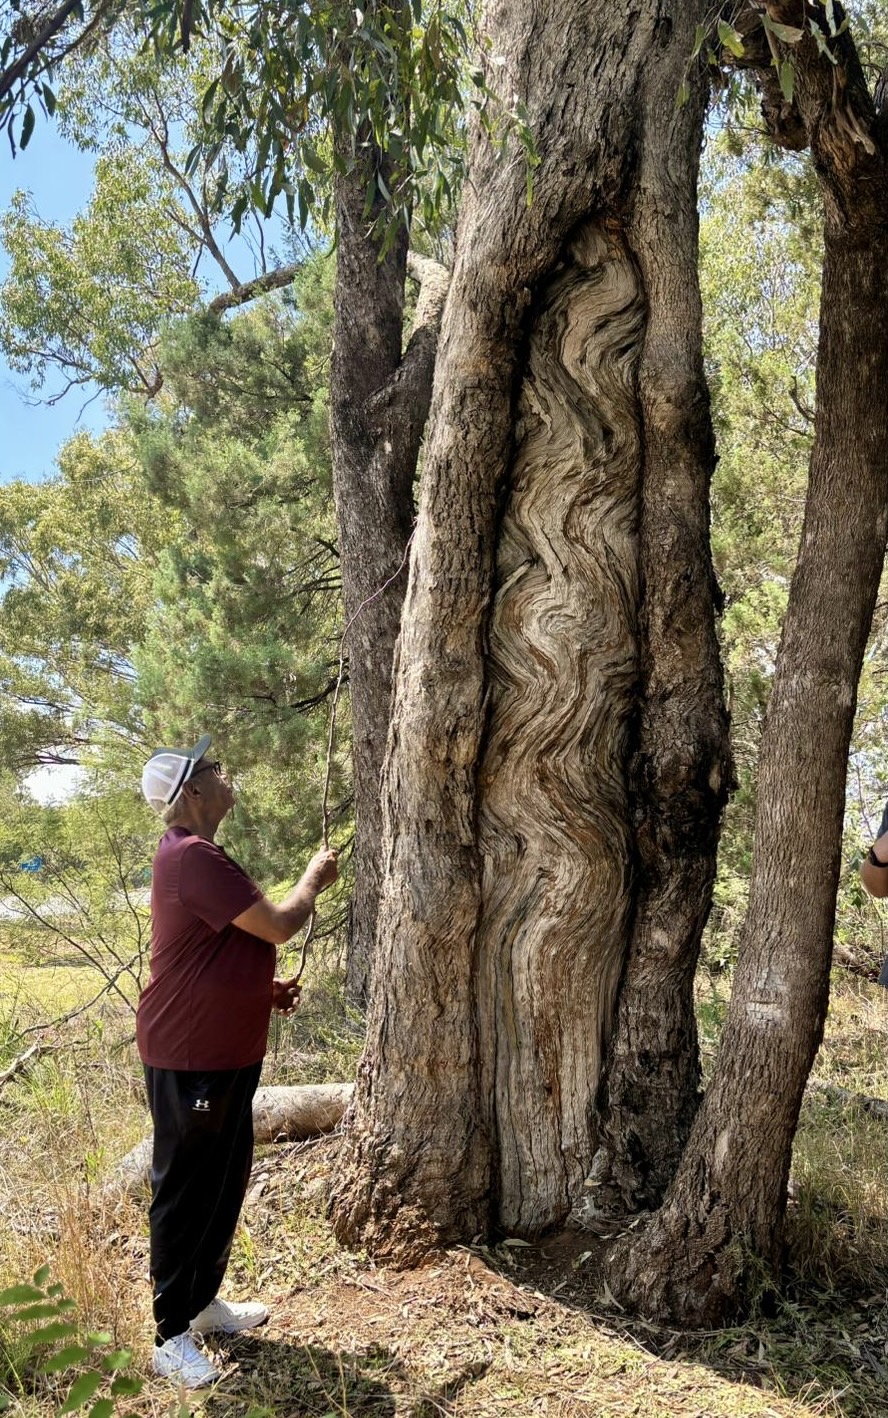
I just spent an incredible week immersed in Aboriginal culture, where I had the privilege of working shoulder to shoulder with First Nations organisations as part of my AGSM Executive MBA journey.
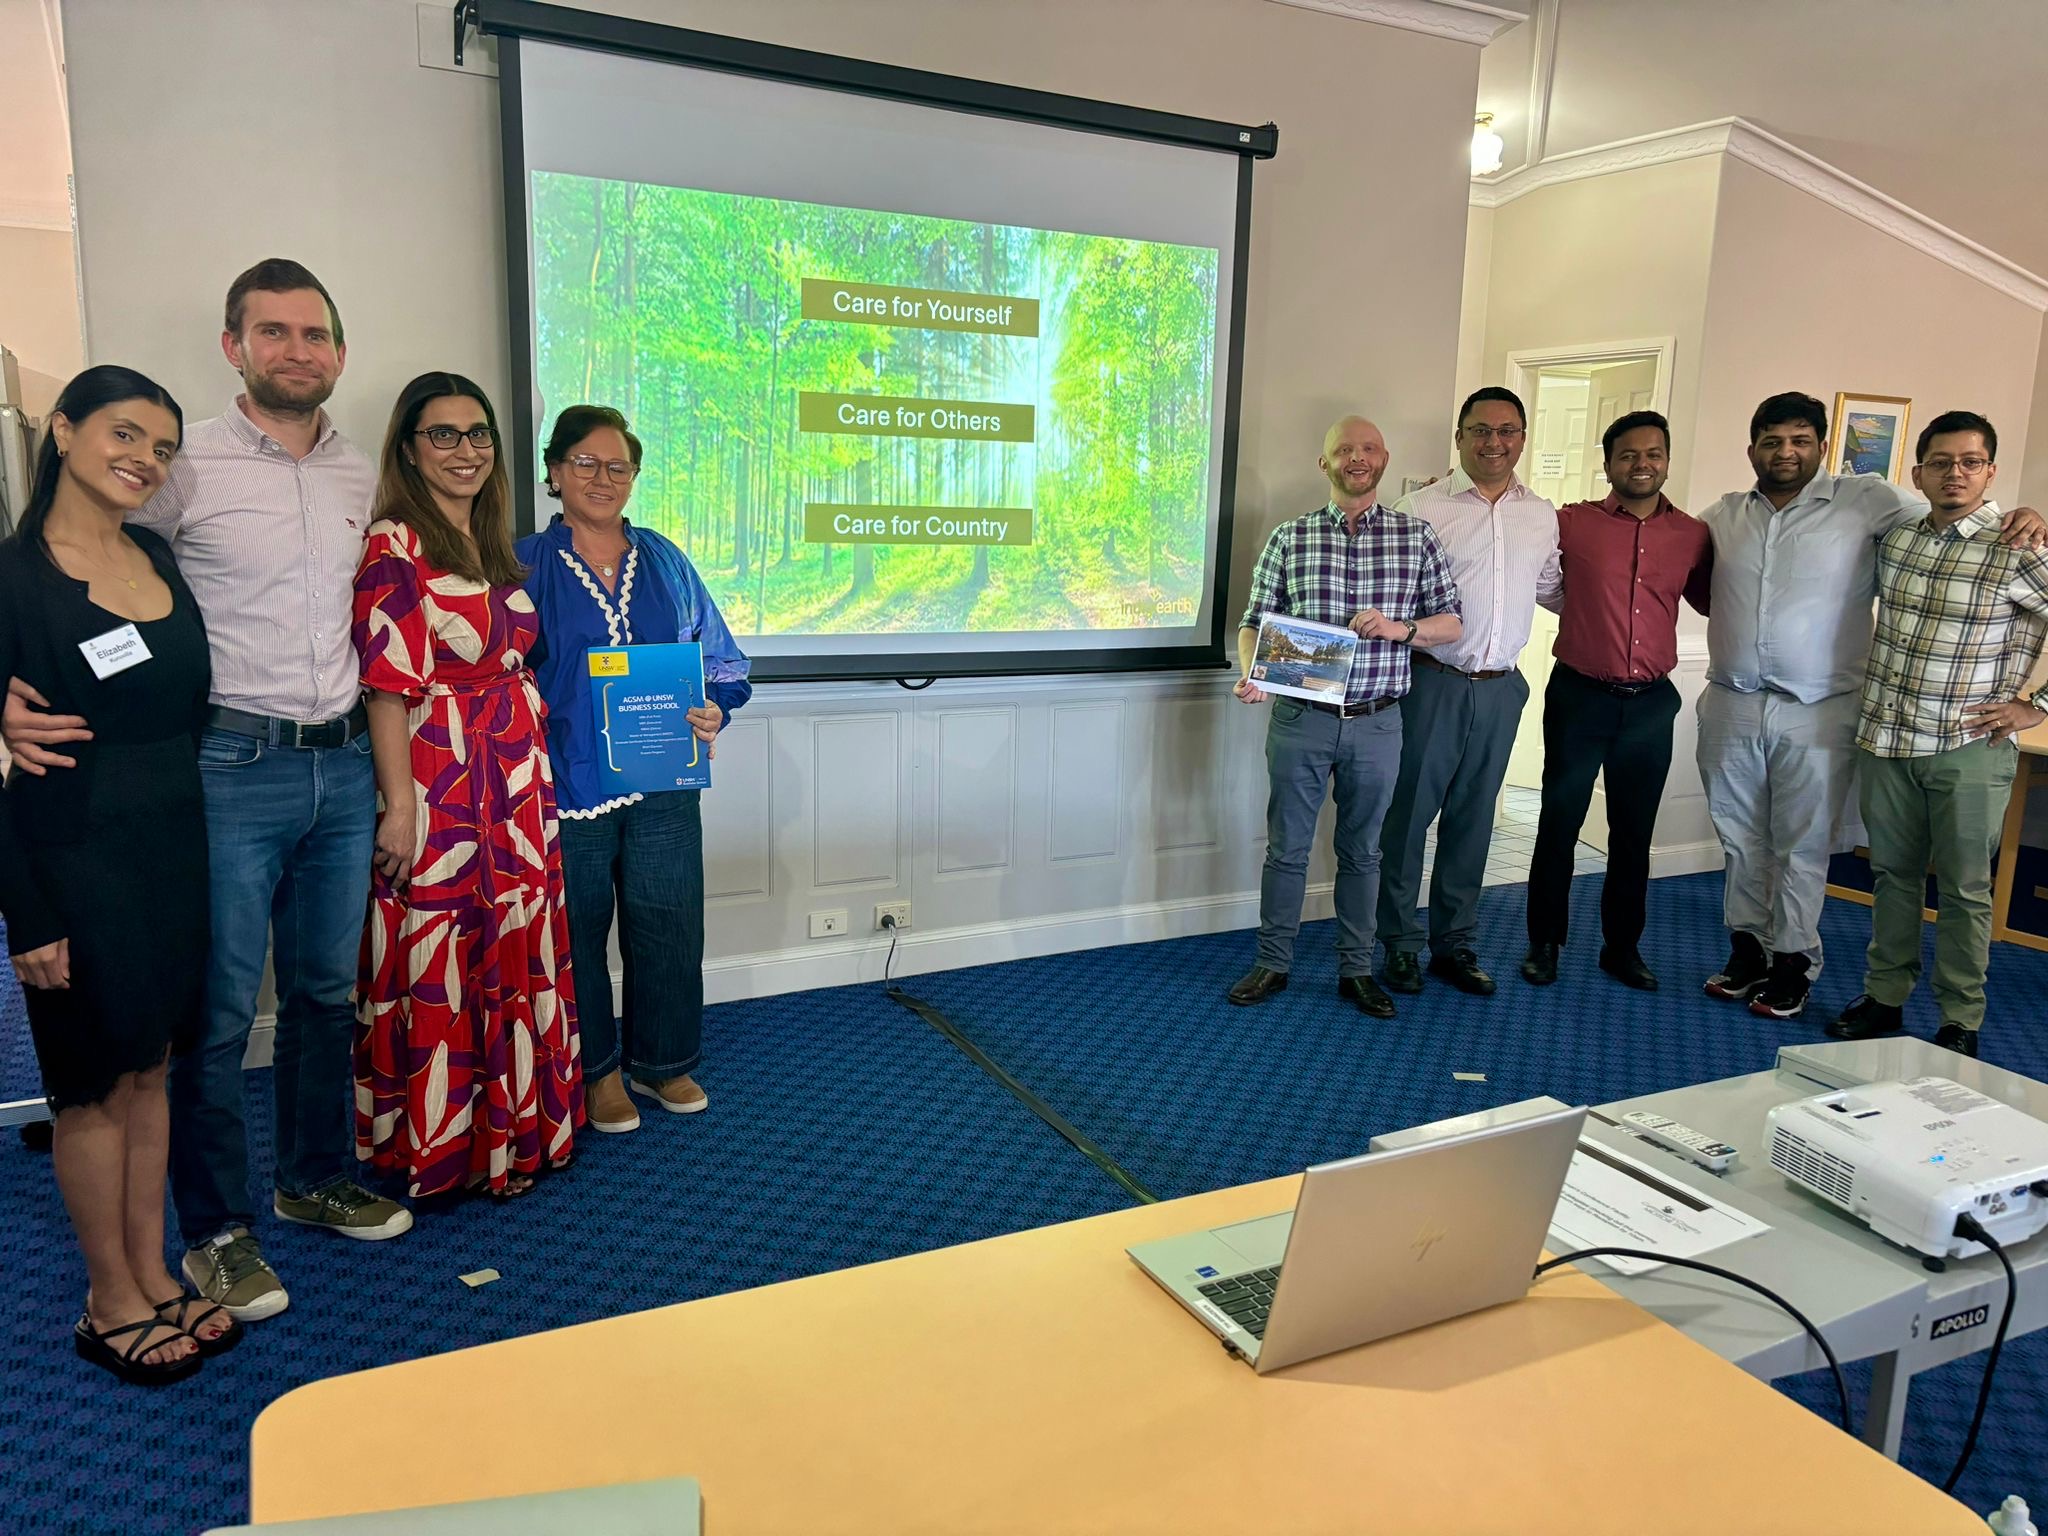
This experiential learning project allowed me to take the academic knowledge from all my previous MBA courses and apply it in real-world contexts. What a great way to wrap up the program!
It was also an opportunity to deliver the final client presentation to Indigiearth, a 100% Aboriginal-owned native foods business, concluding the capstone strategic consulting engagement we’ve been working on this term.
Learning directly from Elders and community members enriched my understanding of Aboriginal traditions, values and the profound connection to land that underpins Indigenous enterprises. I’m proud to have been a part of this journey, bringing together cultural respect and strategic vision.
In cybersecurity, collaboration is essential. With growing complexity in the threat landscape, leaders often find themselves working with parties they may not fully align with—whether internal teams, external stakeholders, or even rival firms.
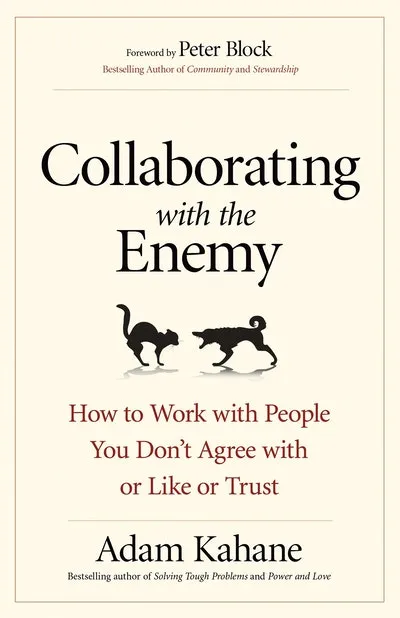
Adam Kahane’s book Collaborating with the Enemy: How to Work with People You Don’t Agree with or Like or Trust outlines principles for collaborating effectively, especially in challenging environments where trust and agreement are minimal. Kahane’s “stretch collaboration” approach can transform the way cybersecurity leaders address conflicts and turn rivals into partners to meet critical security goals. In this blog, I’ll share my key takeaways.
Adapted from Kotter, J. 2007, ‘Leading change: Why transformation efforts fail’, Harvard Business Review, vol. 73, no. 2, pp. 1–10.
Cyber security leaders have to be effective change agents to be successful. Cyber capability uplift and risk reduction initiatives often require significant transformation in the organisation. In this blog, I’ll introduce a tried and tested change management framework and demonstrate its application to cyber security in an illustrative case study.