Asset management is often regarded as the foundation of a security programme. You can’t protect something that you don’t know you have. This extends beyond internal systems to your organisation’s partners. Depending on the line of business, supply chains can get increasingly complex. They include vendors, manufacturers, retailers and distributors in multiple geographies and regulatory regimes. Securing such a network is no easy task and should start with visibility and careful risk management.
I previously wrote about the complexity of communication and the multi-faceted nature of the CISO role. Combining these perspectives, I would like to give an overview of what a communication strategy might look like for a security leader.
I recently had a chance to collaborate with researchers at The Optus Macquarie University Cyber Security Hub. Their interdisciplinary approach brings industry practitioners and academics from a variety of backgrounds to tackle the most pressing cyber security challenges our society and businesses face today.
Both academia and industry practitioners can and should learn from each other. The industry can guide problem definition and allow access to data, but also learn to apply the scientific method and test their hypotheses. We often assume the solutions we implement lead to risk reduction but how this is measured is not always clear. Designing experiments and using research techniques can help bring the necessary rigour when delivering and assessing outcomes.
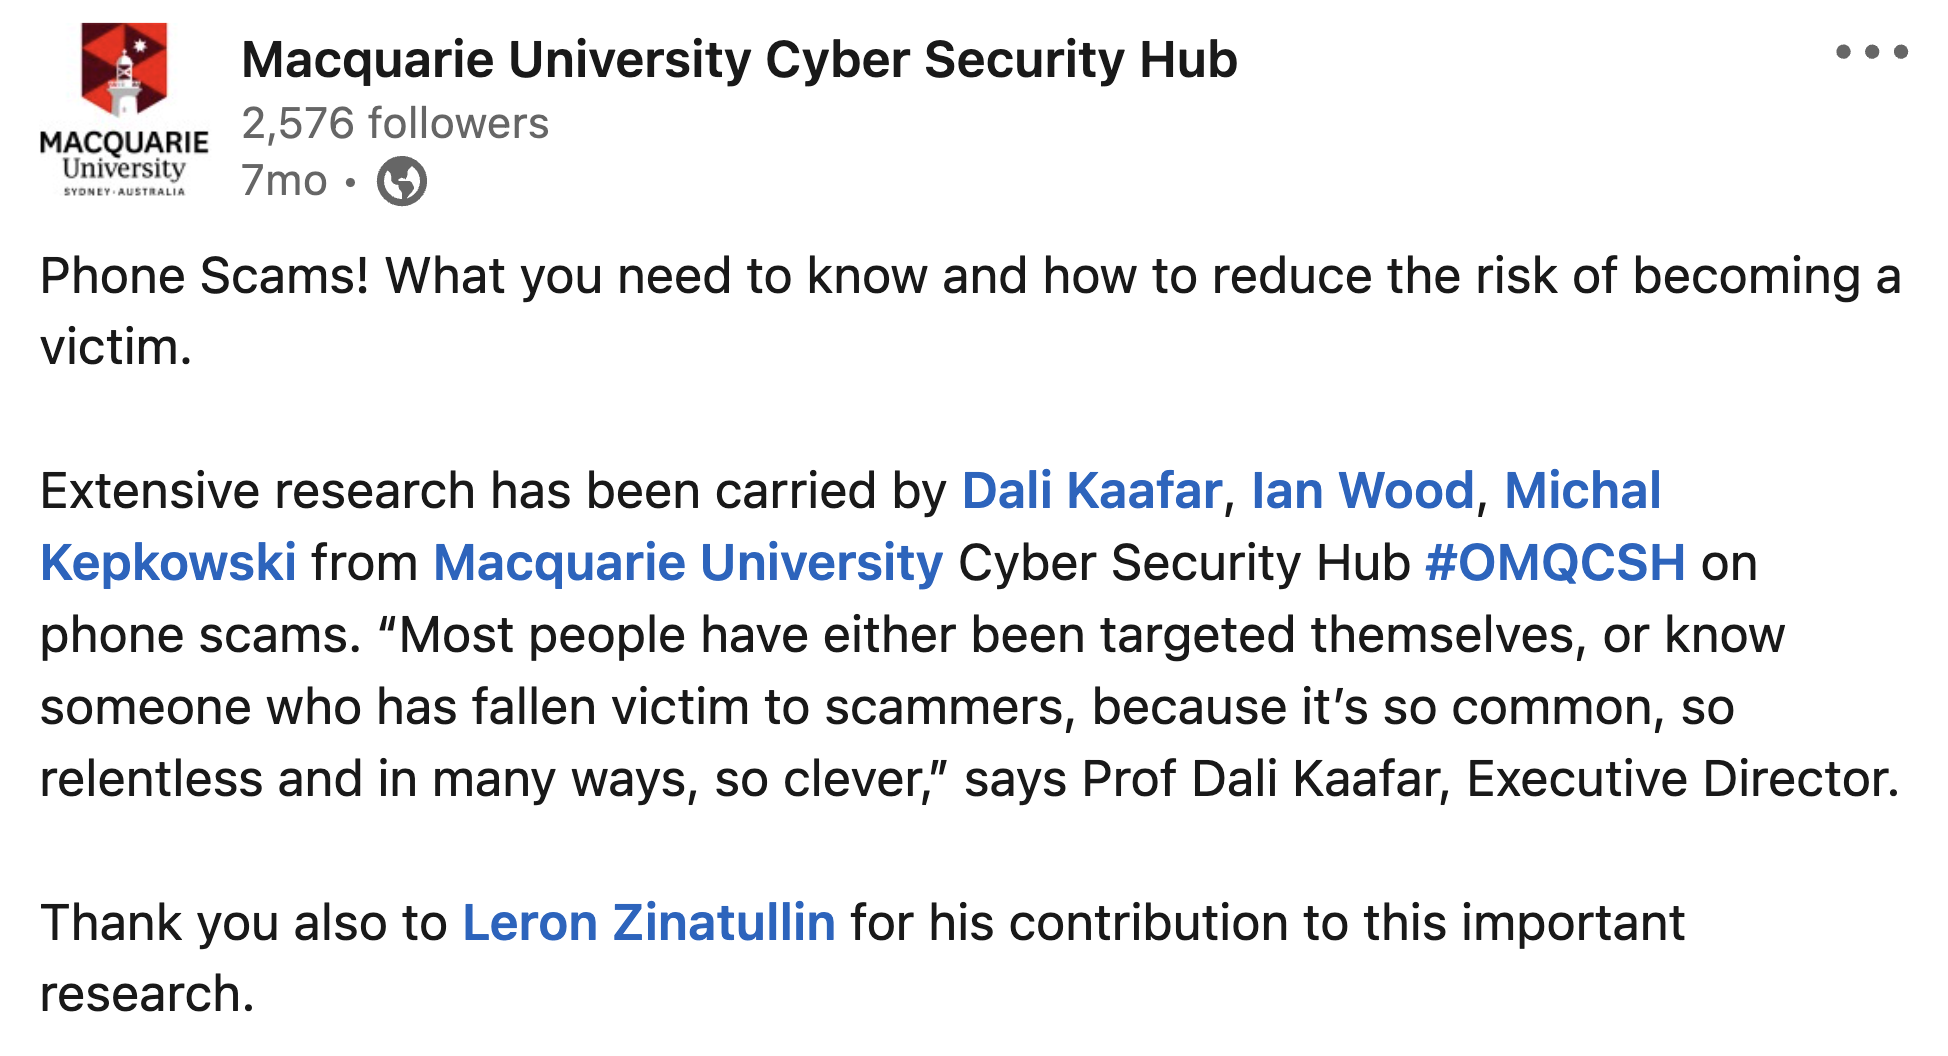
I had an opportunity to work on some exciting projects to help build an AI-powered cyber resilience simulator, phone scam detection capability and investigate the role of human psychology to improve authentication protocols. I deepened my understanding of modern machine learning techniques like topic extraction and emotion analysis and how they can be applied to solve real world problems. I also had a privilege to contribute to a research publication to present our findings, so watch this space for some updates next year.
NISTIR 7756 Contextual Description of the CAESARS System
Knowing your existing assets, threats and countermeasures is a necessary step in establishing a starting point to begin prioritising cyber risk management activities. Indeed, when driving the improvement of the security posture in an organisation, security leaders often begin with getting a view of the effectiveness of security controls.
A common approach is to perform a security assessment that involves interviewing stakeholders and reviewing policies in line with a security framework (e.g. NIST CSF).
A report is then produced presenting the current state and highlighting the gaps. It can then be used to gain wider leadership support for a remediation programme, justifying the investment for security uplift initiatives. I wrote a number of these reports myself while working as a consultant and also internally in the first few weeks of being a CISO.
These reports have a lot of merits but they also have limitations. They are, by definition, point-in-time: the document is out of date the day after it’s produced, or even sooner. The threat landscape has already shifted, state of assets and controls changed and business context and priorities are no longer the same.
The worst time to write a security incident response plan is during an incident itself. Anticipating adverse events and preparing playbooks for likely scenarios and testing them in advance are important facets of a wider cyber resilience strategy.
Incident response, however, is not only about technology, logs and forensic investigation – managing communication is equally important. It is often a compliance requirement to notify the relevant regulator and customers about a data breach or a cyber incident, so having a plan, as well as an internal and external communication strategy, is key.
Security incidents can quickly escalate into a crisis depending on their scale and impact. There are lessons we can learn from other disciplines when it comes to crisis communication.
One of the best example is offered by the Centers for Disease Control and Prevention (CDC). The resources, tools and training materials they have created and made available online for free have been tested in emergency situations around the world, including the latest Covid-19 pandemic.
CDC’s Crisis and Emergency Risk Communication (CERC) manuals and templates emphasise the six core principles of crisis communication:
1. Be first. Quickly sharing information about an incident can help stop the spread, and prevent or reduce impact. Even if the cause is unknown, share facts that are available.
2. Be right. Accuracy establishes credibility. Information should include what is known, what is not known, and what is being done to fill in the information gaps.
3. Be credible. Honesty, timeliness, and scientific evidence encourage the public to trust your information and guidance. Acknowledge when you do not have enough information to answer a question and then work with the appropriate experts to get an answer.
4. Express empathy. Acknowledging what people are feeling and their challenges shows that you are considering their perspectives when you give recommendations.
5. Promote action. Keep action messages simple, short, and easy to remember.
6. Show respect. Respectful communication is particularly important when people feel vulnerable. Respectful communication promotes cooperation and rapport.
Cyber security professionals can adopt the above principles in crisis situations during a cyber incident, demonstrating commitment and competence and communicating with transparency and empathy both inside and outside of the organisation.
Managing change and improving security culture should start with understanding the organisation, the people in it and what drives them.
In the case of cyber security, this begins with understanding why current security practices might not be effective and why people often find workarounds rather than follow security processes.
Security professionals have access to the amounts of data never seen before. Antivirus software, firewalls, data loss prevention solutions – they all generate a staggering amount of alerts.
Security operation centres and the underlying SIEM technology allow us to aggregate, correlate and make sense of these vast troves of data. We can create dashboards and metrics that might look slick and even be useful to security teams but do such data add value to business stakeholders? Do they tell a story to the Board?
I have been fortunate to help and collaborate with a wide variety of organisations during my cyber security career to date. These companies range from large multinationals that are household names to small tech startups that you probably haven’t even heard of.
Although the regulatory landscape, security maturity and key risks often vary dramatically between industries, there are common themes that both an upstart FinTech and an energy giant can benefit from.
Being able to see what works, for example, in the world of Operational Technology and apply some of the learnings to an insurance company and vice versa can bring a fresh perspective and result in unique solutions that can be easily overlooked in traditional sector-specific paradigms. Identifying these synergies and collaboration opportunities between organisations of different sizes, industries, cultures and technological stacks has allowed me to better understand specific issues, challenge the conventional thinking and tailor my advice to fit the overall strategy of a given organisation for best results.
Who needs to buy e-learning modules for employee security awareness programmes when NCSC kindly made available their training for free?
NCSC’s Top Tips For Staff includes online videos (that can be also included in your own learning management system), knowledge check and an infographic.
It’s a quick and easy way to get you started on the journey of building security culture in your company and meet some of the compliance requirements. This can be especially helpful for startups and non-profits with limited budgets.