How to achieve SOC 2 Type 2 attestation

As a CISO who recently led an organisation through successful SOC 2 Type 1 and Type 2 audits, I’d like to share some insights and steps to help others on their journey toward SOC 2 attestation.

SOC 2 may not be for everyone (refer to my blog on compliance frameworks), but it can be useful for organisations dealing with sensitive customer data, particularly in SaaS, as it demonstrates a commitment to security, privacy, and data integrity. The journey toward SOC 2 attestation can be complex, but with careful planning and the right strategies, it’s achievable.

More

Change management and cyber security

Adapted from Kotter, J. 2007, ‘Leading change: Why transformation efforts fail’, Harvard Business Review, vol. 73, no. 2, pp. 1–10.

Cyber security leaders have to be effective change agents to be successful. Cyber capability uplift and risk reduction initiatives often require significant transformation in the organisation. In this blog, I’ll introduce a tried and tested change management framework and demonstrate its application to cyber security in an illustrative case study.

More

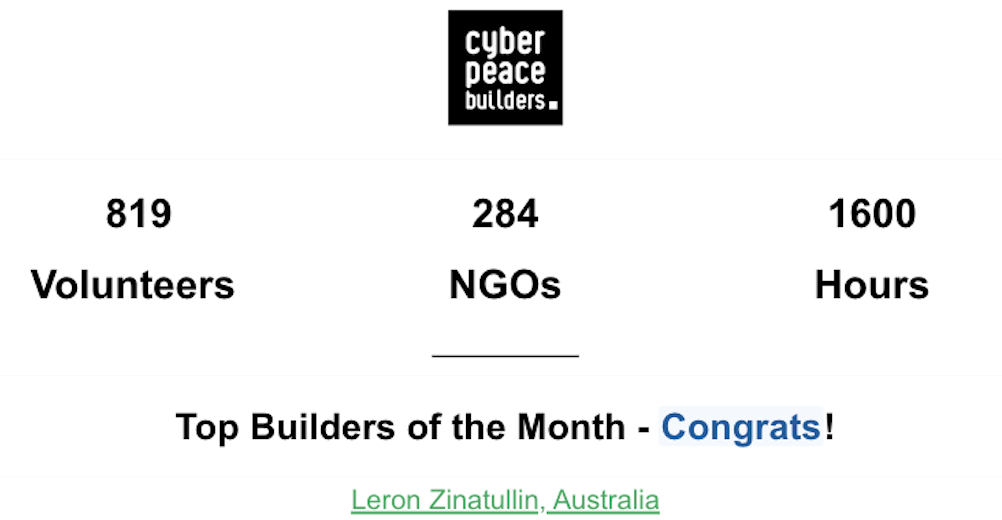
CyberPeace Institute’s Volunteer of the Month

I’m proud to be named CyberPeace Institute‘s Volunteer of the Month.

A big shoutout to CyberPeace for this awesome recognition! It’s been such a rewarding experience to help them in their mission to make the digital world safer for everyone.

The CyberPeace Institute is a non-profit focused on reducing the harm caused by cyberattacks to individuals and communities. Through their CyberPeace Builders program, they offer free cybersecurity support to organisations that need it most, especially those where cyber threats can have a serious impact.

As a volunteer, I’ve had the chance to help for-purpose organisations respond to cyber attacks, develop incident response plans, run security awareness training, perform dark web monitoring and craft essential policies and procedures. Plus, I’ve provided general cyber advice along the way. It’s been an incredible journey being part of a team that’s making a real difference.

Scenario analysis in cyber security: building resilience

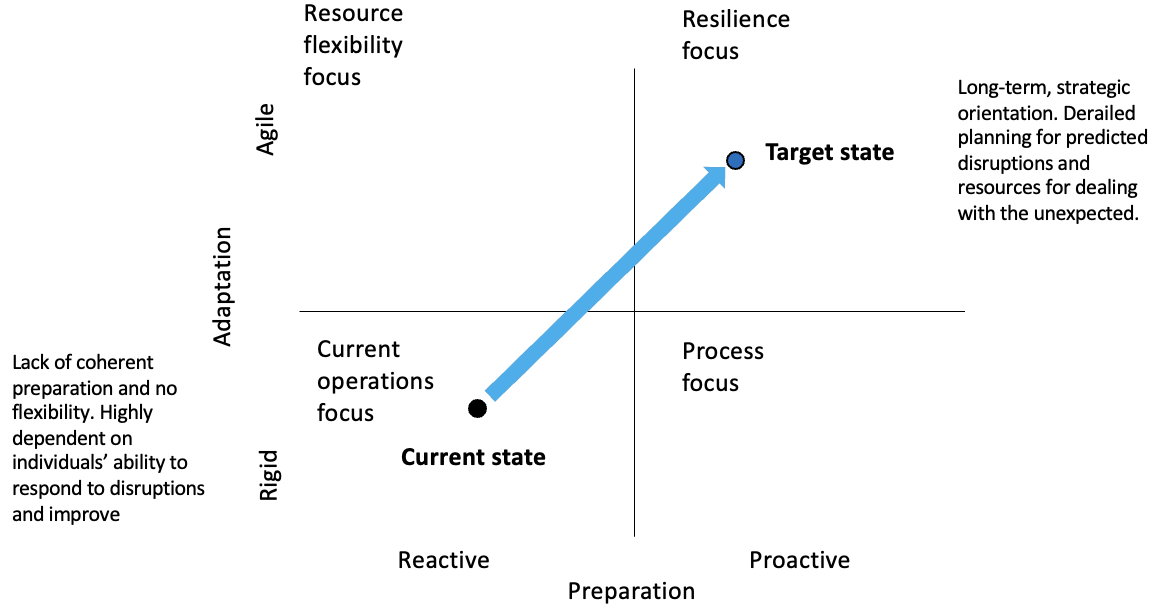
Resilience matrix, adapted from Burnard, Bhamra & Tsinopoulos (2018, p. 357).

Scenario analysis is a powerful tool to enhance strategic thinking and strategic responses. It aims to examine how our environment might play out in the future and can help organisations ask the right questions, reduce biases and prepare for the unexpected.

What are scenarios? Simply put, these are short explanatory stories with an attention- grabbing and easy-to-remember title. They define plausible futures and often based on trends and uncertainties.

More

How to adopt NIST CSF 2.0

CSF 2.0 Functions. Source: NIST

NIST released a new version of the Cybersecurity Framework with a few key changes:

  • It now can be applied beyond critical infrastructure, making it more versatile and straightforward to adopt.
  • It introduces a new core “Govern” function that includes categories from other sections, with increased focus on supply chain risk management and accountability.
  • It highlights synergies with the NIST Privacy Framework.

I often use this framework to develop and deliver information security strategy. Although, other methodologies exist, I find its layout and functions facilitate effective communication with various stakeholder groups, including the Board.

More

Cyber security for social impact

As a cyber security leader, I feel strongly about social issues related to human rights in the context of privacy, data protection and safe use of technology. I believe technology can be an enabler but also a potential cause of harm that needs to be considered.

I started volunteering with the CyberPeace Institute to leverage my cyber and technology skills to empower not-for-profit organisations to combat cyber threats and protect the communities they serve.

More

Systems thinking in cyber security

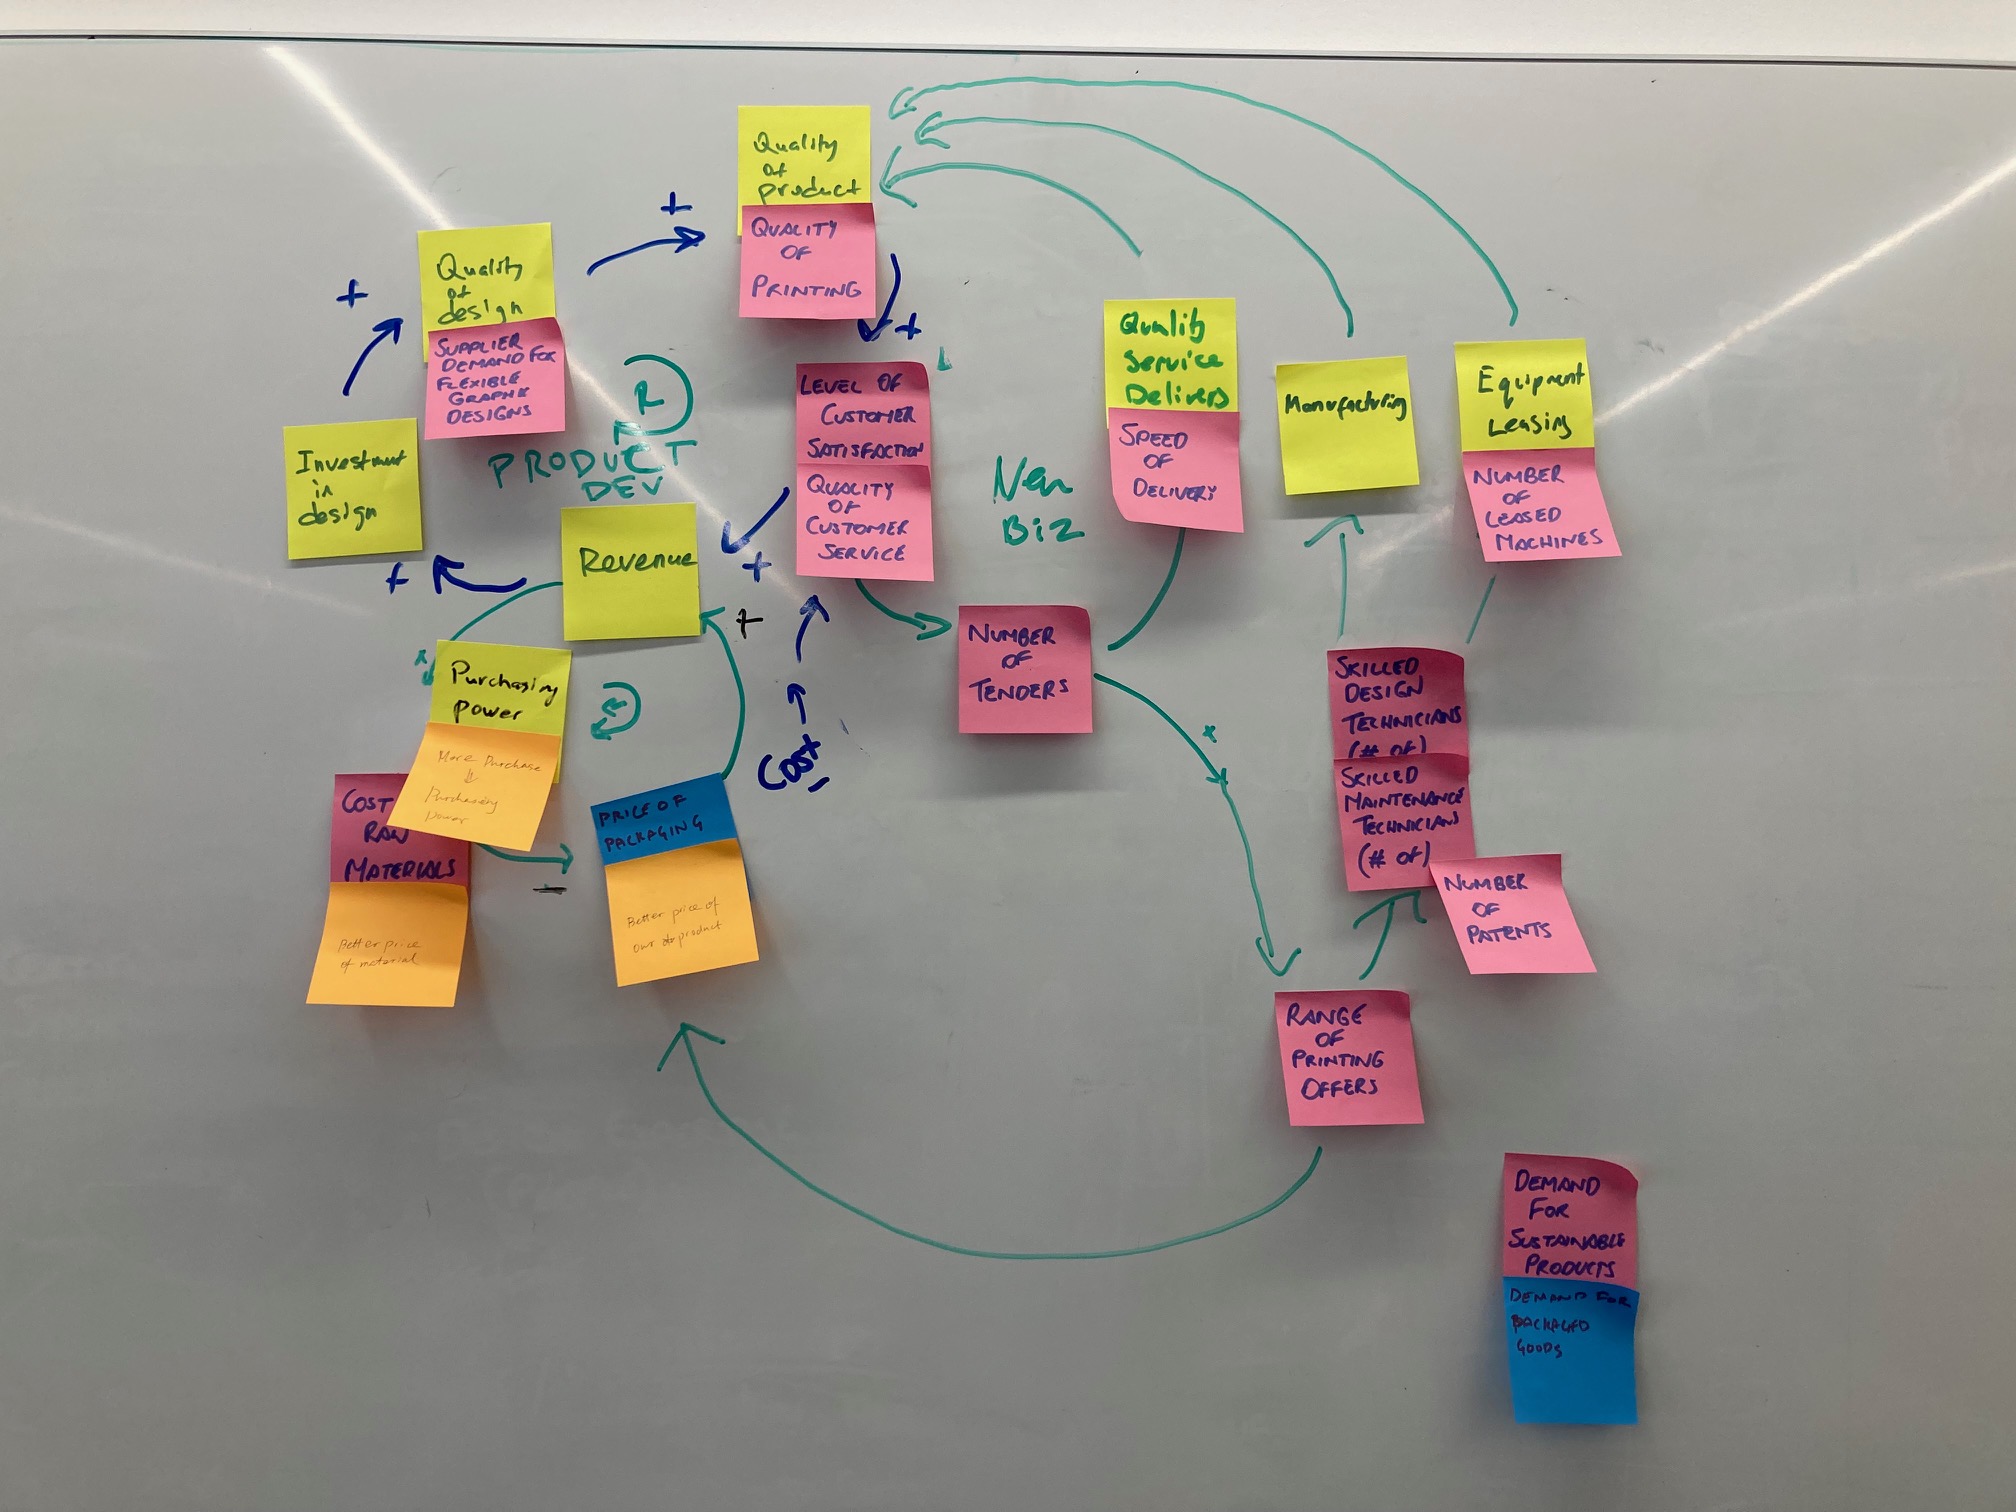
Cyber security leaders deal with complex problems all the time, but only a few are well equipped to deal with such challenges effectively. Systems thinking is a discipline that can help CISOs improve their ability to see the bigger picture and move beyond simplistic linear cause-effect relationships and point-in-time snapshots.

Systems thinking is a mindset that encourages you to see interdependencies, processes and patterns of complex systems. Complex systems contain multiple interacting feedback loops and it is this feature that make them so challenging to understand, diagnose and improve.

In this blog I outline some examples of complex systems, recommend tools to begin to understand and influence them and demonstrate how these techniques can be applied to improve digital safety and security.

More

Developing effective negotiation skills

Negotiation is a core skill that can make or break your success as a CISO.

While technical expertise is important, it’s equally critical to recognise the value of negotiation skills in cyber security leadership. By developing and applying strong negotiation skills, you’ll be better equipped to lead your organisation in an increasingly complex and challenging cyber security landscape.

I recently completed a negotiations workshop by Filip Hron and highly recommend him as a facilitator and his book ‘Negotiations Evolved’. I particularly appreciate his focus on ethics and value creation.

In this blog, I outline how some of the skills can be applied to the cybersecurity context.

More

How to maximise the return on security investment

Not every conversation a CISO is having with the Board should be about asking for a budget increase or FTE uplift. On the contrary, with the squeeze on security budgets, it can be an opportunity to demonstrate how you do more with less.

To demonstrate business value and achieve desired impact, a CISO’s cyber security strategy should go beyond cyber capability uplift and risk reduction and also improve cost performance.

Security leaders don’t have unlimited resources. Significant security transformation, however, can be achieved leveraging existing investment and security resource levels.

More