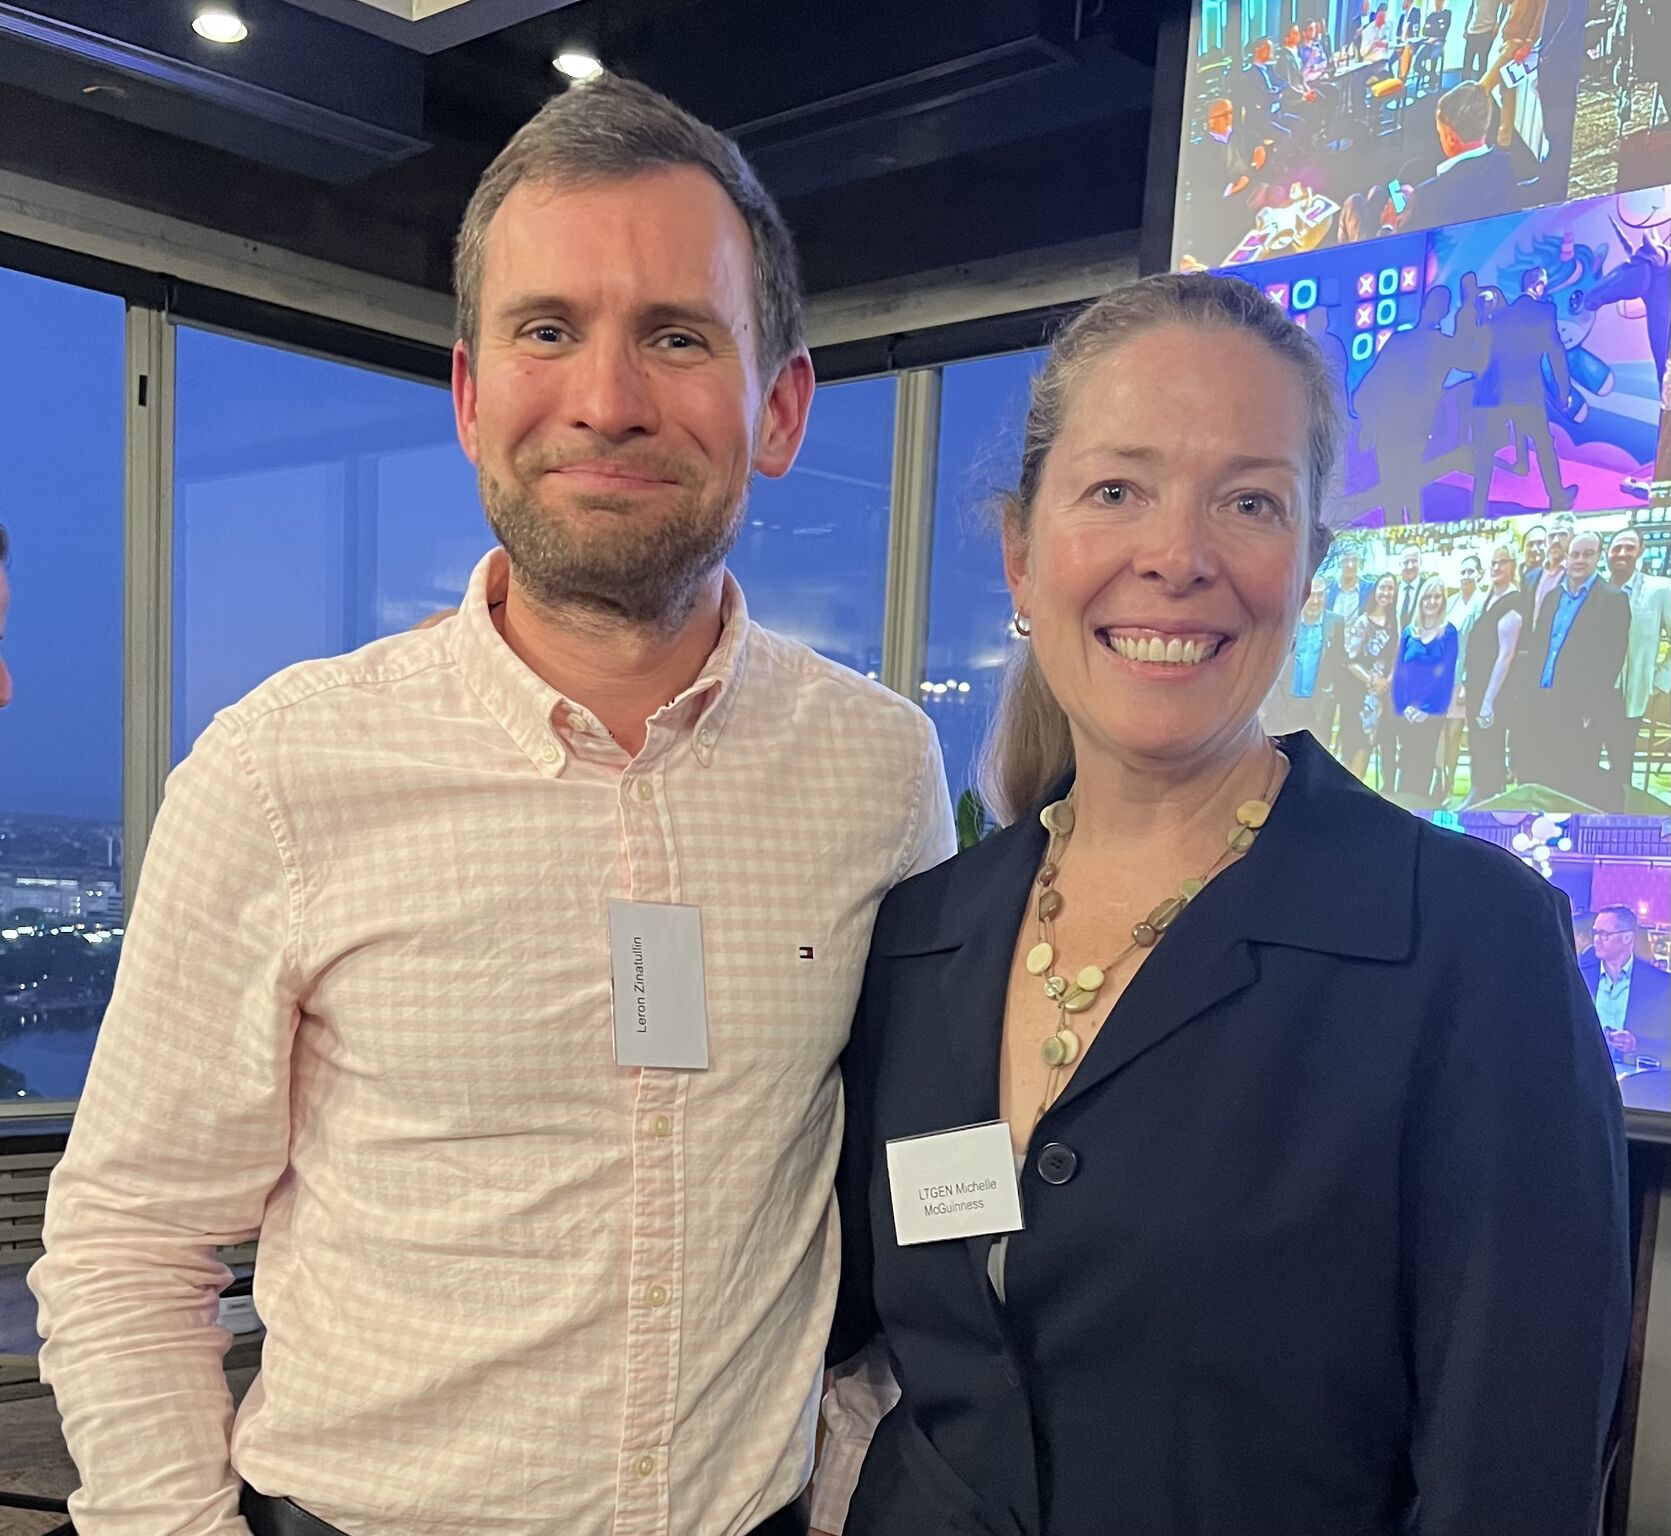
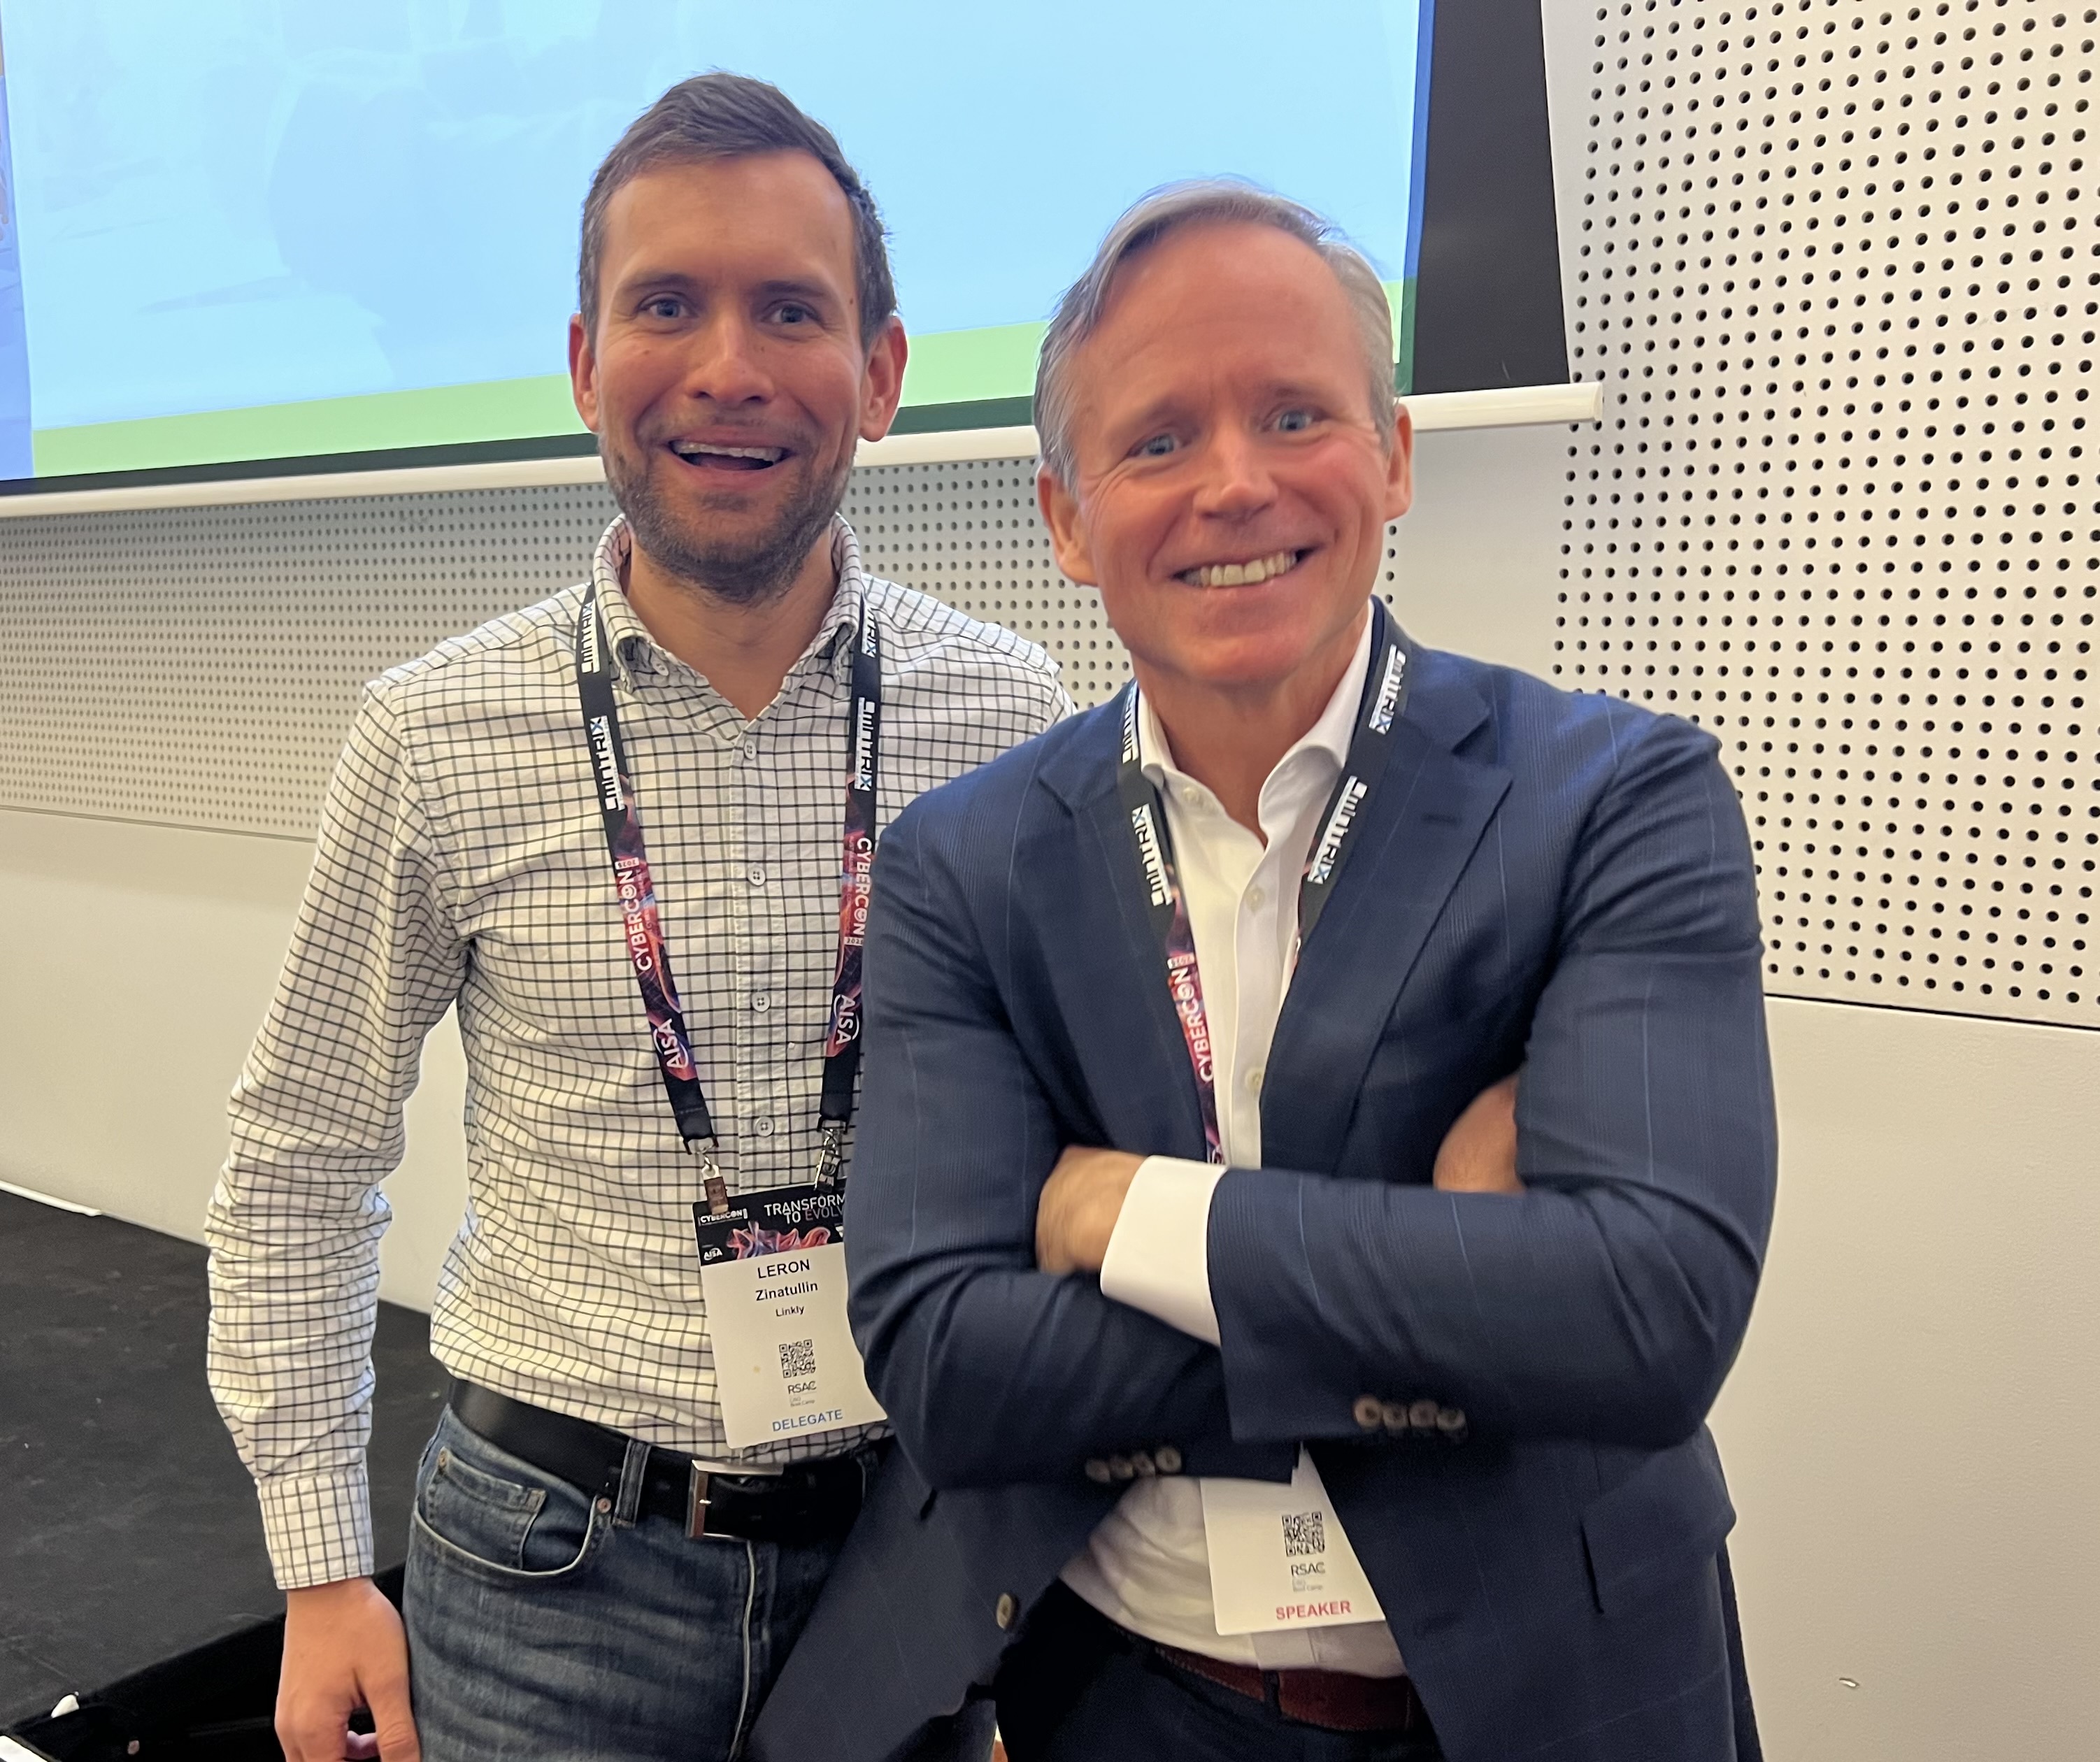
It was great to chat with Lieutenant General Michelle McGuinness, the National Cyber Security Coordinator, about the Australian Cyber Security Strategy as well as key initiatives, strategic imperatives and challenges that CISOs must navigate.
I appreciate an opportunity to contribute to the ongoing conversation on cyber threat landscape, risk and AI governance.
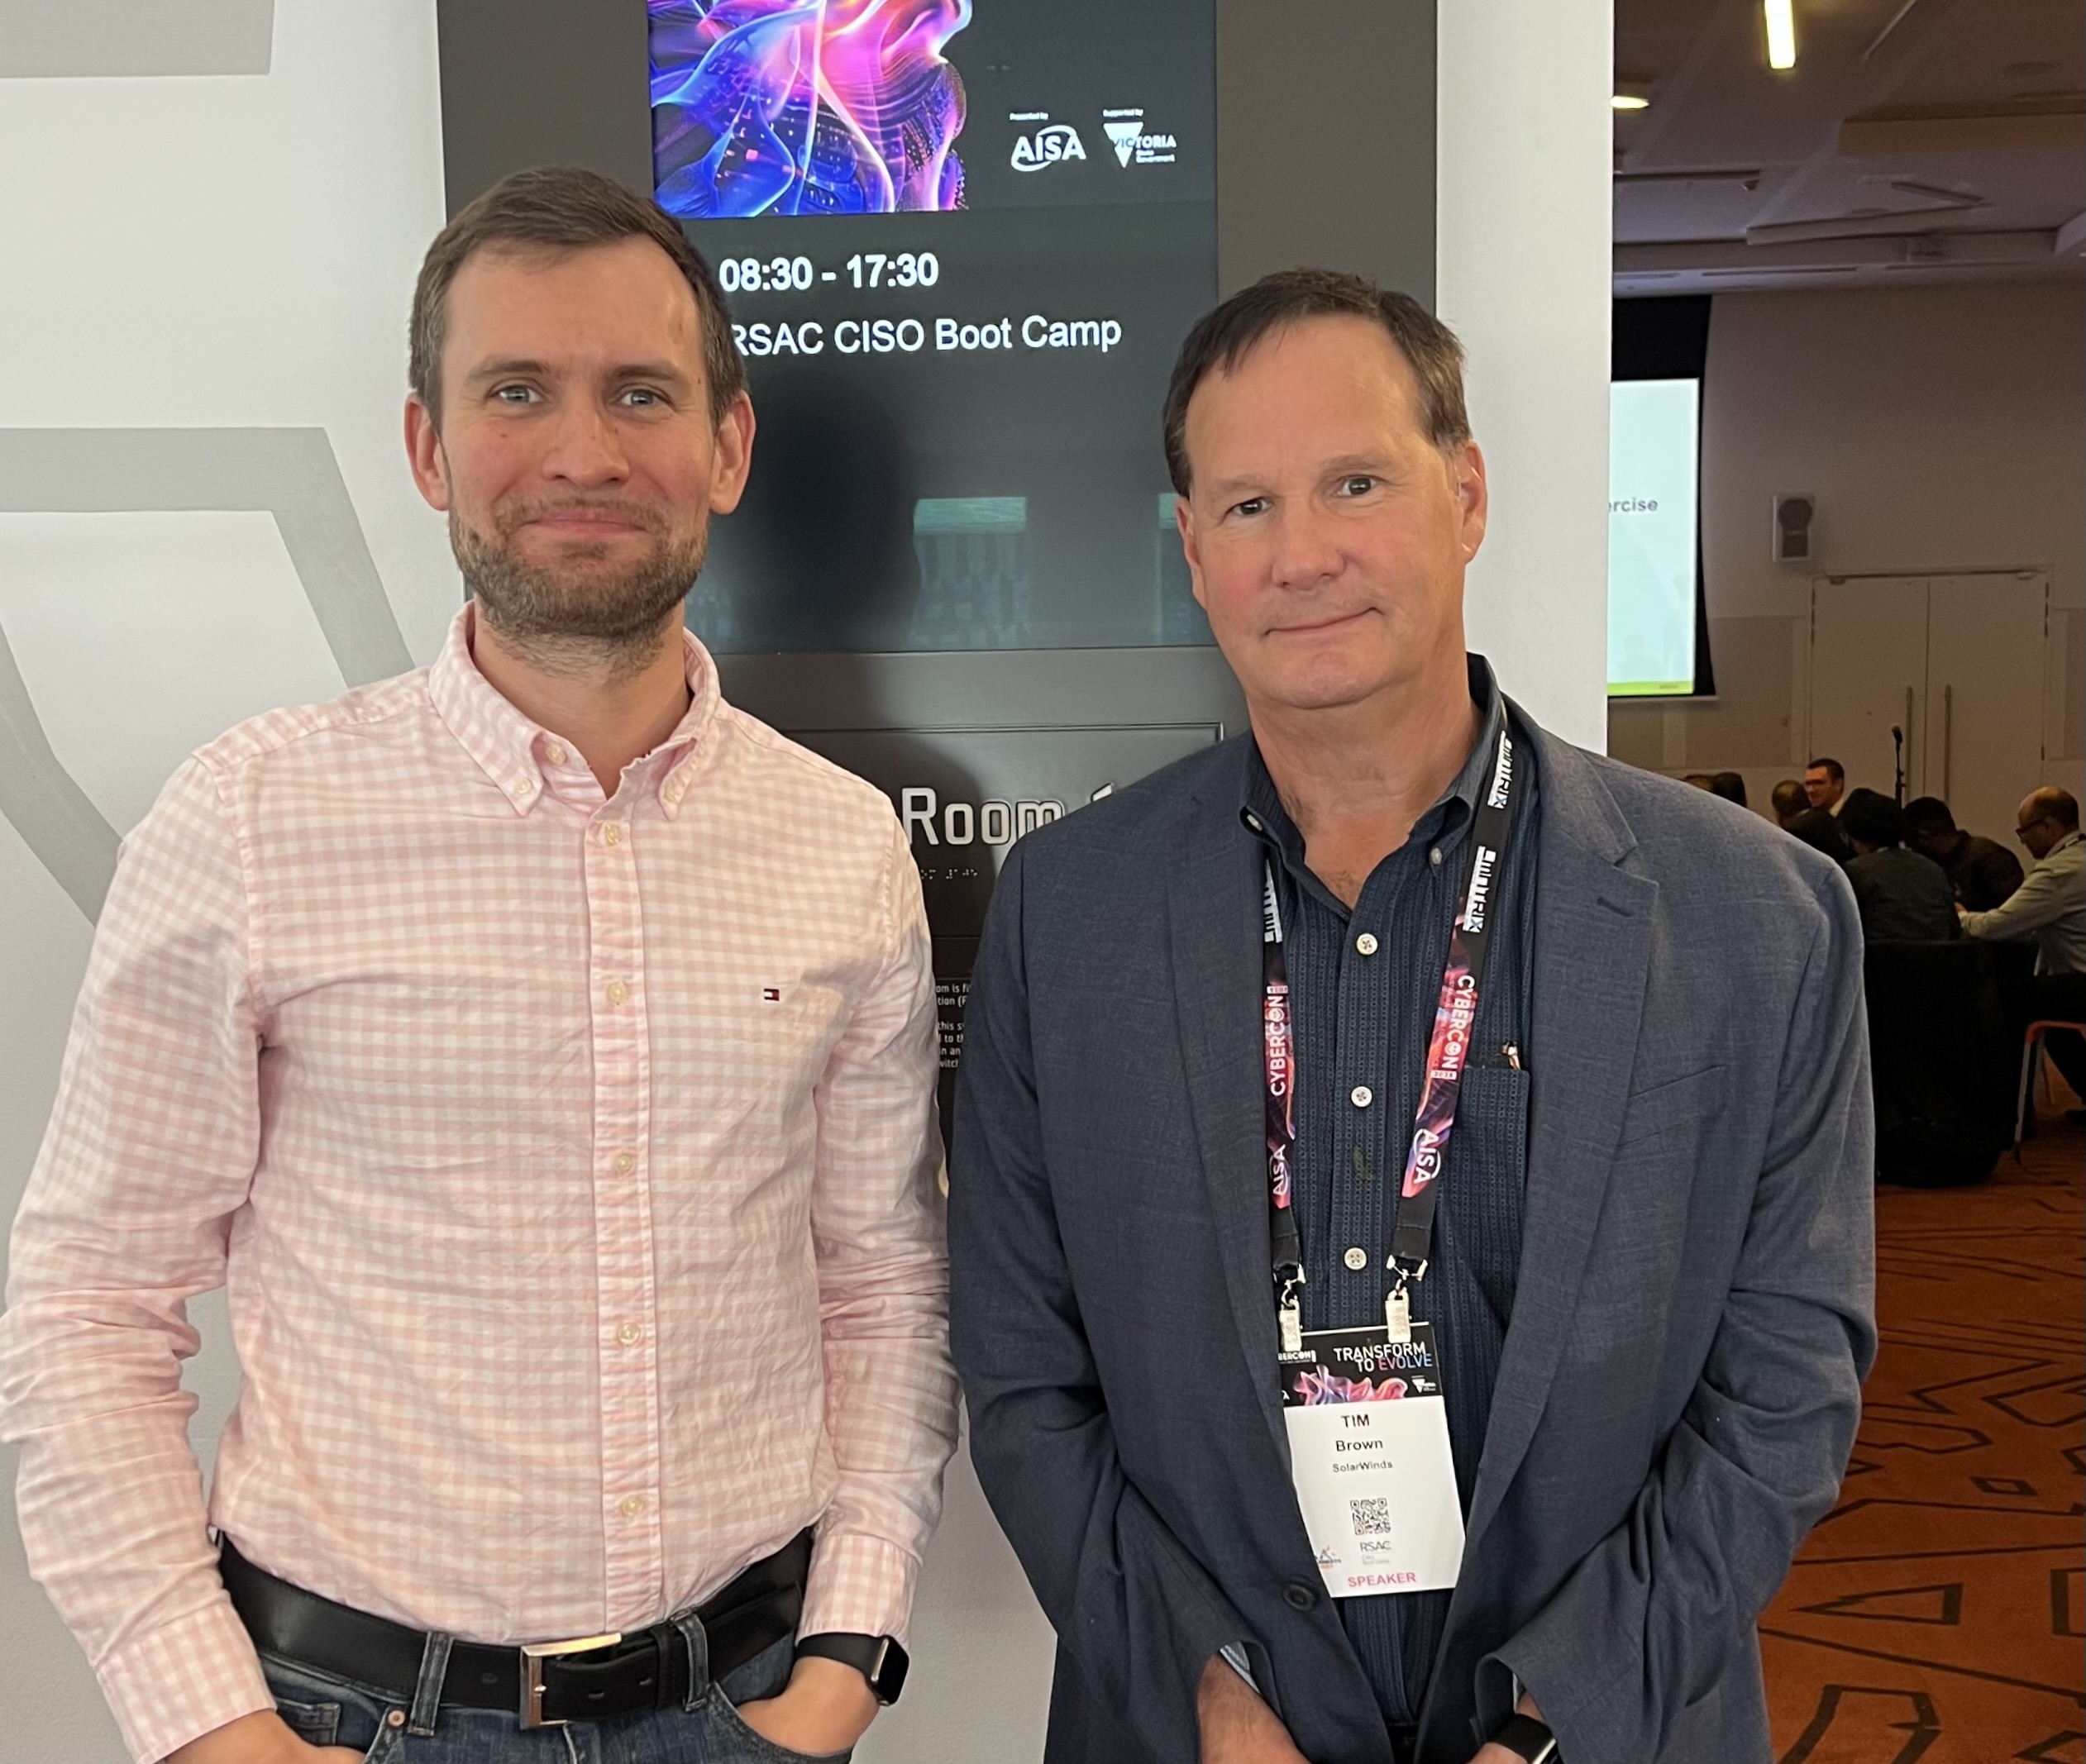
It was so good to attend the RSAC CISO Bootcamp at CyberCon Melbourne – a practical session for CISOs.
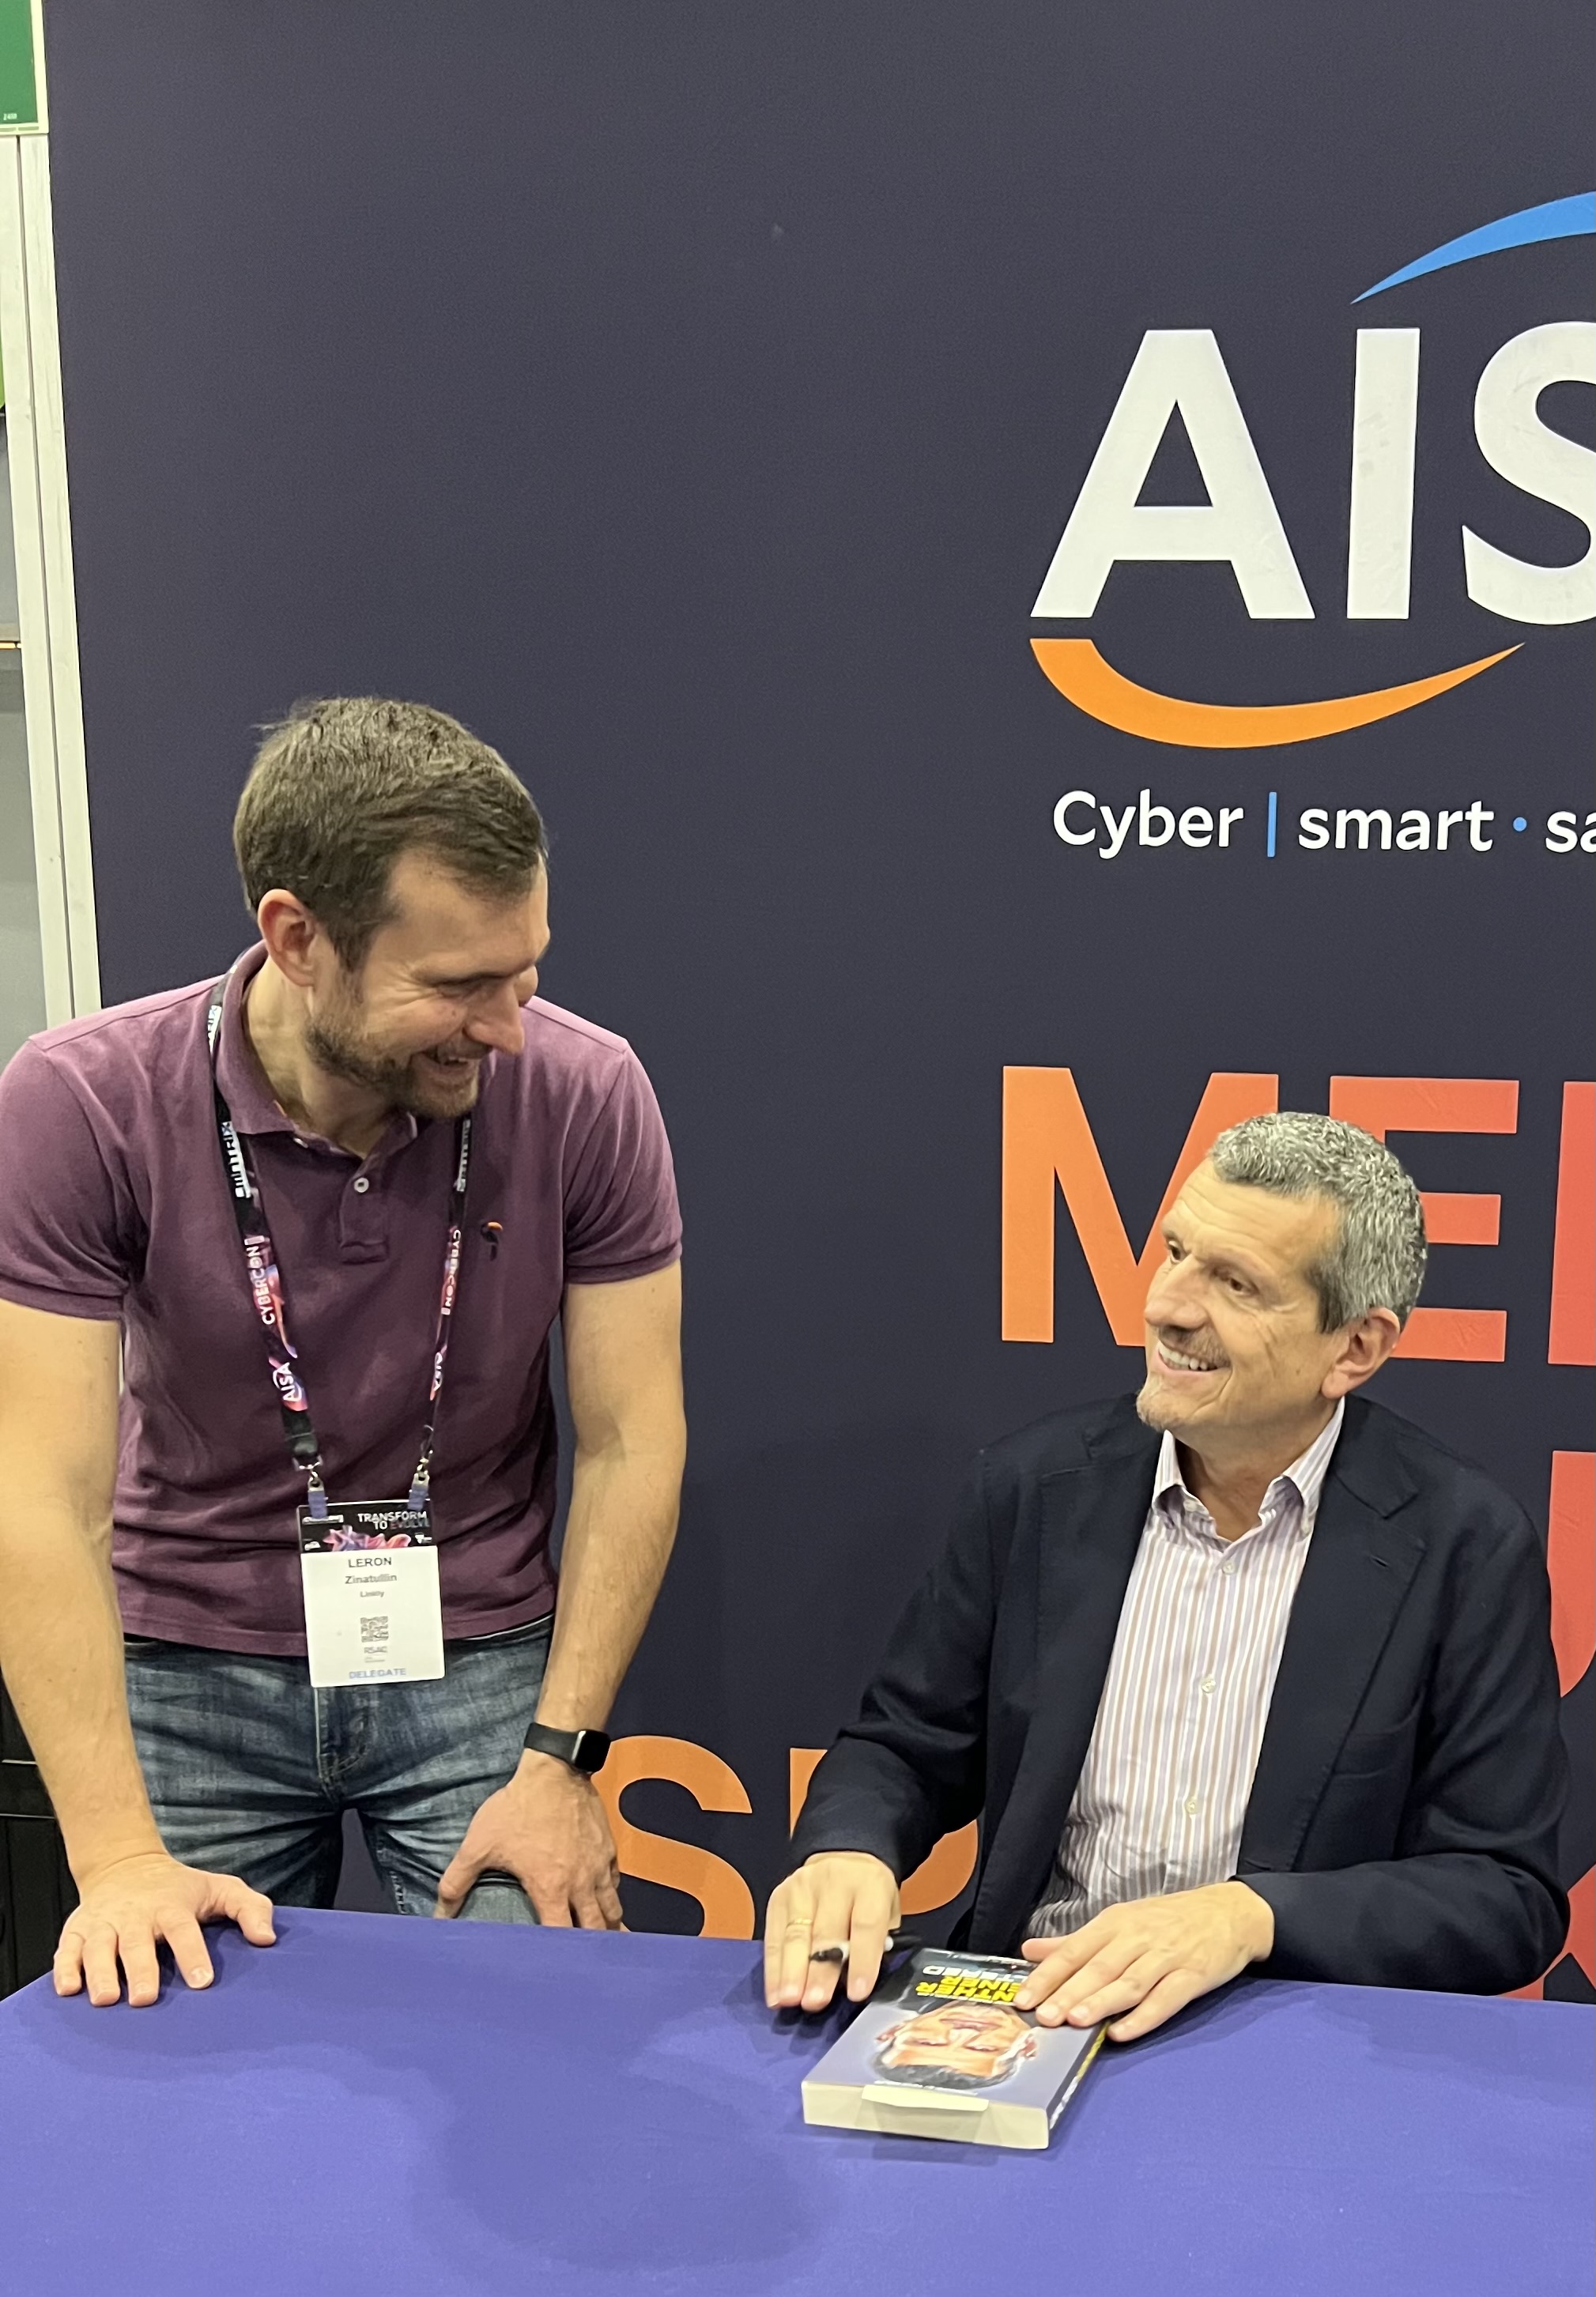
Highlights that stuck with me: 💡 A conversation with Brian Krebs on AI security and organised cybercrime: attackers are tooling up fast; our defences must keep pace. 💡 A candid, closed-door session with Tim Brown, CISO of SolarWinds, about crisis response: execution matters, but so does the personal toll on teams and leaders. 💡 A chat with F1’s Guenther Steiner on teamwork and resilience in high-pressure environments.
Events like this remind me how much strength there is in our community. I’m proud to contribute and be part of it. You don’t need a challenge coin to get help – if you want to compare notes or need a sounding board, reach out.
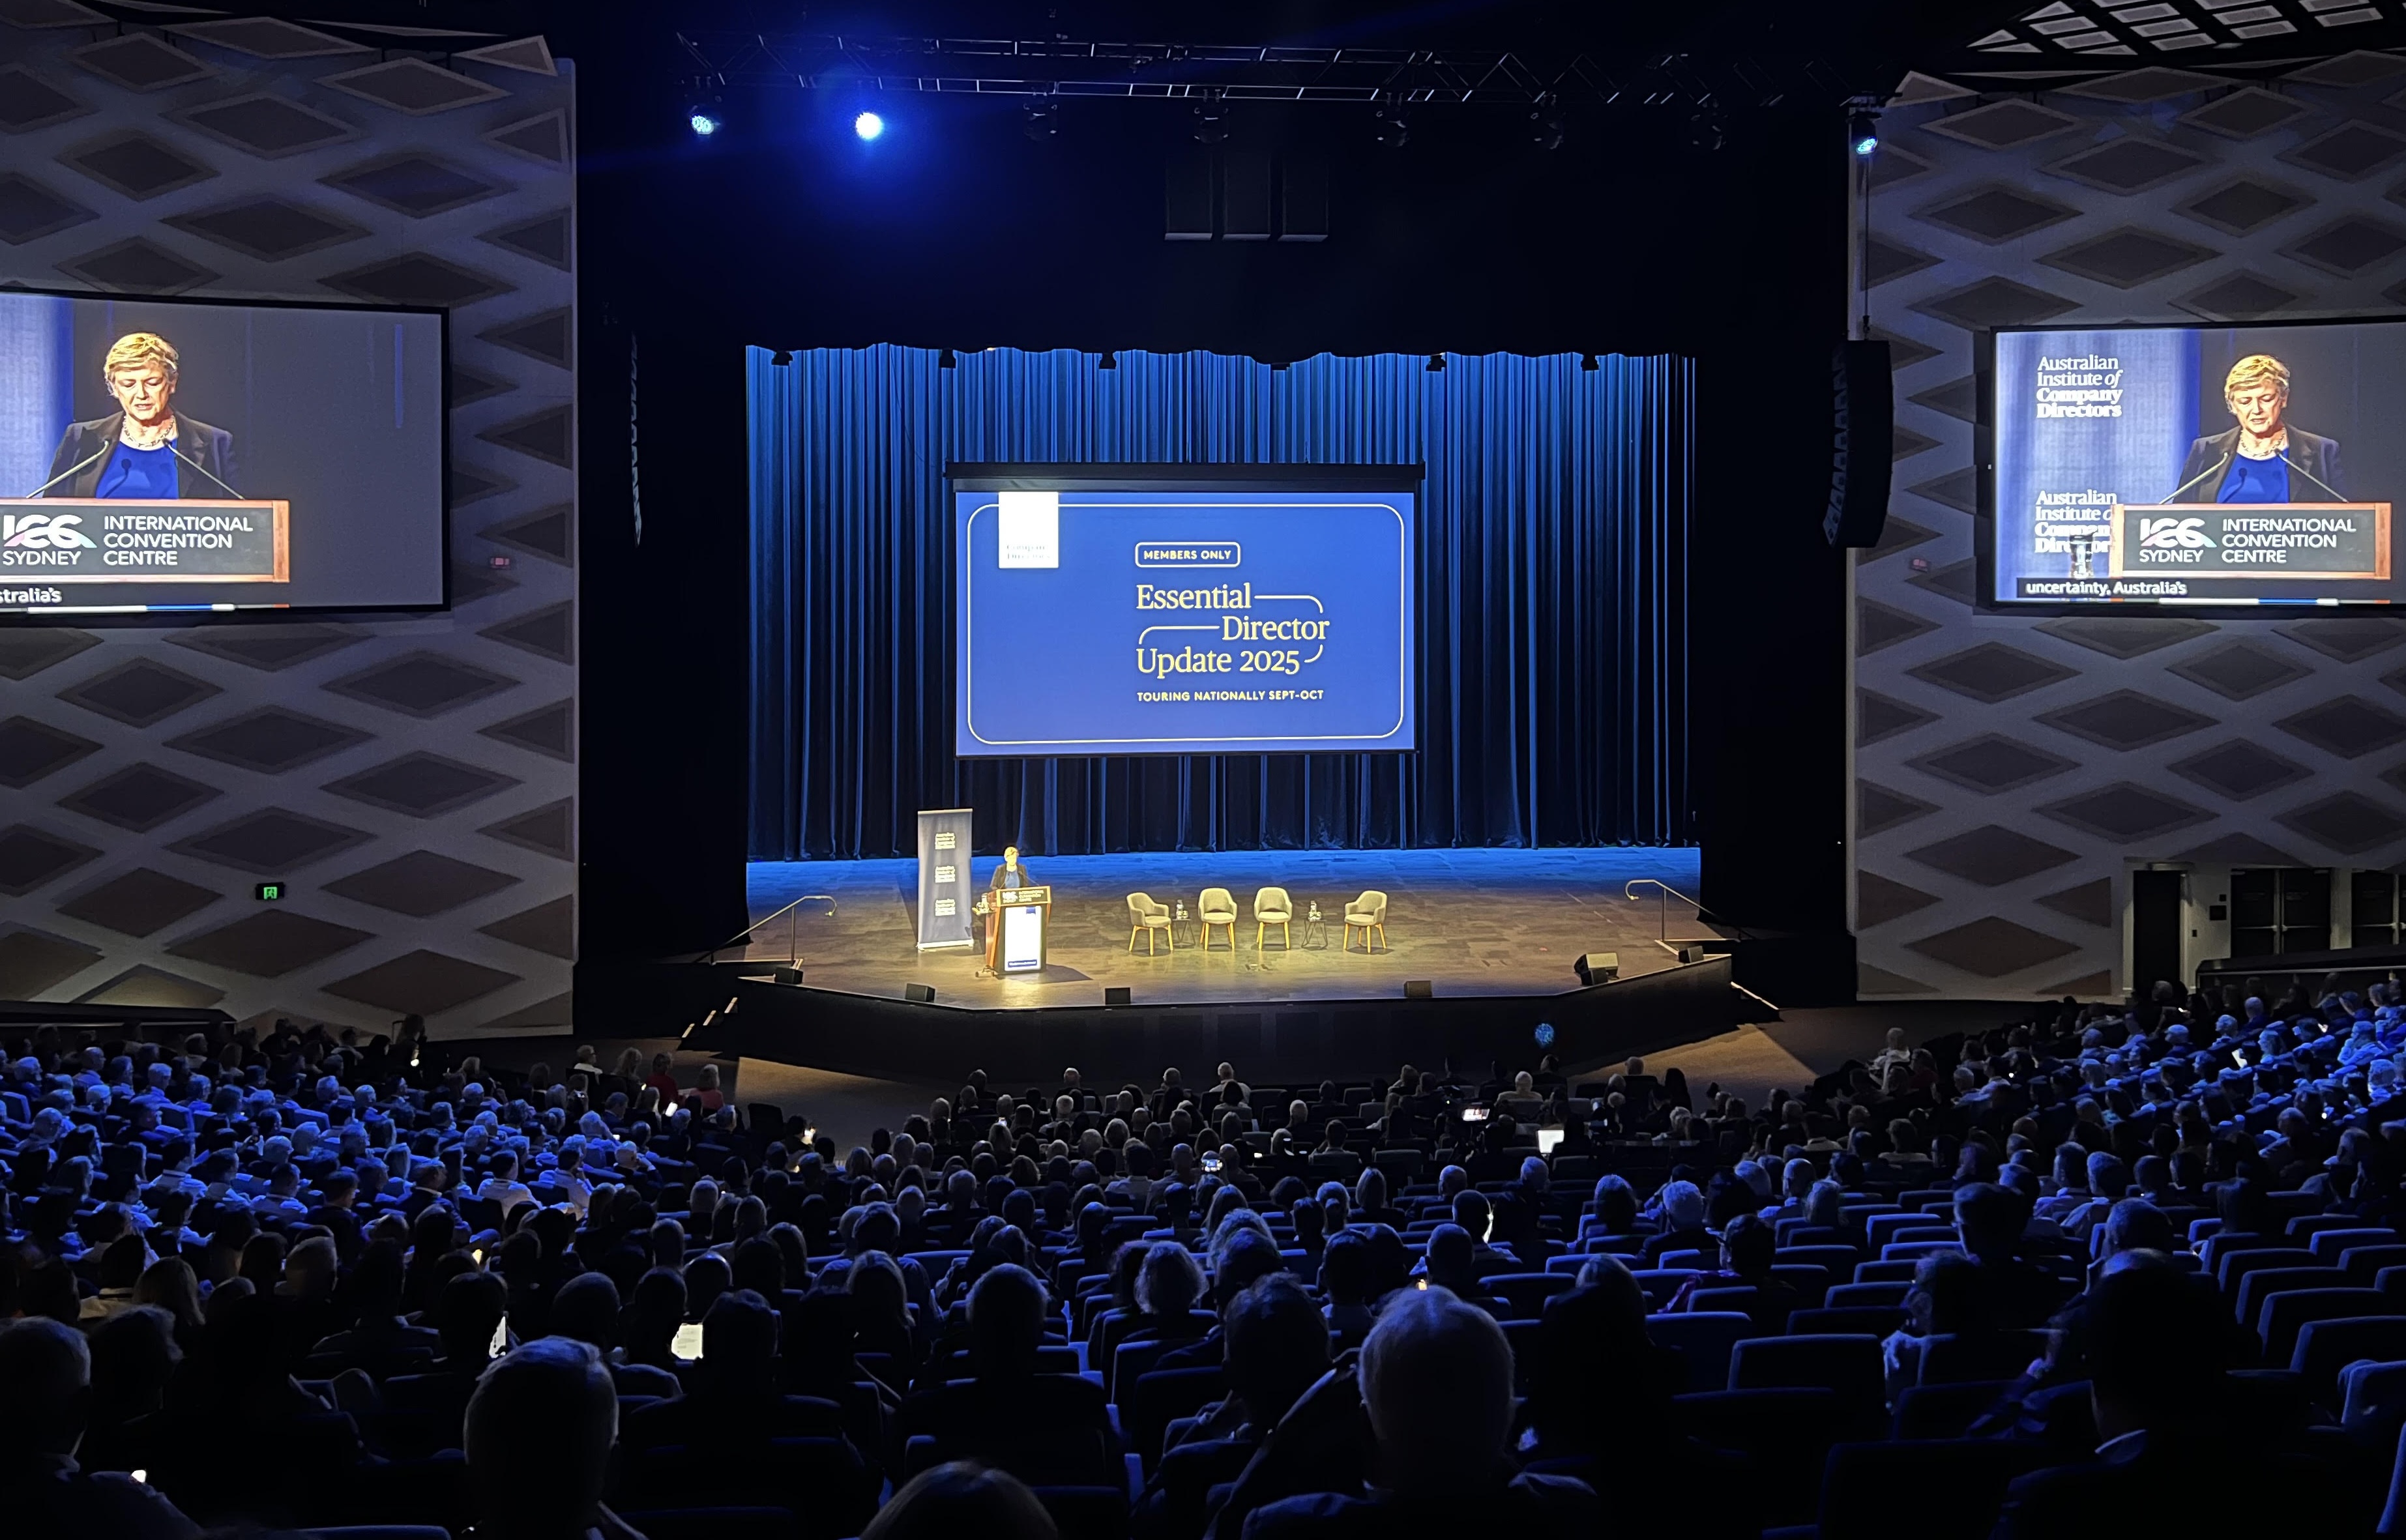
It was good to attend the Essential Director Update – a timely reminder that good governance now requires foresight as well as oversight.
Staying on the forefront of contemporary governance demands AI and cybersecurity competency.
My key takeaways for boards and executives: ☑️ Data is the fuel: protect data integrity (accurate, consistent, timely) and focus governance where it creates the most value. ☑️ AI is everywhere, no longer just an IT challenge: adopt a human-centred approach, define guardrails around intent, and factor legal and ethical considerations into every deployment. ☑️ Balance innovation with risk: prioritise highest-value use cases, automate safety controls where possible, but don’t outsource accountability. ☑️ Cybersecurity must be risk-based: know your crown jewels, expect incidents, build crisis response plans and regularly test your defences. ☑️ People first: changing work practices will affect roles and culture; steer the transition and invest in policy and education.
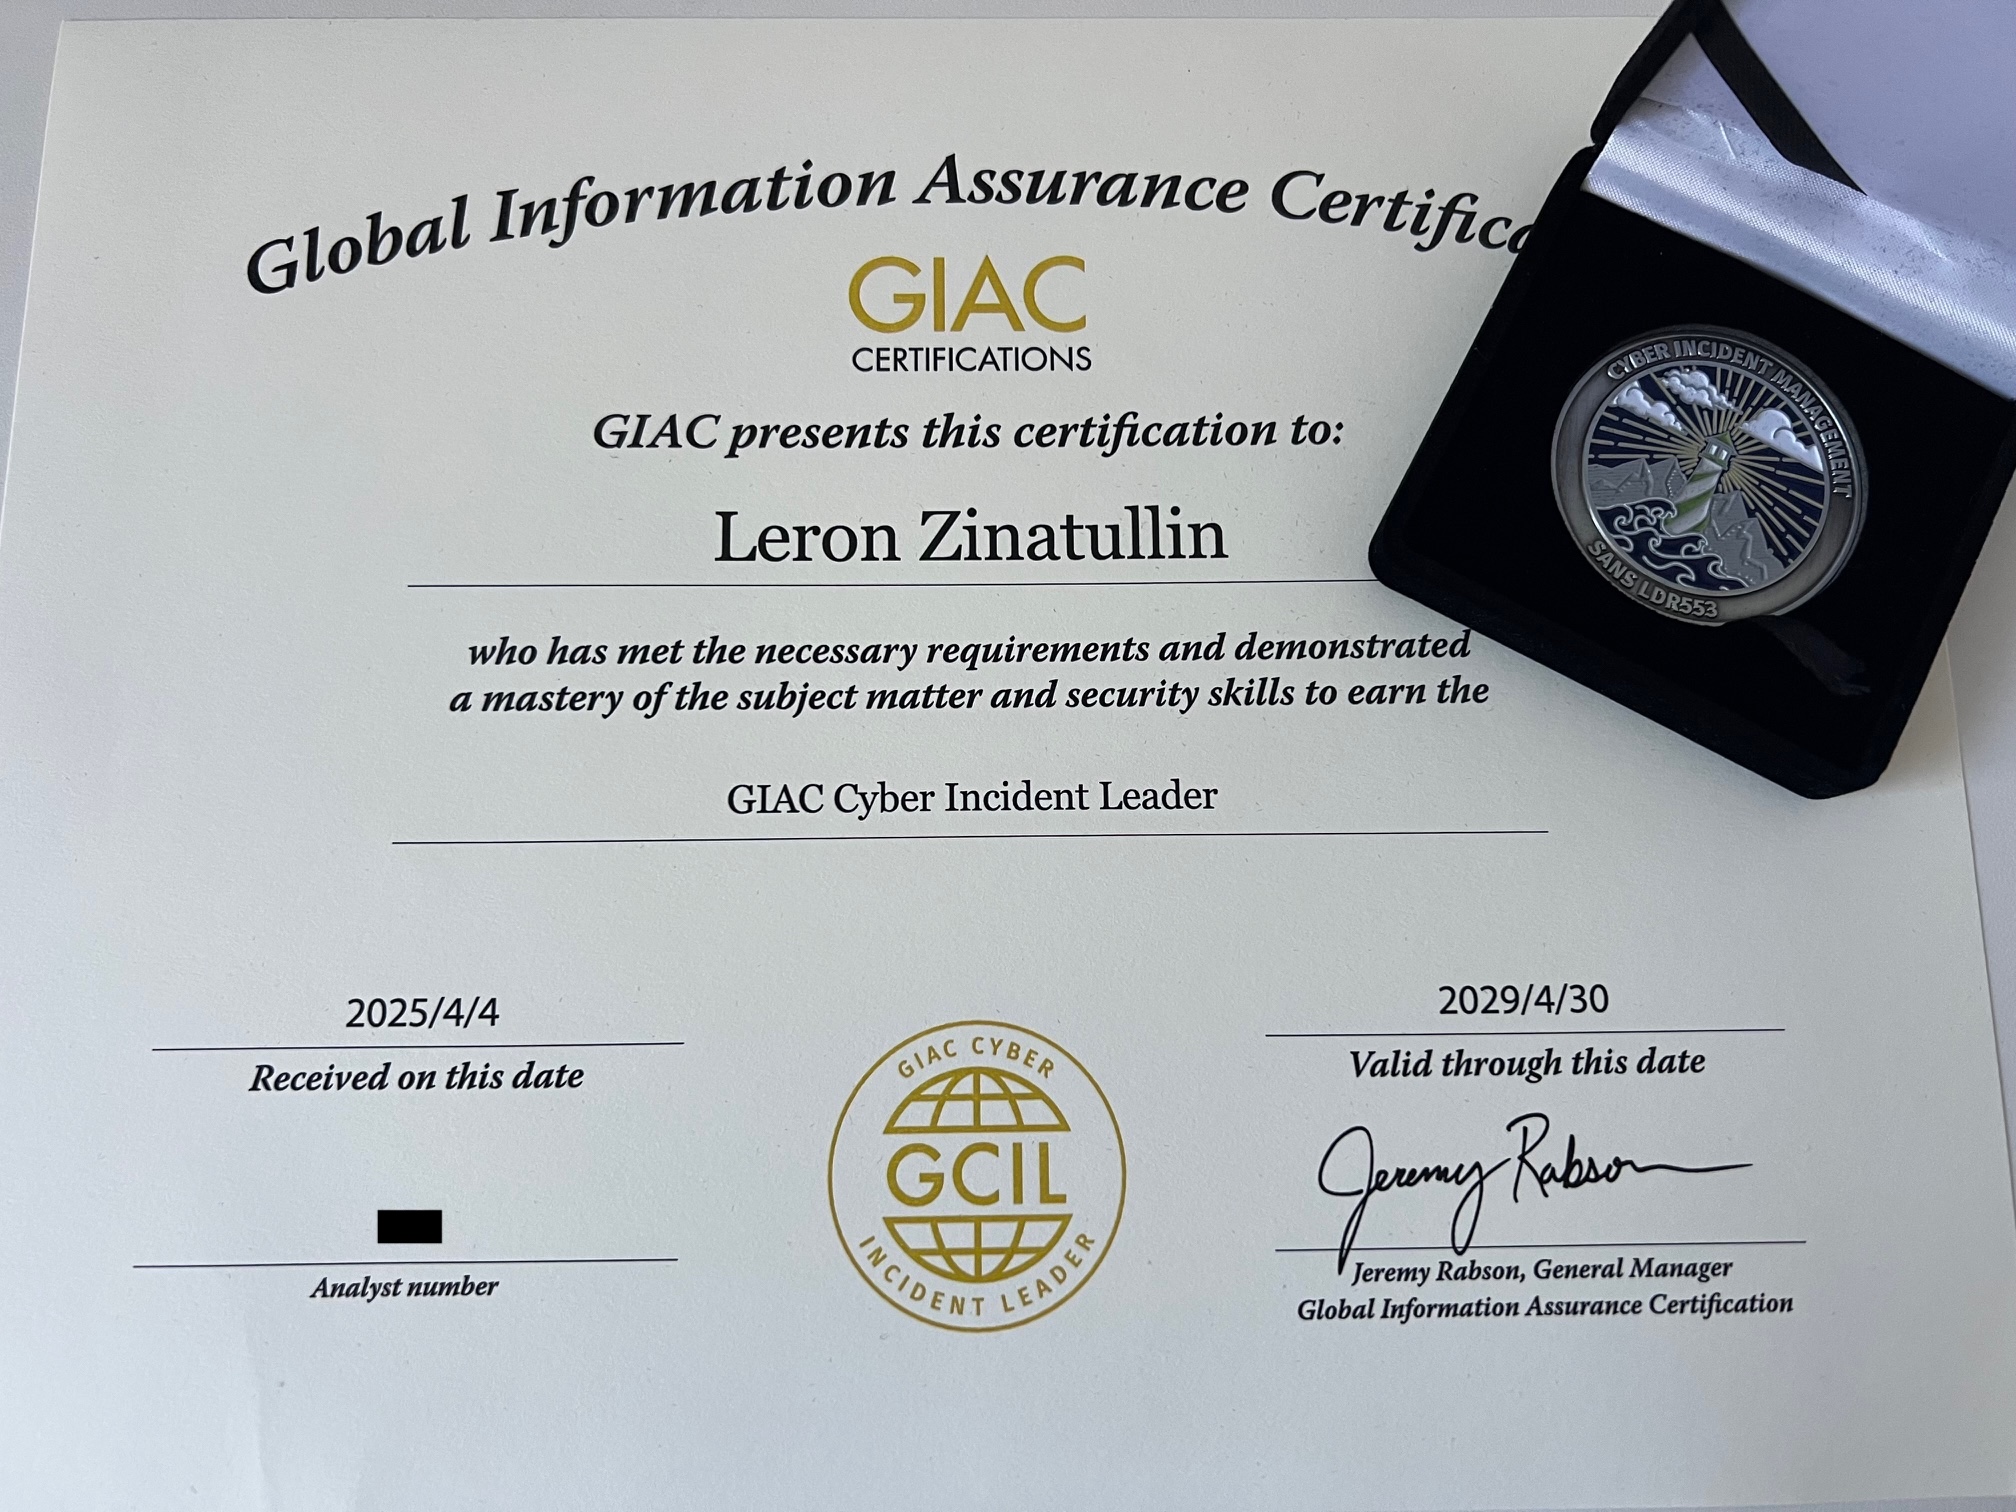
I’m proud to share that I’ve completed SANS’s LDR553: Cyber Incident Management hands-on training and earned the GIAC Cyber Incident Leader (GCIL) certification.
This course sharpened my ability to guide teams through every stage of a breach. I was awarded a challenge coin for the top score in the final capstone project.
I’m thrilled to share that I’ve recently earned the GIAC Strategic Planning, Policy, and Leadership (GSTRT) certification- a milestone that validates my ability to architect and sustain cybersecurity programs with a sharp focus on business value and executive alignment.
During the session, Richard broke down risk quantification, focusing on identifying the risks most likely to cause significant business losses where assets, threats and vulnerabilities intersect.
I’m also glad to receive his book for correctly estimating cost in our the discussions. It’s one of the most influential books in security: it challenges subjective risk assessments, offering practical frameworks for using data, probability and economics to drive smarter security decisions.
Cyber security is a relentless race to keep pace with evolving threats, where staying ahead isn’t always possible. Advancing cyber maturity demands more than just reactive measures—it requires proactive strategies, cultural alignment, and a deep understanding of emerging risks.
I had an opportunity to share my thoughts on staying informed about threats, defining cyber maturity, and aligning security metrics with business goals with Corinium’s Maddie Abe ahead of my appearance as a speaker at the upcoming CISO Sydney next month.
I had a great week at the AICD’s Company Directors Course learning about governance, risk, strategy, legal environment, financial literacy, performance and achieving board effectiveness.
I particularly liked the interactive discussions and case studies to practice ethical decision making, applying concepts in practice and adopting the director mindset.
I had the privilege to join a brilliant cohort of CISOs at the RSA Conference CISO Bootcamp. It was an energising experience, where seasoned experts and emerging leaders in cybersecurity came together to tackle our industry’s most pressing challenges.
The bootcamp was more than just a learning experience; it was a platform for sharing personal insights, gaining fresh perspectives and engaging in a thought-provoking debate.
From discussing emerging threats to exchanging strategies for resilience, it was a reminder of the power of community in cybersecurity. A huge thanks to all organisers and speakers for creating a space where we can grow together and tackle our industry’s biggest challenges.
It’s been fantastic to have an opportunity to give back to the community and volunteer with ISACA this year.
The Sydney Chapter hosted a number of professional development events for cyber, risk, governance and IT professionals with a common objective of building digital trust and securing our interconnected world. I had a chance to support these initiatives, ranging from fundraising for a mental health charity to helping organise conferences.
I found this experience incredibly rewarding and made some good friends along the way.