I’ve been invited to speak at the CSO30 Conference today on applying behavioural science to cyber security.
I talked about the role behavioural science plays in improving cybersecurity in organisations, the challenges of applying academic theory in practice and how to overcome them.
I shared some tips on how to build the culture of security and measure the success of your security programme.
We also spoke about the differences in approaches and scalability of your security programme depending on the size and context you organisation, including staffing and resourcing constraints.
Overall, I think we covered a lot of ground in just 30 minutes and registration is still open if you’d like to watch a recording.
One of the UK’s leading research-intensive universities has selected The Psychology of Information Security to be included in their flagship Information Security programme as part of their ongoing collaboration with industry professionals.
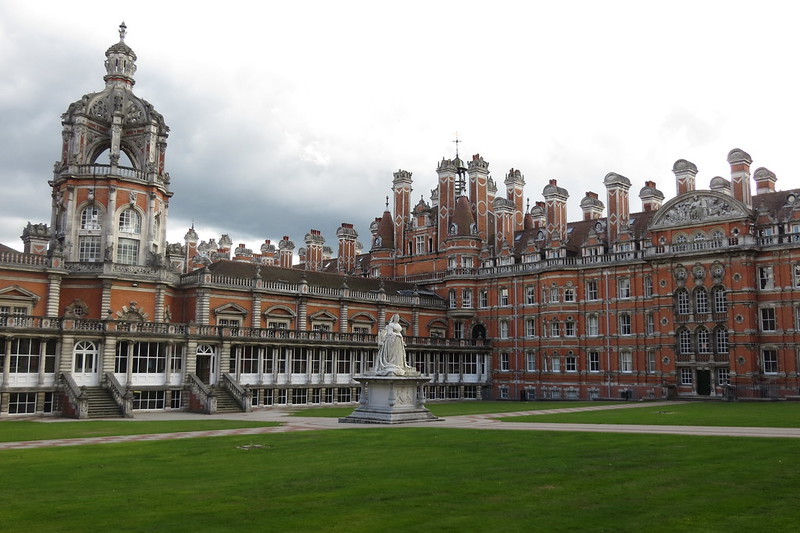
Royal Holloway University of London’s MSc in Information Security was the first of its kind in the world. It is certified by GCHQ, the UK Government Communications Headquarters, and taught by academics and industrial partners in one of the largest and most established Information Security Groups in the world. It is a UK Academic Centre of Excellence for cyber security research, and an Engineering and Physical Sciences Research Council (EPSRC) Centre for Doctoral Training in cyber security.
Researching and teaching behaviours, risk perception and decision-making in security is one of the key components of the programme and my book is one of the resources made available to students.
“We adopted The Psychology of Information Security book for our MSc in Information Security and have been using it for two years now. Our students appreciate the insights from the book and it is on the recommended reading list for the Human Aspects of Security and Privacy module. The feedback from students has been very positive as it brings the world of academia and industry closer together.”
Dr Konstantinos Mersinas, Director of Distance Learning Programme and MSc Information Security Lecturer.
Using abstractions to think about risks is a useful technique to identify the ways an attacker could compromise a system.
There are various approaches to perform threat modelling but at the core, it’s about understanding what we are building, what can go wrong with it and what we should do about it.
Here is a good video by SAFECode introducing the concept:
I had a lot of fun participating in a panel discussion with fellow CISOs exploring the link between cyber security and business strategy. It’s a subject that is very close to my heart and I don’t think it gets enough attention.
In the course of the debate we covered a number of topics, ranging from leveraging KPIs and metrics to aligning with the Board’s risk appetite. We didn’t always agree on everything but I believe that made the conversation more interesting.
As an added bonus, my book The Psychology of Information Security was highlighted as an example of things to consider while tackling this challenge and to improve communication.
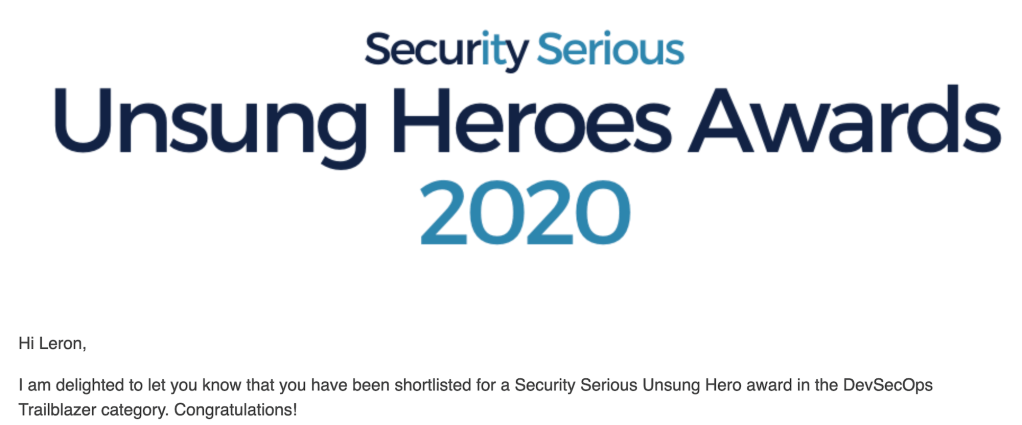
Ensuring security is embedded in the development lifecycle of software, from start to finish, is pivotal in creating a more cyber secure world. This award recognises individuals who are spearheading this initiative so that the creation of applications can continue to be dynamic, without sacrificing cybersecurity.
I’m excited to make the shortlist and wish best of luck to all the contenders!
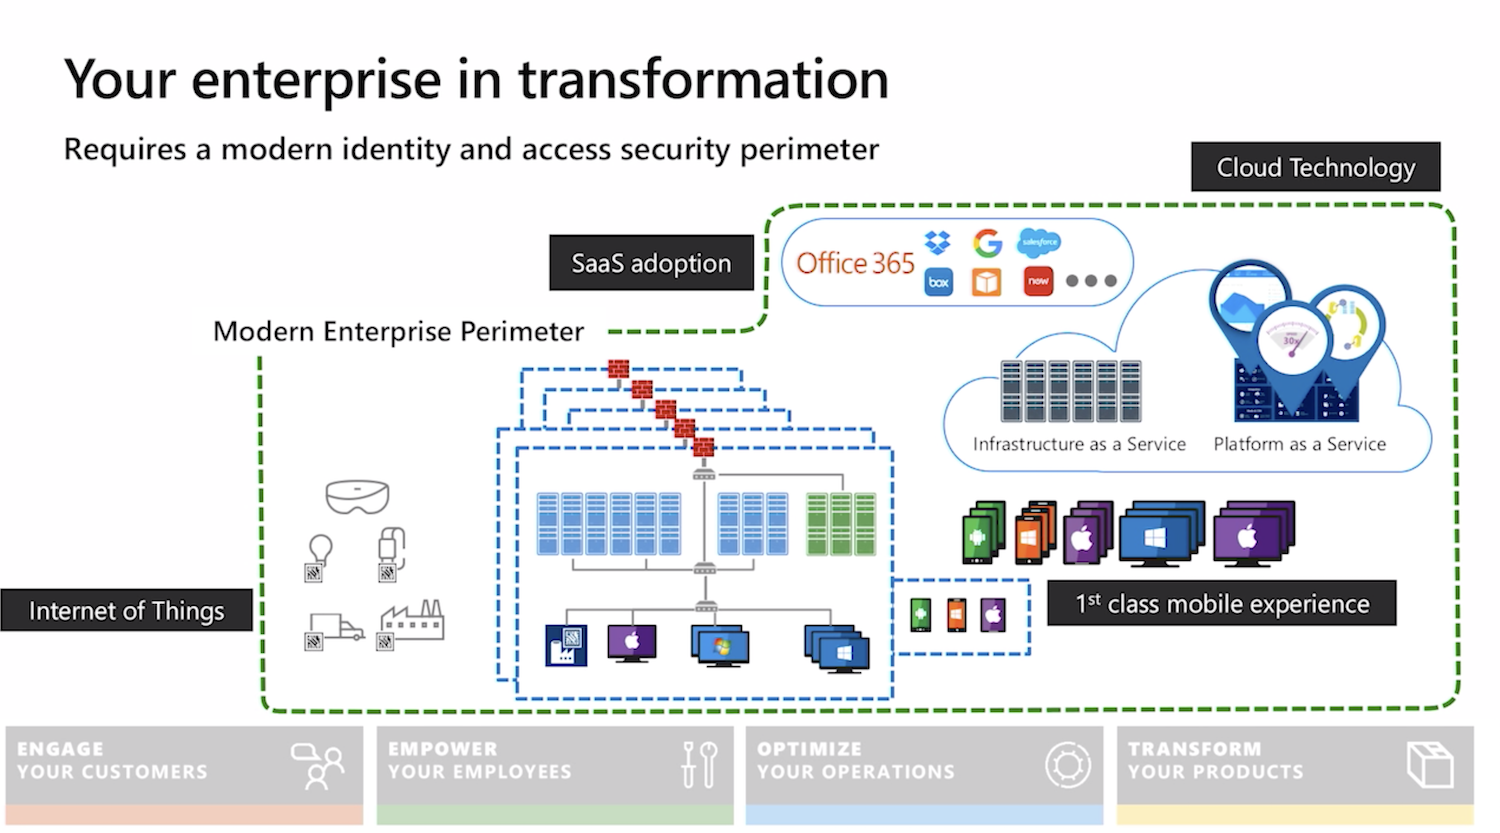
Chief Information Security Officer Workshop is a collection of on-demand videos and slide decks from Microsoft aimed to help CISOs defend a hybrid enterprise (that now includes cloud platforms) from increasingly sophisticated attacks.
As many organisations are recognising and experiencing first-hand, cyber-attacks are no longer a matter of if, but when. Recent cyber breaches at major corporations highlight the increasing sophistication, stealth, and persistence of cyber-attacks that organisations are facing today. These breaches are resulting in increased regulatory and business impact.
I’m excited to make the shortlist for the Personality of the Year category. The award recognises thought leadership, commitment to developing others and raising the profile of cyber security among businesses.
I had a chance to contribute to a free eBook by Cisco on adapting to the challenges presented by the Covid-19 pandemic. Check it out for advice on securing your remote workforce, improving security culture, adjusting your processes and more.
The Software and Security Engineering course taught at the University of Cambridge is available for free online. It includes video lectures, slide decks, reading materials and more.
Whether you are new to information security or a seasoned professional, this course will help you build solid foundations.
Lecture 9 covering critical systems is my favourite. It bring together previous discussions on psychology, usability and software engineering in the context of safety. It adds to the array of the case studies from Lecture 6, focusing on software failures and what we can learn from them. It also offers a fascinating analysis of the Therac-25 accidents and Boeing 737 Max crashes.